Ontact
CertiK reviewed OnTact on 3 Jan 2024: 6 findings, 0 critical; 4 marked fixed, 2 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings6
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 1 |
| Medium | 0 | 0 | 1 |
| Low | 0 | 0 | 2 |
HighCentralization Risks in TokenLock.solOpen
In the contract `TokenLock` the role `_owner` has authority over the functions shown in the diagram below. 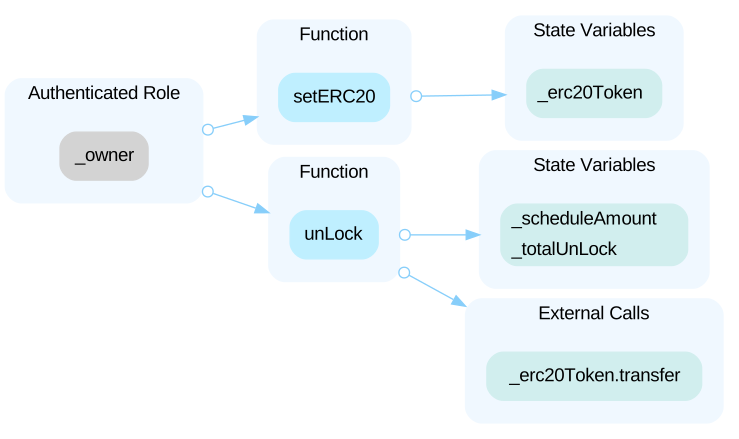 - `setERC20(address tokenAddress)`: Allows setting the address of the ERC20 token that will be managed by this contract. This function requires that the token address is not the zero address. It is a privileged function accessible only by the contract owner. - `unLock()`: This function is responsible for unlocking tokens according to the schedule defined in the contract. It iterates through the unlock schedule and transfers the unlocked tokens to the appropriate receiver address. It is a privileged function accessible only by the contract owner. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project.
HighInitial Token DistributionOpen
All of the `OnTact` tokens are sent to the contract deployer or one or several externally-owned account (EOA) addresses. This is a centralization risk because the deployer or the owner(s) of the EOAs can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (8)
- https://github.com/infomeapps/OnTact-Contract/erc20/OnTact.sol at commit cce2f62970b324705391ba1ffcb9b1570b42b270
- https://github.com/infomeapps/OnTact-Contract/mint/Context.sol at commit cce2f62970b324705391ba1ffcb9b1570b42b270
- https://github.com/infomeapps/OnTact-Contract/mint/Ownable.sol at commit cce2f62970b324705391ba1ffcb9b1570b42b270
- https://github.com/infomeapps/OnTact-Contract/erc20/Context.sol at commit cce2f62970b324705391ba1ffcb9b1570b42b270
- https://github.com/infomeapps/OnTact-Contract/mint/TokenLock.sol at commit cce2f62970b324705391ba1ffcb9b1570b42b270
- https://github.com/infomeapps/OnTact-Contract/mint/TokenLockConst.sol at commit cce2f62970b324705391ba1ffcb9b1570b42b270
- https://github.com/infomeapps/OnTact-Contract/erc20/draft-IERC6093.sol at commit cce2f62970b324705391ba1ffcb9b1570b42b270
- https://github.com/infomeapps/OnTact-Contract/erc20/ERC20.sol at commit cce2f62970b324705391ba1ffcb9b1570b42b270
Part of OnTact’s security record
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us