NFMart
CertiK reviewed NFMart on 18 Jun 2024: 3 findings, 0 critical; 1 marked fixed, 2 acknowledged.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings3
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 1 | 1 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 1 | 0 |
HighCentralization Risks in NFM.solFixed
In the contract `AdminRole` the role `_admin` has authority over the functions shown in the diagram below. 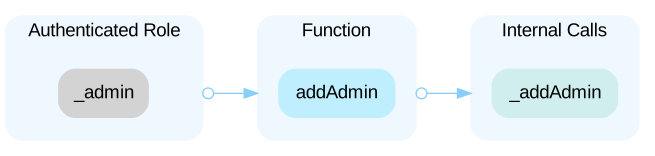 - `addAdmin(address account)`: Adds a new admin, only accessible by an admin role account. Any compromise to the `_admin` account may allow the hacker to take advantage of this authority and updated the sensitive settings and execute sensitive functionalities of the project. --- In the contract `AdminRole` the role `_owner` has authority over the functions shown in the diagram below. 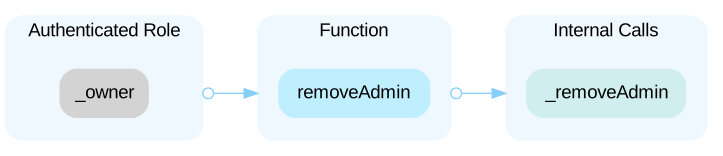 - `removeAdmin(address account)`: Removes an admin, only accessible by the owner role account. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and updated the sensitive settings and execute sensitive functionalities of the project. In the contract `NFM` the role `_admin` has authority over the functions shown in the diagram below. 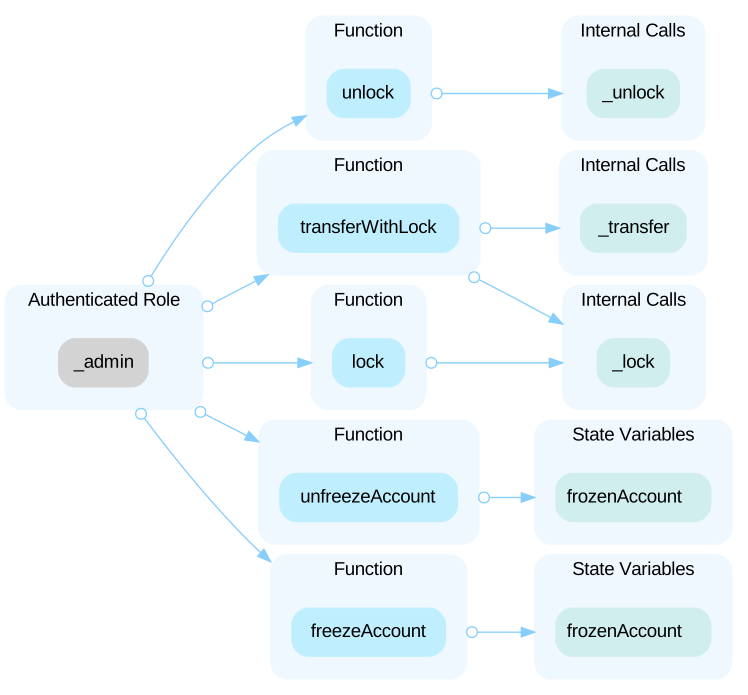 - `freezeAccount(address holder)`: Freezes the specified account, only accessible by an admin role account. - `unfreezeAccount(address holder)`: Unfreezes the specified account, only accessible by an admin role account. - `lock(address holder, uint256 value, uint256 releaseTime)`: Locks a specified amount of tokens until a certain time, only accessible by an admin role account. - `transferWithLock(address holder, uint256 value, uint256 releaseTime)`: Transfers tokens with a lock period, only accessible by an admin role account. - `unlock(address holder, uint256 idx)`: Unlocks a specific locked token, only accessible by an admin role account. Any compromise to the `_admin` account may allow the hacker to take advantage of this authority and updated the sensitive settings and execute sensitive functionalities of the project. --- In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. 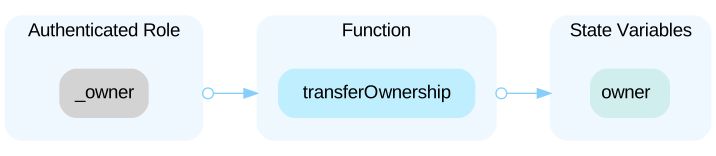 - `transferOwnership(address newOwner)`: Transfers ownership of the contract to a new owner, only accessible by the owner role account. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and updated the sensitive settings and execute sensitive functionalities of the project. --- In the contract `Pausable` the role `_admin` has authority over the functions shown in the diagram below. 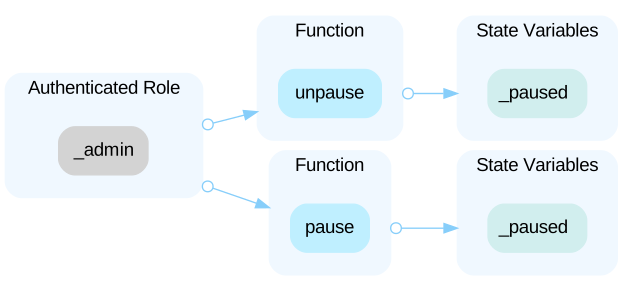 - `pause()`: Pauses the contract, only accessible by an admin role account. - `unpause()`: Unpauses the contract, only accessible by an admin role account. Any compromise to the `_admin` account may allow the hacker to take advantage of this authority and updated the sensitive settings and execute sensitive functionalities of the project.
Contracts in scope1
| Address | Chain | Source code |
|---|---|---|
| 0x9df03fba103491fffde4fbc5fea15efaa43c67a5 | Chain: Ethereum | Source code: Verified source |
Part of NFMart’s security record
 NFMart
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us