LFGswap
CertiK reviewed LFGSwap on 21 Oct 2022: 18 findings, 0 critical; none marked fixed.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings18
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 3 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 15 | 0 | 0 |
HighCentralization Risks in LfgSwapFactory.solOpen
In the contract `LfgSwapFactory` the role `feeToSetter` has authority over the functions shown in the diagram below. Any compromise to the `feeToSetter` account may allow the hacker to take advantage of this authority and set `feeTo`. 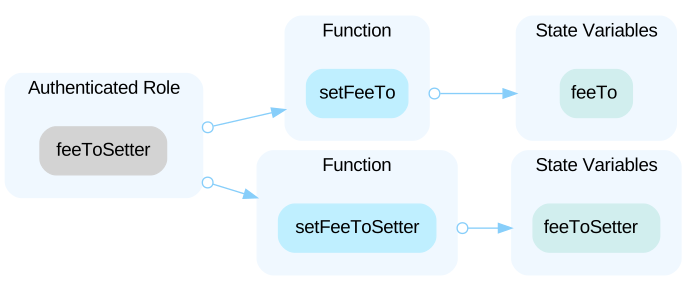
HighCentralization Risks in LfgToken.solOpen
In the contract `LfgToken` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and add or delete `Minter` role. 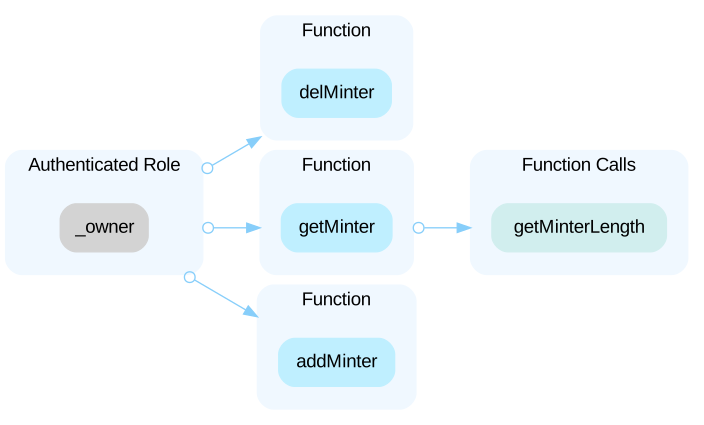 In the contract `LfgToken`, the role `_minters` has authority over the `mint()` function. Any compromise to the `_minters` account may allow a hacker to take advantage of this authority and mint new tokens.
HighInitial Token DistributionOpen
Tokens are sent to `msg.sender` when deploying the contract. This could be a centralization risk as the `msg.sender` can distribute tokens without obtaining the consensus of the community.
LowCommented Out CodeOpen
Commented out code is redundant.
LowDivide by ZeroOpen
The call to `burn()` function will fail if the value of `_totalSupply` is 0.
LowFunction Should Be Declared ExternalOpen
The functions which are never called internally within the contract should have external visibility for gas optimization.
LowIncorrect CommentOpen
Based on the coefficient `mul(2)` and based on the formula at 2.4 of https://uniswap.org/whitepaper.pdf, the correct fee is equivalent to 1/3th.
LowMissing Input ValidationOpen
In function `_burn()`, `_approve()` and `_transfer()`, addresses should be checked before assigning to make sure they are not zero addresses.
LowMissing Zero Address ValidationOpen
Addresses should be checked before assignment or external call to make sure they are not zero addresses.
LowPotential Integer UnderflowOpen
In the function `LfgToken.getMinter()`, the input `_index` is checked to ensure the index is valid. However, it is possible that `getMinterLength() == 0` which might lead to integer underflow in the calculation: ```solidity=43 require(_index <= getMinterLength() - 1, "JfToken: index out of bounds"); ```
Show 8 more
LowRedundant CheckOpen
In the `swap` function, the `require(amount0Out > 0 || amount1Out > 0, 'LfgSwap: INSUFFICIENT_OUTPUT_AMOUNT');` will always be satisfied due to the condition `if( amount0Out > 0 || amount1Out > 0 )`.
LowRedundant Interfaces `IMigrator` and `ISwapMiningOpen
The `IMigrator` and `ISwapMining` interfaces are not used by other code.
LowTypo in File Name `SafaMath.sol`Open
There is a typo in the file name `SafaMath.sol`.
LowTypos in `require()` Check Error MessagesOpen
There is a typos in `require` messages: - `UniswapV2Library` expected `LfgSwapLibrary`; - `UniswapV2` expected `LfgSwap`. - `JfToken` expected `LfgToken`
LowUnused Import FileOpen
The following import file is not used in the audit files: ````Solidity=3 import "@openzeppelin/contracts/access/Ownable.sol"; ````
LowUnused Library `FixedPoint`Open
The library `FixedPoint` is never used within the project and thus can be removed.
LowUser-Defined GettersOpen
The linked functions are equivalent to the compiler-generated getter functions for the respective variables.
LowVariables That Could Be Declared as ImmutableOpen
The linked variables assigned in the constructor can be declared as `immutable`. Immutable state variables can be assigned during contract creation but will remain constant throughout the lifetime of a deployed contract. A big advantage of immutable variables is that reading them is significantly cheaper than reading from regular state variables since they will not be stored in storage.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (16)
- contracts/libraries/SafaMath.sol
- contracts/core/LfgSwapPair.sol
- contracts/libraries/FixedPoint.sol
- contracts/libraries/LfgSwapLibrary.sol
- contracts/core/LfgSwapFactory.sol
- contracts/interface/ILfgSwapPair.sol
- contracts/libraries/TransferHelper.sol
- contracts/LfgToken.sol
- contracts/interface/ILfgSwapRouter.sol
- contracts/interface/IERC20LfgSwap.sol
- contracts/libraries/UQ112x112.sol
- contracts/interface/ISwapMining.sol
- contracts/interface/ILfgSwapFactory.sol
- contracts/interface/IWETH.sol
- contracts/core/LfgSwapRouter.sol
- contracts/interface/ILfgToken.sol
Part of LFGSwap’s security record
 LFGSwap
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us