A3S protocol
CertiK reviewed A3S Protocol on 2 Sep 2022: 12 findings, 0 critical; all acknowledged, none fixed.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings12
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 3 | 0 |
| Medium | 0 | 1 | 0 |
| Low | 0 | 8 | 0 |
HighCentralization Risks in A3SWalletFactory.solAcknowledged
In the contract `A3SWalletFactory` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. - function `updateBaseMetaURI()`, to update the NFT base URI. - function `updateWhilelistAddress()`, to update the whitelist validation contract. - function `updateFee()`, to update the NFT mint fees. - function `withdrawEther()`, to withdraw ether from this contract. - function `withdrawToken()`, to withdraw `fiatToken` ERC20 tokens from this contract. - function `UUPSUpgradeable.upgradeTo()`, to upgrade this contract to a new contract. - function `UUPSUpgradeable.upgradeToAndCall()`, to upgrade this contract to a new contract and call a function of the new contract. 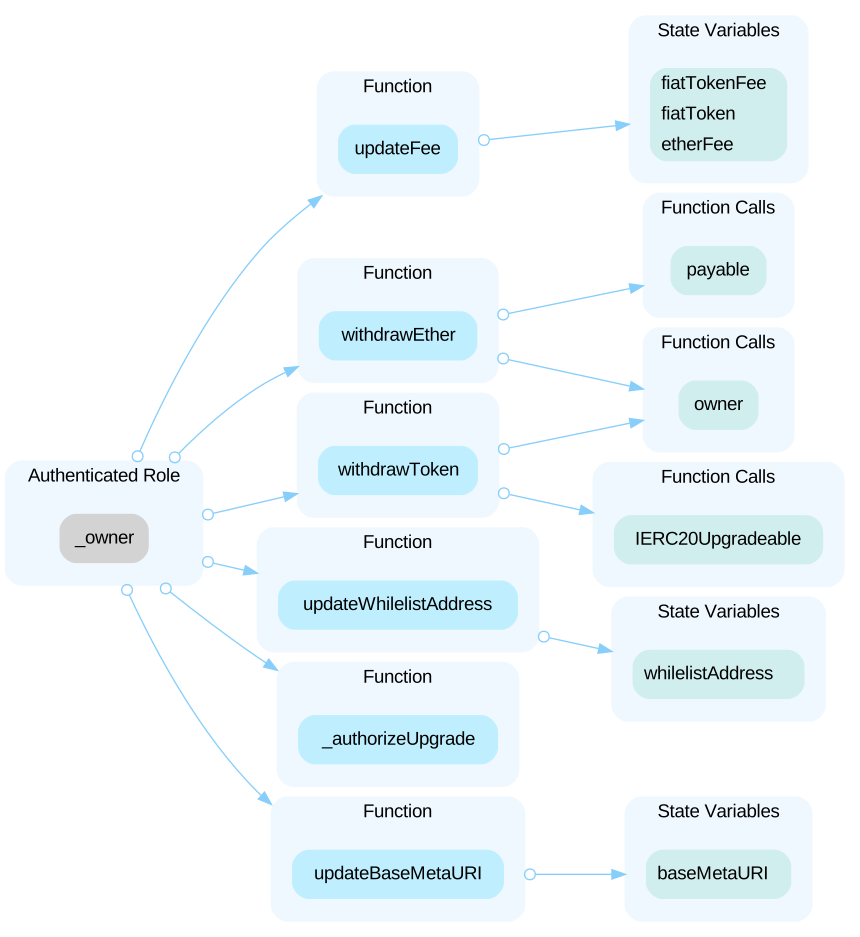
HighCentralization Risks in MerkleWhitelist.solAcknowledged
In the contract `MerkleWhitelist` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. - function `updateExecutor()`, to update the `executor` address, which has permission to update the Merkle root hash. - function `updateRootHash()`, to update the Merkle root hash and change the whitelist user list. - function `updateFactory()`, to update the `factory` contract address, which has permission to call the `claimWhitelist()` function. - function `updateRound()`, to increase round. If the NFT minting is limited, the whitelisted users can mint one NFT in a new round. - function `updateIsLimited()`, to enable/disable limited NFT minting. 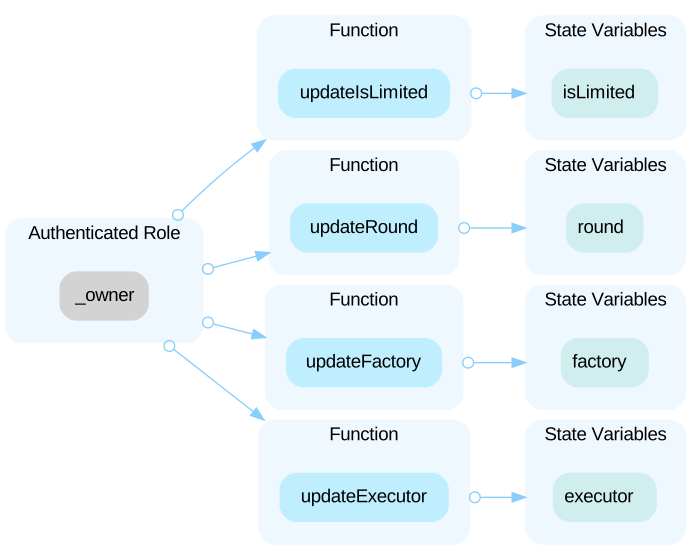 In the contract `MerkleWhitelist` the role `executor` has authority over the functions shown in the diagram below. Any compromise to the `executor` account may allow the hacker to take advantage of this authority. - function `updateRootHash()`, to update the Merkle root hash and change the whitelist user list. 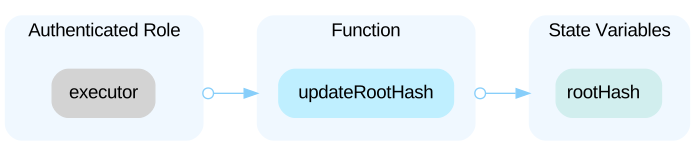 In the contract `MerkleWhitelist` the role `factory` has authority over the functions shown in the diagram below. Any compromise to the `factory` account may allow the hacker to take advantage of this authority. - function `claimWhitelist()`. The `factory` contract will call this function to check if the user has permission to mint NFT. 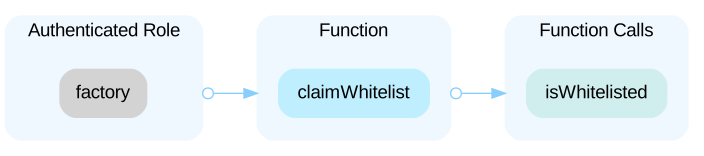
HighCentralized Control of Contract UpgradeAcknowledged
`A3SWalletFactory` is an upgradeable contract, the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, he can change the implementation of the contract and drain tokens from the contract.
MediumIncorrect Mintable Status If `round` is ZeroAcknowledged
If `isLimited` is true, the `owner` is on the whitelist, and `round` is zero, the mintable status will be 1. In this case, the user can not mint NFT in the zero round, so the mintable status should be zero. ```solidity=57 if (isLimited) { if (isWhitelisted(owner, proof)) { if (claimedWhitelist[owner] == round) { status = 1; } else { status = 2; } } } else { status = 3; } ```
LowImproper Usage of `public` and `external` TypeAcknowledged
`public` functions that are never called by the contract could be declared as `external`. `external` functions are more efficient than `public` functions.
LowMissing Emit EventsAcknowledged
There should always be events emitted in the sensitive functions that are controlled by centralization roles.
LowMissing Zero Address ValidationAcknowledged
Addresses should be checked before assignment or external call to make sure they are not zero addresses. ```solidity=28 factory = factoryAddress; ``` - `factoryAddress` is not zero-checked before being used. --- ```solidity=41 (bool success, bytes memory returnData) = payable( address(contractAddress) ).call{value: amount}(payload); ``` - `contractAddress` is not zero-checked before being used. --- ```solidity=133 whilelistAddress = whitelistContract; ``` - `whitelistContract` is not zero-checked before being used. --- ```solidity=144 fiatToken = token; ``` - `token` is not zero-checked before being used. --- ```solidity=27 executor = executorAddress; ``` - `executorAddress` is not zero-checked before being used. --- ```solidity=39 factory = factoryAddress; ``` - `factoryAddress` is not zero-checked before being used.
LowPotential Timeout in `walletListOwnerOf()` FunctiAcknowledged
Nodes process view function call locally, and each node may limit the execution time. If the value of `tokenIdCounter` is very large, the call to view function `walletListOwnerOf()` takes too long and may fail. ```solidity=218 for (; id <= tokenIdCounter.current(); id++) { if (ownerOf(id) == owner) { results[count] = walletOf(id); count++; } } ```
LowShadowing Local VariableAcknowledged
A local variable is shadowing another component defined elsewhere. ```solidity=50 function isMintable(address owner, bytes32[] calldata proof) ``` - Local variable `owner` in `MerkleWhitelist.isMintable` shadows the function `owner` in `Ownable`. --- ```solidity=72 function isWhitelisted(address owner, bytes32[] calldata proof) ``` - Local variable `owner` in `MerkleWhitelist.isWhitelisted` shadows the function `owner` in `Ownable`. --- ```solidity=81 function claimWhitelist(address owner, bytes32[] calldata proof) external { ``` - Local variable `owner` in `MerkleWhitelist.claimWhitelist` shadows the function `owner` in `Ownable`.
LowThird Party DependencyAcknowledged
The contract is serving as the underlying entity to interact with one or more third-party protocols. The scope of the audit treats third-party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. ```solidity=37 address public fiatToken; ``` - The contract `A3SWalletFactory` interacts with third party contract with `IERC20Upgradeable` interface via `fiatToken`.
Show 2 more
LowUnchecked ERC-20 `transfer()`/`transferFrom()` CaAcknowledged
The return value of the transfer()/transferFrom() call is not checked. ```solidity=77 IERC20Upgradeable(fiatToken).transferFrom( msg.sender, address(this), fiatTokenFee ); ``` --- ```solidity=165 IERC20Upgradeable(fiatToken).transfer(owner(), amount); ```
LowUnused EventAcknowledged
```solidity=17 event GeneralCall(address indexed contractAddress, bytes indexed payload); ``` - `GeneralCall` is declared in `A3SWallet` but never emitted.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (6)
- contracts/libraries/A3SWalletHelper.sol
- contracts/MerkleWhitelist.sol
- contracts/A3SWallet.sol
- contracts/IA3SWalletFactory.sol
- contracts/A3SWalletFactory.sol
- contracts/IMerkleWhitelist.sol
Part of A3S Protocol’s security record
 A3S Protocol
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us