Wemix WonderStaking - Retainer 31
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix WonderStaking - Retainer 31) on 16 Jun 2023: 22 findings, 1 critical; 17 marked fixed, 5 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings22
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 1 |
| High | 3 | 0 | 0 |
| Medium | 1 | 0 | 3 |
| Low | 1 | 0 | 13 |
HighCentralization Risks in NCPStaking.solOpen
In the contract `NCPStaking` the role `_ncp` has authority over the functions shown in the diagram below. Any compromise to the `_ncp` account may allow the hacker to take advantage of this authority and can change `_feeCollector`, `_rewarder` and `feeRatio`. 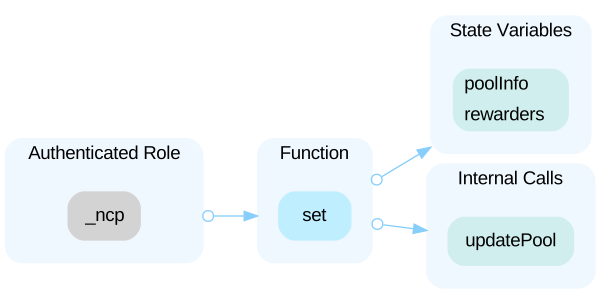 In the contract `NCPStaking` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and can call multiple functions such as `setPlatformFeeRatio`, `setWithdrawalNFT` , `add` and so on. The hacker can set the fee ratio to 100% or overwrite an exist pools to reset all user rewards. And also, In the contract `NCPStaking`, there are no upper boundaries for the `setUnbondTime` and `setRewardFeeRationRequestDelay` functions. It is possible to set the `unBondTime` and `_feeRationRequestDelay` up to any arbitrary amount. 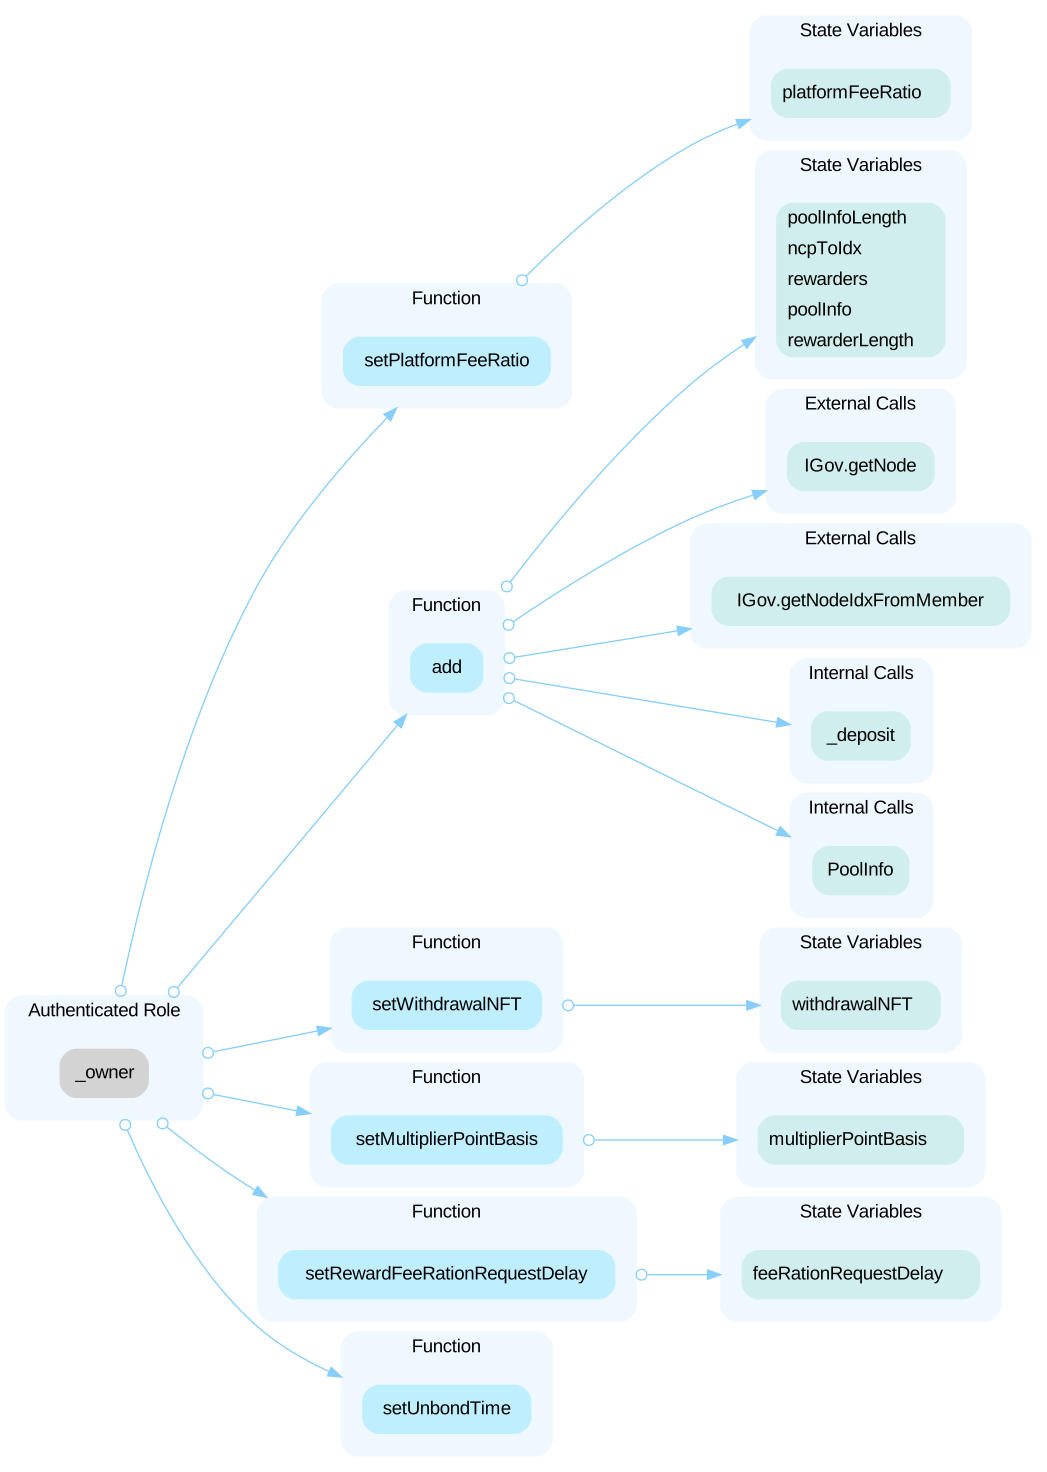 In the contract `NCPStaking` the role `_rewarderowner` has authority over the functions shown in the diagram below. Any compromise to the `_rewarderowner` account may allow the hacker to take advantage of this authority and can change `rewardFeeRatio`. 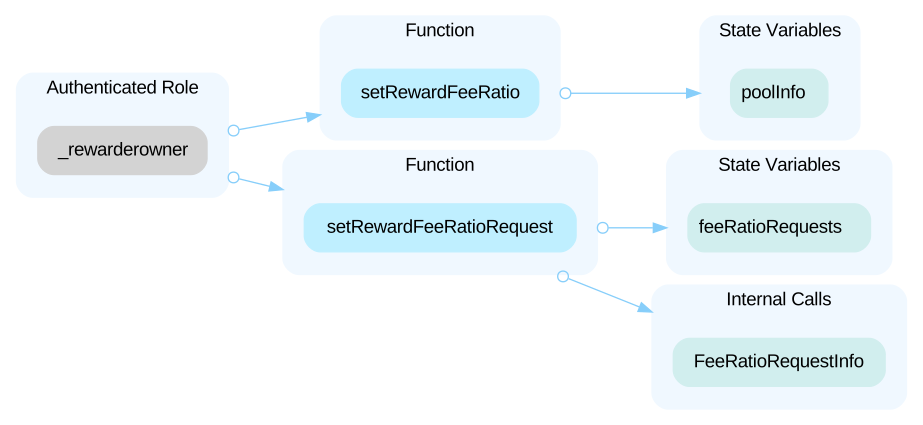
HighCentralization Risks in Rewarder.solOpen
In the contract `Rewarder`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and can withdraw all funds from the contract by calling `emergencyExit` function. **In this case user rewards in `NCPStaking` will be lost.** 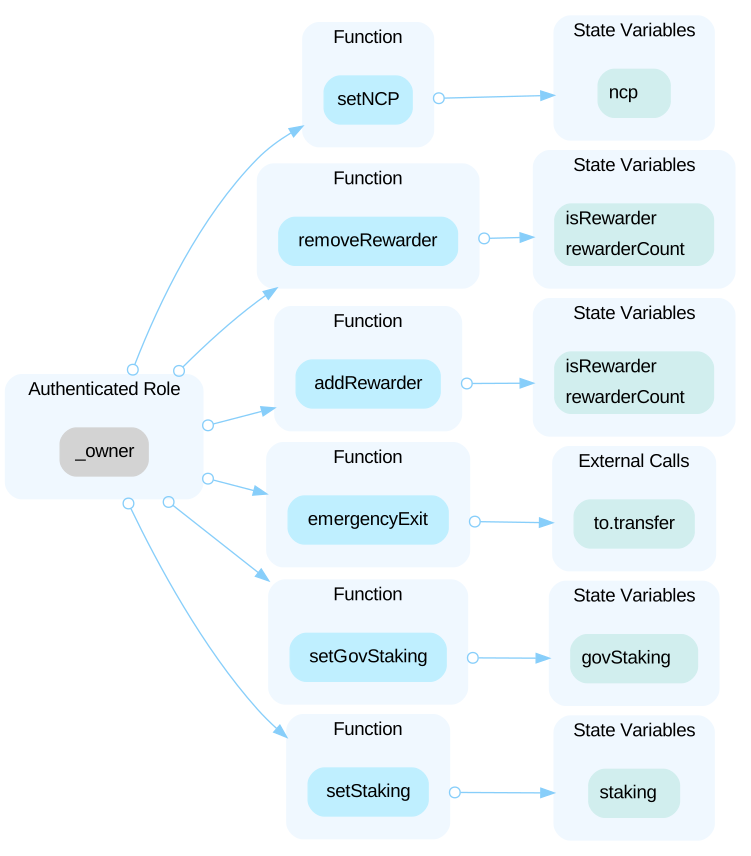
HighCentralized Control of Contract UpgradeOpen
`NCPStaking`, `Rewarder`, `NCPStakingGateway`, and `WithdrawalNFT` are upgradeable contracts, the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, he can change the implementation of the contract and drain tokens from the contract.
MediumFunction `_deposit` allows user to claim reward oOpen
In the current implementation of the `_deposit(pid, amount, to, claimReward)` function, `_harvest` is invoked for the destination account ("to" parameter), leading to the disbursement of pending rewards to that account. ```solidity=871 if (user.amount > 0) { _harvest(pid, to, to, claimReward, true); // console.log("after harvest",pool.activatedMP); } ``` This raises a potential security issue in a situation where, for example, User A executes `deposit()` with the destination account set as User B and the `claimReward` parameter set to `True`. In this case, the reward associated with User B would be claimed and transferred to User B, but this process takes place without requiring explicit authorization from User B. This could potentially allow User A to interfere with User B's rewards under certain circumstances.
LowTrack of `userTokenIdList[address(0)]` will increOpen
In the current implementation of `WithdrawalNFT.sol`, `userTokenIdList[address(0)]` will also be tracked. Every time of NFT mint/burn will iterate through the `userTokenIdList[address(0)]`, which is unnecessary and will increase gas consumption of the execution. ```solidity=49 function _beforeTokenTransfer( address from, address to, uint256 firstTokenId, uint256 batchSize ) internal override { require(batchSize == 1, "WithdrawalNFT: batch size must be 1"); super._beforeTokenTransfer(from, to, firstTokenId, batchSize); bool flag = false; for(uint256 i = 0;i<userTokenIdList[from].length;i++){ if(userTokenIdList[from][i] == firstTokenId){ flag = true; for(uint256 j = i;j<userTokenIdList[from].length-1;j++){ userTokenIdList[from][j] = userTokenIdList[from][j+1]; } userTokenIdList[from].pop(); break; } } } function _afterTokenTransfer( address from, address to, uint256 firstTokenId, uint256 batchSize ) internal override { require(batchSize == 1, "WithdrawalNFT: batch size must be 1"); super._afterTokenTransfer(from, to, firstTokenId, batchSize); userTokenIdList[to].push(firstTokenId); } ```
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (4)
- contracts/gateway/NCPStakingGateway.sol
- contracts/NCPStaking.sol
- contracts/Rewarder.sol
- contracts/withdrawalToken/WithdrawalNFT.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us