Xdoge
CertiK reviewed Xdoge on 8 Apr 2024: 4 findings, 0 critical; 2 acknowledged, 2 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings4
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 2 | 0 |
HighCentralization Risks in TradeX.solOpen
In the contract `TradeX` - the role `DEPLOYER_ROLE` has the authority to upgrade all facets and initialize them. - the role `DEFAULT_ADMIN_ROLE` has the authority to edit other roles. - other roles can perform sensitive operations. Any compromise to the privileged roles may allow the hacker to take advantage of this and - upgrade any facet with new functionality - add/remove pairs/brokers/commissions, etc. - update staking reward via `updateTokenPerBlock()` - provide any prices and execute the orders
HighCentralization Risks in TradeXLP.solOpen
In the contract `TradeXLP` the role `ADMIN_ROLE` has authority over the functions shown in the diagram below. 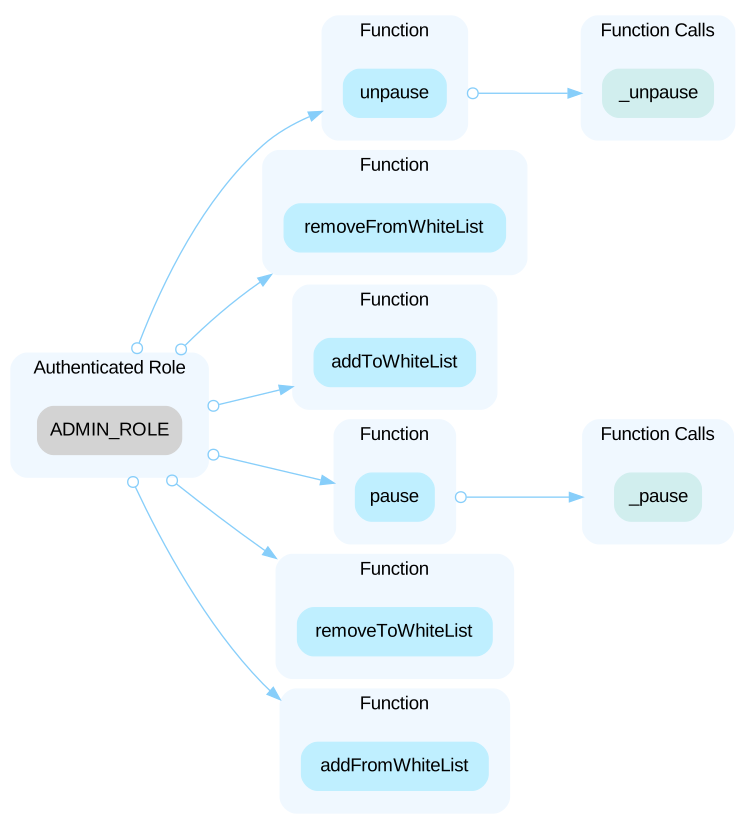 In the contract `TradeXLP` the role `MINTER_ROLE` has authority over the functions shown in the diagram below. 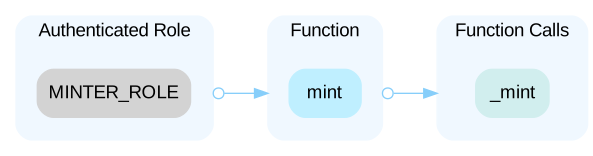 In the contract `TradeXLP` the role `UPGRADER_ROLE` has authority over the functions shown in the diagram below. 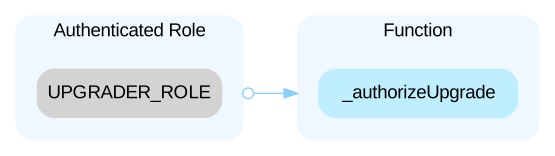 Any compromise to the privileged roles may allow the hacker to take advantage of this and - `mint()` any amount of `TradeXLP` - `upgradeTo()` any other implementation contract - `pause()`/`unpause()`, update whitelists
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (83)
- contracts/diamond/libraries/LibVault.sol
- contracts/diamond/facets/VaultFacet.sol
- contracts/dependencies/IWETH.sol
- contracts/diamond/interfaces/IPriceFacade.sol
- contracts/diamond/libraries/LibTokenReward.sol
- contracts/utils/Constants.sol
- contracts/diamond/facets/TradingCloseFacet.sol
- contracts/diamond/libraries/LibLpManager.sol
- contracts/diamond/security/OnlySelf.sol
- contracts/diamond/interfaces/ITradingPortal.sol
- contracts/diamond/interfaces/ITradingChecker.sol
- contracts/diamond/libraries/LibStakeReward.sol
- contracts/diamond/interfaces/ITimeLock.sol
- contracts/diamond/interfaces/ITradingClose.sol
- contracts/test/MockTrademanInit.sol
- contracts/diamond/libraries/LibOrderAndTradeHistory.sol
- contracts/utils/Bits.sol
- contracts/diamond/upgradeInitializers/TrademanInit.sol
- contracts/diamond/interfaces/IStakeReward.sol
- contracts/diamond/facets/StakeRewardFacet.sol
- contracts/diamond/interfaces/IDiamondCut.sol
- contracts/diamond/interfaces/IPausable.sol
- contracts/diamond/interfaces/IOraclePrice.sol
- contracts/diamond/libraries/LibChainlinkPrice.sol
- contracts/diamond/interfaces/IArbSys.sol
- contracts/diamond/interfaces/ITradingConfig.sol
- contracts/diamond/facets/LimitOrderFacet.sol
- contracts/diamond/libraries/LibPriceFacade.sol
- contracts/diamond/facets/TradingOpenFacet.sol
- contracts/diamond/facets/BrokerManagerFacet.sol
- contracts/diamond/facets/DiamondCutFacet.sol
- contracts/diamond/facets/TransitionFacet.sol
- contracts/diamond/interfaces/ITrading.sol
- contracts/test/MockTrademanWETH9.sol
- contracts/diamond/security/ReentrancyGuard.sol
- contracts/diamond/libraries/LibDiamond.sol
- contracts/diamond/facets/DiamondLoupeFacet.sol
- contracts/diamond/interfaces/ITokenReward.sol
- contracts/diamond/interfaces/IFeeManager.sol
- contracts/diamond/facets/OrderAndTradeHistoryFacet.sol
- contracts/diamond/interfaces/ITradingOpen.sol
- contracts/diamond/libraries/LibChain.sol
- contracts/diamond/facets/TokenRewardFacet.sol
- contracts/diamond/facets/AccessControlEnumerableFacet.sol
- contracts/diamond/interfaces/IPairsManager.sol
- contracts/diamond/interfaces/IBook.sol
- contracts/diamond/facets/PairsManagerFacet.sol
- contracts/diamond/interfaces/IOrderAndTradeHistory.sol
- contracts/diamond/interfaces/IVault.sol
- contracts/diamond/interfaces/ITradingReader.sol
- contracts/diamond/interfaces/ITradingCore.sol
- contracts/diamond/interfaces/ILp.sol
- contracts/diamond/libraries/LibTradingConfig.sol
- contracts/diamond/facets/TradingPortalFacet.sol
- contracts/diamond/facets/TimeLockFacet.sol
- contracts/diamond/interfaces/ILpManager.sol
- contracts/diamond/facets/TradingConfigFacet.sol
- contracts/diamond/facets/TradingReaderFacet.sol
- contracts/diamond/facets/ChainlinkPriceFacet.sol
- contracts/diamond/libraries/LibBrokerManager.sol
- contracts/test/MockTrademanAggregator.sol
- contracts/diamond/interfaces/ILimitOrder.sol
- contracts/diamond/libraries/LibTrading.sol
- contracts/diamond/TradeX.sol
- contracts/test/MockTrademanERC20.sol
- contracts/diamond/interfaces/IChainlinkPrice.sol
- contracts/diamond/facets/TradingCheckerFacet.sol
- contracts/diamond/interfaces/IDiamondLoupe.sol
- contracts/diamond/security/Pausable.sol
- contracts/TradeXLP.sol
- contracts/diamond/libraries/LibLimitOrder.sol
- contracts/diamond/libraries/LibPairsManager.sol
- contracts/diamond/libraries/LibTimeLock.sol
- contracts/test/MockDiamondCutFacet.sol
- contracts/diamond/facets/TradingCoreFacet.sol
- contracts/diamond/libraries/LibTradingCore.sol
- contracts/diamond/facets/PriceFacadeFacet.sol
- contracts/diamond/interfaces/IBrokerManager.sol
- contracts/diamond/libraries/LibAccessControlEnumerable.sol
- contracts/diamond/facets/LpManagerFacet.sol
- contracts/diamond/facets/FeeManagerFacet.sol
- contracts/diamond/facets/PausableFacet.sol
- contracts/diamond/libraries/LibFeeManager.sol
Part of Xdoge’s security record
 Xdoge
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us