
AGG security record
As of 14 Oct 2026, AGG has 1 audit report on Trustblock, by CertiK, dated 6 Dec 2023. That report lists no open critical findings.
Record last updated . It holds audits and findings, contracts and incidents up to Oct 2026. Statuses are the security firms’ own. Trustblock does not review code.
Audits1
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| AGG - Audit | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
Findings2
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 0 | 0 |
HighCentralization Related RisksAGG - Audit · CertiK · 6 Dec 2023Not fixed
In the contract `AccessControl` the role `adminRole` has authority over the following functions: - grantRole() - revokeRole() Any compromise to the `adminRole` account may allow the hacker to take advantage of this authority and grant associated role to any account or revoke the role from any account. Note that `DEFAULT_ADMIN_ROLE` is the admin role for all roles. ----------- In the contract `AccessControl` the role `role` has authority over the following function: - renounceRole() Any compromise to the `role` account may allow the hacker to take advantage of this authority and renounce corresponding privileges to functions within other contracts. --- In the contract `AGGToken` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and pause/unpause token transfers. 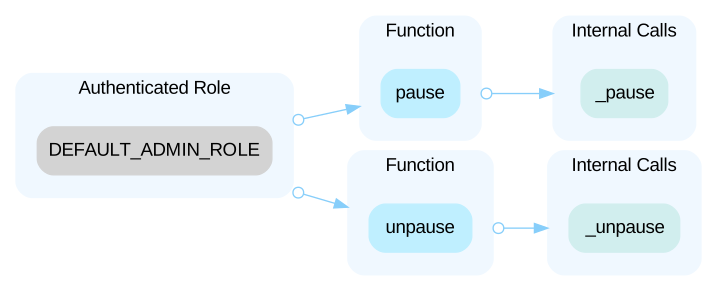 --- In the contract `AGGToken` the role `BURNER_ROLE` has authority over the function shown in the diagram below. Any compromise to the `BURNER_ROLE` account may allow the hacker to take advantage of this authority and burn tokens from the role's account. 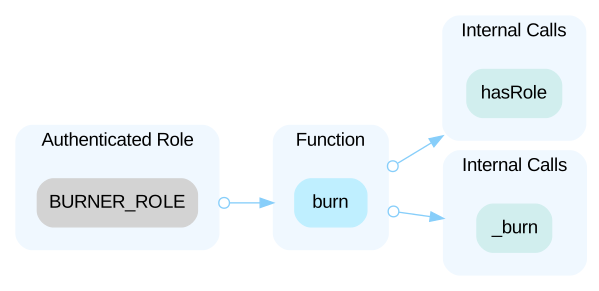 --- In the contract `AGGToken` the role `MINTER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this authority and mint tokens. ----- In the contract `Ownable` the role `owners` has authority over the functions shown in the diagram below. Any compromise to the `owners` account may allow the hacker to take advantage of this authority and add/remove owners. 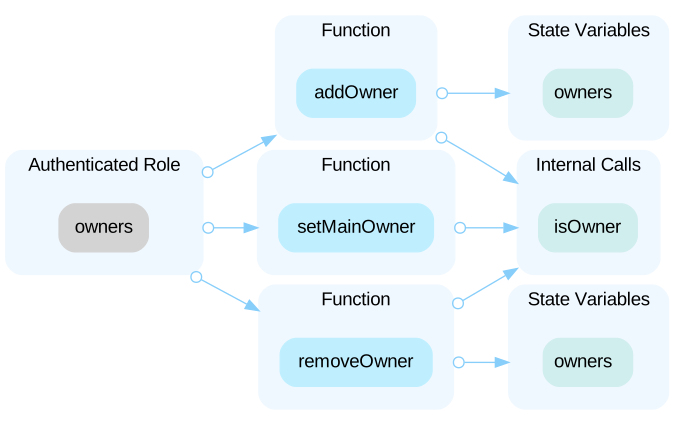 ----- In the contract `TimeLock` the role `owners` has authority over the functions shown in the diagram below. Any compromise to the `owners` account may allow the hacker to take advantage of this authority and update the `timeLock` variable. 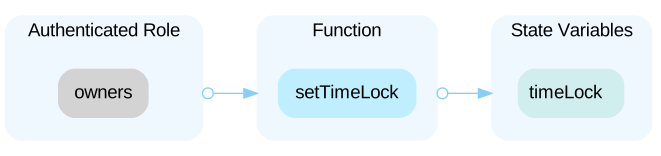
Open the reportHighCentralized Token Holding Position RiskAGG - Audit · CertiK · 6 Dec 2023Not fixed
On Dec 5, 2023, the address 0x26B4ECac28D8fD0cc4B3d31eF08d871A6e439743 holds all the AGG tokens. This is a centralization risk because the address can distribute tokens without obtaining the consensus of the community. Any compromise to the address may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="agg"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us