
Api3 security record
As of 30 Oct 2026, Api3 has 3 audit reports by 2 security firms on Trustblock; the latest is by Quantstamp, dated 24 Jun 2025. Those reports list no open critical findings.
Record last updated . It holds audits and findings, contracts and incidents up to Oct 2026. Trustblock does not review code.
Audits3
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| API3 - Data Feed Proxy Combinators | Security firm: Quantstamp | Date: | Scope: Files named in the report | No open critical findings | Open · certificate.quantstamp.com |
| API3Market | Security firm: Quantstamp | Date: | Scope: Files named in the report | No open critical findings | Open · certificate.quantstamp.com |
| API3 - audit | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
Findings17
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 1 | 0 |
| Medium | 0 | 5 | 0 |
| Low | 0 | 10 | 1 |
HighCentralization Risks in StakeableVesting.solAPI3 - audit · CertiK · 7 Feb 2023Acknowledged
In the contract `StakeableVesting` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify critical configurations of the contract. 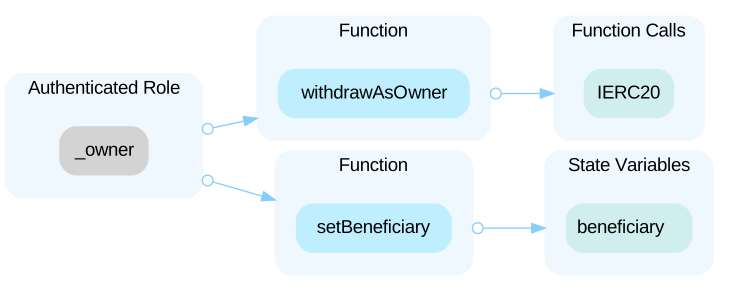 In the contract `StakeableVesting` the role `beneficiary` has authority over the functions shown in the diagram below. Any compromise to the `beneficiary` account may allow the hacker to take advantage of this authority and withdraw assets from the contract. 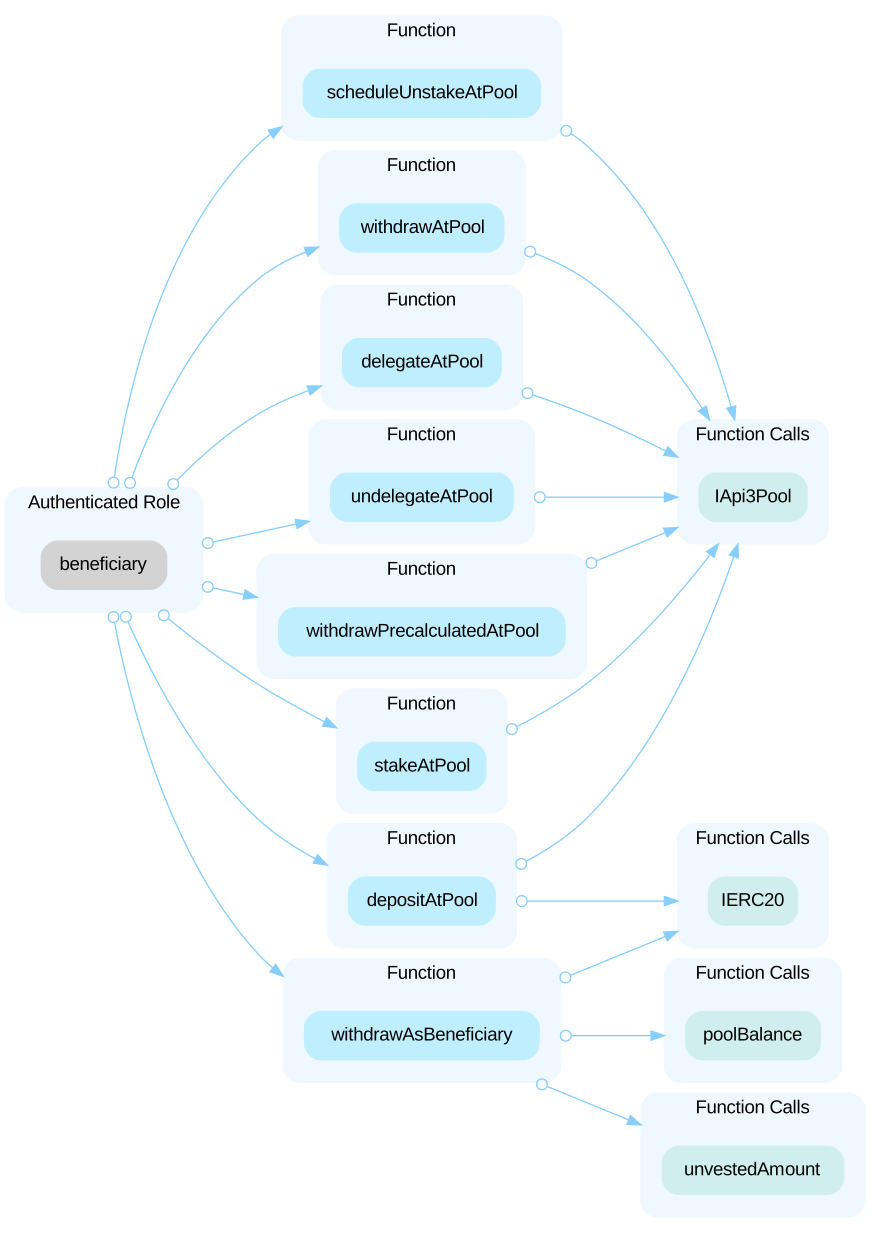
Open the reportMediumAggregation of Stale Price Feed(s)API3 - Data Feed Proxy Combinators · Quantstamp · 24 Jun 2025Acknowledged
The `ProductApi3ReaderProxyV1` returns the product of possibly stale data feed sources. It returns `block.timestamp` as the timestamp for the new value, masking the age of the underlying data feeds. A consuming protocol utilizing this wrapper cannot apply their freshness policy to the returned price, leading to outdated prices and creating an opportunity for attackers. This could lead to protocols unintentionally accepting stale price data and attackers exploiting those protocols.
Open the reportMediumSilent Truncation on `int224` Cast without Bounds ChecksAPI3 - Data Feed Proxy Combinators · Quantstamp · 24 Jun 2025Acknowledged
Multiple contracts perform unchecked casts from `int256` to `int224`, which can silently truncate values exceeding the `int224` range, leading to incorrect and misleading outputs. Solidity does not revert on narrowing conversions, so these casts may discard high-order bits without warning: - `ProductApi3ReaderProxyV1.read()`: Multiplies two proxy values and divides by 1e18 before casting to `int224` without checking bounds, risking overflow and silent truncation. - `NormalizedApi3ReaderProxyV1.read()`: Scales a Chainlink feed value (up or down) and casts to `int224` without verifying that the result fits within range. - `InverseApi3ReaderProxyV1.read()`: Inverts a proxy value using 1e36 divided by the feed value, then casts to `int224`, with a misleading comment implying a revert on overflow.
Open the reportMediumAttacker Can DoS Queue with Low-Quality SubscriptionsAPI3Market · Quantstamp · 27 Feb 2024Acknowledged
The subscription queues have a maximum size of 5 subscriptions. As long as the new subscription is equal to or better than at least one subscription in the queue, it will added. If it is equal, it must have an `endTimestamp` further in the future. However, if the queue is full and someone wants to queue a subscription that is better than all of them but has a lower `endTimestamp`, that subscription will fail to be added with error "Subscription queue full". Therefore, an attacker could fill the queue with the lowest-quality subscriptions and prevent better subscriptions from being added. However, this requires that more unique update parameters exist in the Merkle tree for a given dAPI name than the maximum allowed in the queue. The API3 team has confirmed that more than five possible update parameter configurations should not exist in the Merkle tree. Since the number of approved update parameter configurations, however, cannot be verified on-chain, this issue remains possible.
Open the reportMediumReliance on Correctness of Merkle Tree ConstructionAPI3Market · Quantstamp · 27 Feb 2024Acknowledged
The smart contracts in scope rely on the correct off-chain construction of Merkle trees. The following constraints are not enforced on-chain upon Merkle root submission and, if ever accidentally or intentionally violated, could lead to security issues and/or inconsistencies: 1. The Management Merkle Tree cannot contain a specific dAPI name more than once. Otherwise, anyone can change the pointer of the dAPI name to the data feed ID. 2. A dAPI name in the management Merkle tree should not be re-pointed to a different data feed during an active subscription. This might violate the purchasing conditions of the subscriber. 3. All entries of the same dAPI name in the management Merkle tree must point to the same sponsor wallet.
Open the reportMediumSponsor Wallet Owner Needs to Be TrustedAPI3Market · Quantstamp · 27 Feb 2024Acknowledged
Purchasing a subscription will result in a payment to sponsor wallets that can be quite substantial (> 5 ETH). These funds should be used by Airseekers to pay for the gas fees of updates. However, the owner of the sponsor wallet needs to be trusted not to mistreat the funds. The only incentive that keeps them from draining those funds is reputation. Furthermore, compromised sponsor wallets will also prevent the continued operation of already purchased subscriptions unless the API3 team provides funds.
Open the reportLowPrecision Loss on Value DownscalingAPI3 - Data Feed Proxy Combinators · Quantstamp · 24 Jun 2025Acknowledged
The `ScaledApi3FeedProxyV1` wrapper allows to downscale any data feed to a lower number of decimals. This loss of precision may result in inaccurate pricing, which can potentially be exploited by an attacker. While it is the responsibility of the integrating protocol, downscaling precision may be a risk in general.
Open the reportLowSilent Underflow to ZeroAPI3 - Data Feed Proxy Combinators · Quantstamp · 24 Jun 2025Acknowledged
The current implementation of price inversion carries the marginal risk of underflowing to zero. In case the data feed value becomes larger than ` 1e36`, the inverted price will incorrectly return zero, enabling various exploits for protocol utilizing the price inversion mechanism. While this is highly unlikely for data feeds like ETH/USD (ETH would have to be worth one quintillon USD), it may occur for data feeds that, e.g., involve hyper-inflated asset or exotic asset pairs.
Open the reportLowAll Chains Must Be in Sync with Same StateAPI3Market · Quantstamp · 27 Feb 2024Acknowledged
The Merkle roots of management Merkle trees can be replayed across all chains. This is intended to reduce the signing overhead. However, if all chains are not synchronized in terms of data feed IDs, this could potentially result in invalid Merkle trees being activated and, consequently, incorrect data feed IDs being activated or transactions reverting because the data feed ID is not registered anymore. Furthermore, identical data feed IDs must be used across all chains.
Open the reportLowCritical Role Transfer Not Following Two-Step PatternAPI3Market · Quantstamp · 27 Feb 2024Acknowledged
The owner of the contracts can call `transferOwnership()` to transfer the ownership to a new address. If an uncontrollable address is accidentally provided as the new owner address then the contract will no longer have an active owner, and functions with the `onlyOwner` modifier can no longer be executed. This is only relevant if `HashRegistry.sol` is used as a standalone contract since ownership transfer is disallowed in `API3Market`.
Open the reportShow 6 more
LowGreedy Subscription PurchaseAPI3Market · Quantstamp · 27 Feb 2024Acknowledged
Users can deposit more funds than necessary to purchase subscriptions through `buySubscription()`. Although the API3 Front-end likely mitigates this, it should not be possible for a user to deposit exceptionally more than needed when buying a subscription. Particularly, if the sponsor wallet already has (almost) sufficient funds to cover subscriptions, the function shouldn't accept these excess funds.
Open the reportLowOut of Scope Contracts Being CalledAPI3Market · Quantstamp · 27 Feb 2024Acknowledged
In several instances, the `API3Market` contract calls functions in the `API3ServerV1 ` contract. However, the target contract is out of scope for this audit. While we checked the interdependencies, we trust that the `API3ServerV1` correctly handles all function calls. Particularly, we trust that necessary checks for external functions in `API3Market` are made in `API3ServerV1` to prevent unauthorized state changes, such as `Api3Market.updateBeaconWithSignedData()`.
Open the reportLowOwner Can Override SignersAPI3Market · Quantstamp · 27 Feb 2024Acknowledged
In `HashRegistry`, the owner can specify which signers are required to set the hash for a specific hash type. However, the owner can also set the hash for any hash type. This leads to a situation in which the owner's address has a disproportionate control when compared to the signers. For example, consider a scenario where the owner's address operates under a 4-of-8 multisig scheme, and there exists a specific hash type that requires authorization from 4 signers. In this case, the 4-of-8 multisig configuration is, in essence, less secure compared to a setup that directly uses a 4-of-4 multisig structure, which would be entirely made up of these signers. Additionally, the separation of roles may be violated in a case where the addresses responsible for updating a specific hash type are overruled by the owner address. Of course, the owner can also set the signers, so it needs to be the most secure.
Open the reportLowOwnership Can Be RenouncedAPI3Market · Quantstamp · 27 Feb 2024Acknowledged
If the `owner`renounces their ownership, all ownable contracts will be left without an owner. Consequently, any function guarded by the `onlyOwner` modifier will no longer be able to be executed. This is only relevant in case `HashRegistry.sol` is used as a standalone contract.
Open the reportLowPrivileged Roles and OwnershipAPI3Market · Quantstamp · 27 Feb 2024Acknowledged
The following are the smart contracts and their associated roles. Many of the smart contracts contain roles that are necessary for the correct operation of the system. Therefore, roles, such as the default admin role, should be held by a multi-sig wallet. 1. `Api3Market` 1. Has an `owner` but all privileged functions exist in the inherited `HashRegistry`. 2. `HashRegistry` 1. Is inherited by `Api3Market` and shares an `owner`. 2. The `owner` can set signers for specific hash types including removing or adding signers. 3. The `owner` can set hashes for hash types, including overriding hashes set by the signers. 4. The signers can use m-of-m signatures to set the hash for a hash type they are allowed to set. 5. The signers can also delegate their signature to any address including addresses that do not have an associated private key. This will effectively prevent the hash from being changed until the delegation expires or the owner removes them. This is equivalent to a signer choosing not to sign. 3. `AirseekerRegistry` 1. All of its state-changing functions can only be called by the owner except for `registerDataFeed()`. 2. It may be owned by `Api3Market` or exist as a standalone smart contract with a different owner. The `owner` privileges on `HashRegistry.sol`implies the following rights: 1. The `owner` can change the data feed ID(s) the dAPI name points to. 2. The sponsor wallet that will receive funds for a (dAPI name, data feed ID) tuple. 3. The accepted `updateParameters`, `duration`, and `price` of a dAPI name.
Open the reportLowOut of Scope DependencyAPI3 - audit · CertiK · 7 Feb 2023Acknowledged
The contract serves as the underlying entity to interact with one or more out-of-scope contracts. The scope of the audit treats out of scope contracts as black boxes, assumes their functional correctness, and the audited contracts interact with those contracts in a correct way. However, in the real world, those contracts might contain logic issues or security vulnerabilities, and this may lead to lost or stolen assets. ```solidity=29 address public immutable override api3Token; ``` - The contract `StakeableVesting` interacts with the out-of-scope contract with `IERC20` interface via `api3Token`. --- ```solidity=32 address public immutable api3Pool; ``` ```sol=243 staked = IApi3Pool(api3Pool).userStake(address(this)); ( unstaked, , , unstaking, unstakeScheduledFor, lastDelegationUpdateTimestamp, ) = IApi3Pool(api3Pool).getUser(address(this)); ``` ```sol=281 function poolBalance() private view returns (uint256) { uint256 staked = IApi3Pool(api3Pool).userStake(address(this)); (uint256 unstaked, , uint256 unstaking, , , , ) = IApi3Pool(api3Pool) .getUser(address(this)); return staked + unstaked + unstaking; } ``` - The contract `StakeableVesting` interacts with the out-of-scope contract with `IApi3Pool` interface via `api3Pool`. --- ```solidity=13 address public immutable override api3Token; ``` - The contract `StakeableVestingFactory` interacts with the out-of-scope contract with `IERC20` interface via `api3Token`.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="api3"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us