Avium Origins has 1 public audit report from CertiK; dated 24 Jan 2023; no critical findings reported.
Last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Statuses are the security firms’ own
15 findings are still open or acknowledged in the firms’ reports: 1 high, 14 low (all open).
Centralization Risks in Origins
Avium 1 - audit addendum · CertiK · 24 Jan 2023 · Report ↗
Declaration Naming Convention
Avium 1 - audit addendum · CertiK · 24 Jan 2023 · Report ↗
External Call Inside Loop
Avium 1 - audit addendum · CertiK · 24 Jan 2023 · Report ↗
Missing Emit Events
Avium 1 - audit addendum · CertiK · 24 Jan 2023 · Report ↗
Missing Zero Address Validation
Avium 1 - audit addendum · CertiK · 24 Jan 2023 · Report ↗
Redundant Code Components
Avium 1 - audit addendum · CertiK · 24 Jan 2023 · Report ↗
Shadowing Local Variable
Avium 1 - audit addendum · CertiK · 24 Jan 2023 · Report ↗
Uninitialized Local Variable
Avium 1 - audit addendum · CertiK · 24 Jan 2023 · Report ↗
Unlocked Compiler Version
Avium 1 - audit addendum · CertiK · 24 Jan 2023 · Report ↗
Unsafe Integer Cast
Avium 1 - audit addendum · CertiK · 24 Jan 2023 · Report ↗
Newest first
| Report | Security firm | Date | Scope | Critical findings | Findings | Source |
|---|---|---|---|---|---|---|
| Avium 1 - audit addendum | Security firm: CertiK | Date: | Scope: Files listed | None open | Findings: 1 high · 14 low 15 open | skynet.certik.com ↗ |
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 14 | 0 | 0 |
In the contract `Origins` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change different contract parameters, pause/unpause the contract and even withdraw all funds from it. 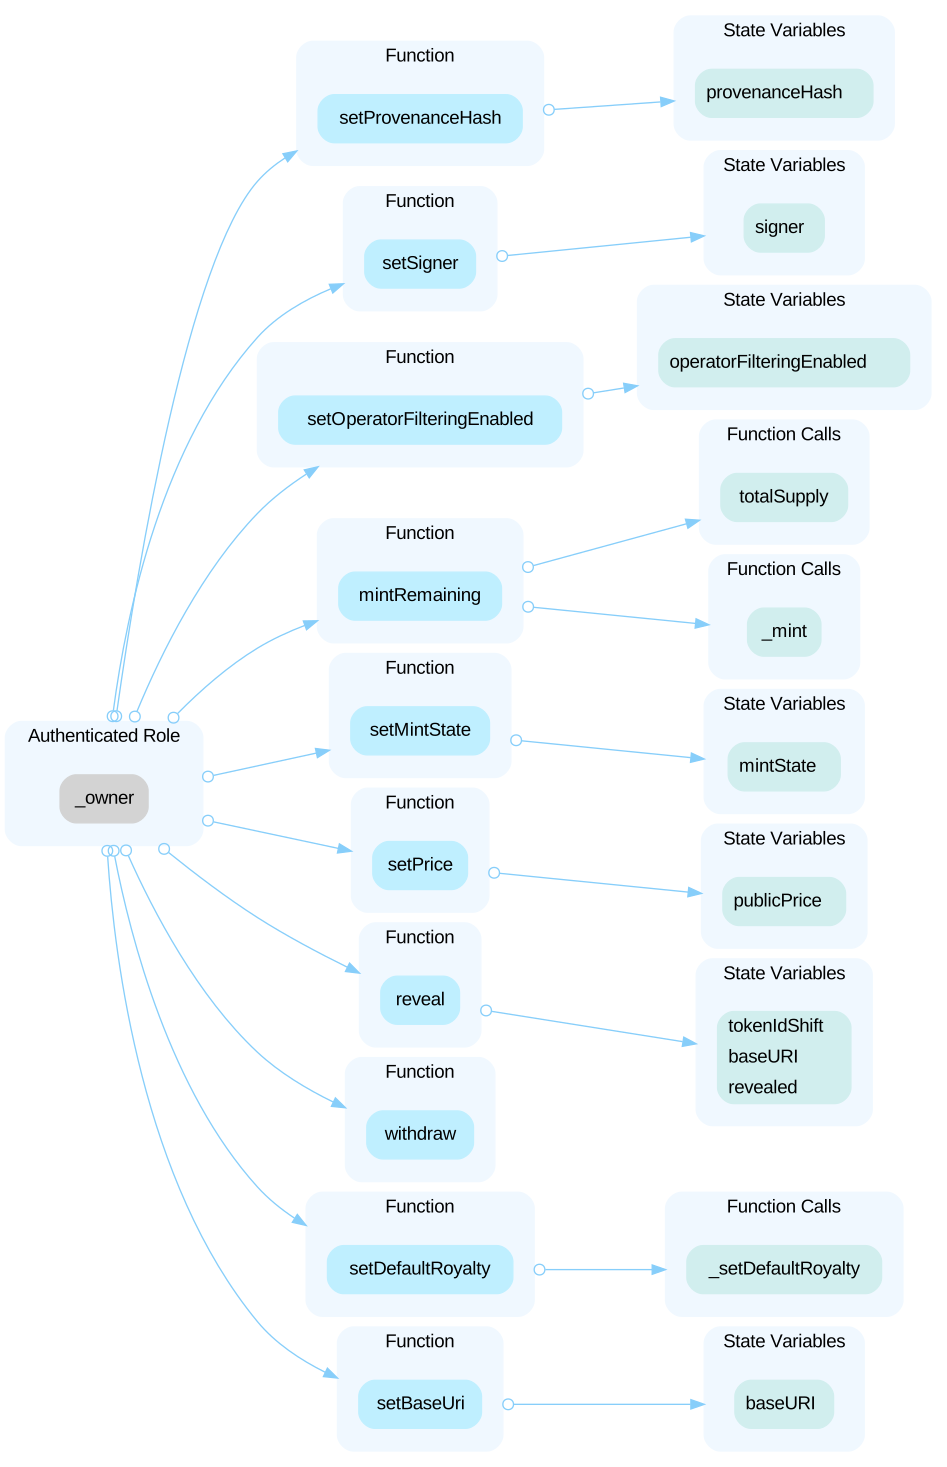
Open the reportOne declaration does not conform to the [Solidity style guide](https://solidity.readthedocs.io/en/v0.7.3/style-guide.html#naming-conventions) with regards to its naming convention. Particularly: - `camelCase`: Should be applied to function names, argument names, local and state variable names, modifiers - `UPPER_CASE`: Should be applied to `constant` variables - `CapWords`: Should be applied to contract names, struct names, event names and enums ```solidity=56 bytes32 private DOMAIN_SEPARATOR; ``` - Variable `DOMAIN_SEPARATOR` is not in `camelCase`.
Open the reportExternal calls are made inside a *for* loop. This might lead to a denial-of-service attack. If any of the calls fail, it will cause the entire loop to revert. ```solidity=21 erc721Contract.transferFrom(msg.sender, to[i], tokenIds[i][j]); ```
Open the reportThere should always be events emitted in the sensitive functions that are controlled by centralization roles.
Open the reportAddresses should be checked before assignment or external call to make sure they are not zero addresses. ```solidity=74 signer = signer_; ``` - `signer_` is not zero-checked before being used. --- ```solidity=247 to.transfer(address(this).balance); ``` - `to` is not zero-checked before being used.
Open the reportThe linked statements do not affect the functionality of the codebase and appear to be either leftovers from test code or older functionality.
Open the reportA local variable is shadowing another component defined elsewhere. ```solidity=68 address owner, ``` - Local variable `owner` in `Origins.constructor` shadows the function `owner` in `Ownable`.
Open the report```solidity=18 for (uint256 i; i < length; ) { ``` - Local variable `i` is never initialized. --- ```solidity=20 for (uint256 j; j < tokenLength; ) { ``` - Local variable `j` is never initialized. --- ```solidity=38 for (uint256 i; i < length; ) { ``` - Local variable `i` is never initialized.
Open the reportThe contracts cited have an unlocked compiler version. An unlocked compiler version in the source code of the contract permits the user to compile it at or above a particular version. This, in turn, leads to differences in the generated bytecode between compilations due to differing compiler version numbers. This can lead to ambiguity when debugging, as compiler specific bugs may occur in the codebase that would be hard to identify over a span of multiple compiler versions rather than a specific one.
Open the report```solidity=75 ogwlPrices[0] = uint128(prices_[0]); ``` - The type conversion `uint128(prices_[0])` from larger type uint256 to smaller type uint128 may truncate data. --- ```solidity=76 ogwlPrices[1] = uint128(prices_[1]); ``` - The type conversion `uint128(prices_[1])` from larger type uint256 to smaller type uint128 may truncate data. --- ```solidity=188 _setAux(msg.sender, uint64(aux + (1 << bitPos))); ``` - The type conversion `uint64(aux + (1 << bitPos))` from larger type uint256 to smaller type uint64 may truncate data.
Open the report`MintNotStarted` is declared but never used: ```solidity=33 error MintNotStarted(); ```
Open the report`PriceChanged` is declared in `Origins` but never emitted: ```solidity=97 event PriceChanged(uint256 mintState, uint256 price); ```
Open the reportOne state variables are never used in the codebase. Variable `PUBLIC_PRICE` in `Origins` is never used in `Origins`. ```solidity=44 uint256 private constant PUBLIC_PRICE = 2; ```
Open the reportIt is not recommended to use Solidity's `transfer()` and `send()` functions for transferring Ether, since some contracts may not be able to receive the funds. Those functions forward only a fixed amount of gas (2300 specifically) and the receiving contracts may run out of gas before finishing the transfer. Also, EVM instructions' gas costs may increase in the future. Thus, some contracts that can receive now may stop working in the future due to the gas limitation. ```solidity=247 to.transfer(address(this).balance); ``` - `Origins.withdraw()` uses `transfer()`.
Open the reportDifferent magic numbers are used as-is in code.
Open the reportThe reports name a repository or files. Open a report to see its scope.
Trustblock holds 1 public audit report for Avium Origins, dated 24 Jan 2023. The latest is by CertiK (“Avium 1 - audit addendum”).
CertiK wrote the report Trustblock holds for Avium Origins.
15 findings are still open or acknowledged in the firms’ reports: 1 high, 14 low (all open). No critical finding is reported. Statuses are the security firms’ own.
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="avium-origins"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us