
BitDCA security record
As of 30 Oct 2026, BitDCA has 1 audit report on Trustblock, by CertiK, dated 19 Feb 2025. That report lists no open critical findings.
Record last updated . It holds audits and findings, contracts and incidents up to Oct 2026. Trustblock does not review code.
Audits1
Newest first
Findings6
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 2 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 1 | 3 |
HighCentralization Related RisksBitDCA · CertiK · 19 Feb 2025Acknowledged
### BDCAVesting In the contract `BDCAVesting`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer or renounce ownership, and set vesting schedules and allocations for multiple addresses once. 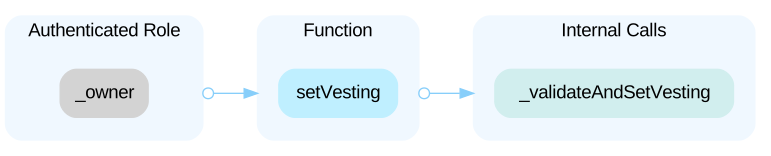 ### BDCAVestingCEX In the contract `BDCAVestingCEX`, the role `_manager` has authority over the functions shown in the diagram below. Any compromise to the `_manager` account may allow the hacker to take advantage of this authority and start the vesting process allowing the user to claim tokens. 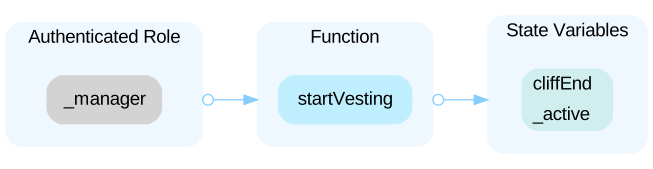 ---- In the contract `BDCAVestingCEX`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer or renounce ownership, set the manager address as long as the contract is not activated, and set vesting allocations for multiple addresses once as long as the contract is not activated. 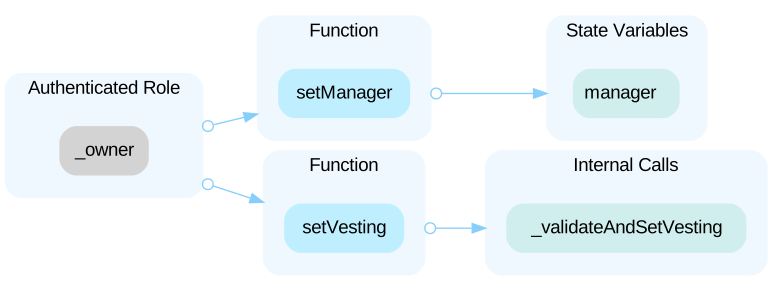
Open the reportHighInitial Token DistributionBitDCA · CertiK · 19 Feb 2025Acknowledged
All of the `BDCA Token` tokens are sent to the contract deployer. This is a centralization risk because the deployer can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
Open the reportLowInconsistent Solidity VersionsBitDCA · CertiK · 19 Feb 2025Acknowledged
The codebase contains multiple Solidity versions, which can lead to unexpected behavior, potential vulnerabilities, difficulties in maintaining the code, and inconsistencies in the execution of the smart contract. Using different versions may also result in increased complexity during code auditing, as different security features and bug fixes are present in different versions of the compiler. Versions used: `^0.8.20`, `^0.8.9` ```solidity=3 pragma solidity ^0.8.20; ``` `^0.8.20` is used in contracts/BDCAVestingCEX.sol file. ```solidity=3 pragma solidity ^0.8.20; ``` ```solidity=2 pragma solidity ^0.8.9; ``` `^0.8.9` is used in contracts/BDCA.sol file. ```solidity=2 pragma solidity ^0.8.9; ```
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="bitdca"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us