
Confti security record
As of 24 Oct 2026, Confti has 1 audit report on Trustblock, by CertiK, dated 18 Oct 2022. That report lists no open critical findings.
Record last updated . It holds audits and findings, contracts and incidents up to Oct 2026. Trustblock does not review code.
Audits1
Newest first
Findings25
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 2 | 1 |
| Medium | 0 | 4 | 1 |
| Low | 10 | 0 | 7 |
HighCentralization RisksConfti · CertiK · 18 Oct 2022Acknowledged
In the contract `Division`, the role `routerContract.whiteList()` has the authority over the following function: - function `mintDivision()`: mint any amount of `Division` token to any arbitrary address `account`, - function `burnDivision()`: burn the `Division` token of any address `account`. In the contract `Router`, the role `curator` has authority over the functions shown in the diagram below. 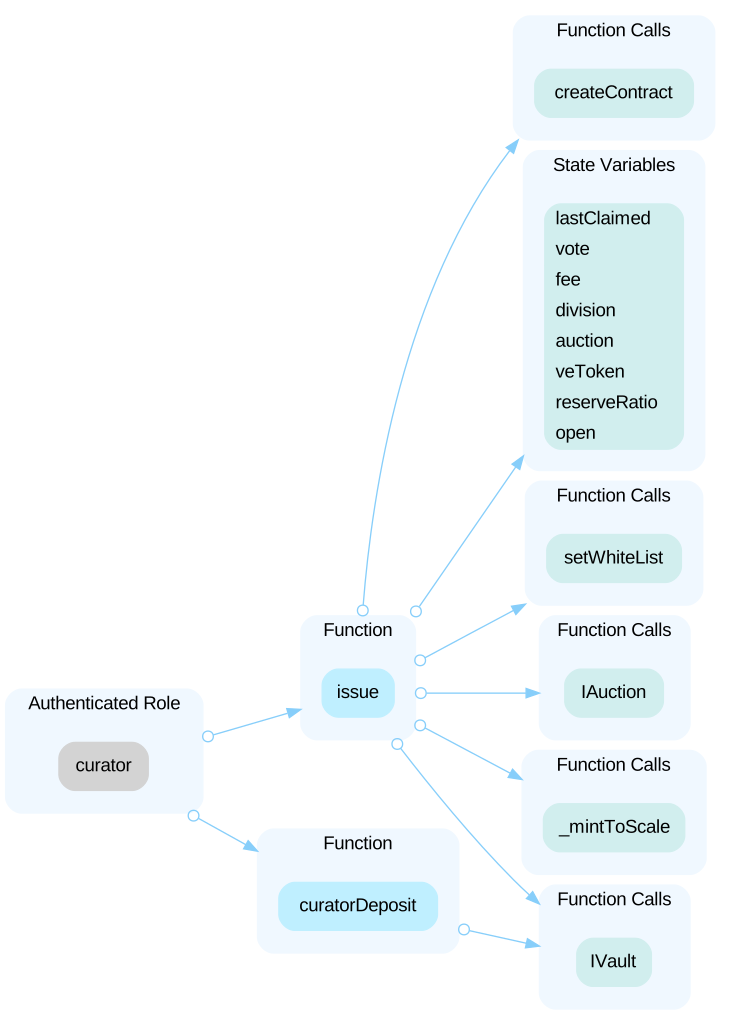 In the contract `Router`, the role `whiteList` has authority over the functions shown in the diagram below. 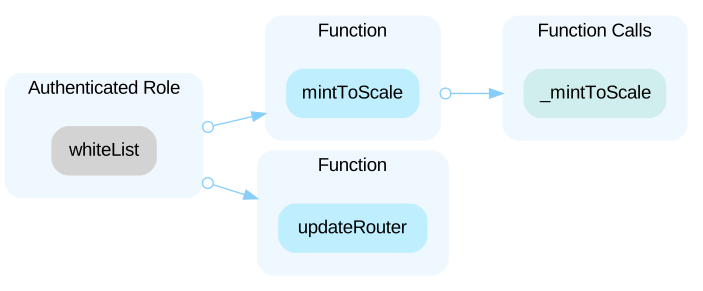 In the contract `Factory`, the role `_owner` has authority over the functions shown in the diagram below. 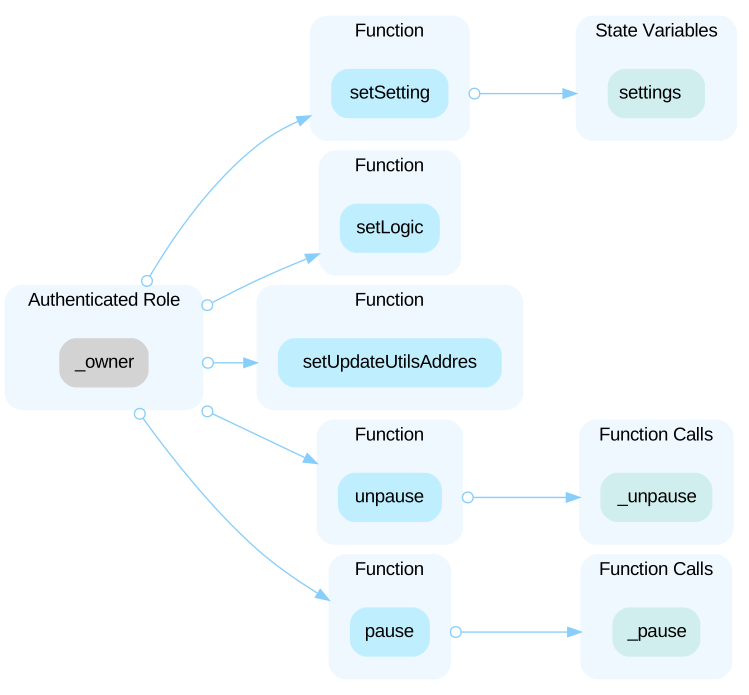 In the contract `Settings`, the role `_owner` has authority over the functions shown in the diagram below. 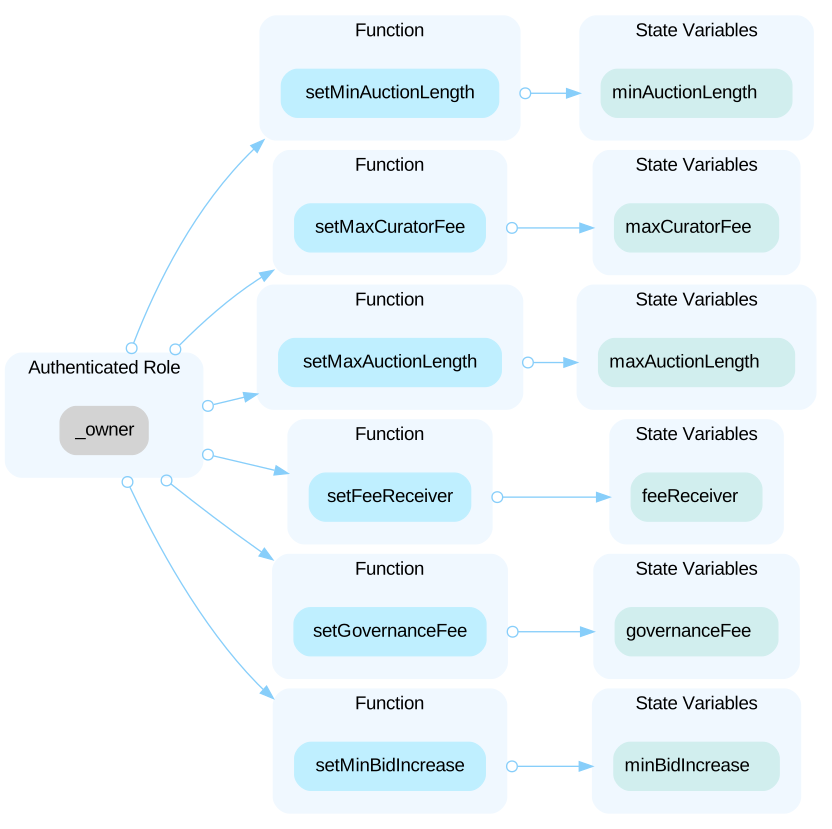 Any compromise to the privileged accounts may allow the hacker to take advantage of this authority and users' assets may suffer loss.
Open the reportHighCentralized Control of Contract UpgradeConfti · CertiK · 18 Oct 2022Acknowledged
`Router`, `Auction`, `Vault`, `VeToken`, `Vote`, `v1Tov2` are upgradeable contracts, the `IRouterData(router).whiteList()` and `IRouterData(router).curator()` can upgrade the contracts or change configuration variables without the community's commitment. `Router` and `v1Tov2` can be changed by the owner of contract `Factory`. Only the `Vote` contract is updated after voting. If an attacker compromises the account, he can change the implementation of the contracts and drain tokens from these contracts.
Open the reportMediumLack Of Access ControlConfti · CertiK · 18 Oct 2022Acknowledged
The linked functions can be called by anyone as it has no access restriction. This enables anyone to call these functions.
Open the reportMediumLogic issue on auction priceConfti · CertiK · 18 Oct 2022Acknowledged
In the below code snippet of function `setPrice()`, the auction price is set to each `_nftInVaultIndex` which is corresponding to a specific NFT token. However, all of the auction functions `start()`, `bid()` and `end()` are using the auctions[0].price, which is the price of the NFT token whose `_nftInVaultIndex` is 0. It seems that the logic is selling all the freedom NFT tokens one time, then it may be better to have one state variable to specify the total price of all the freedom NFT tokens. ```solidity=33 uint256 _nftInVaultIndex = IVaultData(getVault()).nftIndex(nft,nftId); auctions[_nftInVaultIndex].price = price_; ```
Open the reportMediumPotential Risk of `delegatecall`Confti · CertiK · 18 Oct 2022Acknowledged
DelegateCall, as the name implies, is a calling mechanism of how the caller contract calls the target contract function but when the target contract executed its logic, the context is not on the target contract but on the caller contract. So all developers should be aware of the risk that the `target` address may do harm to the current contract. In addition, it may also cause function clashing. Refer to https://forum.openzeppelin.com/t/beware-of-the-proxy-learn-how-to-exploit-function-clashing/1070. Auction.updateAuction(address) (contracts/Template/Istanbul10/logic/Auction.sol#141-148) uses delegatecall to a input-controlled function id - (_ok,returnData) = _updataTemplate.delegatecall(abi.encodeWithSignature(updateAuctionUtils())) (contracts/Template/Istanbul10/logic/Auction.sol#143-145) ```solidity=143 (bool _ok, bytes memory returnData) = _updataTemplate.delegatecall(abi.encodeWithSignature( "updateAuctionUtils()" )); ``` --- Router.updateRouter(address) (contracts/Template/Istanbul10/logic/Router.sol#210-217) uses delegatecall to a input-controlled function id - (_ok,returnData) = updataTemplate.delegatecall(abi.encodeWithSignature(updateRouterUtils())) (contracts/Template/Istanbul10/logic/Router.sol#212-214) ```solidity=212 (bool _ok, bytes memory returnData) = updataTemplate.delegatecall(abi.encodeWithSignature( "updateRouterUtils()" )); ``` --- Vault.updateVault(address) (contracts/Template/Istanbul10/logic/Vault.sol#303-310) uses delegatecall to a input-controlled function id - (_ok,returnData) = updataTemplate.delegatecall(abi.encodeWithSignature(updateVaultUtils())) (contracts/Template/Istanbul10/logic/Vault.sol#305-307) ```solidity=305 (bool _ok, bytes memory returnData) = updataTemplate.delegatecall(abi.encodeWithSignature( "updateVaultUtils()" )); ``` --- VeToken.updateVeToken(address) (contracts/Template/Istanbul10/logic/VeToken.sol#1128-1134) uses delegatecall to a input-controlled function id - (_ok,returnData) = _updataTemplate.delegatecall(abi.encodeWithSignature(updateVeTokenUtils())) (contracts/Template/Istanbul10/logic/VeToken.sol#1129-1131) ```solidity=1129 (bool _ok, bytes memory returnData) = _updataTemplate.delegatecall(abi.encodeWithSignature( "updateVeTokenUtils()" )); ```
Open the reportMediumShare in `cash()` may be shrunk by `VeToken.totalConfti · CertiK · 18 Oct 2022Acknowledged
In the function `Router.cash()`, the users holding Division can get the ETH from the NFT auction. The amount they can get is determined by their Division balance. However, the calculation formula also includes `IVeToken(veToken).totalClaimable()` as a portion of denominator. The `IVeToken(veToken).totalClaimable()` is the available locking rewards in `VeToken`. If the curator or `govAddress` has locked some Division in `VeToken` and not called the `VeToken.claim()` function, they will get less ETH since the locked rewards has not been distributed yet. ```solidity=168 uint256 bal = IERC20(division).balanceOf(msg.sender); require(bal > 0, "cash:no tokens to cash out"); uint256 share = bal * address(vault).balance / (IERC20(division).totalSupply() + IVeToken(veToken).totalClaimable()); ```
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="confti"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us