Incident
Incident,
Source: De.Fi incident database.
- Audits before it
- 0.
- Audits since
- 3, the latest dated 13 Apr 2023.

As of 3 Nov 2026, DEBT Box has 3 audit reports by 1 security firm on Trustblock; the latest is by CertiK, dated 13 Apr 2023. Those reports list no open critical findings. It also holds 6 deployed contracts on 1 chain and 1 incident (latest 12 Dec 2022).
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| Grow | Security firm: CertiK | Date: | Scope: 1 address on BNB Chain | No open critical findings | Open · skynet.certik.com |
| Digital Linked Gold | Security firm: CertiK | Date: | Scope: 1 address on BNB Chain | No open critical findings | Open · skynet.certik.com |
| The Debt Box (BGLD, NATG, ALUM, XPLR) | Security firm: CertiK | Date: | Scope: 4 addresses on BNB Chain | No open critical findings | Open · skynet.certik.com |
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 5 | 0 |
| Medium | 0 | 2 | 0 |
| Low | 19 | 9 | 0 |
In the contract `GROW` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify different token settings such as the UniSwap (PancakeSwap) router, dividends and fees. 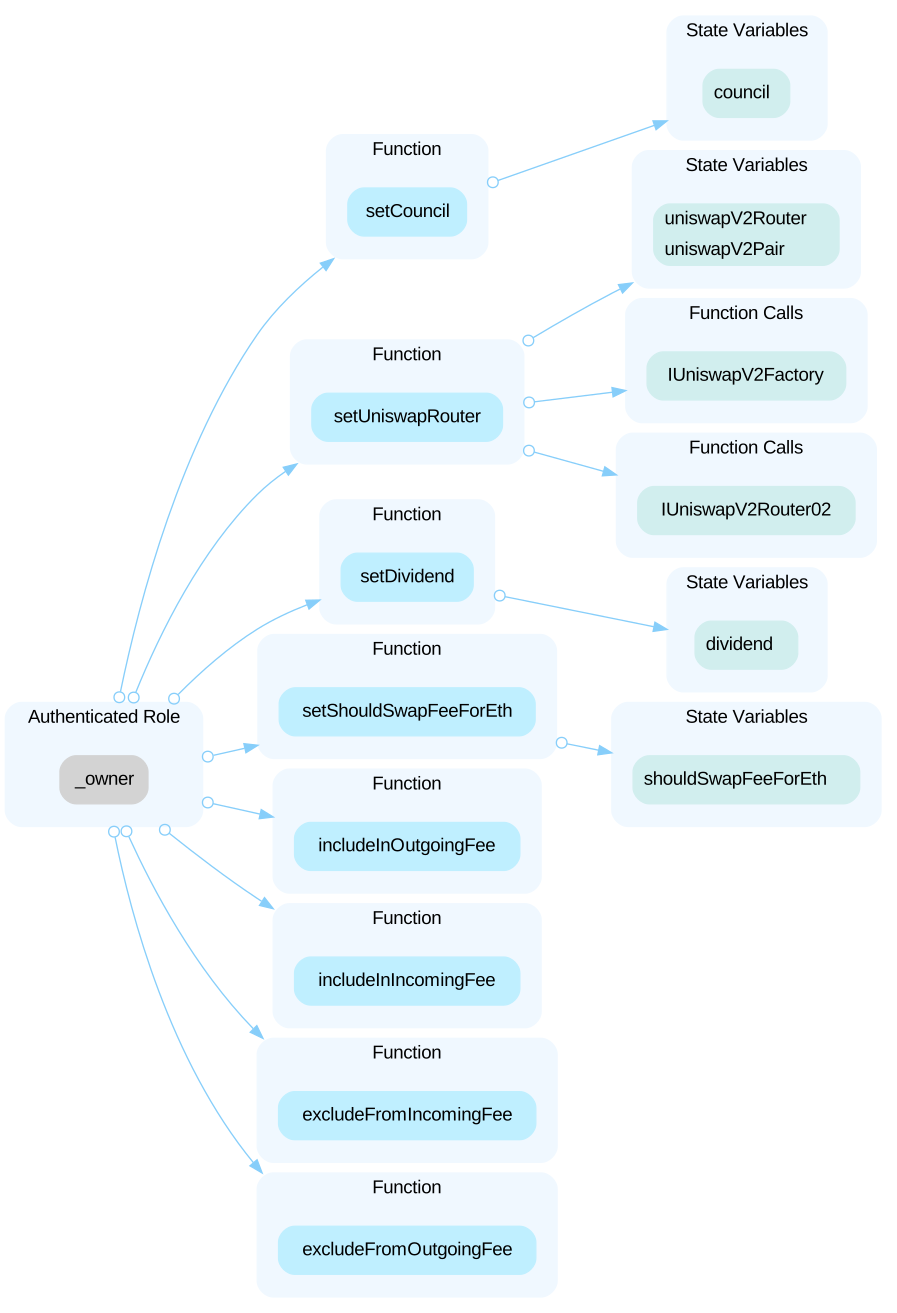 Furthermore, the role `_owner` has authority over the functions `renounceOwnership()` and `transferOwnership()`. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and renounce and transfer ownership at any time.
Open the reportAll of the `GROW` tokens are sent to the contract deployer when deploying the contract. This could be a centralization risk as the deployer can distribute `GROW` tokens without obtaining the consensus of the community.
Open the reportIn the contract `DigitalLinkedGold` the role `_owner` has authority over the functions: * `mint()` Any compromise to the `_owner` account may allow the hacker to take advantage of this authority
Open the reportIn the contract `Explore` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify the configuration of the contract and mint tokens to himself. 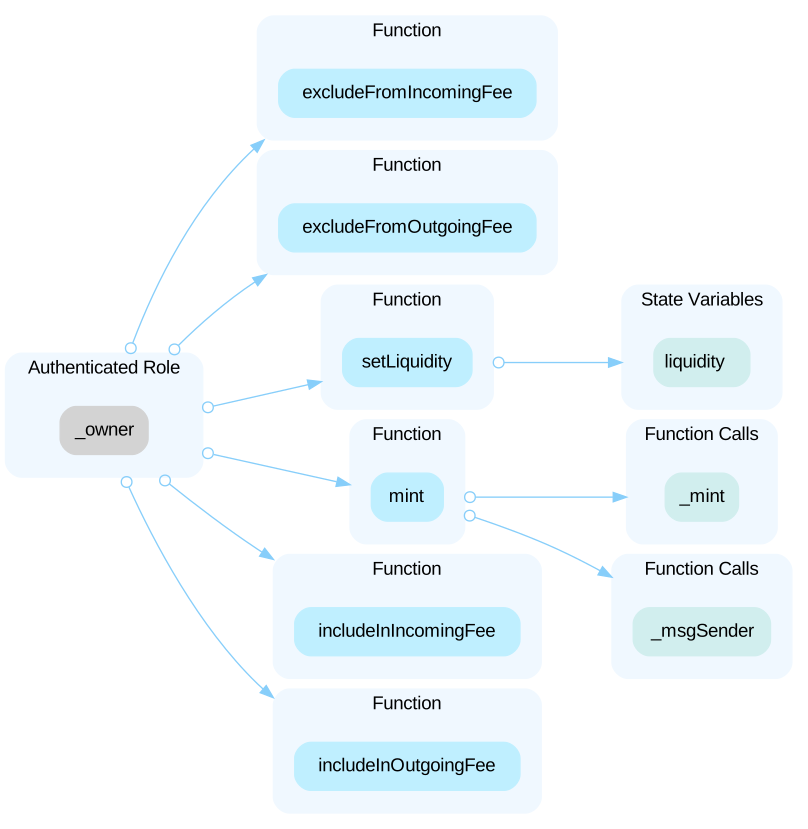 In the contract `Aluminum` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify the configuration of the contract and mint tokens to himself. 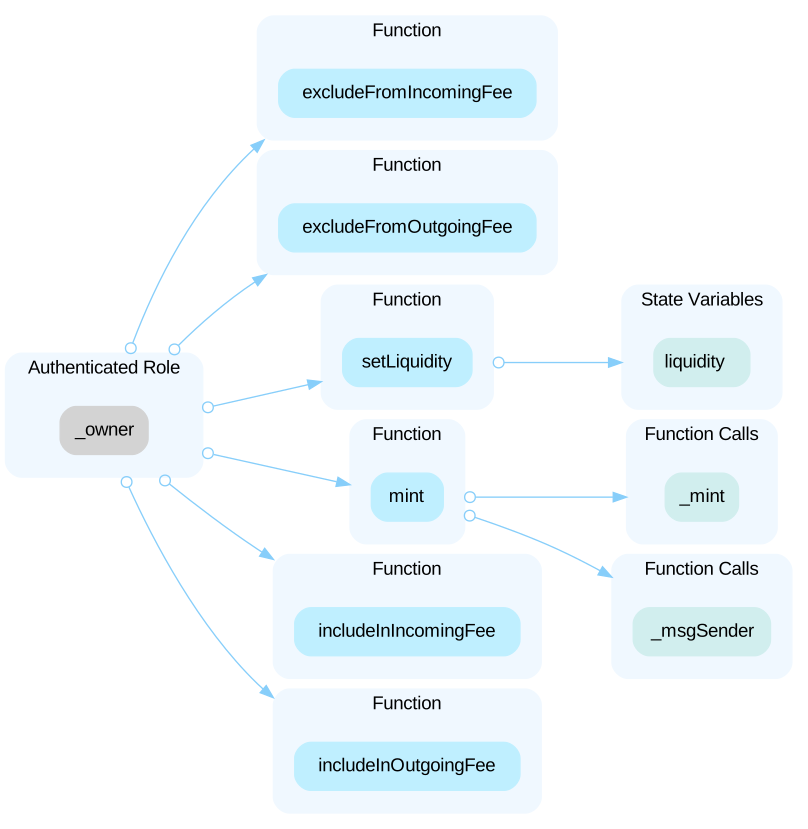 In the contract `BlackGold` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify the configuration of the contract and mint tokens to himself. 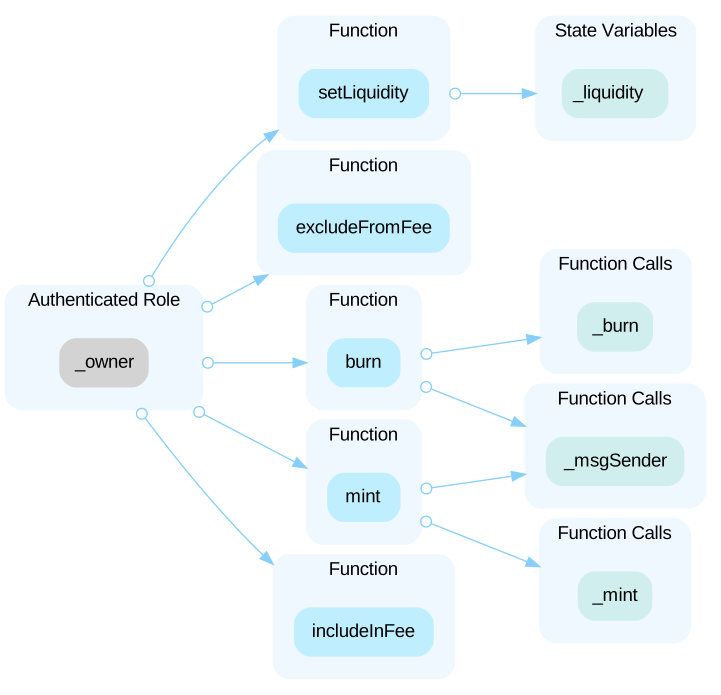 In the contract `NaturalGas` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify the configuration of the contract and mint tokens to himself. 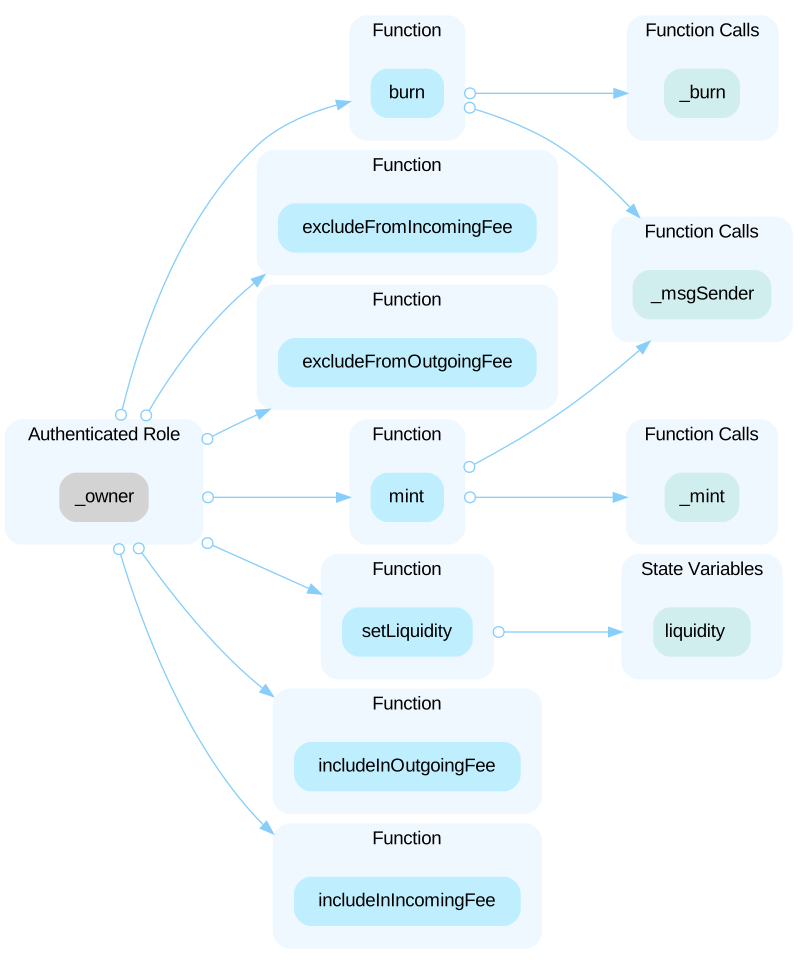
Open the reportThe contract owner can set the liquidity address to any address. The target address can be an EOA address or a smart contract. The implementation of the liquidity address is unknown, and whether the collected tokens will be used to provide liquidity is unknown.
Open the reportThe audited token contracts burn additional tokens from the sender's address during a token transfer. This behavior can potentially be exploited if the token's liquidity exists in Uniswap V2 (and its forks), and the liquidity pair address is not excluded from such a fee. The unique 'Skim()' and 'Sync()' functions in the Uniswap V2 pair contract enable such an attack. Please see the 'Scenario' section to understand how this issue can be exploited.
Open the reportThe contract uses the `pragma solidity 0.5.17` directive. This indicates that an outdated version of the compiler is used, which is prone to several disclosed bugs.
Open the report10% of the transfer fee will deduct from the sender's wallet, on top of the transfer amount. If user A approves user B 200 tokens and user B uses the "TransferFrom" function to transfer 100 A's tokens, A's balance will deduct by 110, and the "allowance" will only deduct by 100. The allowance reduction in the "TransferFrom" function doesn't put the "Fee" into consideration.
Open the reportMathematical operations in the aforementioned function perform divisions before multiplications. Performing multiplication before division can sometimes avoid loss of precision.
Open the reportLine 646 only checks if the sender is excluded from the fee: ```sol=646 " if (!_isExcludedFromFee[sender]) {" ``` But line 661 checks if both the sender and recipient are excluded from the fee: ```sol=661 if (!_isExcludedFromFee[sender] && !_isExcludedFromFee[recipient]) { ``` The fee check logic is inconsistent across two "if" statements.
Open the reportThe linked code is to transfer the "liquidityFee" to the "liquidity" address, but the value used in the `Transfer` event is "miningFee" instead of the "liquidityFee". ```sol=537 _balances[sender] = _balances[sender] - liquidityFee; _balances[liquidity] = _balances[liquidity] + liquidityFee; emit Transfer(sender, liquidity, miningFee); ```
Open the reportThere should always be events emitted in the sensitive functions that are controlled by centralization roles.
Open the reportThere should always be events emitted in the sensitive functions that are controlled by centralization roles.
Open the reportThere should always be events emitted in the sensitive functions that are controlled by centralization roles.
Open the reportThere should always be events emitted in the sensitive functions that are controlled by centralization roles.
Open the reportMultiple OpenZeppelin libraries are included in the source code file. It is highly recommended NOT to include OpenZeppelin library code directly in the source code because even slight changes to the library code may lead to major vulnerabilities/bugs.
Open the reportAttached through a shared contract address. Our incident data ends in Oct 2026.
Source: De.Fi incident database.
| Address | Chain | Source code |
|---|---|---|
| 0x891dc083842d1865ffdb8519b9dcaf363af5422a | Chain: BNB Chain | Source code: Verified source |
| 0x3f3701e818a560eacd6fca1477e36b9338a2cbed | Chain: BNB Chain | Source code: Verified source |
| 0x2f31750a50df85d9c0ef88d0c2fe9f014233755a | Chain: BNB Chain | Source code: Verified source |
| 0x9578a6cdfcb2d1a3075385217737f71adc29279d | Chain: BNB Chain | Source code: Verified source |
| 0xc2319e87280c64e2557a51cb324713dd8d1410a3 | Chain: BNB Chain | Source code: Verified source |
| 0xbc6488c75b47daff2cddd64003a203540b3112e4 | Chain: BNB Chain | Source code: Verified source |
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="debt-box"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us