
Derify protocol security record
As of 3 Nov 2026, Derify protocol has 3 audit reports by 1 security firm on Trustblock; the latest is by CertiK, dated 7 Dec 2023. Those reports list no open critical findings.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Audits3
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| Derify Protocol v2 | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
| Derify protocol Ⅱ | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
| Derify Protocol | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
Findings47
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 11 | 1 |
| Medium | 2 | 3 | 4 |
| Low | 11 | 0 | 14 |
HighCentralization Related RisksDerify Protocol v2 · CertiK · 7 Dec 2023Acknowledged
In the contract `DerifyClearing`/ `DerifyClearingModule` the role `EXECUTOR_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `EXECUTOR_ROLE` account may allow the hacker to take advantage of this authority: - withdraw executor's reward - transfer limit order to market - stop the position for profit or loss - liquidate or partial liquidate the user 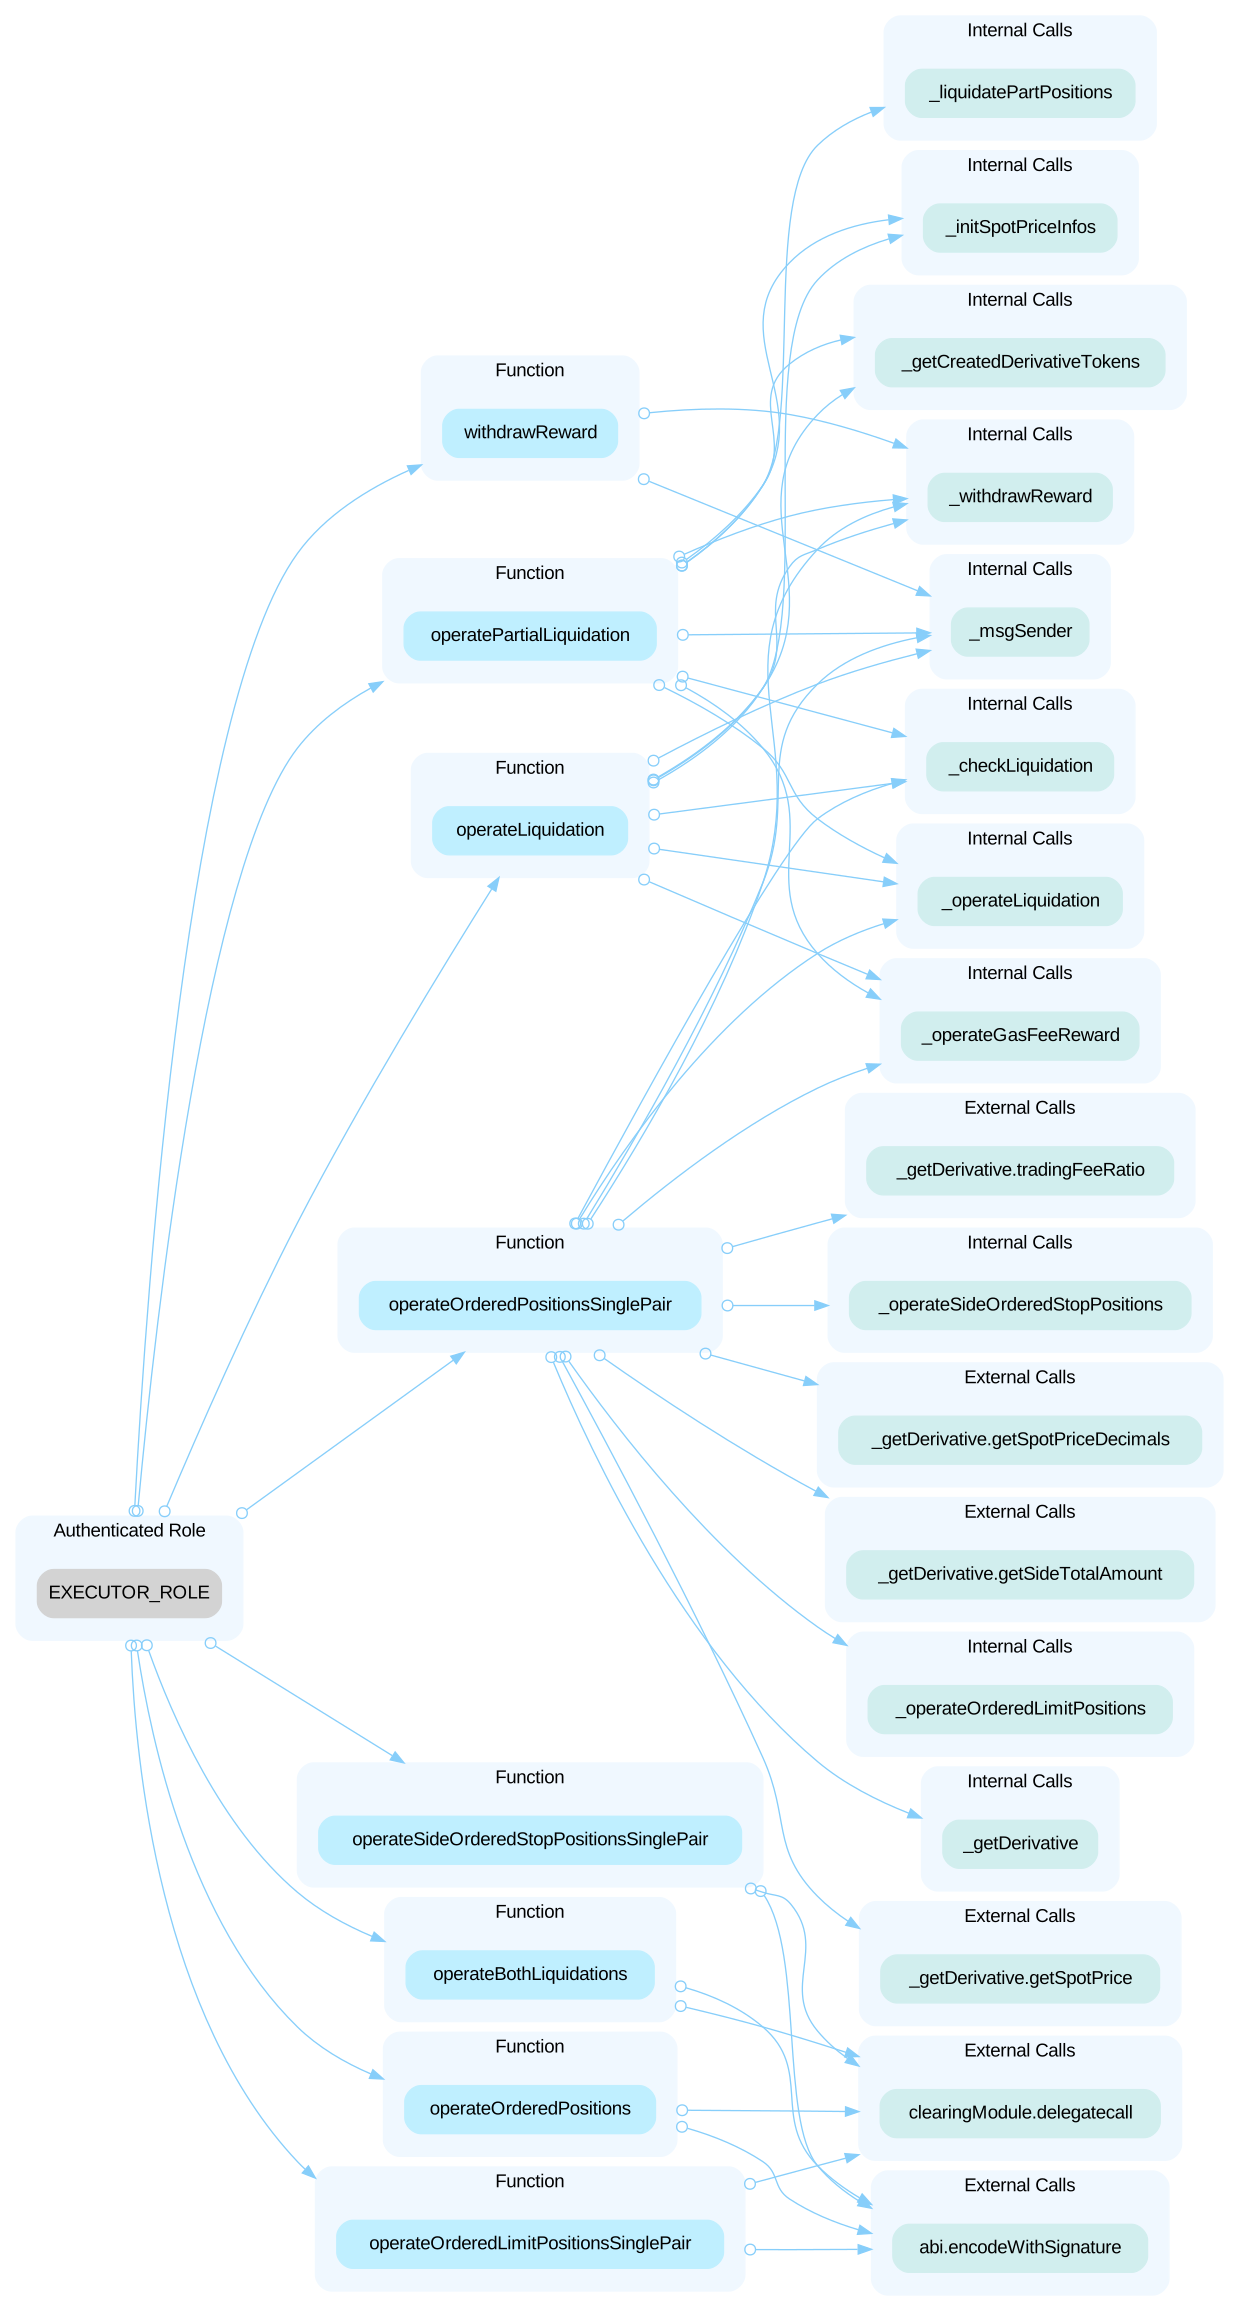 In the contract `DerifyClearing` / `DerifyClearingModule` the role `PAUSER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `PAUSER_ROLE` account may allow the hacker to take advantage of this authority: - pause and unpause the contract 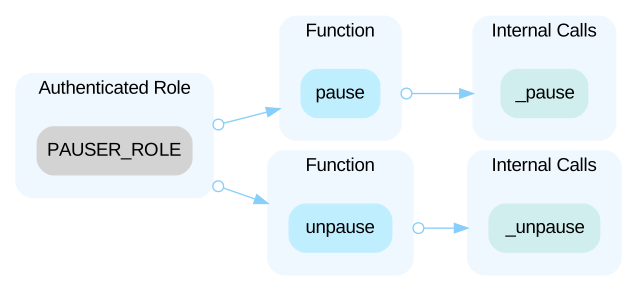 In the contract `DerifyClearing` / `DerifyClearingModule` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority: - update contract‘s ratio 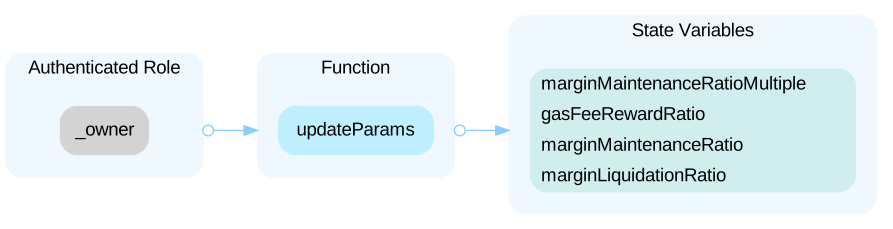 In the contract `DerifyExchange` the role `BUYBACK_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `BUYBACK_ROLE` account may allow the hacker to take advantage of this authority: - buyBack Drf tokens 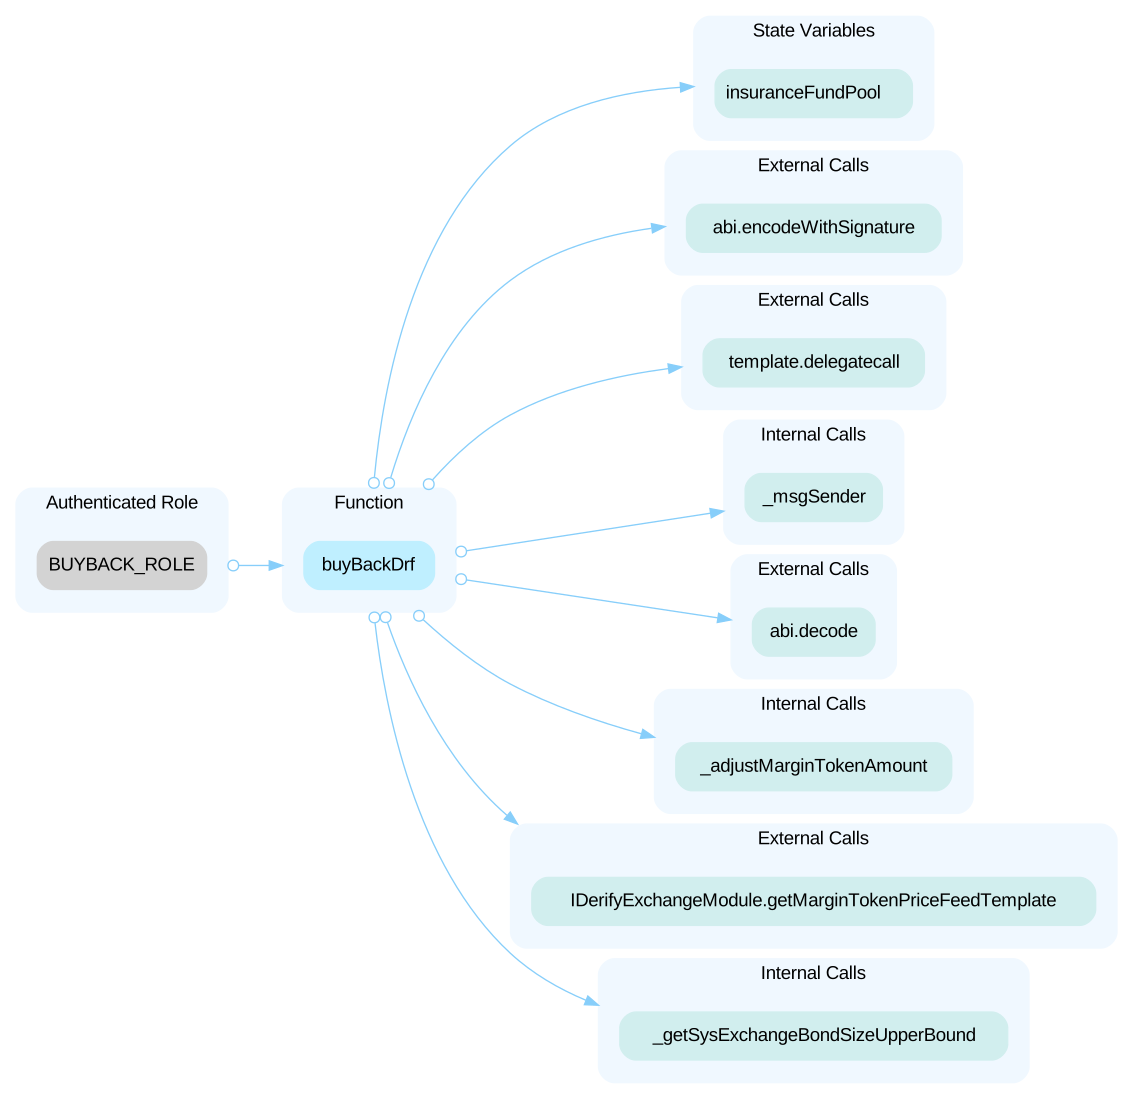 In the contract `DerifyExchange` the role `CLEARING_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `CLEARING_ROLE` account may allow the hacker to take advantage of this authority: - transfer one's tokens to others - remove the trader 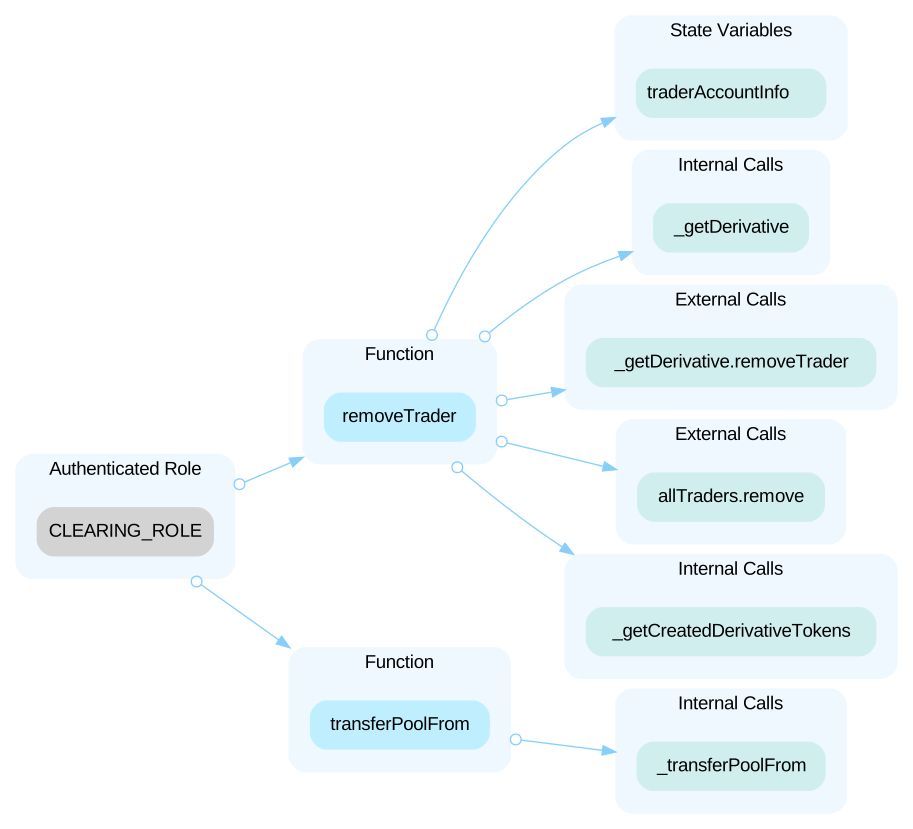 In the contract `DerifyExchange` the role `FEE_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `FEE_ROLE` account may allow the hacker to take advantage of this authority: - update the trader's balance - charge the trading fee 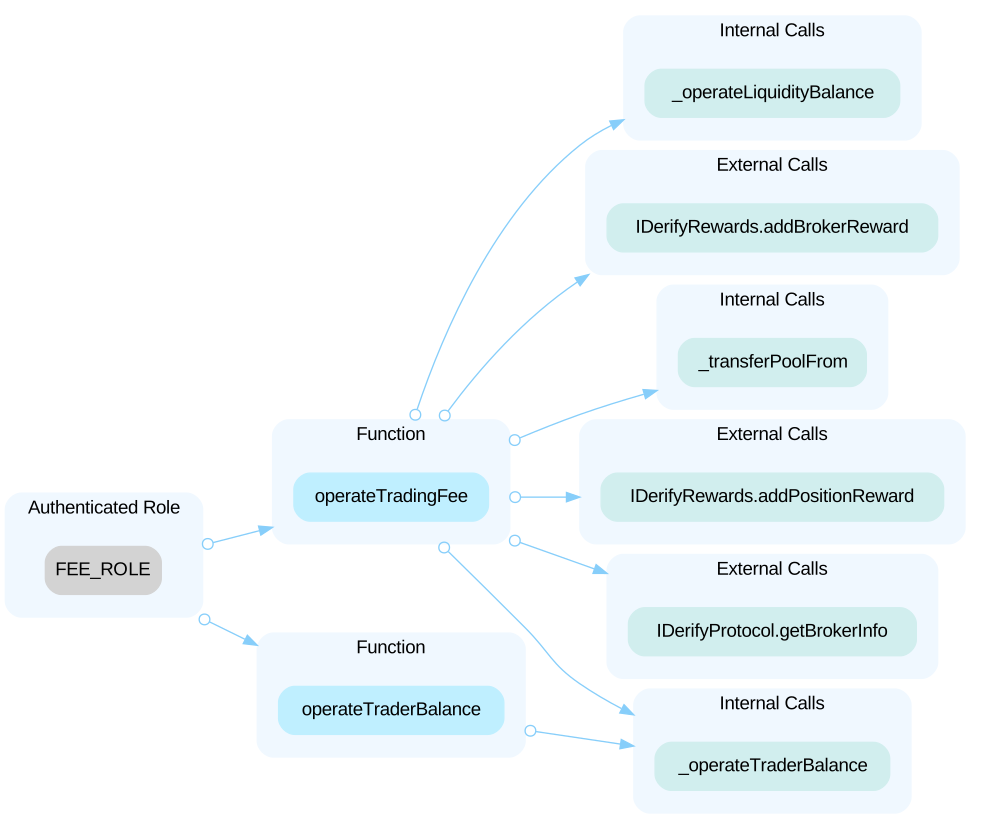 In the contract `DerifyExchange` the role `PAUSER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `PAUSER_ROLE` account may allow the hacker to take advantage of this authority: - pause and unpause the contract 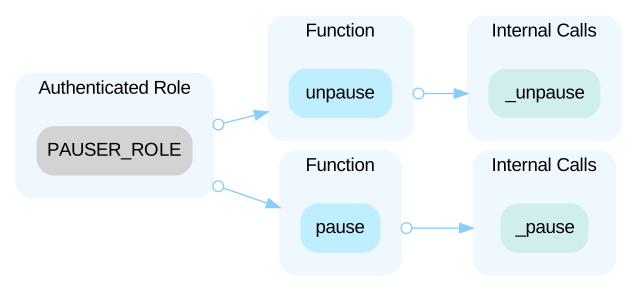 In the contract `DerifyExchange` the role `REWARD_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `REWARD_ROLE` account may allow the hacker to take advantage of this authority: - transfer marginToken to trader 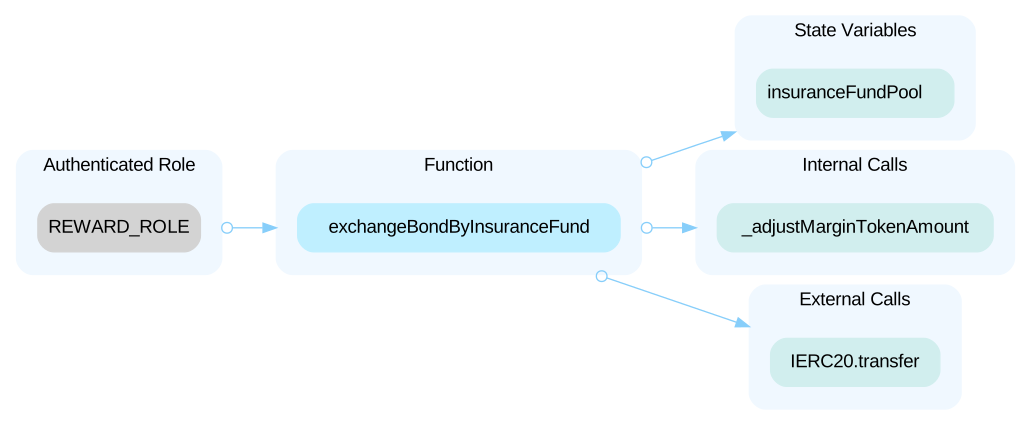 In the contract `DerifyExchange` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority: - initialize the contract - update the variable `thetaRatio`, `buyBackFundRatio` and `minOpenAmount` 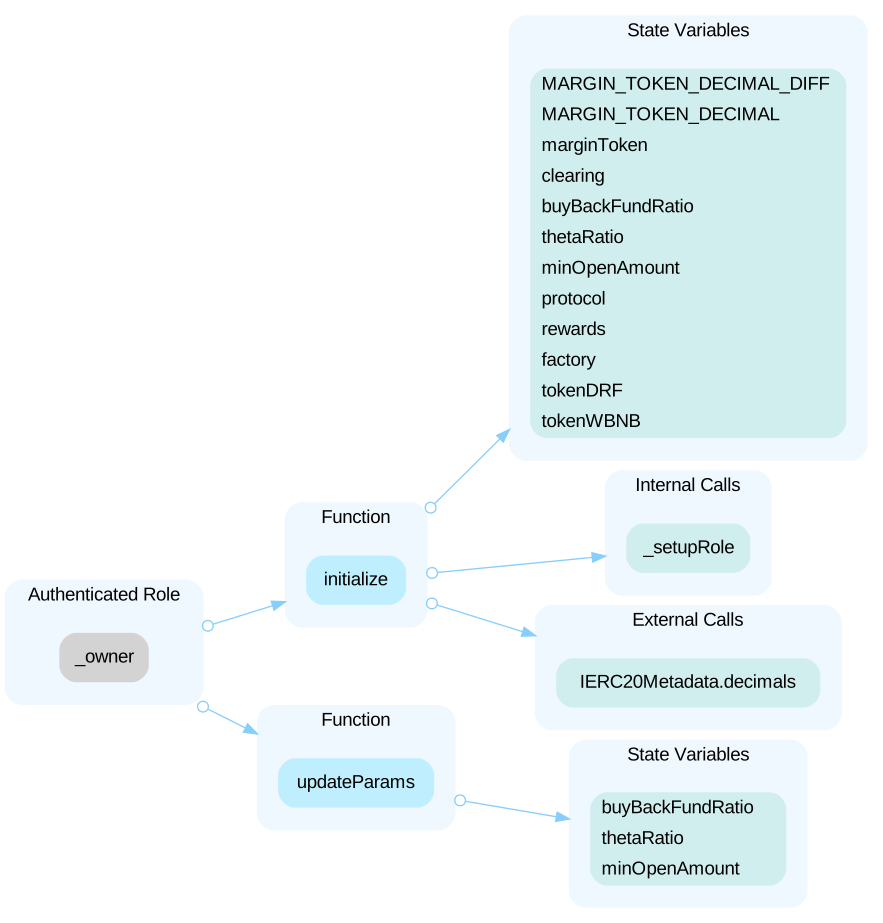 In the contract `DerifyDerivative` / `DerifyDerivativeModule` the role `CALLER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `CALLER_ROLE` account may allow the hacker to take advantage of this authority: - open market price position - create and cancel the limit price order - close the Position - remove the trader 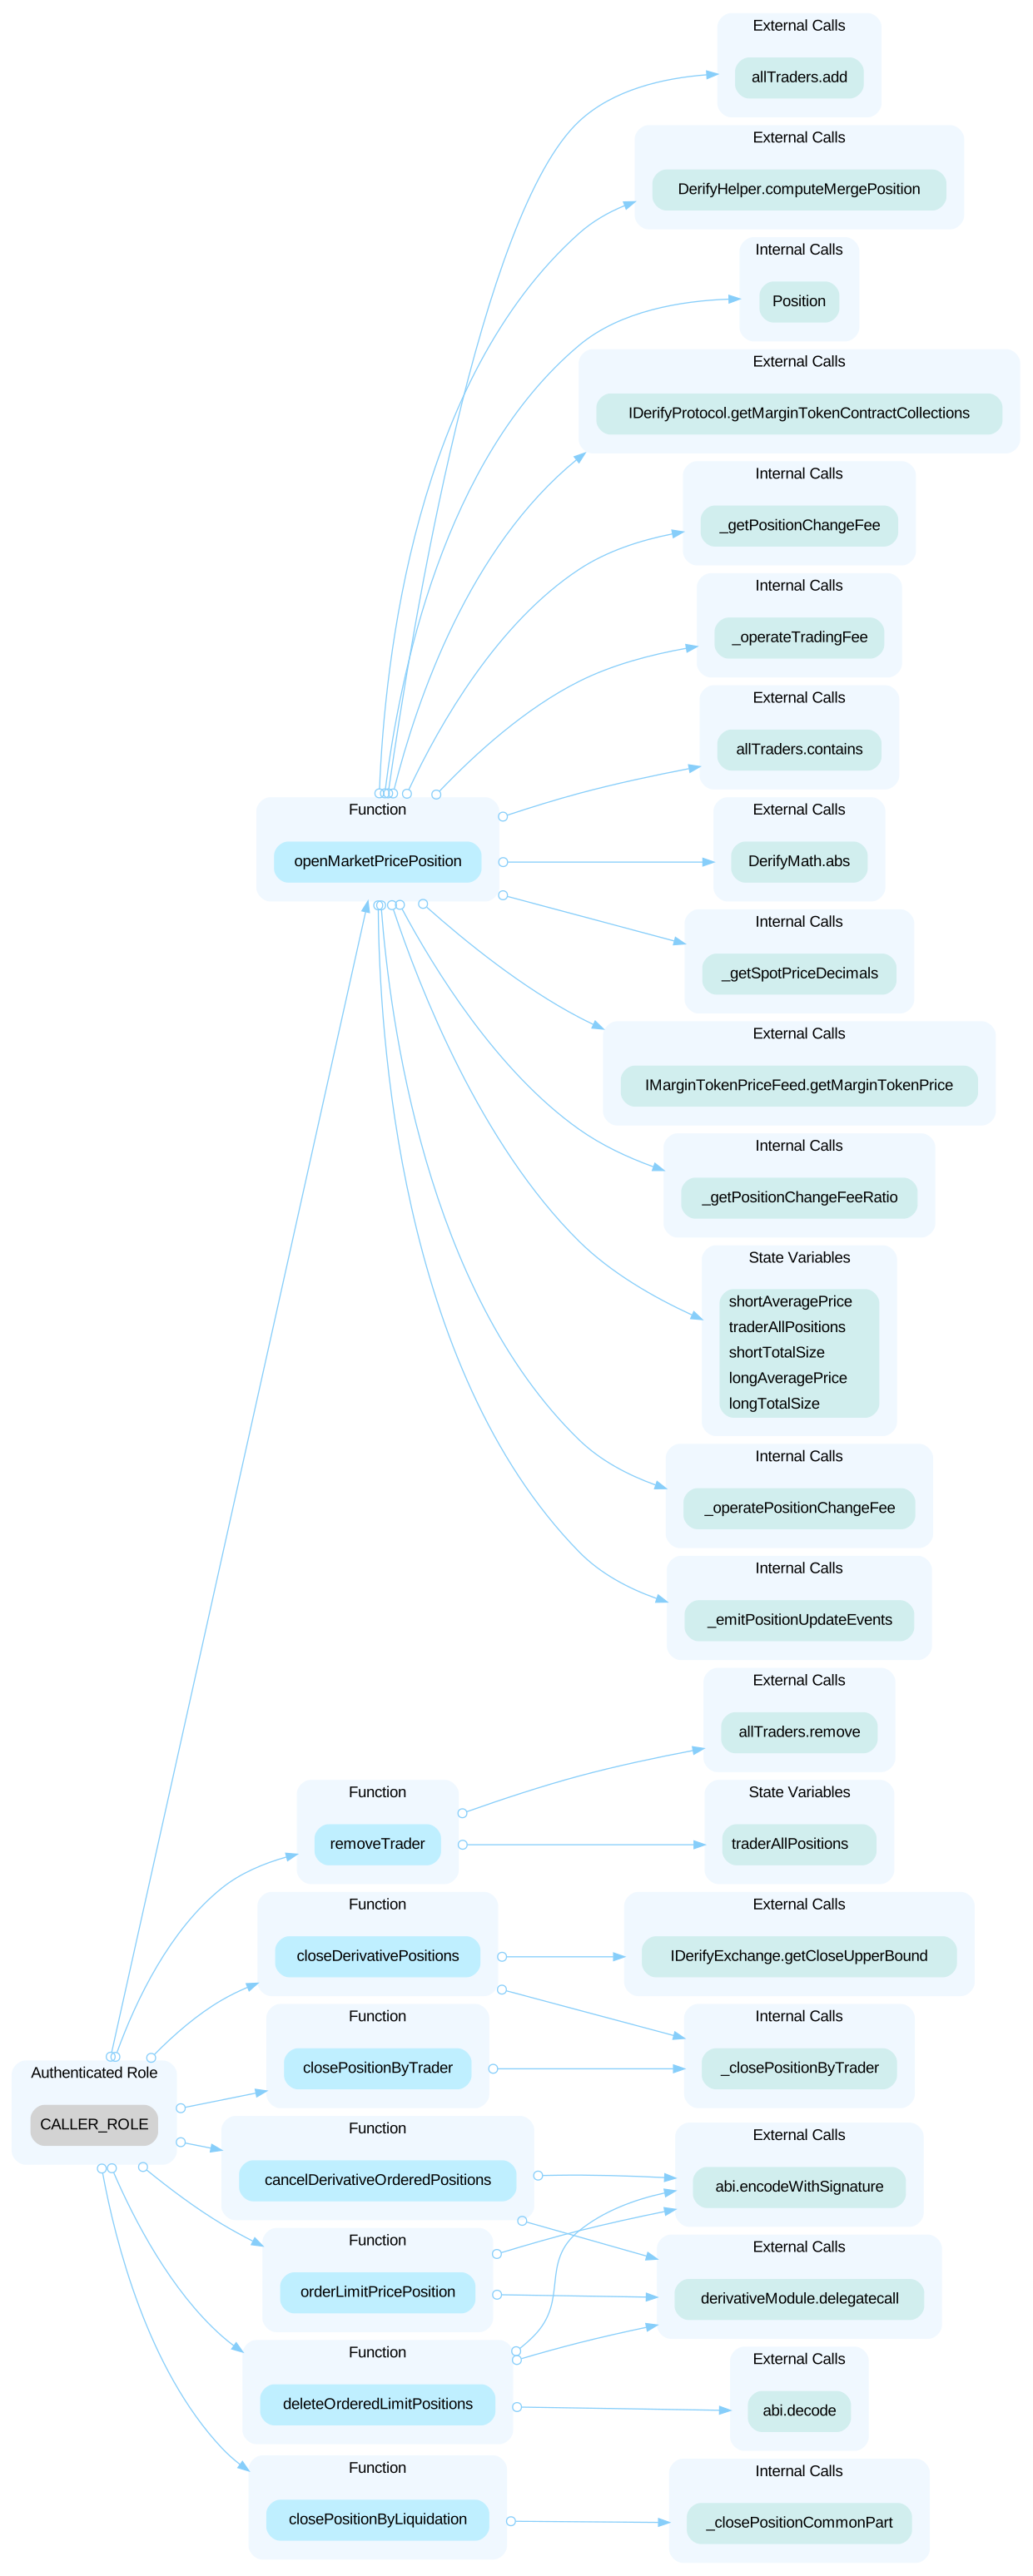 In the contract `DerifyDerivative`/ `DerifyDerivativeModule` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority: - initialize the contract - update the variable : - function lockDerivative(), to lock the price of the derivative. Any compromise to the `owner` account may allow the hacker to take advantage of this authority.
Open the reportHighInsufficient Validation of Oracle DataDerify Protocol v2 · CertiK · 7 Dec 2023Acknowledged
The `DerifyDerivative` contract does not check whether the price oracle returns non-zero value, nor the staleness of the data. Stale Oracle price can be caused by any issues with the Oracle provider. Thus, in the case that the Oracle returns an old price (which is incorrect at the moment of the request) this `price` will be valid and will lead to unexpected behavior. `latestRoundData` may return stale data, and there aren't any checks to ensure that this doesn't happen. This can be caused by any issues with Chainlink, such as oracle consensus problems or chain congestion, which may result in this contract relying on outdated data. **Notice**: The return data `answeredInRound`, which was previously used when answers could take multiple rounds to be computed, is deprecated. Its value is always equal to `roundId`. You can verify within the `OffchainAggregator.sol` contract specifically at L810 where the `latestRoundData()` function is defined.
Open the reportHigh`gasFee` decided by parameter in function `updateDerify protocol Ⅱ · CertiK · 16 Sep 2022Acknowledged
In the contract `DerifyBroker`, the owner can call function `updateDrfReward()` to release drf rewards to the brokers. At the same time, the gas fee will be taken from the brokers' accounts. However, the gas fee is decided by the parameter `gasFeeAmounts`, which means that the owner can decide how much usd will be withdrawn from the broker account to cover the gas fee. There is no limit to the process, if the owner makes a mistake or the account has been hacked, the broker can only endure the unfair result.
Open the reportHighCentralization Related Risks in DerifyClearing.soDerify protocol Ⅱ · CertiK · 16 Sep 2022Acknowledged
In the contract `DerifyClearing`, the role `owner` has authority over the following functions: - function updateParams(), to change params for the contract. The role `PAUSER_ROLE` has authority over the following functions: - function pause() and unpause(), to set pause status for the contract. The role `EXECUTOR_ROLE` has authority over the following functions: - function withdrawReward(), to claim rewards from the contract. - function operateOrderedPositions(), operateOrderedPositionsSinglePair() and to operate ordered positions. - function operateBothLiquidations(), operatePartialLiquidation() and operateLiquidation(), to operate liquidation. - function operateOrderedLimitPositionsSinglePair(), operateSideOrderedStopPositionsSinglePair(), to operate order limit positions and side ordered stop positions. The role can charge `estimateGasFee` which is decided by the parameter. AND In the contract `AccesscontrolEmuerable` which is the parent contract of the contract `DerifyClearing`, the role `role_admin` has authority over the following functions: - function grantRole() and revokeRole(), to grant roles to or revoke roles from the users. - Any compromise to the privileged accounts may allow a hacker to take advantage of this authority and bring unpredictable damages to the project.
Open the reportHighCentralization Related Risks in DerifyDerivative.Derify protocol Ⅱ · CertiK · 16 Sep 2022Acknowledged
In the contract `DerifyDerivative`, the role `DEFAULT_ADMIN_ROLE` has authority over the following functions: - function initialize(), to change many sensitive state variables at any time. The role `CALLER_ROLE` has authority over the following functions: - function openMarketPricePosition(), to open position for the user. - function orderLimitPricePosition(), to order limit price positions. - function closePositinoByTrader(), to close positions. - function closePositionByLiquidation(), to close position in the liquidation way. - function closeDerivativePositions(), to close positions. - function cancleDerivativeOrderedPositions(), to cancel limit price position orders. - function deleteOrderedLimitPositions(), to delete limit price positions. - function removeTrader(), to remove a trader's info. AND In the contract `AccesscontrolEmuerable` which is the parent contract of the contract `DerifyDerivative`, the role `role_admin` has authority over the following functions: - function grantRole() and revokeRole(), to grant roles to or revoke roles from the users. - Any compromise to the privileged accounts may allow a hacker to take advantage of this authority and bring unpredictable damages to the project.
Open the reportHighCentralization Related Risks in DerifyExchange.soDerify protocol Ⅱ · CertiK · 16 Sep 2022Acknowledged
In the contract `DerifyExchange`, the role `owner` has authority over the following functions: - function initialize(), to initialize the contract. The role `FEE_ROLE` has authority over the following functions: - function operateTraderBalance(), to operate the trader's balance. - function operateTradingFee(), to operate trading fee for the user. The role `REWARD_ROLE` has authority over the following functions: - function exchangeBondByInsurance(), to redeem usd with bond. The role `CLEARING_ROLE` has authority over the following functions: - function transferPoolFrom(), to process the pool balance. - function removeTrader(), to remove the trader. The role `BUYBACK_ROLE` has authority over the following functions: - function buyBackDrf(), to buy back drf with usd. The role `PAUSER_ROLE` has authority over the following functions: - function pause() and unpause(), to change the pause status for the contract. AND In the contract `AccesscontrolEmuerable` which is the parent contract of the contract `DerifyExchange`, the role `role_admin` has authority over the following functions: - function grantRole() and revokeRole(), to grant roles to or revoke roles from the users. - Any compromise to the privileged accounts may allow a hacker to take advantage of this authority and bring unpredictable damages to the project.
Open the reportHighCentralization Related Risks in DerifyRewards.solDerify protocol Ⅱ · CertiK · 16 Sep 2022Acknowledged
In the contract `DerifyRewards`, the role `owner` has authority over the following functions: - function initialize(), to initialize the contract. - function updateTradersPositionReward(), to update position rewards for the users. The role `PAUSER_ROLE` has authority over the following functions: - function pause() and unpause(), to set pause status for the contract. The role `EXCHANGE_ROLE` has authority over the following functions: - function payBond(), to add bond tokens for the users. AND In the contract `Accesscontrol` which is the parent contract of the contract `DerifyRewards`, the role `role_admin` has authority over the following functions: - function grantRole() and revokeRole(), to grant roles to or revoke roles from the users. Any compromise to the `[fixme]` account may allow a hacker to take advantage of this authority and bring unpredictable damages to the project.
Open the reportHighCentralization Risks in bDRF.sol and eDRF.solDerify protocol Ⅱ · CertiK · 16 Sep 2022Acknowledged
In the contract `eDRF` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and bring unpredictable damages to the project. 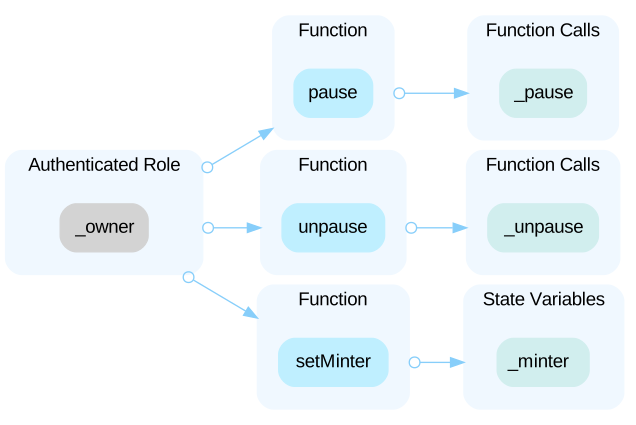 In the contract `bDRF` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and bring unpredictable damages to the project. 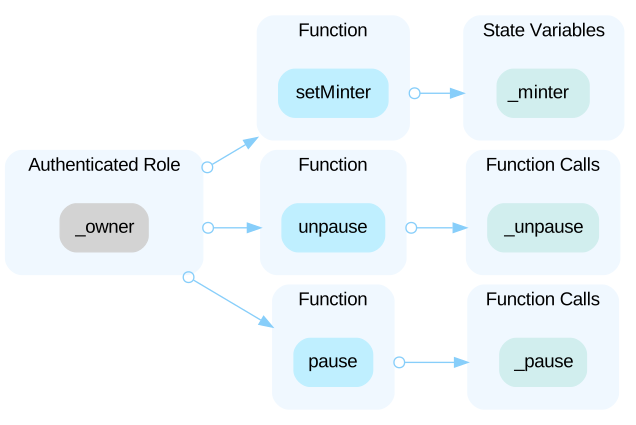
Open the reportHighCentralization Risks in DerifyBroker.solDerify protocol Ⅱ · CertiK · 16 Sep 2022Acknowledged
In the contract `DerifyBroker` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and bring unpredictable damages to the project. 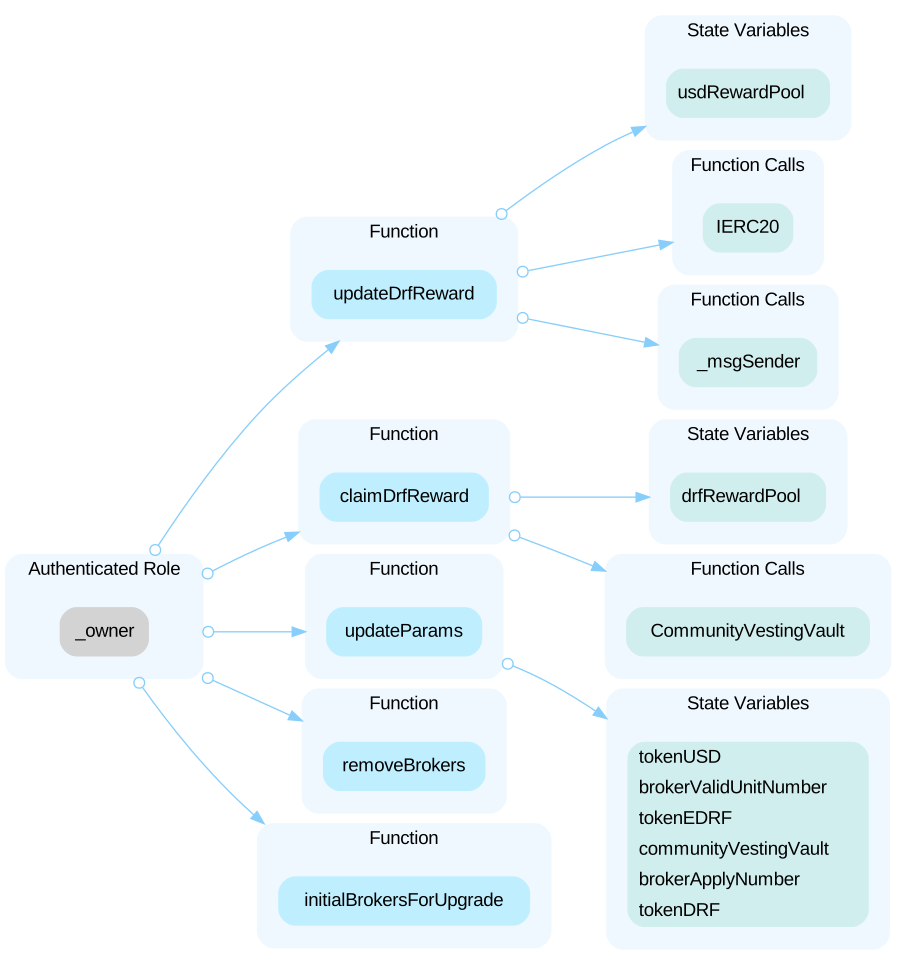 The role `PAUSER_ROLE` has authority over following functions: - function pause() and unpause(), to change the pause status of the contract. The role `EXCHANGE_ROLE` has authority over following functions: - function addBrokerReward(), to add usd rewards for brokers. Any compromises to the `PAUSER_ROLE` and `EXCHANGE_ROLE` accounts may allow the hacker to take advantage of this authority and bring unpredictable damages to the project. In the parent contract `AccessControl`, the role `ADMIN_ROLE`(ROLES' admin roles) has authority over the following functions: - function grantRole() and revokeRole(), to grant roles to or revoke roles from the users. Any compromises to the `ADMIN_ROLE` accounts may allow the hacker to take advantage of this authority and bring unpredictable damages to the project.
Open the reportShow 4 more
HighestimateGasFee determined by parameterDerify protocol Ⅱ · CertiK · 16 Sep 2022Acknowledged
The issue is similar to the situation where the owner updates brokers' rewards and takes fees. According to the white paper, the `clearing` role may be public to the users. We understand that the project needs to make the clearing public to users and allow them to arbitrage to trigger clearing and processing limit price positions. But if there is no way to limit the amount of the fee within the project, users' assets are also at risk of arbitrary charges.
Open the reportMediumLack of reasonable lower and Upper LimitDerify Protocol v2 · CertiK · 7 Dec 2023Acknowledged
There are no lower/upper boundaries when changing all the ratio in the function `updateParams()`.
Open the reportMediumPotential Front-running Order Cancellation to AvoDerify Protocol v2 · CertiK · 7 Dec 2023Acknowledged
Users are able to place multiple limit orders with gradually decreasing prices to open long positions. In the event of a significant and rapid market downturn, these users, by monitoring the mempool for any order operation transactions, may swiftly cancel the higher-priced orders that have become unfavorable compared to the current market price. This activity could disrupt the intended order execution flow . File: DerifyClearing.sol ```solidity=442 _getDerivative(token).openMarketPricePosition( IDerifyDerivative.TradeType.LimitPriceOpen, trader, theBroker, IDerifyDerivative.Side.LONG, executeSize, loops[k].price, loops[k].leverage ); operatedSize += executeSize; _getDerivative(token).deleteOrderedLimitPositions( trader, IDerifyDerivative.Side.LONG, k, executeSize, loops[k].price, loops[k].leverage, loops[k].timestamp ); ``` Front-running could happen as a result of: a) Oracle related issues: for instance, if oracle is missing an update for whatever reason or faces increased latency there is a risk of an arbitrager front-running the price feed and exploiting any differences with stale oracle price. b) MEV: even if oracle is functioning as designed, on Ethereum mainnet arbitragers could read mempool data and attempt to sandwich the price feed update by paying extra gas cost. Reference: https://chain.link/education-hub/maximal-extractable-value-mev
Open the reportMediumThe oracle price feed will continue to report theDerify Protocol v2 · CertiK · 7 Dec 2023Acknowledged
Chainlink aggregators have a built in circuit breaker if the price of an asset goes outside of a predetermined price band. The result is that if an asset experiences a huge drop in value (i.e. LUNA crash) the price of the oracle will continue to return the minPrice instead of the actual price of the asset. This would allow users to continue borrowing with the asset but at the wrong price. This is exactly what happened to [Venus on BSC when LUNA imploded](https://rekt.news/venus-blizz-rekt/). ChainlinkFeedRegistry#latestRoundData pulls the associated aggregator and requests round data from it. ChainlinkAggregators have minPrice and maxPrice circuit breakers built into them. This means that if the price of the asset drops below the minPrice, the protocol will continue to value the token at minPrice instead of it's actual value. This will allow users to take out huge amounts of bad debt and bankrupt the protocol.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="derify-protocol"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us