
DIN security record
As of 3 Nov 2026, DIN has 1 audit report on Trustblock, by CertiK, dated 14 Jan 2025. That report lists no open critical findings. It also holds 1 deployed contract on 1 chain.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Audits1
Newest first
Findings19
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 3 | 1 |
| Medium | 0 | 1 | 1 |
| Low | 11 | 0 | 2 |
HighCentralization Related RisksDIN · CertiK · 14 Jan 2025Acknowledged
In the contract `OwnableUpgradeable`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and add a manager, renounce ownership of the contract, transfer the contract ownership, or remove a manager. 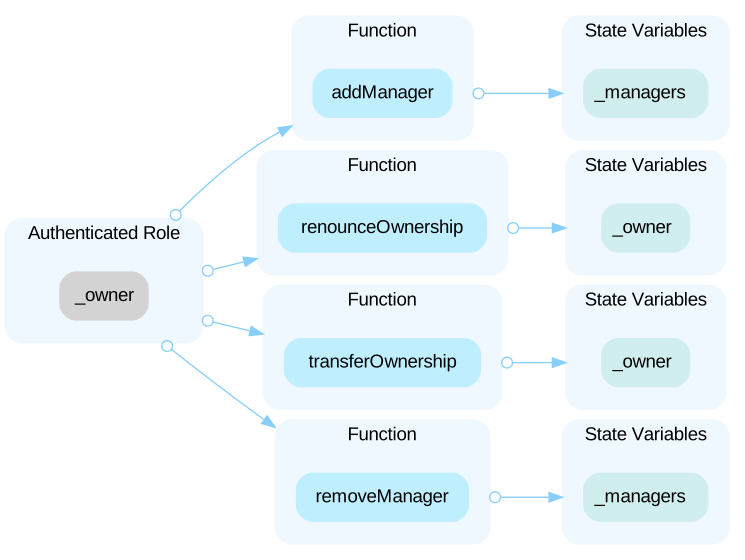 ----- In the contract `DIN`, the role `_manager` has authority over the functions shown in the diagram below. Any compromise to the `_manager` account may allow the hacker to take advantage of this authority and mint tokens to a specified address. 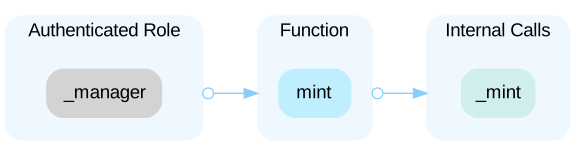 In the contract `DIN`, the role `_managers` has authority over the functions shown in the diagram below. Any compromise to the `_managers` account may allow the hacker to take advantage of this authority and mint tokens to a specified address. 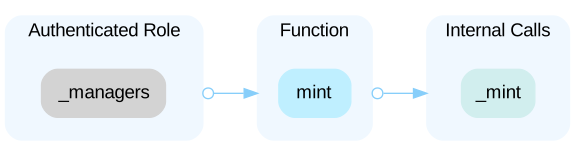 In the contract `DIN`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and mint tokens for a given address. 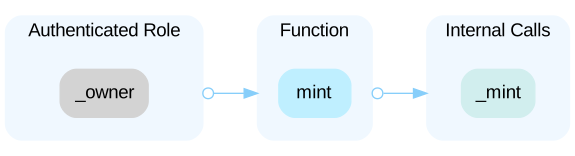 ----- In the contract `Ownable`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer the contract ownership, remove a manager, renounce contract ownership, or add a manager. 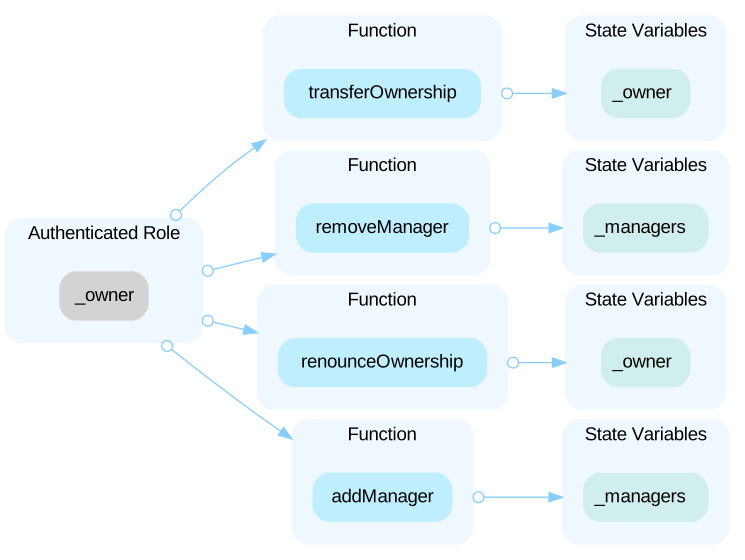 ----- In the contract `NodeStakingConvertor`, the role `_manager` has authority over the functions shown in the diagram below. Any compromise to the `_manager` account may allow the hacker to take advantage of this authority and unregister nodes, update global power status, and register and update node power and weight. 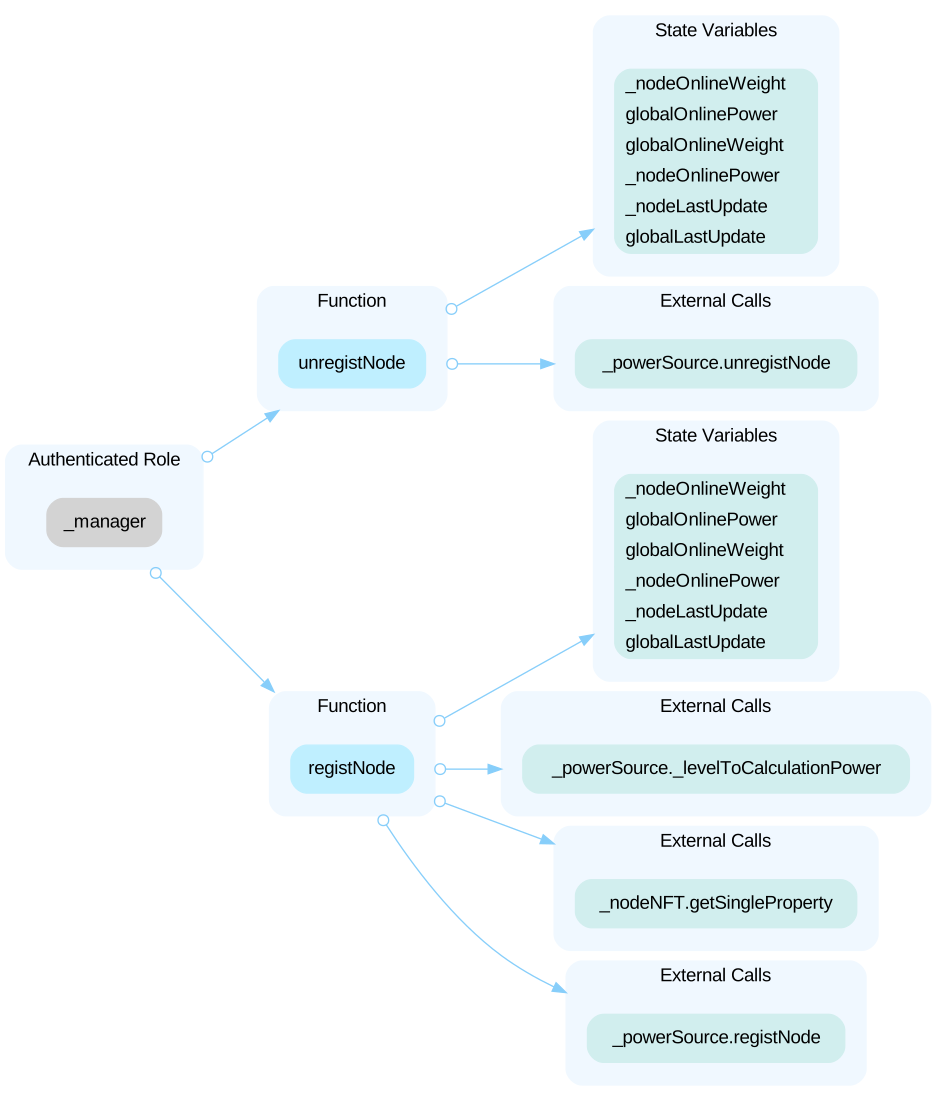 In the contract `NodeStakingConvertor`, the role `_managers` has authority over the functions shown in the diagram below. Any compromise to the `_managers` account may allow the hacker to take advantage of this authority and register nodes with NFT IDs, update power attributes, and unregister nodes with given NFT IDs. 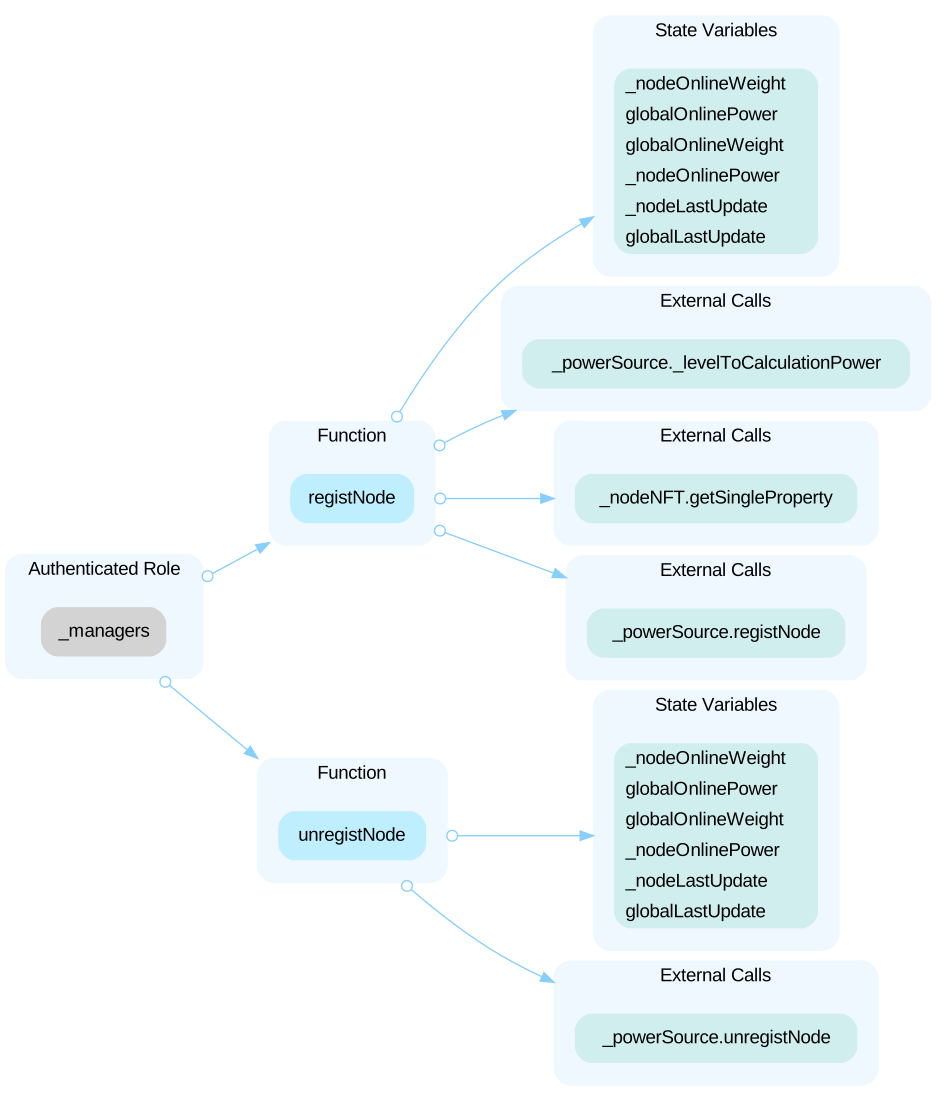 In the contract `NodeStakingConvertor`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change fundamental contract addresses, unregister nodes using provided nftIds, register power nodes with nft identifiers, and change reward configuration settings. 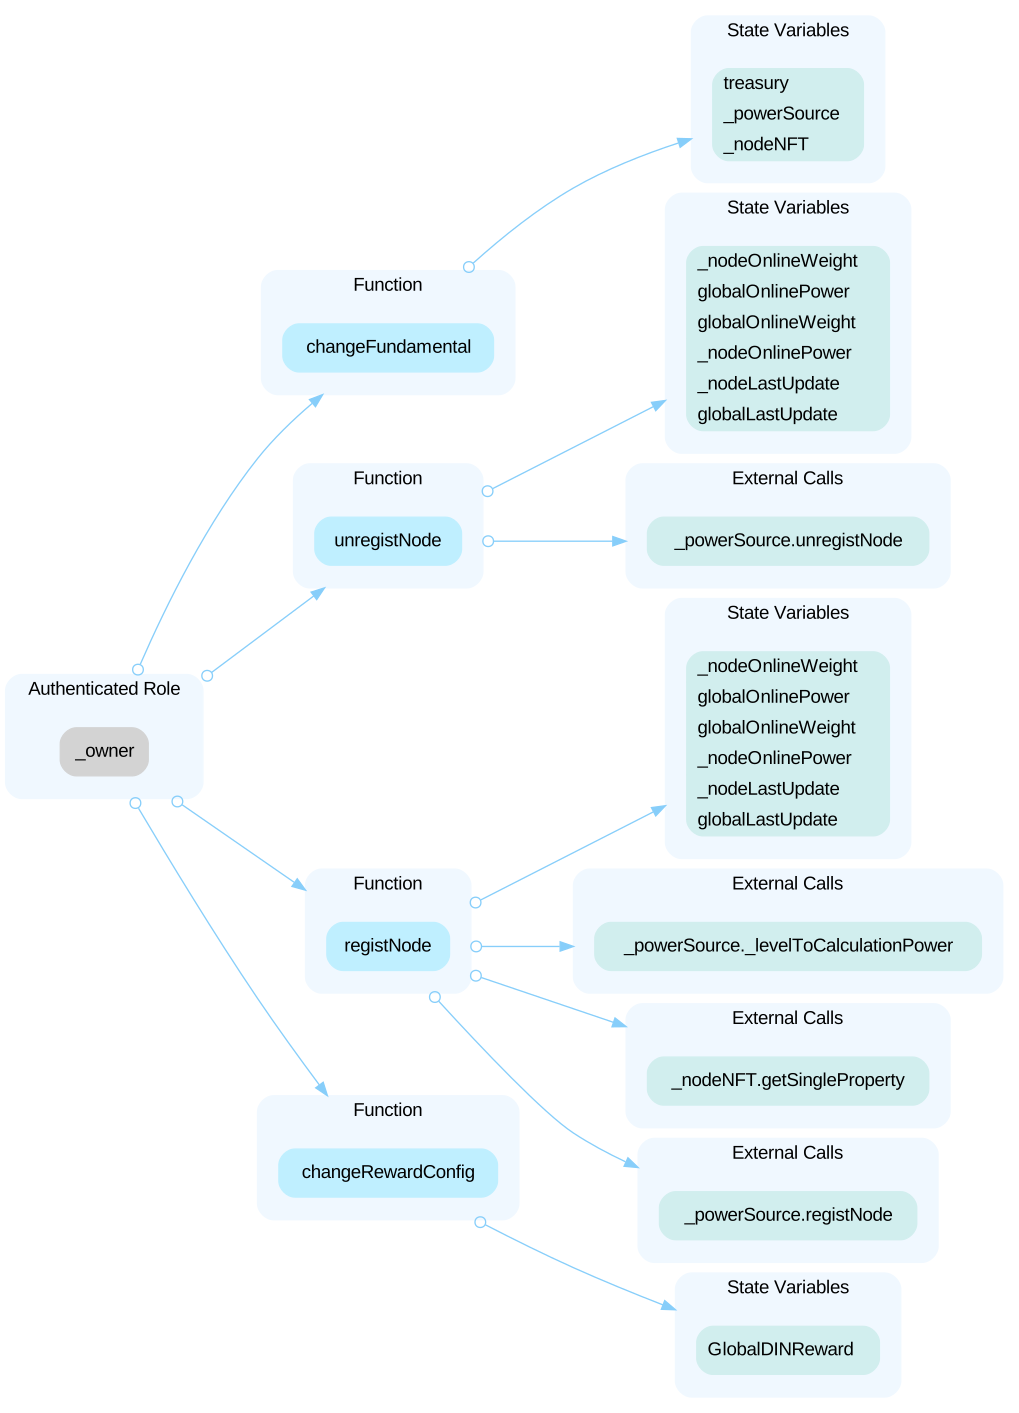 In the contract `OwnableUpgradeable`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and add a manager to the managers list, renounce ownership rights, transfer contract ownership to a new address, or remove a manager. 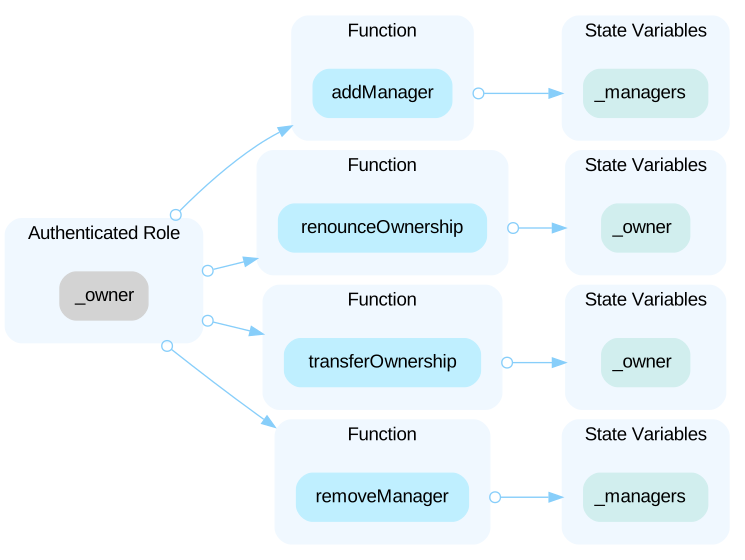 ----- In the contract `NFTAirdrop`, the role `_owner` has authority over the functions shown in the diagram below. The `_owner` role is tasked with defining the anticipated schedule for each power level, which includes setting the `amount`, `tgePercent`, `tgeTimestamp`, and `duration`. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change the console configuration or update the schedule type for a specific power level, which may affect the released amounts. 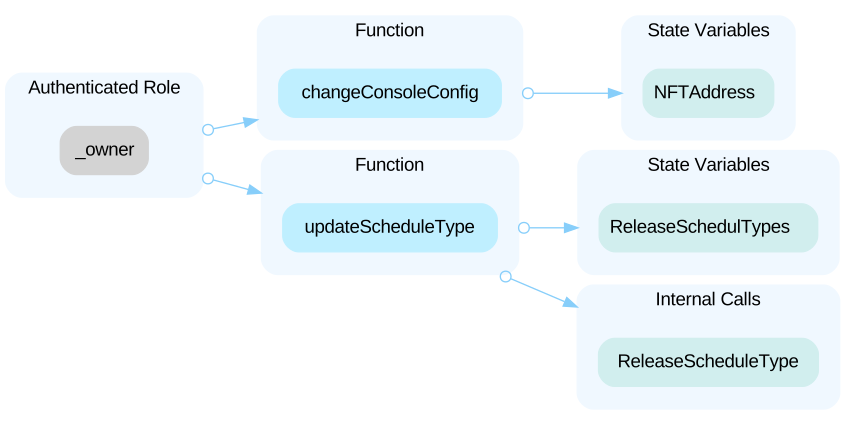 In the contract `OwnableUpgradeable`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advanta
Open the reportHighCentralized Balance ManipulationDIN · CertiK · 14 Jan 2025Acknowledged
In the contract `DIN`, the role `onlyManager` has the authority to mint the token balance of an arbitrary account without sanity restriction. ```solidity function mint(address receipt, uint256 amount) public onlyManager { _mint(receipt, amount); } ``` Any compromise to the `onlyManager` role may allow a hacker to take advantage of this authority and manipulate users' balances.
Open the reportHighCentralized Control of Contract UpgradeDIN · CertiK · 14 Jan 2025Acknowledged
In the contracts `CurveStaking`, `newStakingNative`, `NFTAirdropNative` and `xDINConvertingNative`, the role `admin` has the authority to update the implementation contract. Any compromise to the `admin` account may allow a hacker to take advantage of this authority and change the implementation contract which is pointed by proxy and therefore execute potential malicious functionality in the implementation contract.
Open the reportMediumSources of Rewards Available for Claim ExecutionDIN · CertiK · 14 Jan 2025Acknowledged
Based on the design of the staking-related contracts outlined above, the reward amounts used for calculation and distribution are fixed at the time of contract initialization. To ensure that users can claim rewards successfully, we would like to confirm with the team when the rewards will be transferred to the contract and whether the transferred amounts align with the initially specified reward amounts. Specifically, in the `CurveStaking` contract, where the staking token and reward token are the same, if rewards are not promptly transferred to the contract, claims may deplete other users' staked tokens. Besides, if enough rewards are sent to the contracts, there is also no function to withdraw the undistributed rewards.
Open the reportContracts1
| Address | Chain | Source code |
|---|---|---|
| 0x3ab1a5f76e12202d1ad1548a08a799501581da4e | Chain: BNB Chain | Source code: Verified source |
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="din-previously-web3go"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us