
Edge Matrix Computing security record
As of 3 Nov 2026, Edge Matrix Computing has 2 audit reports by 1 security firm on Trustblock; the latest is by CertiK, dated 15 Oct 2024. Those reports list no open critical findings.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Audits2
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| EMC Finance & Bridge | Security firm: CertiK | Date: | Scope: Files named in the report | 1 critical finding, fixed | Open · skynet.certik.com |
| EdgeMatrix Computing Protocol 2(EMC 2) | Security firm: CertiK | Date: | Scope: Files named in the report | 1 critical finding, fixed | Open · skynet.certik.com |
Findings61
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 2 |
| High | 1 | 4 | 4 |
| Medium | 0 | 3 | 4 |
| Low | 13 | 0 | 30 |
HighCentralization Related RisksEdgeMatrix Computing Protocol 2(EMC 2) · CertiK · 2 Feb 2024Open
In the contract `MerkleClaim` the role `_owner` has authority over the functions shown in the diagram below. 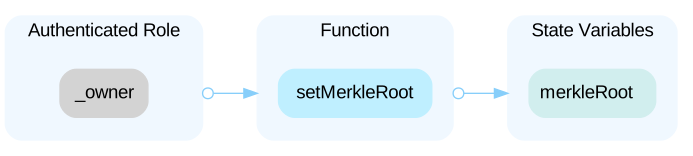 Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and do the following: - replace `merkleRoot` and generate new `merkleProofs` to claim the tokens in the contract. In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. 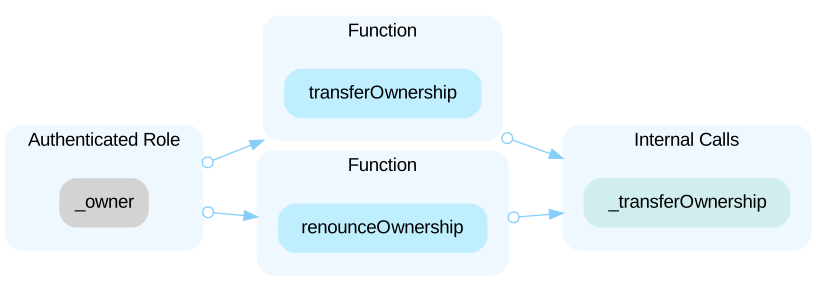 Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and do the following: - transfer ownership to zero address. - transfer ownership to a specific address. --- In the contract `NodeStakeV1` the role `manager` has authority over the functions shown in the diagram below. 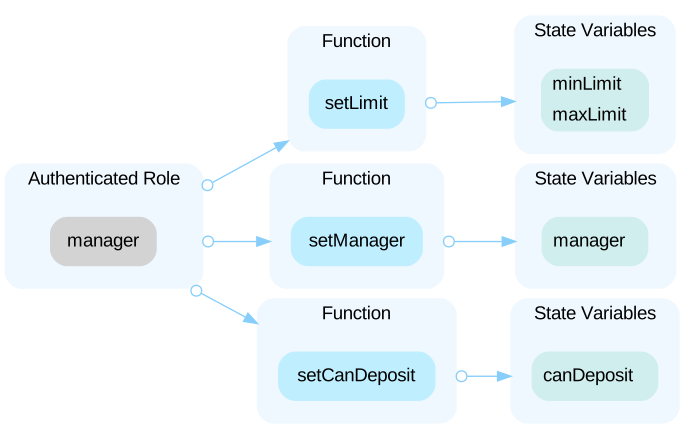 Any compromise to the `manager` account may allow the hacker to take advantage of this authority and do the following: - set upper and lower deposit limits. - turn on or turn off the deposit function. - update `manager` address.
Open the reportLow`_chainID` can be arbitraryEMC Finance & Bridge · CertiK · 15 Oct 2024Open
The `Bridge._chainID` is set in the constructor and can be arbitrary. It is not used by the contract. According to the parameter description: ```sol=113 @param chainID ID of chain the Bridge contract exists on. ``` The `chainID` should represent the ID of the chain on which the contract is deployed. To ensure accuracy, it is recommended to use: ```sol uint256 chainId; assembly { chainId := chainid() } ```
Open the reportLow`_setRoleAdmin` to `DEFAULT_ADMIN_ROLE` Is RedundEMC Finance & Bridge · CertiK · 15 Oct 2024Open
The specific role is assigned with `DEFAULT_ADMIN_ROLE` as the role admin. However, the assignment here is redundant, as `DEFAULT_ADMIN_ROLE` will be the role admin for any role by default.
Open the reportLow`approve()` And `transferFrom()` Are Subject To FEMC Finance & Bridge · CertiK · 15 Oct 2024Open
The `approve()` and `transferFrom()` functions are vulnerable to front-run attacks. This is because the `approve()` method overwrites the current allowance without checking if the spender has already used it. Consequently, if the spender has already spent the amount, the `approve` function will still approve a new amount.
Open the reportLowAssembly UsageEMC Finance & Bridge · CertiK · 15 Oct 2024Open
The smart contract contains assembly code blocks, which enable direct interaction with the Ethereum Virtual Machine (EVM) and permits developers to write low-level code that manipulates the EVM. This low-level access is error-prone and can introduce complexity, vulnerabilities, and logic errors. ```sol=102 assembly { amount := calldataload(0xC4) recipientAddress := mload(0x40) lenRecipientAddress := calldataload(0xE4) mstore(0x40, add(0x20, add(recipientAddress, lenRecipientAddress))) calldatacopy( recipientAddress, // copy to destinationRecipientAddress 0xE4, // copy from calldata @ 0x104 sub(calldatasize(), 0xE) // copy size (calldatasize - 0x104) ) } ``` The code contains bugs: 0xE used instead of 0xE4. Offsets in GenericHandler are wrong. Some comments are misleading and contradict the code.
Open the reportLowFunction `_setupRole()` is DeprecatedEMC Finance & Bridge · CertiK · 15 Oct 2024Open
The use of function `_setupRole()` from inherited contract `AccessControlEnumerable` is deprecated in favor of directly calling internal function `_grantRole()`. Since function `_setupRole()` only calls function `_grantRole()`, it is more direct to use the latter function instead.
Open the reportLowMissing Emit EventsEMC Finance & Bridge · CertiK · 15 Oct 2024Open
There should always be events emitted in the sensitive functions that are controlled by centralization roles.
Open the reportLowPassed and Executed proposals can be cancelled byEMC Finance & Bridge · CertiK · 15 Oct 2024Open
```sol=469 require(proposal._status != ProposalStatus.Cancelled, "Proposal already cancelled"); ``` If expired, the proposal can be cancelled by the admin or relayer even if it was already executed. The status will be changed to Cancelled and the misleading event emitted.
Open the reportLowTransfer to Zero Address in WEMCEMC Finance & Bridge · CertiK · 15 Oct 2024Open
In the `WEMC` token implementation the lack of validation on the `to` parameter in the `transfer()` and `transferFrom()` functions allows tokens to be sent to the zero address. This may result in lost tokens or unexpected behavior.
Open the reportLowVariables That Could Be Declared as ImmutableEMC Finance & Bridge · CertiK · 15 Oct 2024Open
The linked variables assigned in the constructor can be declared as `immutable`. Immutable state variables can be assigned during contract creation but will remain constant throughout the lifetime of a deployed contract. A big advantage of immutable variables is that reading them is significantly cheaper than reading from regular state variables since they will not be stored in storage.
Open the reportShow 4 more
LowIncompatibility With Deflationary Tokens (Non-staEdgeMatrix Computing Protocol 2(EMC 2) · CertiK · 2 Feb 2024Open
The project design may not be compatible with non-standard ERC20 tokens, such as deflationary tokens or rebase tokens.
Open the reportLowPull-Over-Push Pattern In `transferOwnership()` FEdgeMatrix Computing Protocol 2(EMC 2) · CertiK · 2 Feb 2024Open
The change of `_owner` by function `transferOwnership()` overrides the previously set `_owner` with the new one without guaranteeing the new `_owner` is able to actuate transactions on-chain.
Open the reportLowThird-Party Dependency UsageEdgeMatrix Computing Protocol 2(EMC 2) · CertiK · 2 Feb 2024Open
The contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=461 address public immutable override token; ``` - The contract `MerkleClaim` interacts with third party contract with `IERC20` interface via `token`. --- ```solidity=39 IERC20 public immutable token; //Token's contract address for reward. Will be designated as EMC token (has been audited) contract address ``` - The contract `NodeStakeV1` interacts with third party contract with `IERC20` interface via `token`.
Open the reportLowUse of `abi.encodePacked()`EdgeMatrix Computing Protocol 2(EMC 2) · CertiK · 2 Feb 2024Open
As a general practice, use of `abi.encodePacked` isn't recommended, since it is susceptible to hash collisions in some instances where dynamically-sized inputs are used consecutively. While this is not the case in this instance, we also note that `abi.encodePacked` may be removed in future solidity versions (see this issue: [https://github.com/ethereum/solidity/issues/11593](https://github.com/ethereum/solidity/issues/11593)).
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="edge-matrix-chain"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us