
EgoCoin security record
As of 3 Nov 2026, EgoCoin has 1 audit report on Trustblock, by CertiK, dated 4 May 2023. That report lists no open critical findings.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Audits1
Newest first
Findings19
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 3 | 1 |
| Medium | 0 | 1 | 0 |
| Low | 8 | 0 | 6 |
HighCentralization Risks in EgoERC20GotBit.solEGO · CertiK · 4 May 2023Acknowledged
In the contract `EgoToken` the role `ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ADMIN_ROLE` account may allow the hacker to take advantage of this authority and modify the critical configuration of the contract, and move funds. 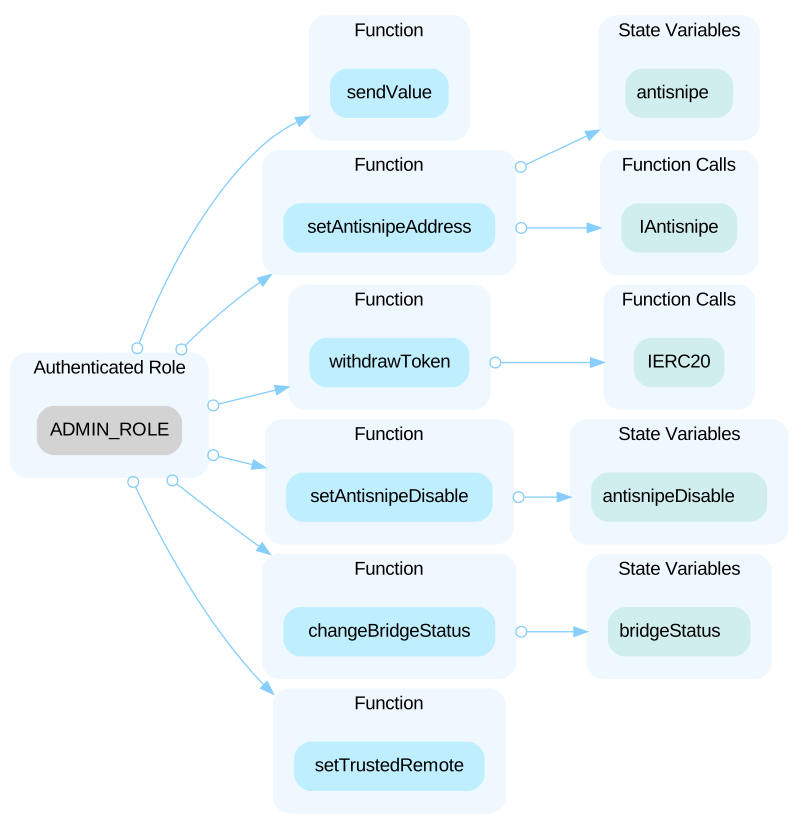 In the contract `EgoToken` the role `PAUSER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `PAUSER_ROLE` account may allow the hacker to take advantage of this authority and pause and unpause the project. 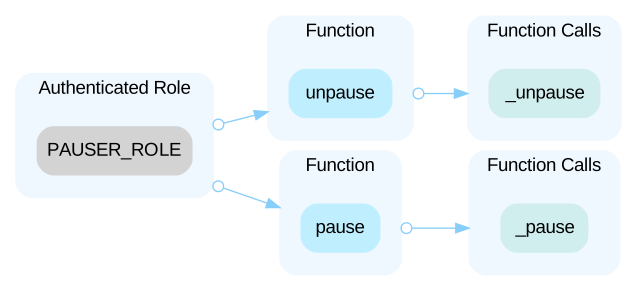
Open the reportHighCentralization Risks in StakingSample.solEGO · CertiK · 4 May 2023Acknowledged
In the contract `Staking` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify critical configurations of the contract. 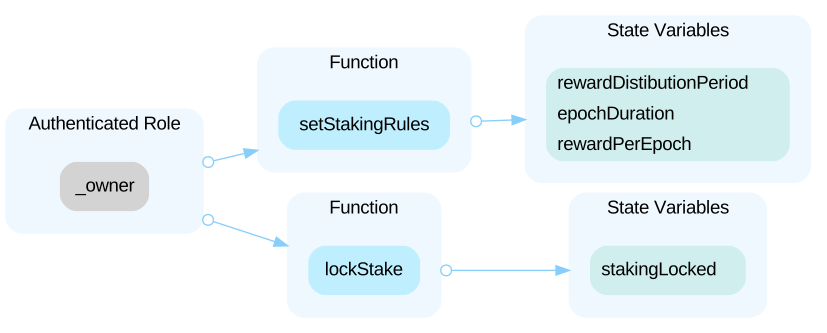
Open the reportHighInitial Token DistributionEGO · CertiK · 4 May 2023Acknowledged
All **EGO** tokens are sent to the "validator" address when deploying the contract. This is a potential centralization risk as the deployer can distribute the tokens without the consensus of the community.
Open the reportMediumOut of Scope DependenciesEGO · CertiK · 4 May 2023Acknowledged
The "EgoERC20GotBit.sol" serves as the underlying entity to interact with third-party **Axelar Library and system**. The scope of the audit treats third-party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. Additionally, In the "EgoERC20GotBit.sol" contract, two functions, "transferRemote" and "_execute," check if the message is signed by the validator. The validator is a complete black box, and the auditor cannot determine the behavior of the validator or how it decides if it should sign a message. The validator and it's code logic is out of the scope of the audit.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="ego"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us