
GOUT security record
As of 3 Nov 2026, GOUT has 1 audit report on Trustblock, by CertiK, dated 26 Nov 2024. That report lists no open critical findings. It also holds 1 deployed contract on 1 chain.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Audits1
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| GOUT - Audit | Security firm: CertiK | Date: | Scope: 1 address on BNB Chain | No open critical findings | Open · skynet.certik.com |
Findings16
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 5 | 0 |
| Medium | 0 | 2 | 0 |
| Low | 9 | 0 | 0 |
HighArbitrage Exploitation of `_transfer()` FunctionGOUT - Audit · CertiK · 26 Nov 2024Acknowledged
The `_transfer()` function includes a burn mechanism using `autoBurnUniswapPair()` designed to reduce the reserve of tokens in the `_autoPair` and potentially increase the token's price. When the transaction is interacting with the `_autoPair`, it may trigger `autoBurnUniswapPair()`. A vulnerability arises when a malicious user takes advantage of the burn mechanism, easpecially in case the accumlated fee in the contract is less than the `minSwapFee`. This mechanism can be exploited by a malicious actor through the following steps: 1. The actor obtains a large number of tokens, possibly using a flash loan for the initial purchase, which provides them with significant capital without upfront investment. 2. After acquiring the tokens, the actor waits for the burn mechanism to be triggered, reducing the overall token supply. 3. Once the burn has taken place, the actor sells the tokens back to the pool, capitalizing on the increased token price due to the reduced supply.
Open the reportHighCentralization Risks in GOUT.solGOUT - Audit · CertiK · 26 Nov 2024Acknowledged
In the contract `GOUT`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and: - `receiveToken`, transfer all the ETH and any type of ERC20 tokens to the owner - `setExcludeFee`, set exclude fee for multiple addresses - `addLiquidity`, add liquidity using ETH and tokens - `setAutoLPBurnSettings`, set auto LP burn settings - `setLaunch`, set the launch status 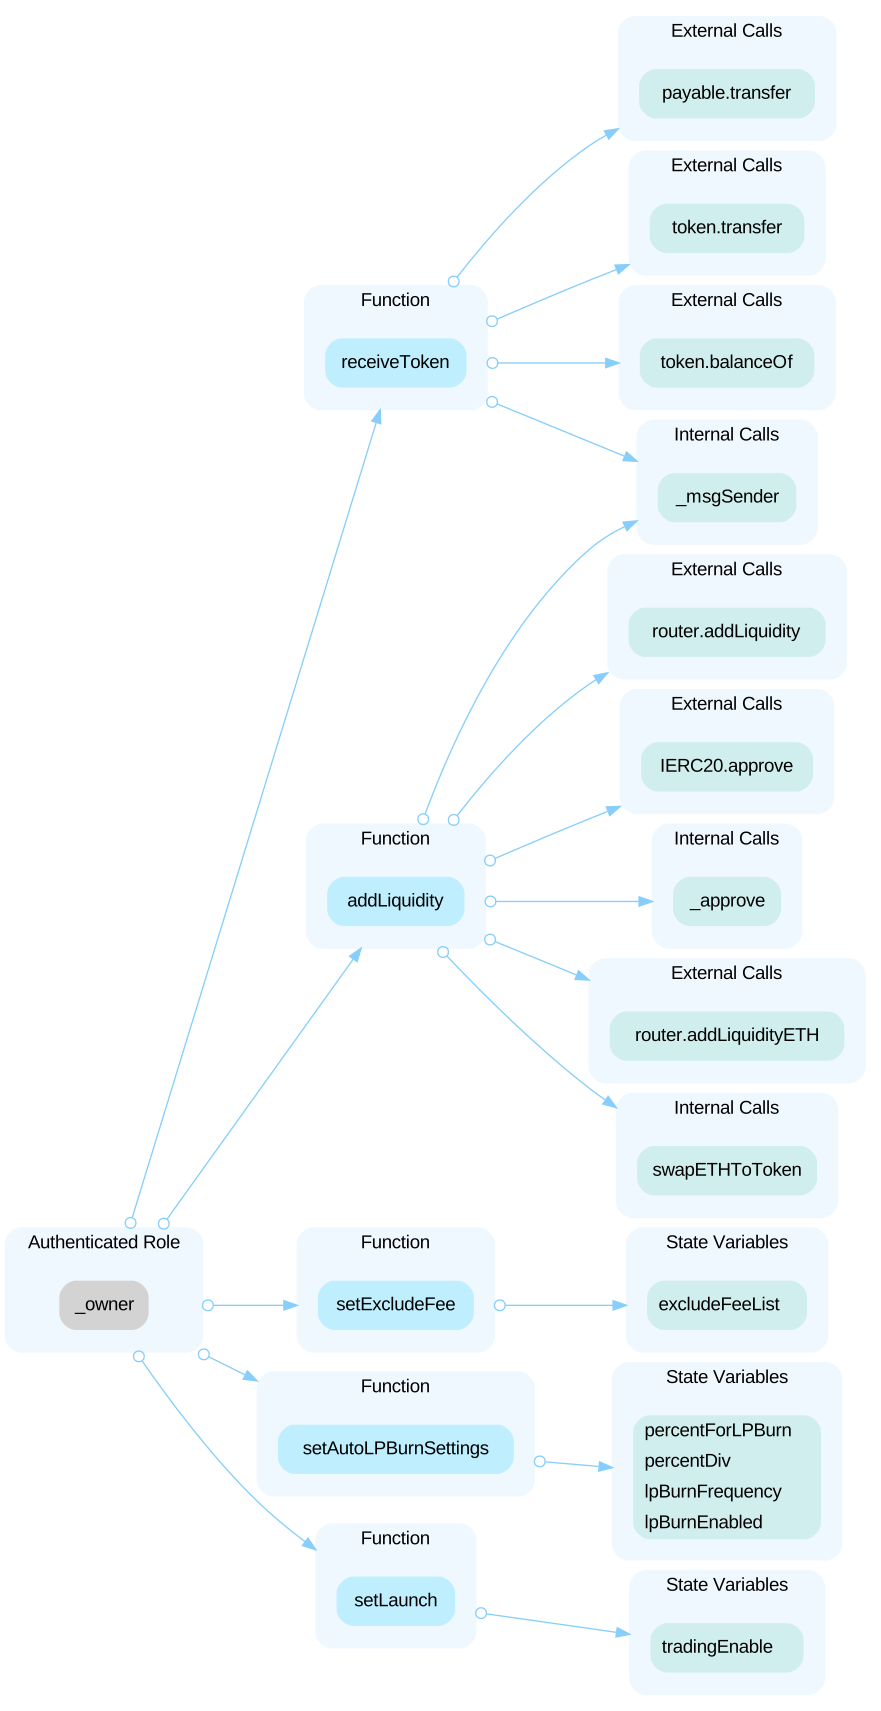 In the contract `Ownable`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer contract ownership or renounce ownership rights. 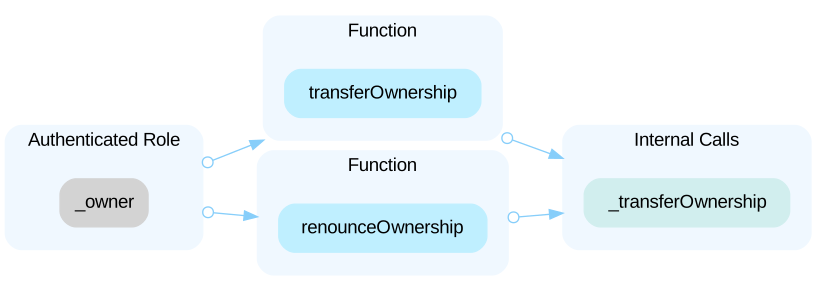
Open the reportHighIncorrect Fee Calculation in `withdrawETH` FunctiGOUT - Audit · CertiK · 26 Nov 2024Acknowledged
The `withdrawETH` function is used for users to sell tokens to the contract and receive ETH. However, it would always revert due to a faulty fee calculation. The problematic line: ```solidity uint256 fee = (amount * feeBase) / feeTotal; ``` uses `feeBase` set to 10,000 and `feeTotal` set to 100, resulting in an effective multiplier of 100 for the fee. This causes the calculated fee to be 100 times the amount, leading to an underflow in the `amount -= fee` operation, and consequently causing the function to revert. This issue makes the `withdrawETH` function unusable and creates a critical barrier to withdrawal functionality.
Open the reportHighInitial Token DistributionGOUT - Audit · CertiK · 26 Nov 2024Acknowledged
All GOUT tokens are sent to the contract and the `_owner` address. This is a centralization risk because the `_owner` can distribute tokens without obtaining the consensus of the community. Any compromise to the address may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
Open the reportHighUnrestricted Token and BNB Withdrawal via `receivGOUT - Audit · CertiK · 26 Nov 2024Acknowledged
The `receiveToken()` function allows the `_owner` to withdraw both BNB and any ERC20 tokens (e.g., GOUT tokens) from the contract without restrictions. This can pose significant risks, as it grants the `_owner` full control over the contract's assets without any limitations or conditions. ```solidity=1389 function receiveToken(address _addr) public onlyOwner { if (_addr == address(0)) { payable(_msgSender()).transfer(address(this).balance); } else { IERC20 token = IERC20(_addr); token.transfer(_msgSender(), token.balanceOf(address(this))); } } ```
Open the reportMediumCalculation Logic and Manipulation Risk in `getWiGOUT - Audit · CertiK · 26 Nov 2024Acknowledged
The `getWithdrawOut()` function is designed to calculate the amount of BNB a user would receive by selling GOUT tokens. The auditor has identified potential concerns regarding the calculation logic and potential manipulation risks associated with this function. Below are the two main questions raised, along with a discussion on their implications. ### Questions for Clarification: 1. **Calculation Logic Using `total + amountIn`:** The function divides `amountIn * address(this).balance` by `total + amountIn` instead of just `total`. This implies that when a user sells all circulating GOUT tokens, they will only receive half of the contract's BNB balance, rather than the full balance. 2. **Manipulation of `total` by the Seller:** the `total` value in the calculation is derived from the `totalSupply()` minus the balances of the `0xdead` address and liquidity pools (`pairETH` and `pairUSDT`). A seller could potentially manipulate `total` by swapping BNB for GOUT to increase the token balance in the `pairETH` address. This would decrease `total`, resulting in a higher amount of BNB received when selling GOUT. ```solidity=1346 function getWithdrawOut(uint256 amountIn) public view returns (uint256) { uint256 total = totalSupply() - balanceOf(address(0xdead)) - balanceOf(pairETH) - balanceOf(pairUSDT); return (amountIn * address(this).balance) / (total + amountIn); } ```
Open the reportMediumMissing Restriction on Multiple Calls to `addLiquGOUT - Audit · CertiK · 26 Nov 2024Acknowledged
The `addLiquidity` function, designed to add initial liquidity, can currently be called multiple times without restriction. The project allows users to sell tokens to the contract, which could lead to the contract accumulating a substantial amountInToken. The contract owner could repeatedly call the addLiquidity function, using these accumulated tokens to gain LP tokens.
Open the reportContracts1
| Address | Chain | Source code |
|---|---|---|
| 0xf86af2fbcf6a0479b21b1d3a4af3893f63207fe7 | Chain: BNB Chain | Source code: Verified source |
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="gout"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us