
Guardians of the Ball audit reports
Guardians of the Ball has 1 public audit report from CertiK; dated 9 Nov 2023; no critical findings reported.
Last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Open findings across every firm3
Statuses are the security firms’ own
3 findings are still open or acknowledged in the firms’ reports: 3 high (all open).
- High
- 3
- High Open
Centralization Related Risks
Guardians of the Ball - GOBAL OTC Sales and Market · CertiK · 9 Nov 2023 · Report ↗
- High Open
Initial Token Distribution
Guardians of the Ball - GOBAL OTC Sales and Market · CertiK · 9 Nov 2023 · Report ↗
- High Open
The privileged role is allowed to withdraw tokens
Guardians of the Ball - GOBAL OTC Sales and Market · CertiK · 9 Nov 2023 · Report ↗
Audits1
Newest first
| Report | Security firm | Date | Scope | Critical findings | Findings | Source |
|---|---|---|---|---|---|---|
| Guardians of the Ball - GOBAL OTC Sales and Market | Security firm: CertiK | Date: | Scope: Files listed | None open | Findings: 3 high · 8 low 8 fixed · 3 open | Original removed |
Findings11
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 3 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 0 | 8 |
HighCentralization Related RisksGuardians of the Ball - GOBAL OTC Sales and Market · CertiK · 9 Nov 2023Open
In the contract `GOBMarket` the role `MANAGER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MANAGER_ROLE` account may allow the hacker to take advantage of this authority and set vesting contract address, add or remove ERC1155 tokens supported by the market, and add or remove currency tokens supported by the market. 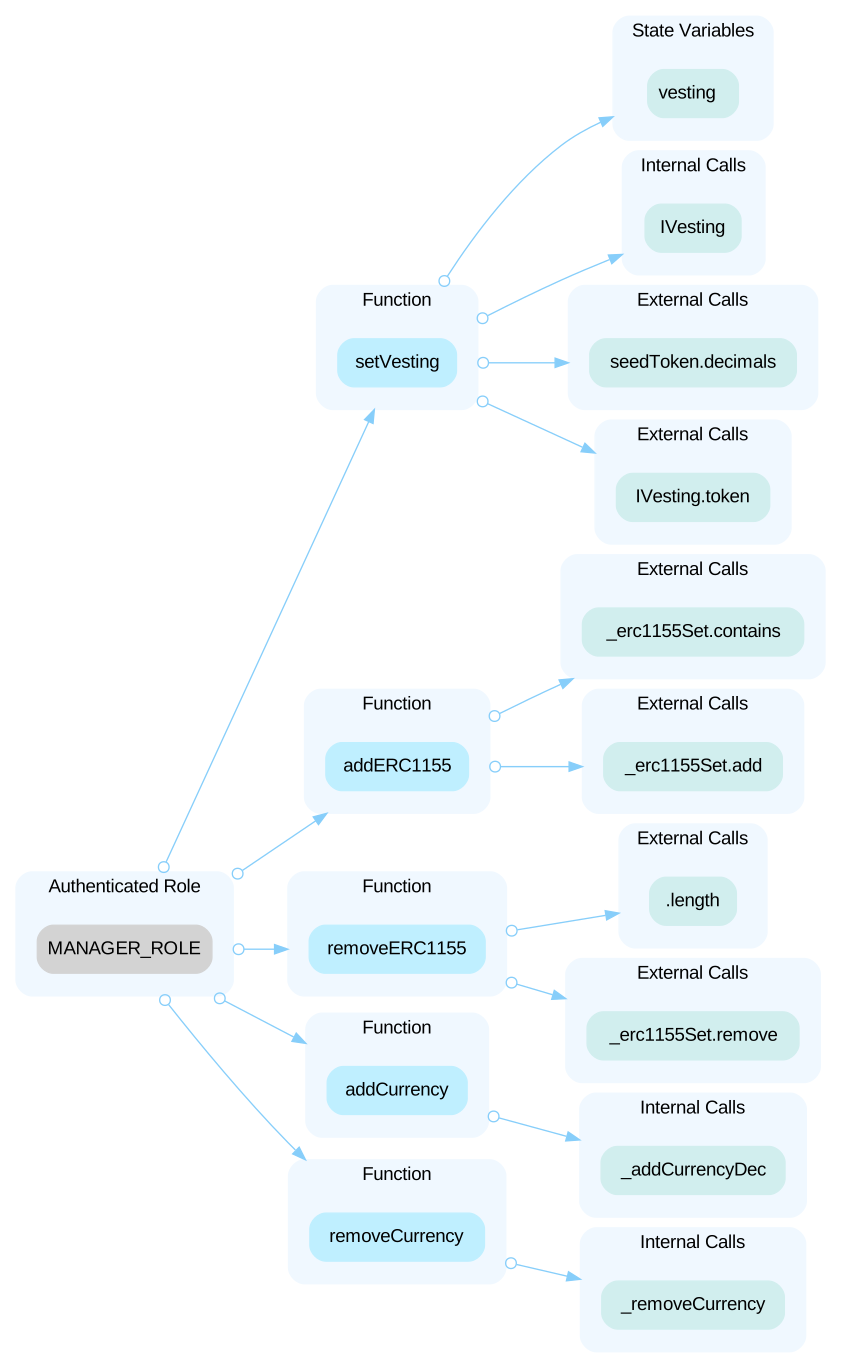 In the contract `GOBMarket` the role `SELLER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `SELLER_ROLE` account may allow the hacker to take advantage of this authority and update the sensitive settings of the market. 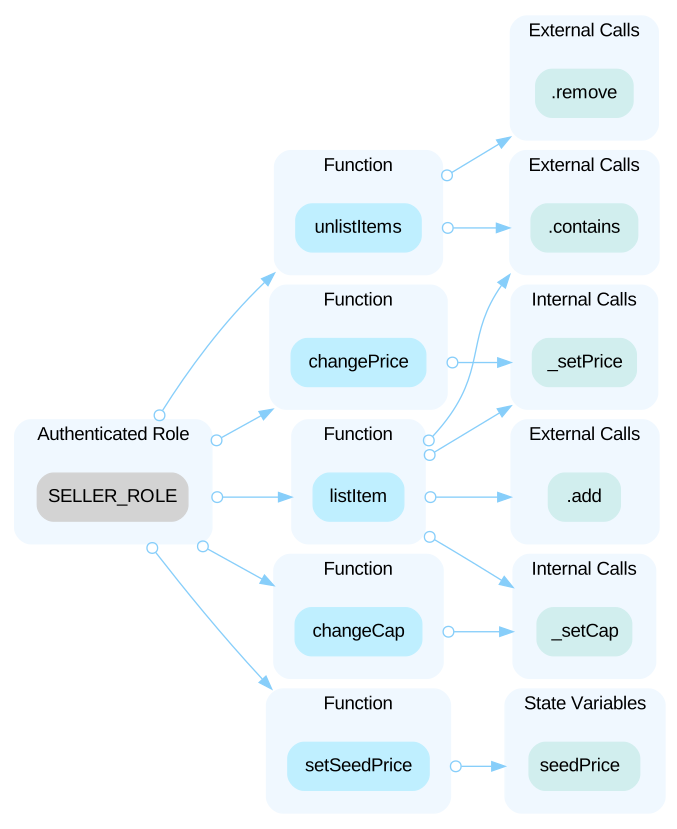 In the contract `GOBMarket` the role `WITHDRAW_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `WITHDRAW_ROLE` account may allow the hacker to take advantage of this authority and withdraw tokens from the market. 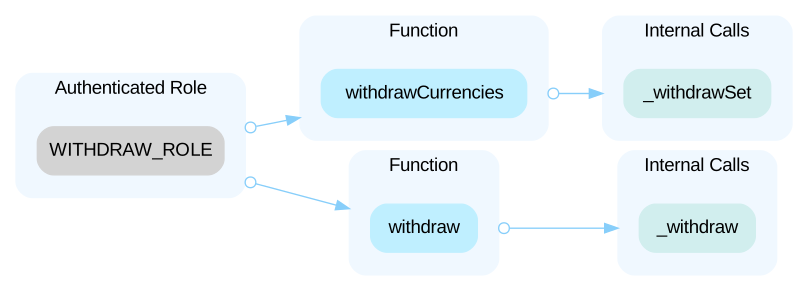 In the contract `GOBMarket` the role `DEFAULT_ADMIN_ROLE` is the admin of `MANAGER_ROLE`, `SELLER_ROLE` and `WITHDRAW_ROLE`. Any compromise to the `DEFAULT_ADMIN_ROLE` account can grant a hacker the authority associated with these roles. ----- In the contract `OTCController` the role `PRICE_MANAGER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `PRICE_MANAGER_ROLE` account may allow the hacker to take advantage of this authority and `setPrice()` for purchasing tokens, add or remove currency tokens supported by OTC. 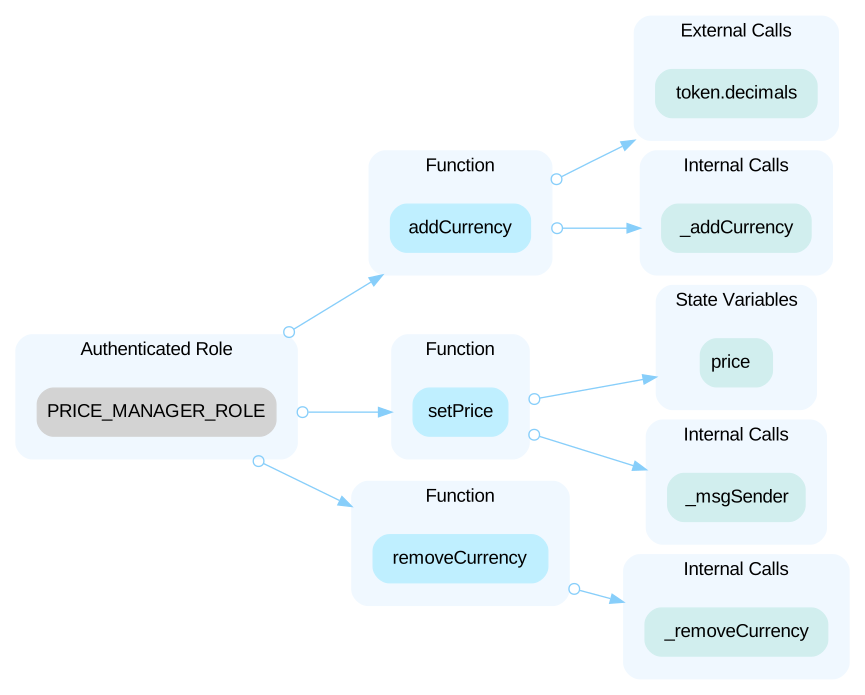 In the contract `OTCController` the role `SALES_TRIGGERER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `SALES_TRIGGERER_ROLE` account may allow the hacker to take advantage of this authority and open or close sales. 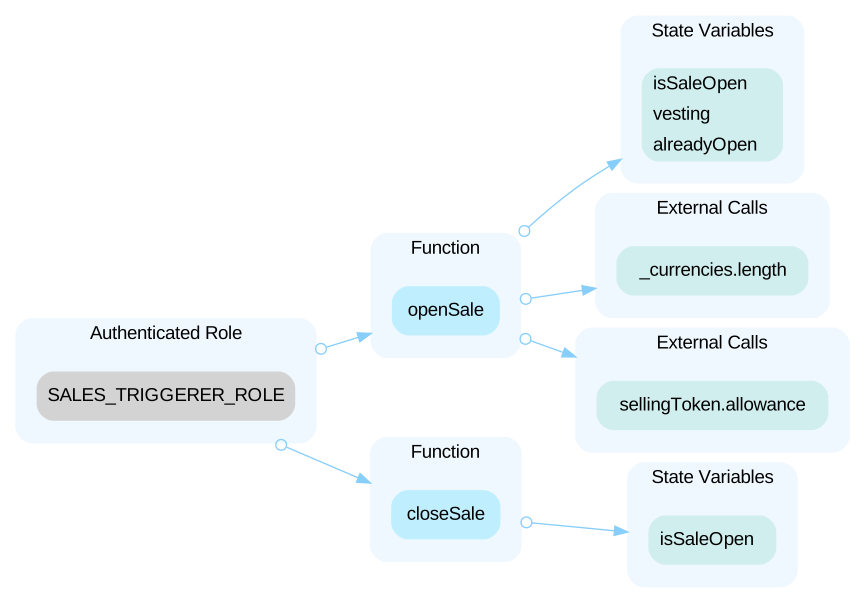 In the contract `OTCController` the role `WITHDRAW_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `WITHDRAW_ROLE` account may allow the hacker to take advantage of this authority and withdraw tokens from the contract. 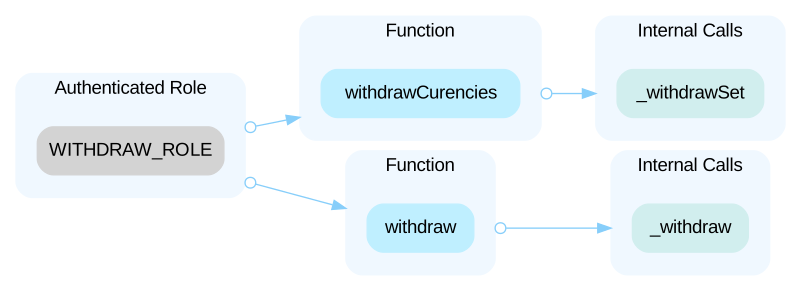 In the contract `OTCController` the role `DEFAULT_ADMIN_ROLE` is the admin of `PRICE_MANAGER_ROLE`, `SALES_TRIGGERER_ROLE` and `WITHDRAW_ROLE`. Any compromise to the `DEFAULT_ADMIN_ROLE` account can grant a hacker the authority associated with these roles. ----- In the contract `Vesting` the role `AUTHORIZED_SPENDER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `AUTHORIZED_SPENDER_ROLE` account may allow the hacker to take advantage of this authority and withdraw tokens from the contract. 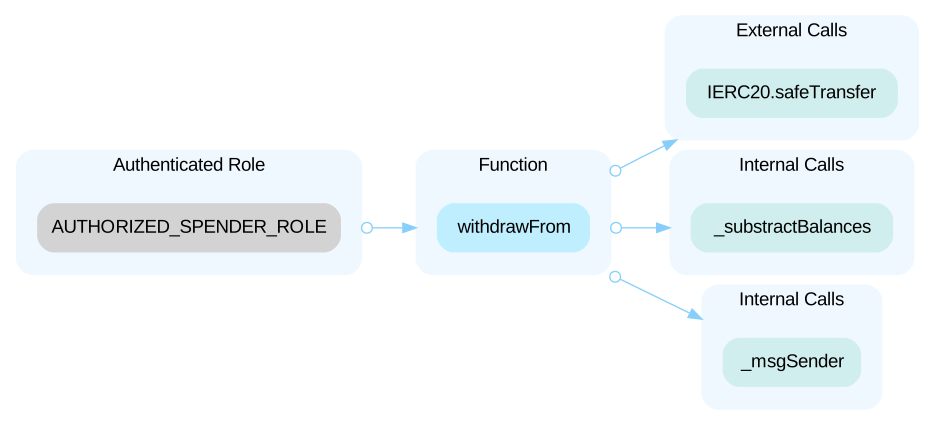 In the contract `Vesting` the role `AUTHORIZER_ROLE` is the admin of `AUTHORIZED_SPENDER_ROLE`. Any compromise to the `AUTHORIZER_ROLE` account can grant a hacker the authority associated with this role. In the contract `Vesting` the role `OTC_CONTROLLER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `OTC_CONTROLLER_ROLE` account may allow the hacker to take advantage of this authority. 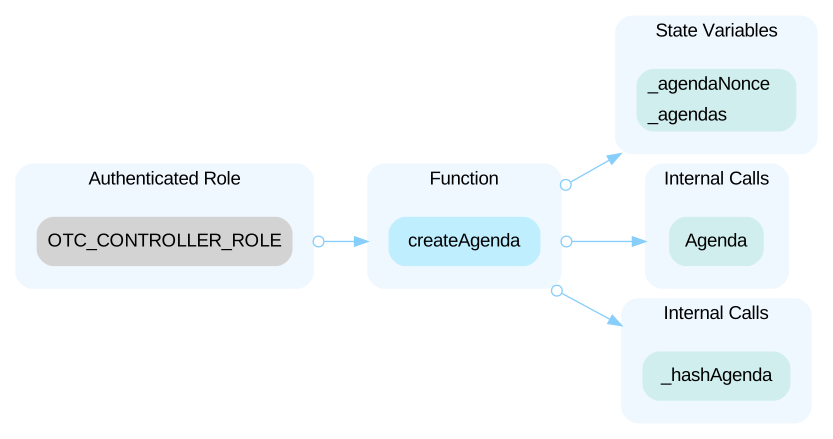
Open the reportHighInitial Token DistributionGuardians of the Ball - GOBAL OTC Sales and Market · CertiK · 9 Nov 2023Open
All of the GuardiansOfTheBallToken tokens are sent to the contract deployer. This is a centralization risk because the deployer can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
Open the reportHighThe privileged role is allowed to withdraw tokensGuardians of the Ball - GOBAL OTC Sales and Market · CertiK · 9 Nov 2023Open
The `withdrawFrom()` function is a sensitive function that permits the `AUTHORIZED_SPENDER_ROLE` to withdraw funds acquired by users through OTC purchases. It is intended to be called by the `GOBMarket._buyItem()` function to process payments for users who call `buyItemWithVesting()` and utilize the `BuyWith.SeedTokenVested` option when buying ERC1155 tokens. The admin of the `AUTHORIZED_SPENDER_ROLE` is `AUTHORIZER_ROLE`. The granting of the `AUTHORIZED_SPENDER_ROLE` to multiple wallets poses a security vulnerability if any of these wallets were to compromise the private key.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Guardians of the Ball: questions
Is Guardians of the Ball audited?
Trustblock holds 1 public audit report for Guardians of the Ball, dated 9 Nov 2023. The latest is by CertiK (“Guardians of the Ball - GOBAL OTC Sales and Market”).
Who audited Guardians of the Ball?
CertiK wrote the report Trustblock holds for Guardians of the Ball.
Are there open findings in Guardians of the Ball’s audits?
3 findings are still open or acknowledged in the firms’ reports: 3 high (all open). No critical finding is reported. Statuses are the security firms’ own.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="guardians-of-the-ball"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us