As of 2 Nov 2026, Hector Network has 2 audit reports by 1 security firm on Trustblock; the latest is by CertiK, dated 19 Dec 2023. Those reports list no open critical findings.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| Hector Network (Redemption System) Audit | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Original removed |
| Hector Network (Audit 2) | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Original removed |
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 2 |
| Medium | 1 | 0 | 2 |
| Low | 5 | 0 | 9 |
In the contract `RedemptionNFT` the role `PAUSER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `PAUSER_ROLE` account may allow the hacker to take advantage of this authority and pause/unpause the transfer of FNFTs. 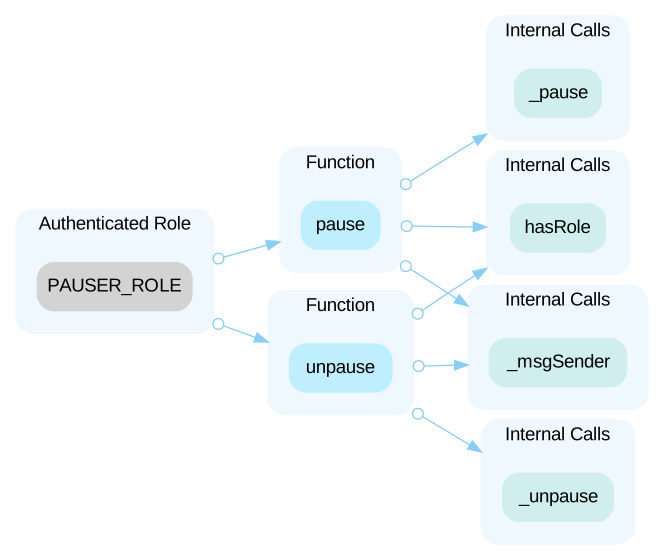 In the contract `RedemptionNFT` the role `_moderator` has authority over the functions shown in the diagram below. Any compromise to the `_moderator` account may allow the hacker to take advantage of this authority and mint tokens to hacker address. 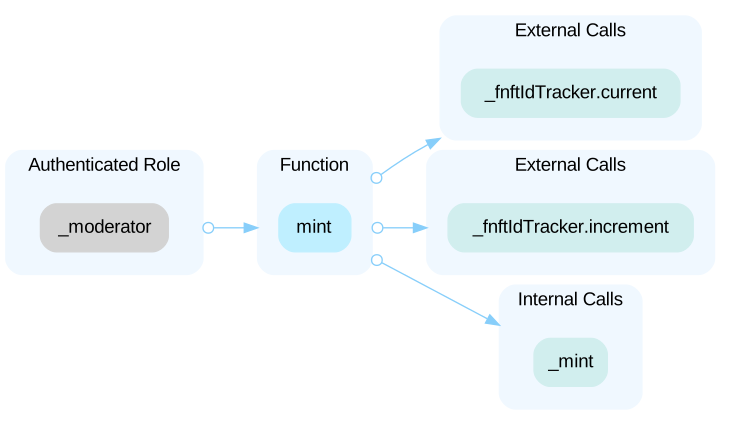 ----- In the contract `HectorRedemption` the role `_moderator` has authority over the functions shown in the diagram below. Any compromise to the `_moderator` account may allow the hacker to take advantage of this authority and withdraw all tokens. 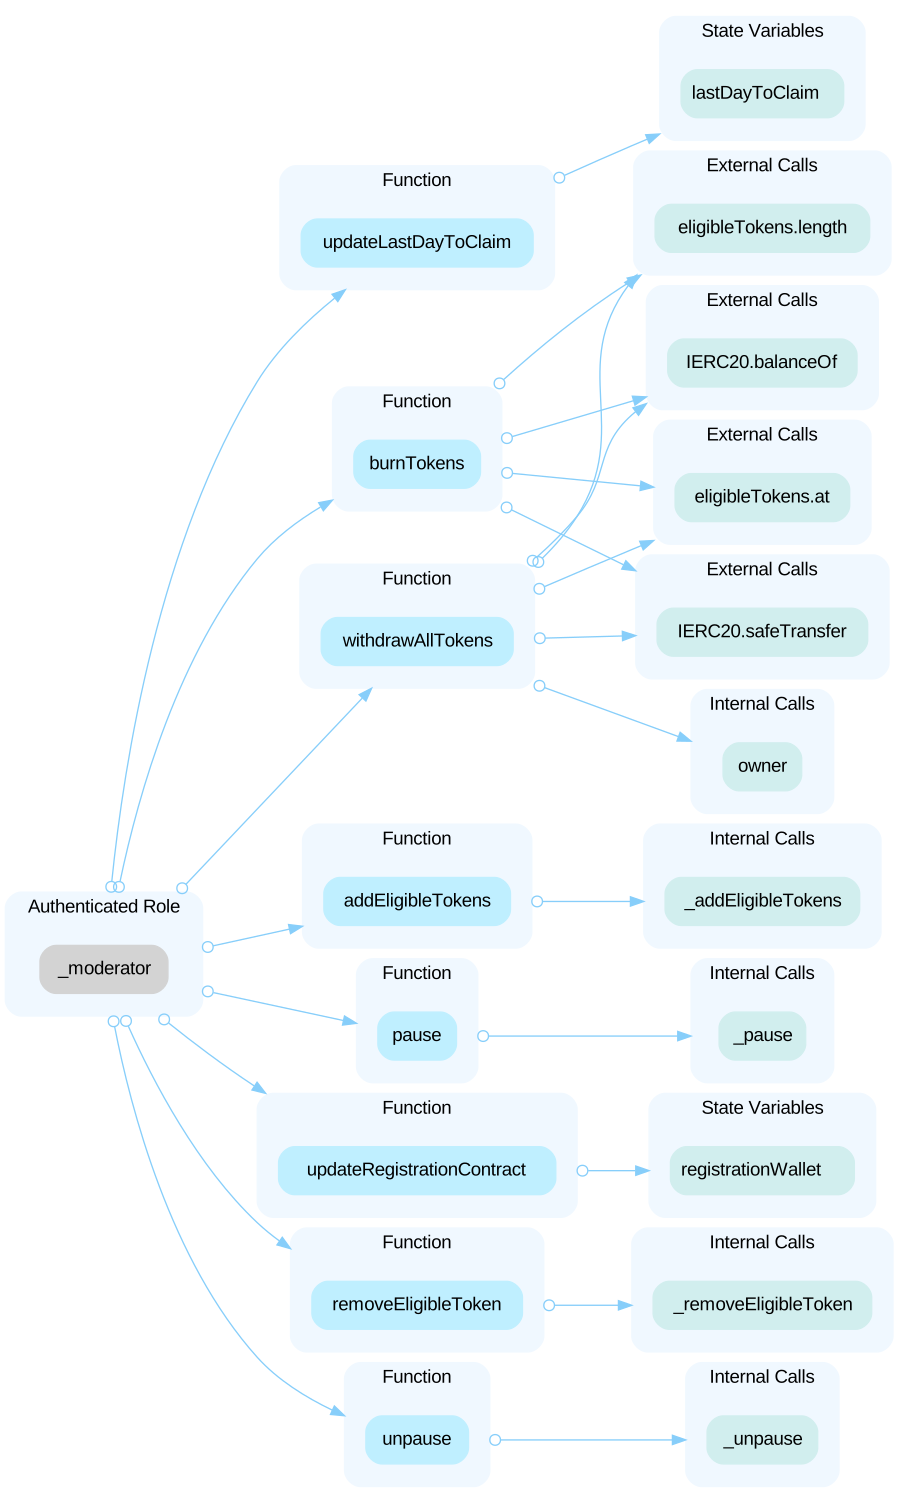 ----- In the contract `HectorRedemptionTreasury` the role `_moderator` has authority over the functions shown in the diagram below. Any compromise to the `_moderator` account may allow the hacker to take advantage of this authority and withdraw all tokens. 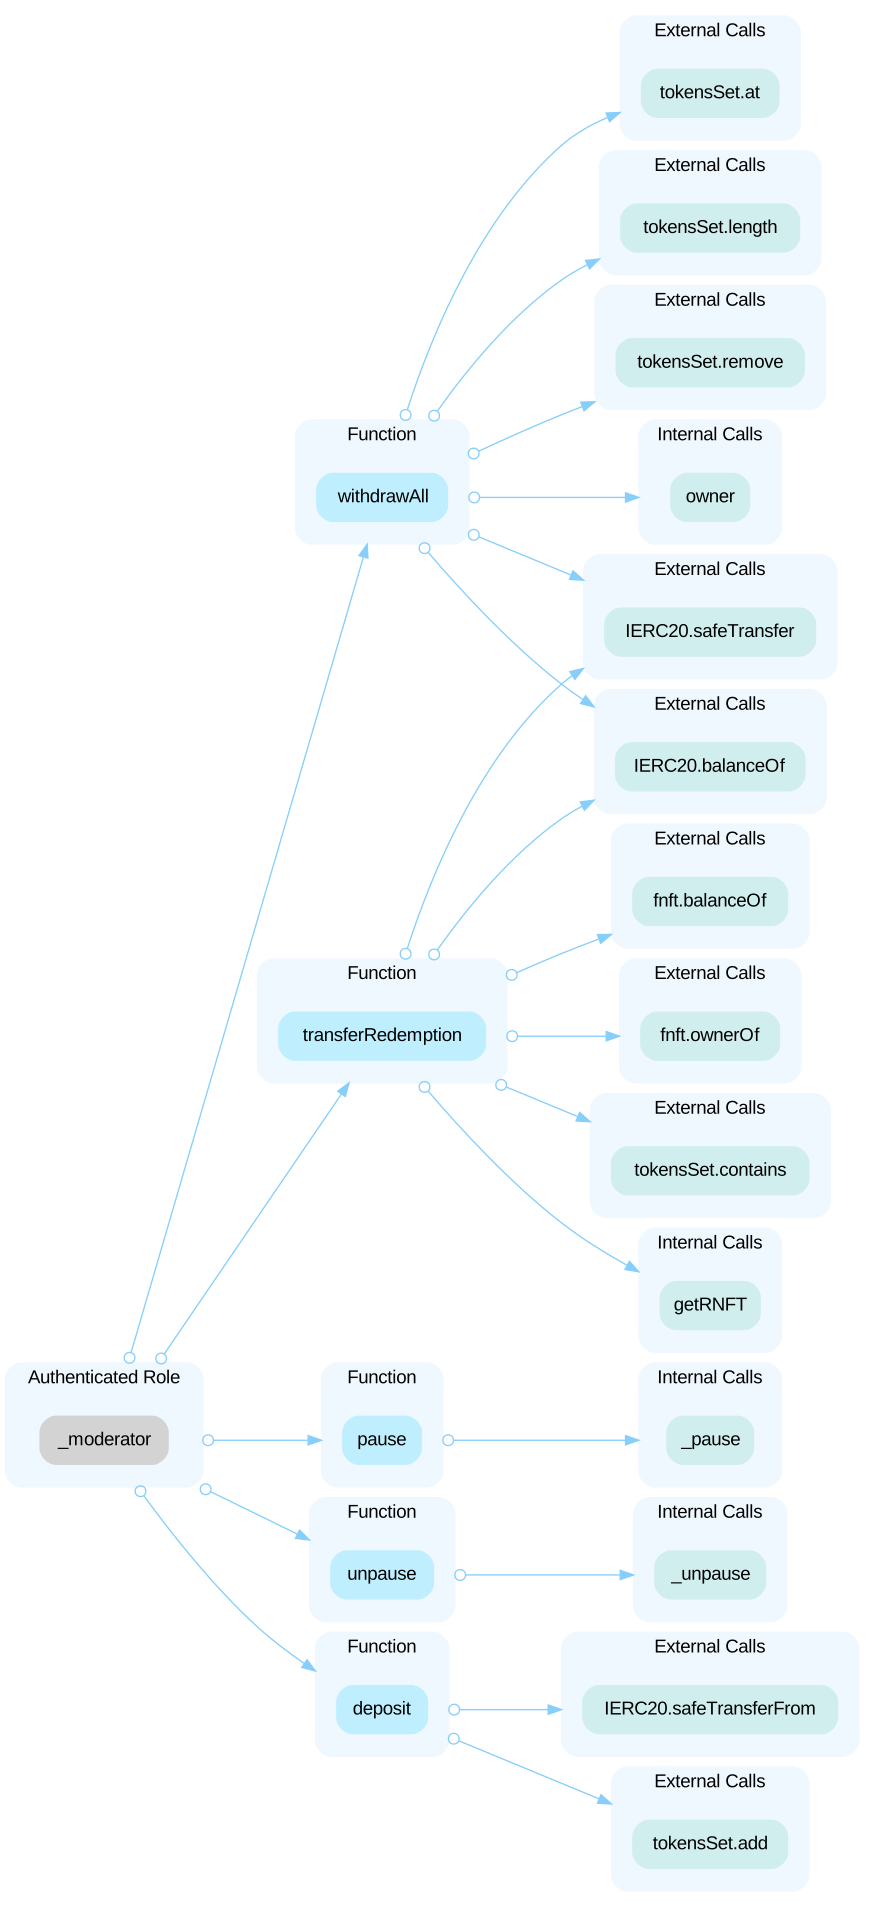 ----- In the contract `LockAccessControl` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change `addressProvider`. 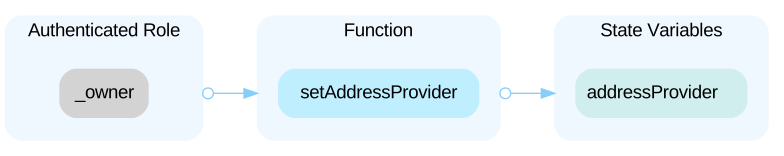 ----- In the contract `LockAddressRegistry` the role `MODERATOR_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MODERATOR_ROLE` account may allow the hacker to take advantage of this authority and set moderators. 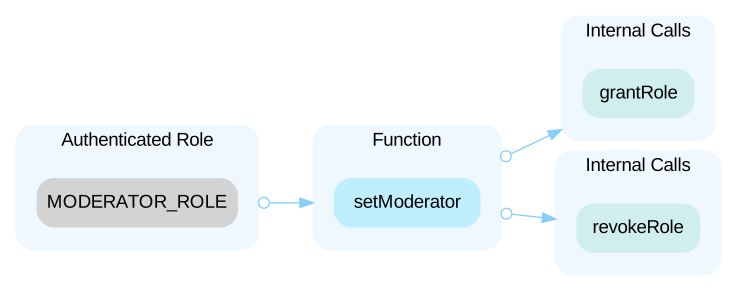 In the contract `LockAddressRegistry` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change important contract addresses. 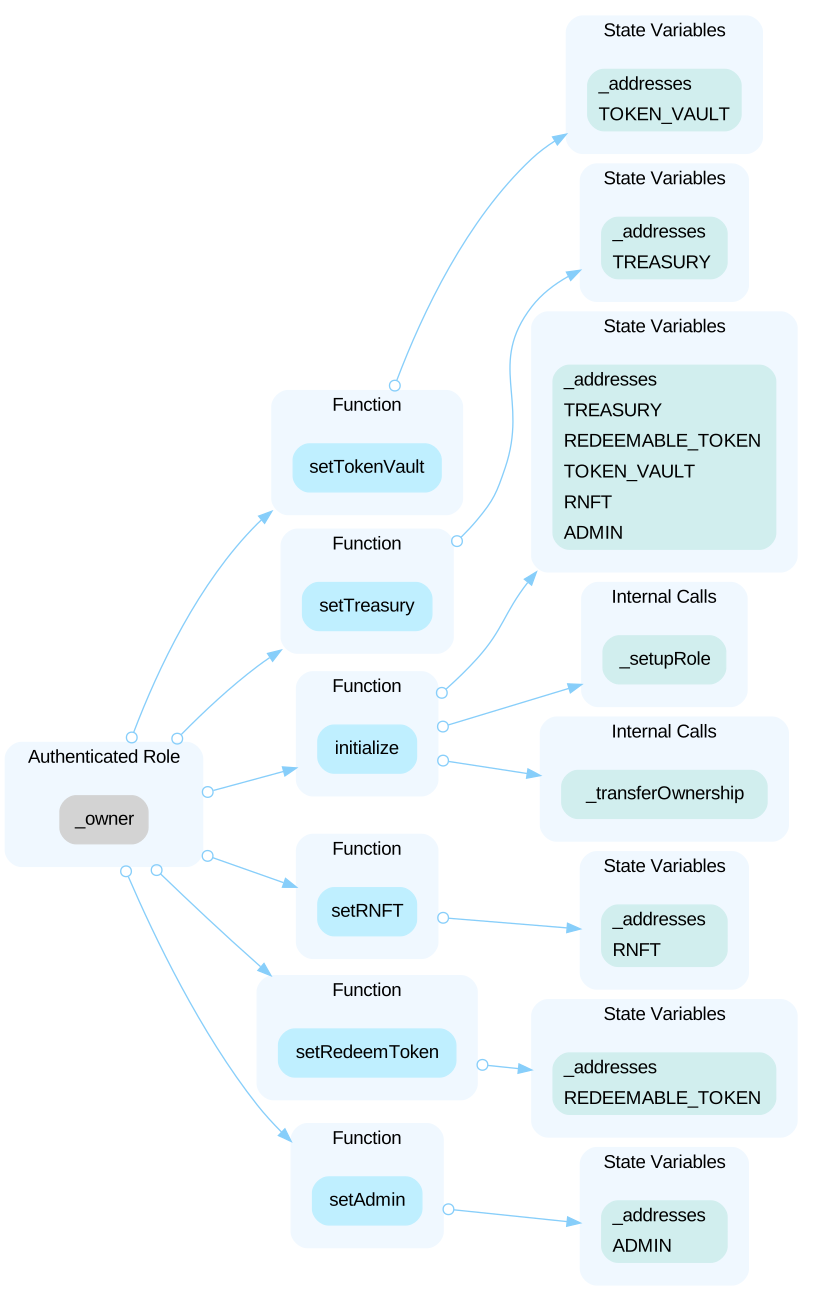 ----- In the contract `TokenVault` the role `_moderator` has authority over the functions shown in the diagram below. Any compromise to the `_moderator` account may allow the hacker to take advantage of this authority and mint FNFTs and withdraw tokens. 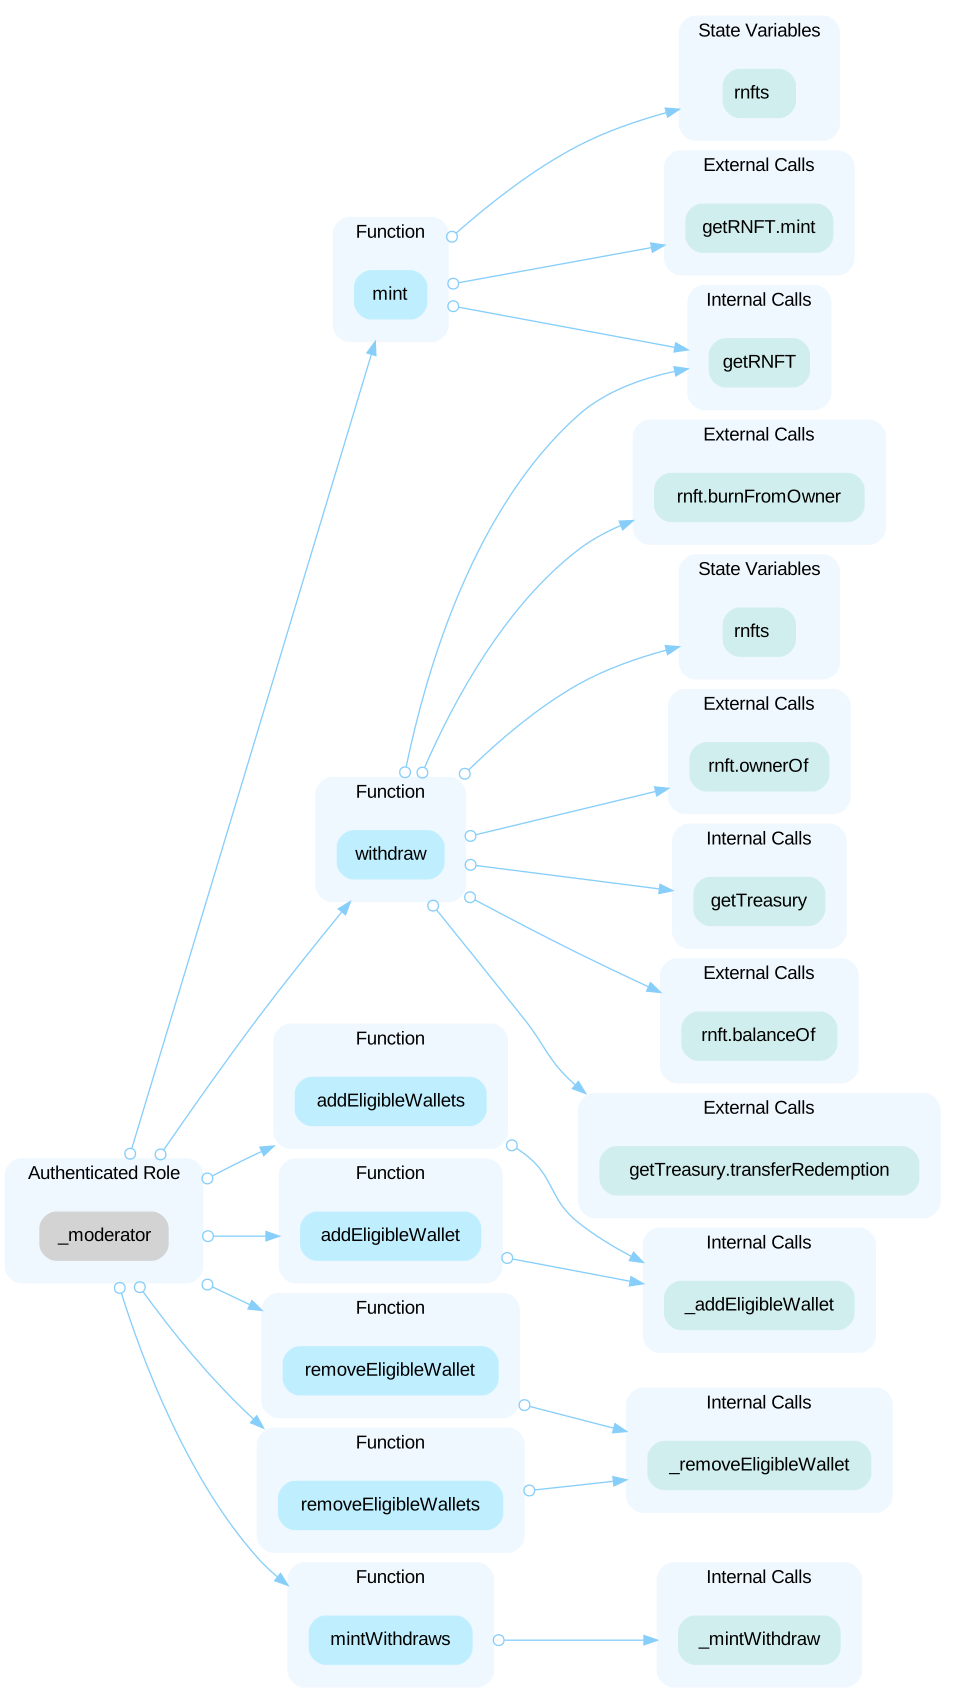 In the contract `TokenVault` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and pause/unpause the contract. 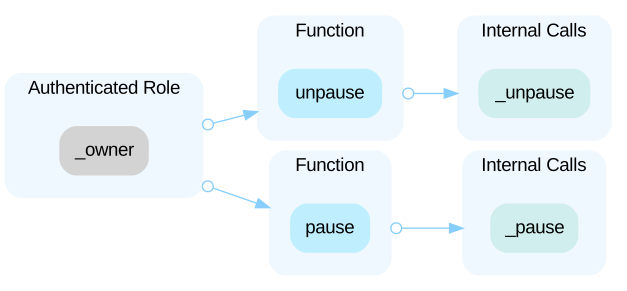 ----- In the contract `HectorRegistration` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and set moderators. 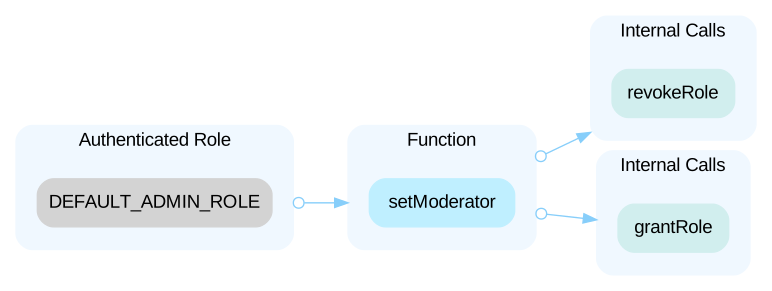 In the contract `HectorRegistration` the role `MODERATOR_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MODERATOR_ROLE` account may allow the hacker to take advantage of this authority and add registered wallets or blacklist addresses. 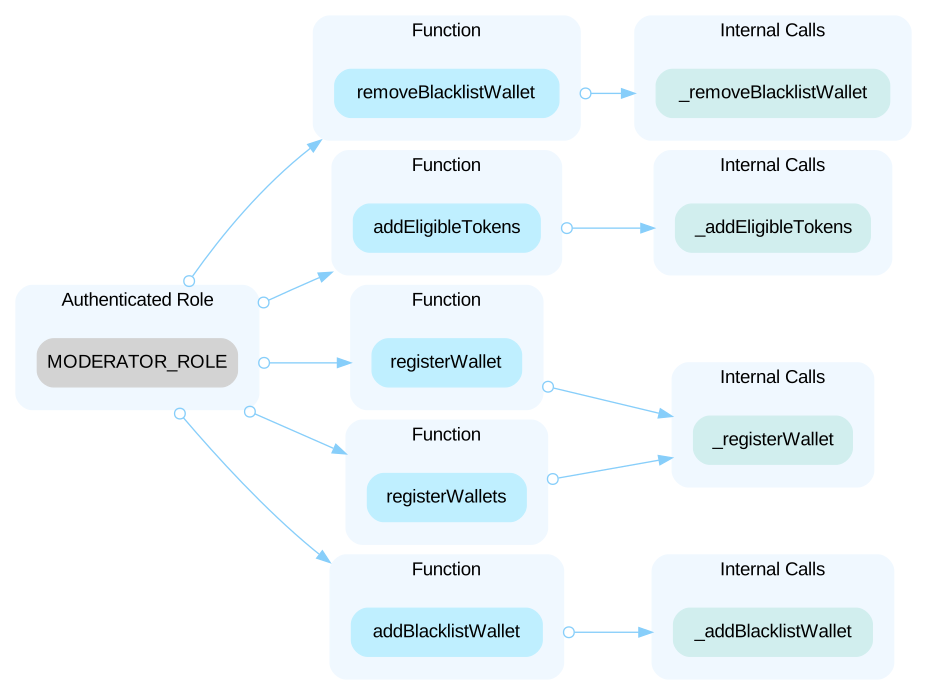
Open the reportIn the contract Emissionor.sol the role `_owner` has authority over the following functions: - `setModerator()` - `setTreasury()` - `setSplitterContract()` - `setRewardToken()` Any compromise to the `_owner` account may allow a hacker to take advantage of this authority and approve or unapproved moderators, or change the addresses of necessary variables. In the contract Emissionor.sol the modifier `onlyMod` has authority over the following functions: - `initialize()` - `emitReward()` Any compromise to the an approved `moderators` account may allow a hacker to take advantage of this authority and affect the reward emitting. In the contract LockAddressRegistry.sol the role `_owner` has authority over the following functions: - `initialize()` - `setAdmin()` - `setTokenVault()` - `setFNFT()` - `setEmissionor()` - `addFarm()` Any compromise to the `_owner` account may allow a hacker to take advantage of this authority and set incorrect privileged contract addresses, potentially as EOA, or approve unintended addresses as farms. In the contract RewardWeight.sol the role `_owner` has authority over the following functions: - `register()` - `setRewardWeight()` - `updateReceiverStatus()` Any compromise to the `_owner` account may allow a hacker to take advantage of this authority and set or change receive rate and/or status. In the contract SplitterDistributor.sol the role `_owner` has authority over the following functions: - `register()` - `setRewardContract()` - `updateReceiverStatus()` Any compromise to the `_owner` account may allow a hacker to take advantage of this authority and change receiver status. In the contract TokenVault.sol the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and pause or unpause the functionality of the vault. 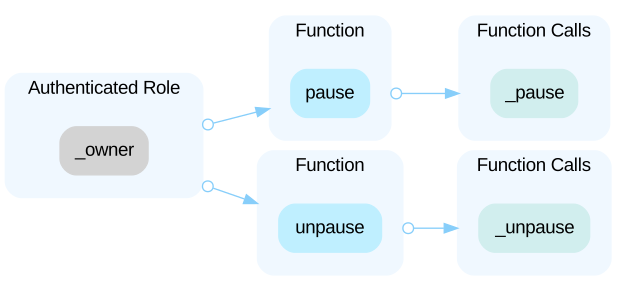 In the contract `RewardReceiver` the role `_owner` has authority over the following functions: - `setRewardToken()` Any compromise to the `_owner` account may allow a hacker to take advantage of this authority and improperly set the token received as rewards.
Open the reportThe contracts in scope are part of a broader system that includes substantial off-chain components. These off-chain components play an essential role, such as calculating the amount of tokens users can redeem, and they are not in scope for this audit. The scope of the audit treats off-chain components and third-party entities as black boxes and assumes their functional correctness. However, in the real world, they can be compromised and this may lead to lost or stolen assets.
Open the reportThe `getBalancesFromWallet()` function calls `_getWalletBalance(_walletAddress)`, which adds `FNFTbalance` with various ERC20 token balances. The meaning of adding tokens of different types and values is unclear and could be confusing to users.
Open the reportThe linked contracts import and use OpenZeppelin's `Counters` contract. OpenZeppelin has deprecated the usage of the `Counters` contract: https://github.com/OpenZeppelin/openzeppelin-contracts/issues/4233
Open the reportThe `initialize()` function can be called multiple times. Prior initialization could be overwritten if called more than once.
Open the reportThe linked functions are equivalent to the compiler-generated getter functions for the respective variables.
Open the reportWhen transferring standard ERC20 deflationary tokens, the input amount may not be equal to the received amount due to the charged transaction fee. For example, if a user stakes 100 deflationary tokens (with a 10% transaction fee) in a MasterChef, only 90 tokens actually arrive in the contract. However, the user can still withdraw 100 tokens from the contract, which causes the contract to lose 10 tokens in such a transaction. Details on this kind of exploit: https://thoreum-finance.medium.com/what-exploit-happened-today-for-gocerberus-and-garuda-also-for-lokum-ybear-piggy-caramelswap-3943ee23a39f We notice that the current plan allows HEC, HEC/DAI, and HEC/USDC as the staking token, which is good for now. We want to ensure that the team does not plan to add any deflationary token(with transition fees) into the LockFarm pool.
Open the reportThe reports name a repository or files. Open a report to see its scope.
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="hector-network"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us