
Honor World Token security record
As of 3 Nov 2026, Honor World Token has 2 audit reports by 1 security firm on Trustblock; the latest is by CertiK, dated 17 Jan 2023. Those reports list no open critical findings.
Record last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Audits2
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| Honorworld - Audit 2 | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
| Honorworld - Audit | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
Findings24
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 6 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 3 | 5 | 9 |
HighCentralization Risks in CrystalFarming.solHonorworld - Audit 2 · CertiK · 17 Jan 2023Acknowledged
In the contract `CrystalFarming` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 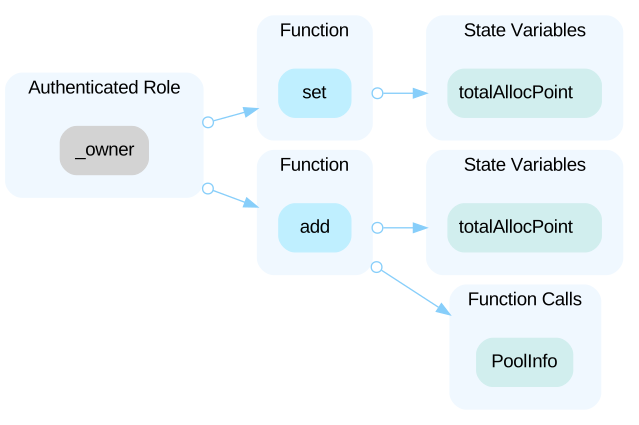 In the contract `CrystalFarming` the role `devaddr` has authority over the functions shown in the diagram below. Any compromise to the `devaddr` account may allow the hacker to take advantage of this authority. 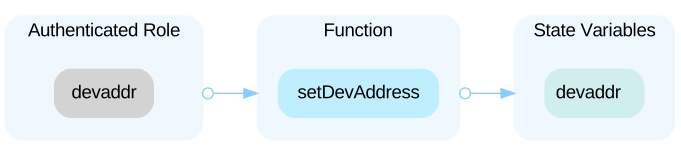
Open the reportHighCentralized Control of Contract UpgradeHonorworld - Audit 2 · CertiK · 17 Jan 2023Acknowledged
`CrystalFarming` is an upgradeable contract, the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, he can change the implementation of the contract and drain tokens from the contract.
Open the reportHighCentralization Risks in HWTToken.solHonorworld - Audit · CertiK · 10 Oct 2022Acknowledged
In the contract `HWTToken` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set the mainPool address. 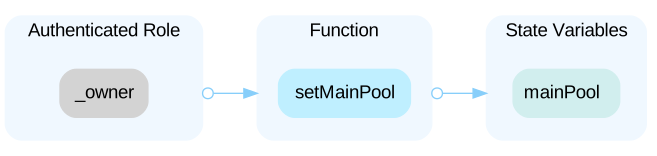 In the contract `HWTToken` the role `mainPool` has authority over the functions shown in the diagram below. Any compromise to the `mainPool` account may allow the hacker to take advantage of this authority and mint HWT to an arbitrary address. 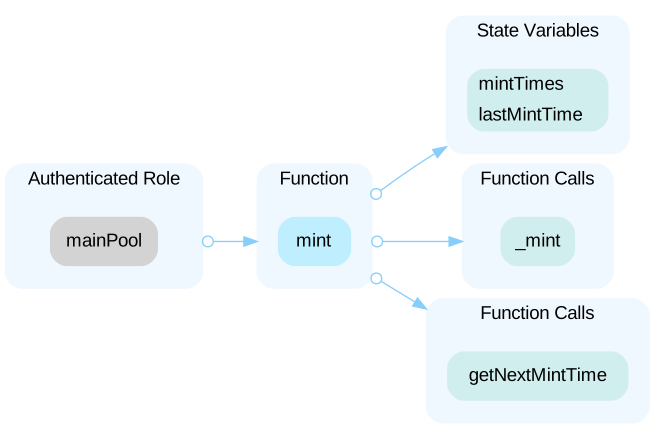
Open the reportHighCentralization Risks in LPStaking.solHonorworld - Audit · CertiK · 10 Oct 2022Acknowledged
In the contract `LPStaking` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and add new liquidity pools and modify the allocation points of the existing ones. 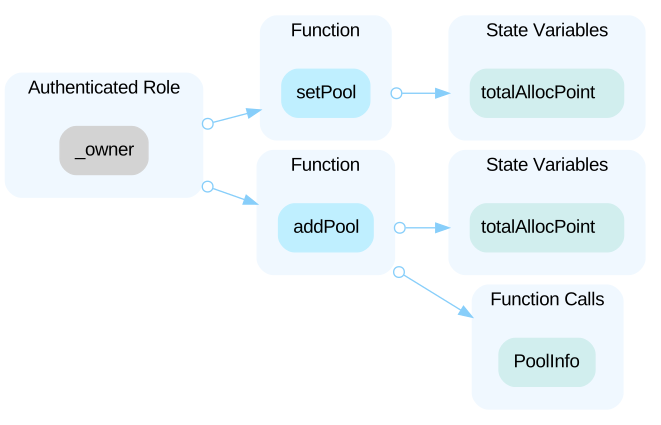 In the contract `LPStaking` the role `devAddress` has authority over the functions shown in the diagram below. Any compromise to the `devAddress` account may allow the hacker to take advantage of this authority to change the `devAddress` address, which receives fees when a withdrawal takes place. 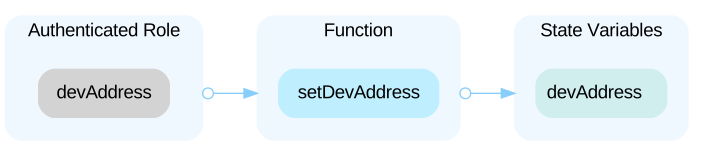
Open the reportHighCentralization Risks in NFTStaking.solHonorworld - Audit · CertiK · 10 Oct 2022Acknowledged
In the contract `NFTStaking` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and arbitrarily set `ApprovedMinter` and `ApprovedOperator` roles, as well as the AuraRule address. 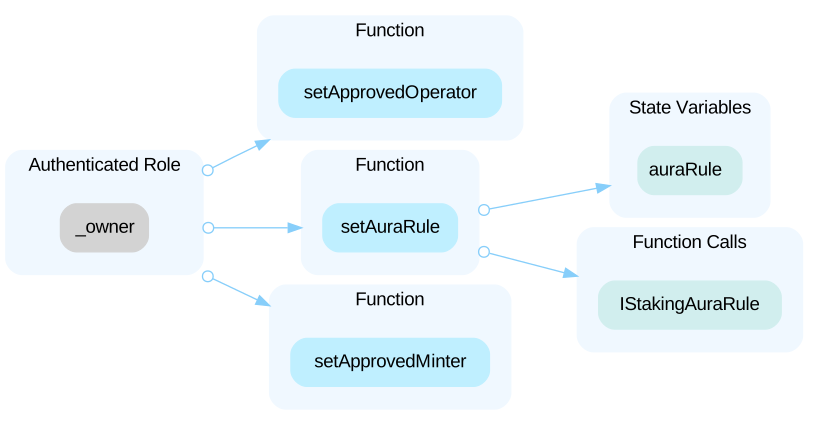 -------------------------------- The role `ApprovedMinter` has the authority to function `directStake()` to stake token on other user's behalf. The role `ApprovedOperator` has the authority to the following functions to manage NFT tokens' ownership: - `escrowOwnership()` - `restoreOwnership()` - `transferOwnership()` Any compromise to the `ApprovedMinter` or `ApprovedOperator` account may allow the hacker to take advantage of this authority and stake or lock user's NFT tokens without their consent.
Open the reportHighCentralization Risks in StrategyPSC.solHonorworld - Audit · CertiK · 10 Oct 2022Acknowledged
In the contract `StrategyPSC` the role `devAddress` has authority over the functions shown in the diagram below. Any compromise to the `devAddress` account may allow the hacker to take advantage of this authority and arbitrarily set `devAddress`, which receives the dev fees. 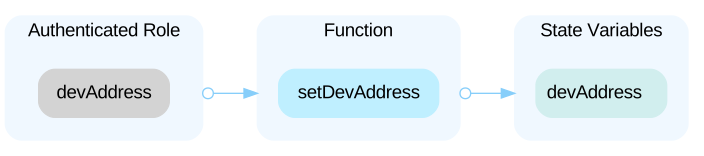 In the contract `StrategyPSC` the role `govAddress` has authority over the functions shown in the diagram below. Any compromise to the `govAddress` account may allow the hacker to take advantage of this authority and arbitrarily set multiple important addresses and disrupt normal contract process by pause/unpause. 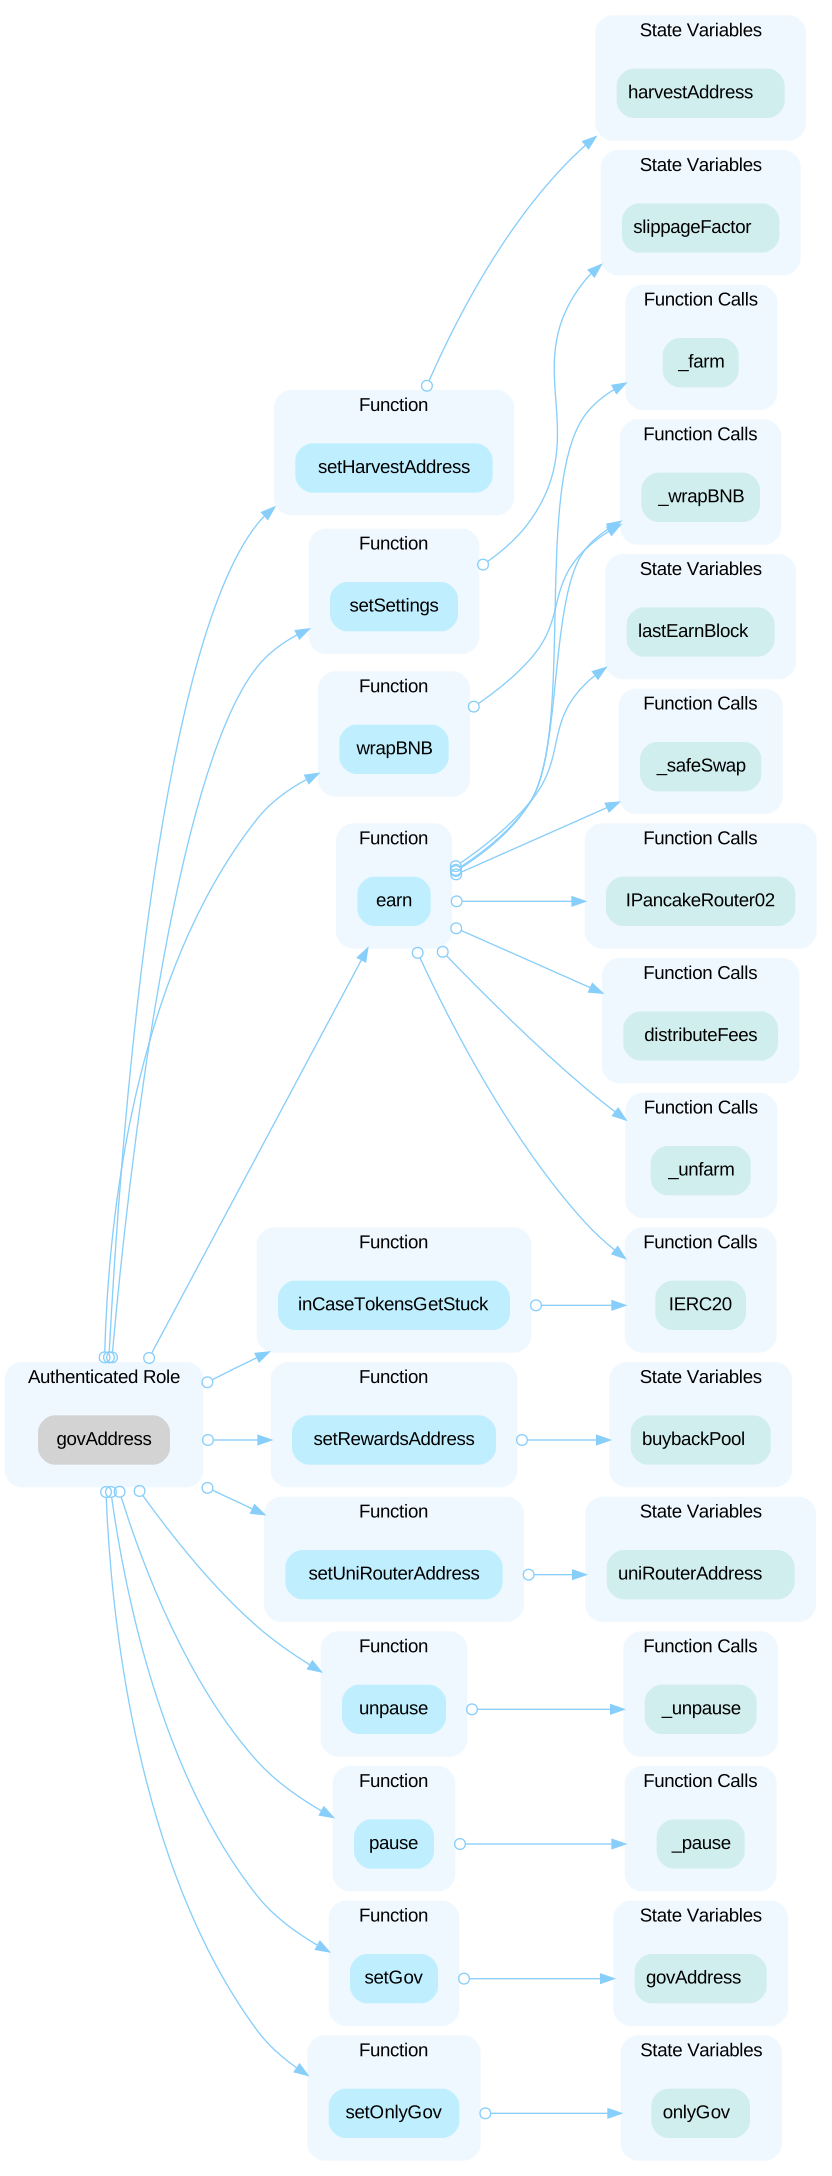 In the contract `StrategyPSC` the role `harvestAddress` has authority over the functions shown in the diagram below. Any compromise to the `harvestAddress` account may allow the hacker to take advantage of this authority and take control over harvest and earn process. 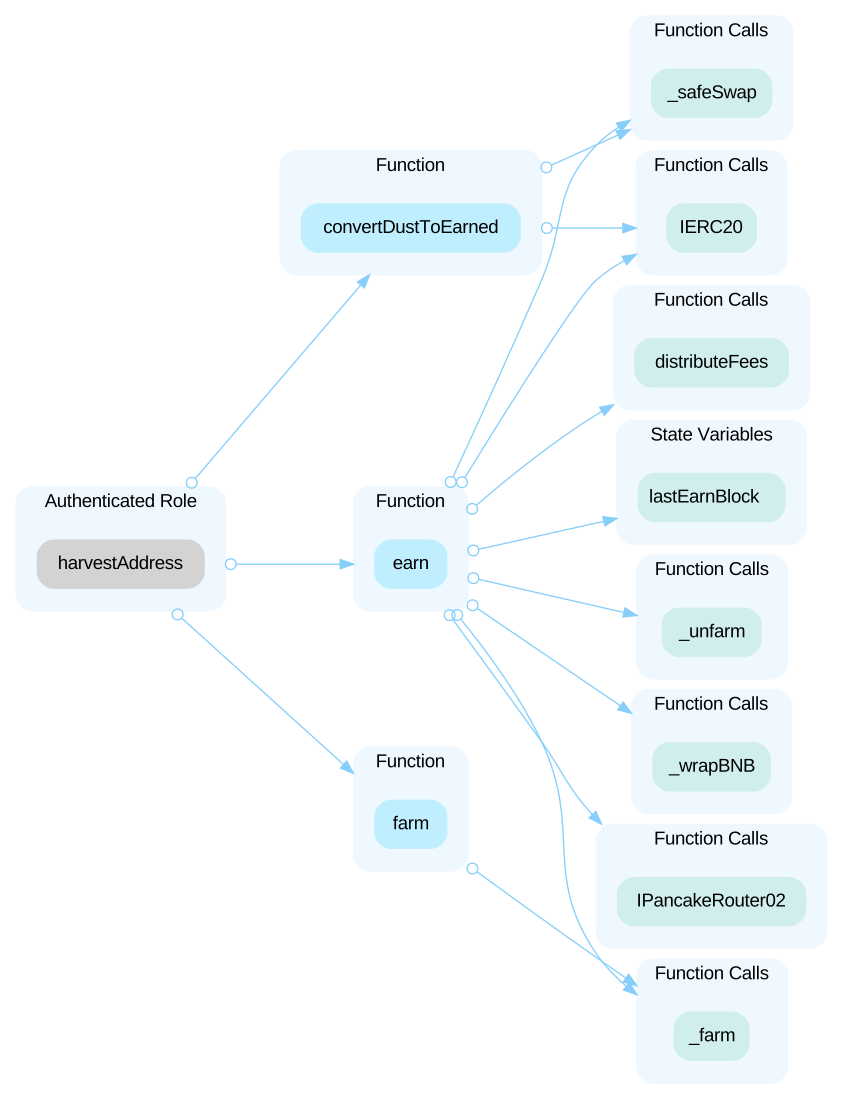
Open the reportLow`boostToken` not usedHonorworld - Audit 2 · CertiK · 17 Jan 2023Acknowledged
The variable `boostToken` is always `address(0)`, and the function `boostReachMax()` always returns 0.
Open the reportLowIncompatibility With Deflationary TokensHonorworld - Audit 2 · CertiK · 17 Jan 2023Acknowledged
When transferring standard ERC20 deflationary tokens, the input amount may not be equal to the received amount due to the charged transaction fee. For example, if a user stakes 100 deflationary tokens (with a 10% transaction fee) in a MasterChef contract, only 90 tokens actually arrive in the contract. However, the user can still withdraw 100 tokens from the contract, which causes the contract to lose 10 tokens in such a transaction. Reference: https://thoreum-finance.medium.com/what-exploit-happened-today-for-gocerberus-and-garuda-also-for-lokum-ybear-piggy-caramelswap-3943ee23a39f
Open the reportLowThird Party DependencyHonorworld - Audit 2 · CertiK · 17 Jan 2023Acknowledged
The contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assume their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=46 IERC1155Upgradeable public rewardToken; ``` - The contract `CrystalFarming` interacts with third party contract with `IERC1155Upgradeable` interface via `rewardToken`. --- ```solidity=47 IRewardSupplierMultiPool public rewardSupplier; ``` - The contract `CrystalFarming` interacts with third party contract with `IRewardSupplierMultiPool` interface via `rewardSupplier`. --- ```solidity=240 function deposit(address _token, uint256 _amount) ``` - The function `CrystalFarming.deposit` interacts with third party contract with `IERC20Upgradeable` interface via `_token`. --- ```solidity=276 function withdraw(address _token, uint256 _amount) ``` - The function `CrystalFarming.withdraw` interacts with third party contract with `IERC20Upgradeable` interface via `_token`. --- ```solidity=365 function _distributeFee(address _token, uint256 _fee) internal { ``` - The function `CrystalFarming._distributeFee` interacts with third party contract with `IERC20Upgradeable` interface via `_token`.
Open the reportLowUninitialized State VariableHonorworld - Audit 2 · CertiK · 17 Jan 2023Acknowledged
One or more state variables are used without being initialized in the constructor. ```solidity=53 address[] public registeredTokens; ``` - `registeredTokens` is never initialized, but used in `CrystalFarming.poolLength`.
Open the reportShow 1 more
LowUnused VariableHonorworld - Audit 2 · CertiK · 17 Jan 2023Acknowledged
The variable `MAX_BOOST` is declared but the current code logic doesn't use this variable.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="honor-world"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us