As of 3 Nov 2026, Icplaza has 2 audit reports by 1 security firm on Trustblock; the latest is by CertiK, dated 17 Oct 2022. Those reports list no open critical findings.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Newest first
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 3 | 0 |
| Medium | 0 | 0 | 2 |
| Low | 1 | 1 | 14 |
In the contract `BSCChannel/TronChannel` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and `mint()` any amount of tokens in ICPlaza chain. 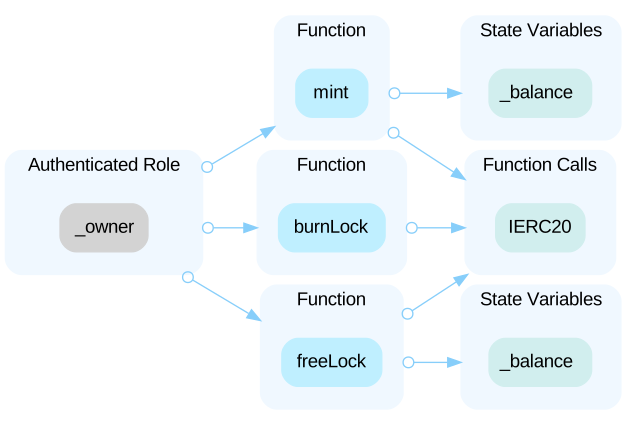
Open the reportIn the contract `BSCOut/TRONOut` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and `transfer()` all the tokens from `_outAccount`. 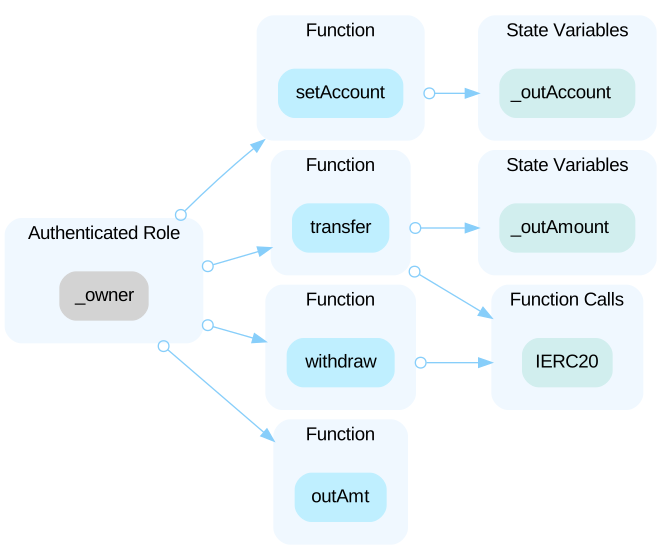
Open the reportIn the contract `USDT` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and `addMinter()` to `mint()` any amount of tokens. 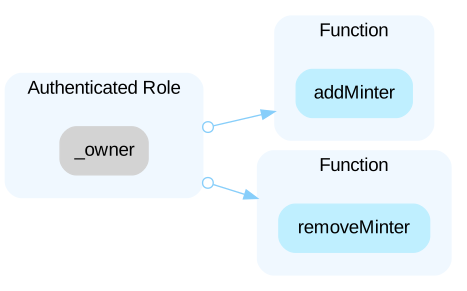
Open the reportThe `validator-dao` module outlines the following scenario: Grantees get the power to do something (e.g. issue ERC20 tokens) by escrowing their cosmos coins to the module address, after issuing ERC20 tokens, the escrowed coins will be absorbed and these cosmos coins will be transferred to the validator address. Obviously, the logic here is incomplete, the grantee cannot withdraw their escrow coins and the process of issuing ERC20 is not in this module. The currently audited code represents a tiny part of the entire protocol. We may most likely not be informed of its true purpose and just have to do our best to ensure that the module's functionality is within manageable limits.
Open the reportThe reports name a repository or files. Open a report to see its scope.
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="icplaza"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us