
Internet Money security record
As of 3 Nov 2026, Internet Money has 9 audit reports by 1 security firm on Trustblock; the latest is by CertiK, dated 7 Jun 2023. Those reports list no open critical findings. It also holds 2 deployed contracts on 2 chains.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Audits9
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| Internet Money Swap Router - PulseChain | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
| Internet Money (IM) - BNB Smart Chain (BSC) | Security firm: CertiK | Date: | Scope: 1 address on BNB Chain | No open critical findings | Open · skynet.certik.com |
| Internet Money Swap Router - BNB Smart Chain (BSC) | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
| T.I.M.E. Dividend (TIME) - BNB Smart Chain (BSC) | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
| T.I.M.E. Dividend (TIME) - Ethereum | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
| Future T.I.M.E. Dividend (FUTURE) - Ethereum | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
| Internet Money Swap Router - Ethereum | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
| Internet Money (IM) - Ethereum | Security firm: CertiK | Date: | Scope: 1 address on Ethereum | No open critical findings | Open · skynet.certik.com |
| Internet Money Wallet | Security firm: CertiK | Date: | Scope: Not recorded (see the report) | No open critical findings | Open · skynet.certik.com |
Findings24
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 5 |
| Medium | 2 | 0 | 9 |
| Low | 1 | 0 | 6 |
HighInitial Token DistributionInternet Money (IM) - BNB Smart Chain (BSC) · CertiK · 28 Mar 2023Fixed
All `IM` tokens are sent to the contract deployer when deploying the contract. This is a potential centralization risk as the deployer can distribute those tokens without the consensus of the community.
Open the reportHighInitial Token DistributionT.I.M.E. Dividend (TIME) - BNB Smart Chain (BSC) · CertiK · 24 Mar 2023Fixed
All `T.I.M.E. Dividend` tokens are sent to the contract deployer when deploying the contract. This is a potential centralization risk as the deployer can distribute those tokens without the consensus of the community.
Open the reportHighInitial Token DistributionT.I.M.E. Dividend (TIME) - Ethereum · CertiK · 24 Mar 2023Fixed
All `T.I.M.E. Dividend` tokens are sent to the contract deployer when deploying the contract. This is a potential centralization risk as the deployer can distribute those tokens without the consensus of the community.
Open the reportHighInitial Token DistributionFuture T.I.M.E. Dividend (FUTURE) - Ethereum · CertiK · 24 Mar 2023Fixed
All `Future T.I.M.E. Dividend` tokens are sent to the contract deployer when deploying the contract. This is a potential centralization risk as the deployer can distribute those tokens without the consensus of the community.
Open the reportHighCentralization Related RisksInternet Money (IM) - Ethereum · CertiK · 6 Mar 2023Fixed
In the contract `BaseERC20` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and mint arbitrary amount of tokens to any account. 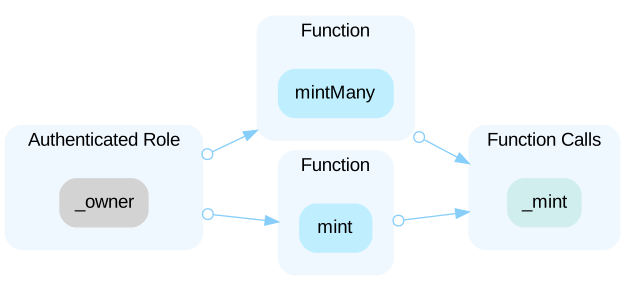
Open the reportMediumFunction Calls User-Provided Addresses With No AcT.I.M.E. Dividend (TIME) - BNB Smart Chain (BSC) · CertiK · 24 Mar 2023Fixed
Calling a user provided address is dangerous, especially in a public function with no access control restriction. An attacker could deploy a malicious contract and use the vulnerable function to trigger a call to the malicious contract, potentially stealing user funds or causing other serious damages. ```solidity=161 function distributeAll(address internetMoneySwapRouter, uint256 amount) public { IInternetMoneySwapRouter(internetMoneySwapRouter).distributeAll(amount); } ```
Open the reportMediumFunction Calls User-Provided Addresses With No AcT.I.M.E. Dividend (TIME) - Ethereum · CertiK · 24 Mar 2023Fixed
Calling a user provided address is dangerous, especially in a public function with no access control restriction. An attacker could deploy a malicious contract and use the vulnerable function to trigger a call to the malicious contract, potentially stealing user funds or causing other serious damages. ```solidity=161 function distributeAll(address internetMoneySwapRouter, uint256 amount) public { IInternetMoneySwapRouter(internetMoneySwapRouter).distributeAll(amount); } ```
Open the reportMediumAccounts, secrets, and API keys reuse in differenInternet Money Wallet · CertiK · 9 Jan 2023Fixed
Two environment variable files `.env.development` and `.env.production`, are found in the `backend-nodejs` folder. Many important accounts, secrets, and API keys are re-used between the development and the production environment.
Open the reportMediumInsecure key derivation functionInternet Money Wallet · CertiK · 9 Jan 2023Fixed
The application uses the crypto-js's EVPKDF derivation function, which does a single iteration of the MD5 hash function to generate the encryption key. MD5 hash algorithm is not a key derivation function. The code below from [crypto-js library](https://github.com/brix/crypto-js/blob/971c31f0c931f913d22a76ed488d9216ac04e306/src/evpkdf.js), shows the configuration used in the derivation function: ```typescript=22 cfg: Base.extend({ keySize: 128/32, hasher: MD5, iterations: 1 }), ```
Open the reportMediumInsecure password hashing algorithmInternet Money Wallet · CertiK · 9 Jan 2023Fixed
The application generates the password hash by doing a double "keccak256", which is considered an insecure way to perform the password hashing. ```js export const getPasswordHash = (password) => { const web3 = new Web3(); try { return web3.utils.keccak256(web3.utils.keccak256(password.toString())); } catch (error) { return null; } }; ```
Open the reportShow 10 more
MediumMnemonic display allow screenshotInternet Money Wallet · CertiK · 9 Jan 2023Fixed
The mnemonic phrase is a list of words that can be used to recover a wallet account. Obtaining the mnemonic can potentially allow the attacker to gain full control of the wallet. The application neither has a mechanism in place to stop a user from taking the screenshot of the displayed wallet secrets nor display a warning to remind the user of the risk of taking a screenshot.
Open the reportMediumProblematic behaviors when swapping BNB to WBNBInternet Money Wallet · CertiK · 9 Jan 2023Fixed
WBNB is the wrapped version of the native BSC token BNB. BNB should always be able to redeem with a 1-1 ratio for WBNB. The application display a UI claim the BNB to WBNB flow is a "swap" and provides the "SushiSwap/PancakeSwap" as an option. After selecting one of the DEX options and submitting the transaction, the transaction will always revert.
Open the reportMediumScreenshot BackgroundingInternet Money Wallet · CertiK · 9 Jan 2023Fixed
On mobile devices, a screenshot of the current activity is taken when an application goes into the background and displayed for aesthetic purposes when the app returns to the foreground. This feature may pose a security risk. Sensitive data may be exposed if the user background the application while sensitive data is displayed. A malicious application that is running on the device and able to continuously capture the screen may also expose data.
Open the reportMediumUnlimited Token approval to a unverified contractInternet Money Wallet · CertiK · 9 Jan 2023Fixed
When users want to swap one token for another, the wallet application requires the user to approve the maximal token allowance for the "https://bscscan.com/address/0x02a060a1bb096572b3d6a67e20f8cdf48c92d7d4" contract. The contract is unverified in the blockchain explorer.
Open the reportLowUnsafe Integer CastT.I.M.E. Dividend (TIME) - BNB Smart Chain (BSC) · CertiK · 24 Mar 2023Fixed
```solidity=84 int256 correctionDelta = int256(magnifiedDividendPerShare * amount); ``` - The type conversion `int256(magnifiedDividendPerShare * amount)` from type uint256 to type int256 may flip the value's sign. ```solidity=134 uint256 product = uint256(int256(magDividendPerShare * balance) + correction); ``` - The type conversion `int256(magDividendPerShare * balance)` from type uint256 to type int256 may flip the value's sign.
Open the reportLowUnsafe Integer CastT.I.M.E. Dividend (TIME) - Ethereum · CertiK · 24 Mar 2023Fixed
```solidity=84 int256 correctionDelta = int256(magnifiedDividendPerShare * amount); ``` - The type conversion `int256(magnifiedDividendPerShare * amount)` from type uint256 to type int256 may flip the value's sign. ```solidity=134 uint256 product = uint256(int256(magDividendPerShare * balance) + correction); ``` - The type conversion `int256(magDividendPerShare * balance)` from type uint256 to type int256 may flip the value's sign.
Open the reportLowATS MisconfigurationInternet Money Wallet · CertiK · 9 Jan 2023Fixed
App Transport Security (ATS) is a set of security checks that the operating system enforces when making connections with NSURLConnection, NSURLSession and CFURL to public hostnames. ATS is enabled by default for applications build on iOS SDK 9 and above. During the pentest, it is observed that on the iOS App, the App Transport Security restrictions are disabled for all network connections. Disabling ATS means that unsecured HTTP connections are allowed. HTTPS connections are also allowed and are still subject to default server trust evaluation. However, extended security checks like requiring a minimum Transport Layer Security (TLS) protocol version are disabled. - https://developer.apple.com/documentation/bundleresources/information_property_list/nsapptransportsecurity - https://cwe.mitre.org/data/definitions/919.html
Open the reportLowLack of token name, symbol and decimal validationInternet Money Wallet · CertiK · 9 Jan 2023Fixed
The extension wallet allows users to import custom tokens, and display the token name and symbol in the wallet UI. The ERC20 token contract standard doesn't have any restrictions on any of the token properties, and anyone can deploy token contracts on the blockchain. Once a token is added, the wallet will fetch the information and display them in it's interface.
Open the reportLowNo root or jailbreak detection on Android/iOS appInternet Money Wallet · CertiK · 9 Jan 2023Fixed
No root or jailbreak detection is implemented in the application. This allows an attacker to modify the app on a rooted Android or jailbroken iOS device, which means the attacker can potentially induce behaviors that otherwise would not occur. Examples of the impact include accessing sensitive application data, overwriting critical functions, and an overall wider attack surface.
Open the reportLowVerbose error messageInternet Money Wallet · CertiK · 9 Jan 2023Fixed
Improper handling of errors can introduce a variety of security problems for an application server. The most common one is the application return detailed stack traces, database dumps, and source code to the user when the server encounters an error. These messages reveal implementation details that should never be revealed. Multiple backend APIs of the internet money application return a verbose error message when receiving a malformed request.
Open the reportContracts2
| Address | Chain | Source code |
|---|---|---|
| 0x0a58153a0cd1cfaea94ce1f7fdc5d7e679eca936 | Chain: Ethereum | Source code: Verified source |
| 0xac5d23ce5e4a5eb11a5407a5fbee201a75e8c8ad | Chain: BNB Chain | Source code: Verified source |
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="internet-money"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us