
Kochi Ken security record
As of 3 Nov 2026, Kochi Ken has 1 audit report on Trustblock, by CertiK, dated 3 Mar 2023. That report lists no open critical findings.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Audits1
Newest first
Findings19
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 2 |
| High | 4 | 0 | 1 |
| Medium | 0 | 0 | 3 |
| Low | 0 | 0 | 9 |
HighCentralization Related RisksKochiken · CertiK · 3 Mar 2023Open
In the `CKochiInvest` contract, the message of the below functions **must be signed** by the `CVerifySignature` contract's `signer`: - `createLaunchpad()`: create a launch pad, - `buy()`: buy a presale, - `claim()`: claim tokens, - `ownerClaim()`: owner claims tokens, - `ownerCancel()`: owner cancels a sale, - `setReferrer()`: set referrer. Users need to have the "verification" message signed by the signer before calling the aforementioned functions. The concern is, if the signer does not sign the message in time, users might not be able to buy tokens or claim tokens. In an extreme case, if the signer's private key is compromised or lost, all the tokens within the contract will be **lost forever**. In the contract `Kochi` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 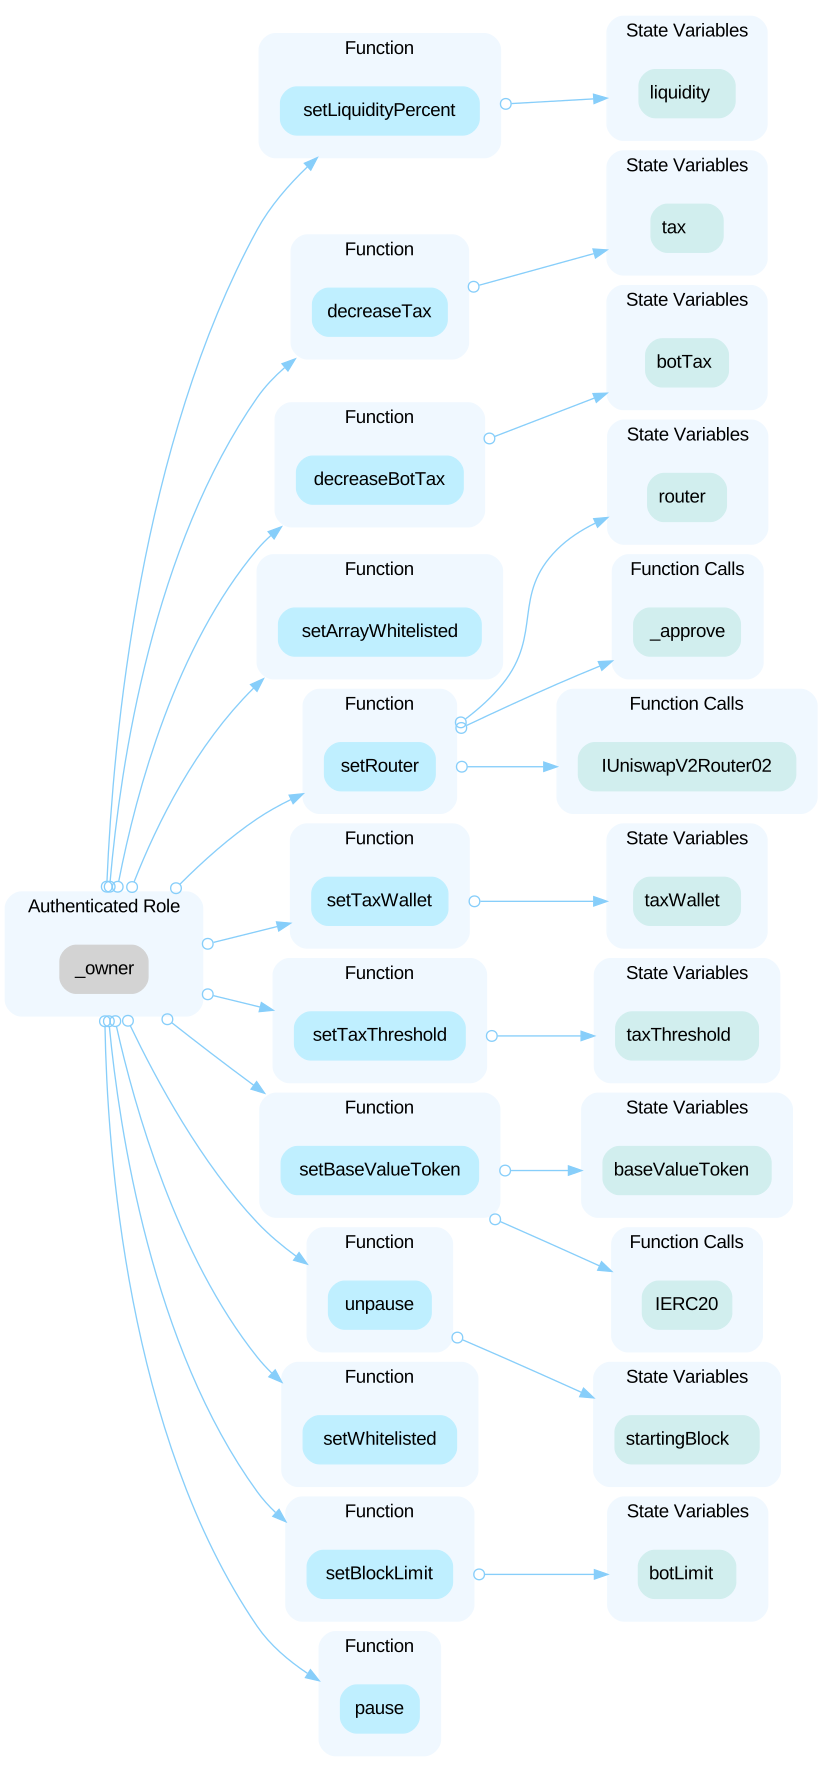 * The pause() is removed in the new version of the contracts on 12/08/2022* In the contract `KochiInvest` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. Furthermore, the function `terminate()` is a privileged function that can terminate presale prematurely and prevent the initiator of the presale from withdrawing the tokens. 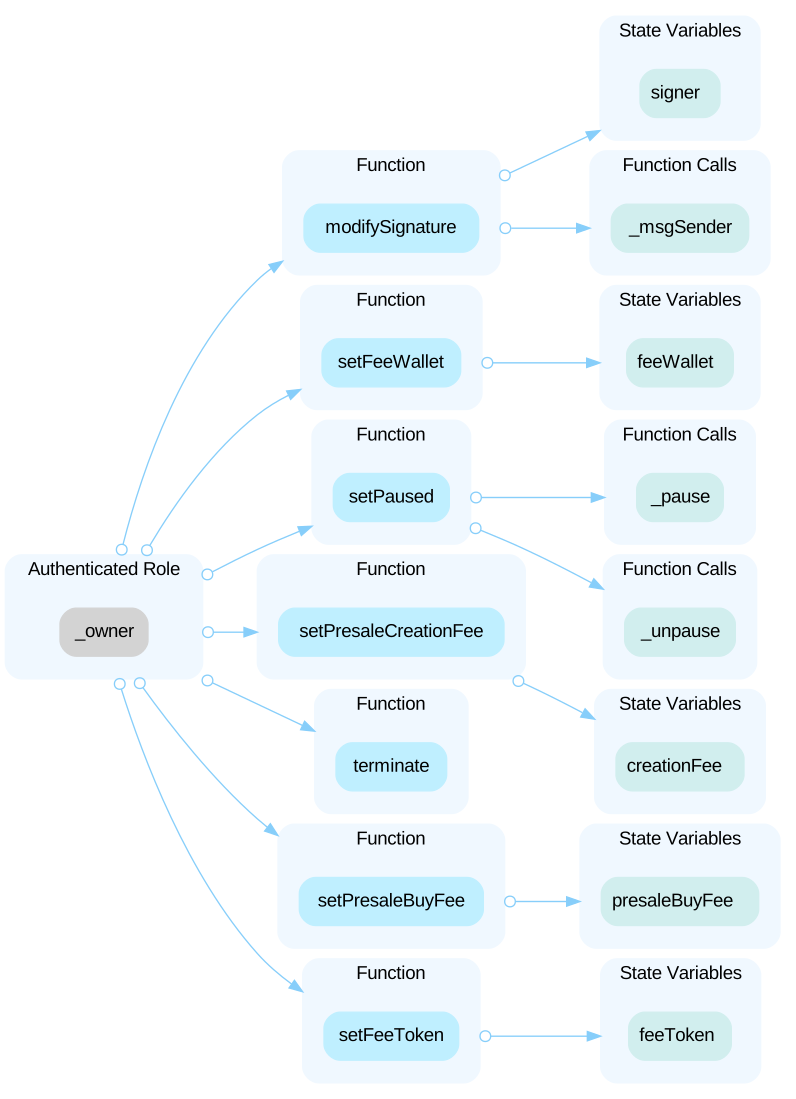 In the contract `KochiLock` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 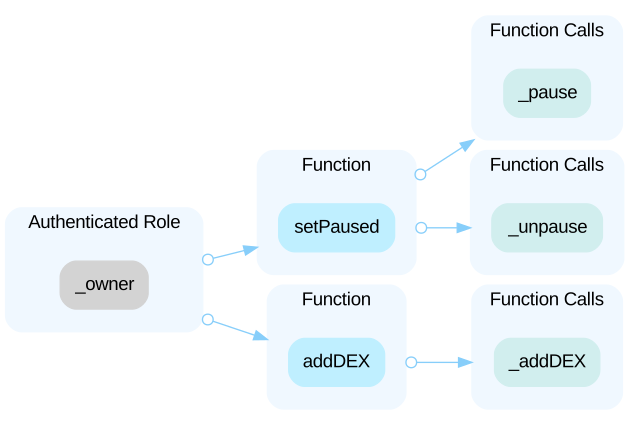 *The below description is based on the new version of the contracts on 12/08/2022* In the contract CKochi.sol the role `_owner` has authority over the functions shown below: - recoverERC20(), recovers tokens except the `KOCHI` tokens; - releaseAndLockLP(), releases and locks the LP tokens; - setLockContract(), set kochiLock. **[CertiK, 01/24/2023]** In the latest update, the function `payTaxes()` was divided into two functions, which are `payTaxes()` and `resolveTaxes()`, `resolveTaxes()` can only be executed by `owner`. However, the current design introduces another issue, namely the unguaranteed liquidity-adding process, meaning there is no guarantee for adding liquidity to the pool in time. Thus, it could lead to unexpected behaviors like token price fluctuation.
Open the reportHighCentralized Control of Contract UpgradeKochiken · CertiK · 3 Mar 2023Open
The contract `CBulksender`, `CKochiInvest`, `CKochiLock`, and `CKochiVest` are upgradeable contracts, the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, he can change the implementation of the contract and drain tokens from the contract.
Open the reportHighCentralized risk in `addLiquidity`Kochiken · CertiK · 3 Mar 2023Open
```solidity= // add the liquidity router.addLiquidity( address(baseValueToken), address(this), tokenAmount, baseAmount, 0, // slippage is unavoidable 0, // slippage is unavoidable taxWallet, block.timestamp ); ``` The `_addLiquidity` function calls the `router.addLiquidity()` function with the `to` address specified as `taxWallet` for acquiring the generated LP tokens from the `KOCHI-USDT` pool. As a result, over time the `taxWallet` address will accumulate a significant portion of LP tokens. If the `taxWallet` is an EOA (Externally Owned Account), mishandling of its private key can have devastating consequences to the project as a whole.
Open the reportHighInitial Token DistributionKochiken · CertiK · 3 Mar 2023Open
All of the `Kochi` tokens are sent to the contract deployer when deploying the contract. This could be a centralization risk as the deployer can distribute tokens without obtaining the consensus of the community. ```solidity=48 _mint(msg.sender, supply); ```
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="kochi-ken"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us