As of 25 Oct 2026, L2Finance has 1 audit report on Trustblock, by CertiK, dated 2 May 2023. That report lists no open critical findings.
Record last updated . It holds audits and findings, contracts and incidents up to Oct 2026. Trustblock does not review code.
Newest first
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 2 | 0 |
| Medium | 0 | 2 | 1 |
| Low | 0 | 0 | 6 |
In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer the ownership to any address. 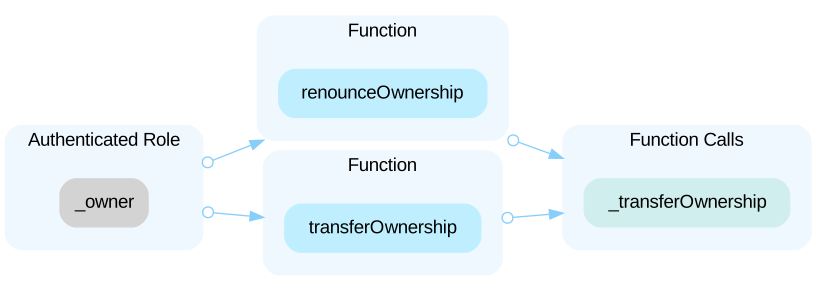 In the contract `HasNoEther` the role `_owner` has authority over the functions shown in the diagram below. This centralization risk may lead to a single point of failure and gives the owner significant control over the contract's behavior: 1. `reclaimEther()` - allows the owner to transfer all ether in the contract to the owner. 2. `reclaimToken()` - allows the owner to transfer any type of ERC20 in the contract to the owner. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and bring unpredictable damages to the project. 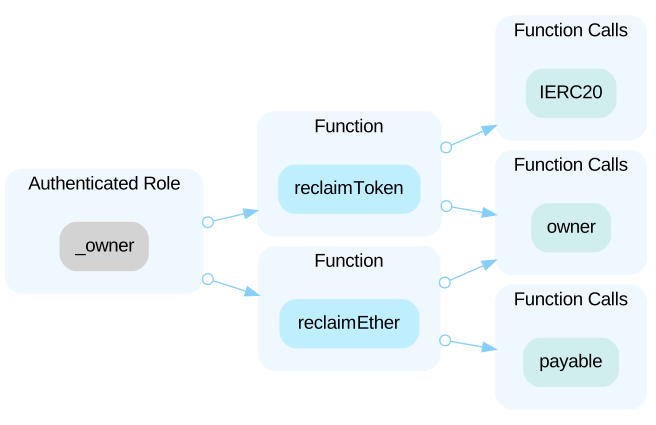 In the contract `L2Finance` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change the `sellBurnFee`, set the `excludeFee`/`_open`/`_key`, set the `_swap` and `_swapAllow` to block certain users from swapping functionality. 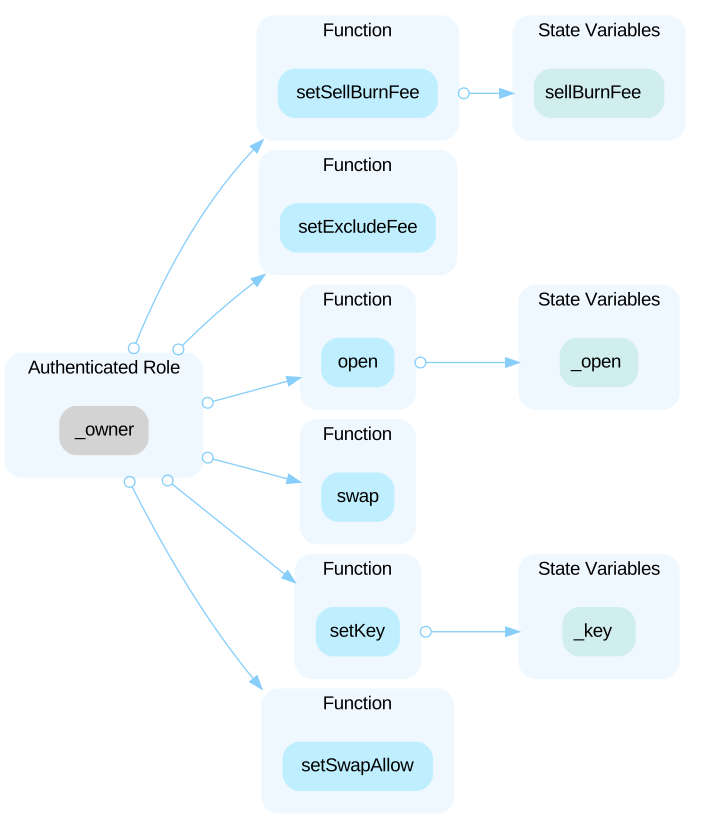
Open the reportAll L2FI tokens are sent to the deployer when deploying the contract. This could be a centralization risk as the deployer can distribute tokens without obtaining the consensus of the community.
Open the reportWhen transferring deflationary ERC20 tokens, the input amount may not be equal to the received amount due to the charged transaction fee. For example, if a user sends 100 deflationary tokens (with a 10% transaction fee), only 90 tokens actually arrived to the contract. However, a failure to discount such fees may allow the same user to withdraw 100 tokens from the contract, which causes the contract to lose 10 tokens in such a transaction. Reference: https://thoreum-finance.medium.com/what-exploit-happened-today-for-gocerberus-and-garuda-also-for-lokum-ybear-piggy-caramelswap-3943ee23a39f ```solidity=843 bool success = IERC20(_usdtAddr).transferFrom(_msgSender(), address(this), amountUSDTIn); ``` - Transferring tokens by `amountUSDTIn`. ```solidity=841 uint256 amountL2FIOut = _getL2FIOut(amountUSDTIn, poolL2FIBal, poolUSDTBal); ``` - This function call executes the following operation. - In `L2Finance._getL2FIOut`, - `uint256 denominator = poolUSDTBal.add(amountUSDTIn);` - In `SafeMath.add`, - `uint256 c = a + b;` - The `amountUSDTIn` appears to be used for bookkeeping purposes without compensating the potential transfer fees. --- ```solidity=861 bool success = IERC20(_usdtAddr).transferFrom(_msgSender(), address(this), amountUSDTIn); ``` - Transferring tokens by `amountUSDTIn`. ```solidity=859 uint256 amountL2FIOut = _getL2FIOut(amountUSDTIn, poolL2FIBal, poolUSDTBal); ``` - This function call executes the following operation. - In `L2Finance._getL2FIOut`, - `uint256 denominator = poolUSDTBal.add(amountUSDTIn);` - In `SafeMath.add`, - `uint256 c = a + b;` - The `amountUSDTIn` appears to be used for bookkeeping purposes without compensating the potential transfer fees.
Open the reportThe function `reclaimToken()` can be called by the owner to drain all ERC20 tokens in the contract, including the USDT and the L2FI. This is both a centralization issue and a logical issue.
Open the reportThe reports name a repository or files. Open a report to see its scope.
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="l2finance"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us