
MBD Financials security record
As of 25 Oct 2026, MBD Financials has 2 audit reports by 2 security firms on Trustblock; the latest is by CertiK, dated 2 May 2024. Those reports list no open critical findings. It also holds 2 deployed contracts on 1 chain.
Record last updated . It holds audits and findings, contracts and incidents up to Oct 2026. Trustblock does not review code.
Audits2
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| MBD Financials Token | Security firm: CertiK | Date: | Scope: 2 addresses on Ethereum | 3 critical findings, fixed | Open · skynet.certik.com |
| MBD Financials (Token) | Security firm: Paladin | Date: | Scope: 1 address on Ethereum | No open critical findings | Open · paladinsec.co |
Findings66
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 3 |
| High | 2 | 2 | 19 |
| Medium | 1 | 0 | 12 |
| Low | 2 | 2 | 23 |
HighCentralization Risks in MBD.solMBD Financials Token · CertiK · 2 May 2024Open
In the contract `MBD` the role `_owner` has authority over the functions shown in the diagram below. 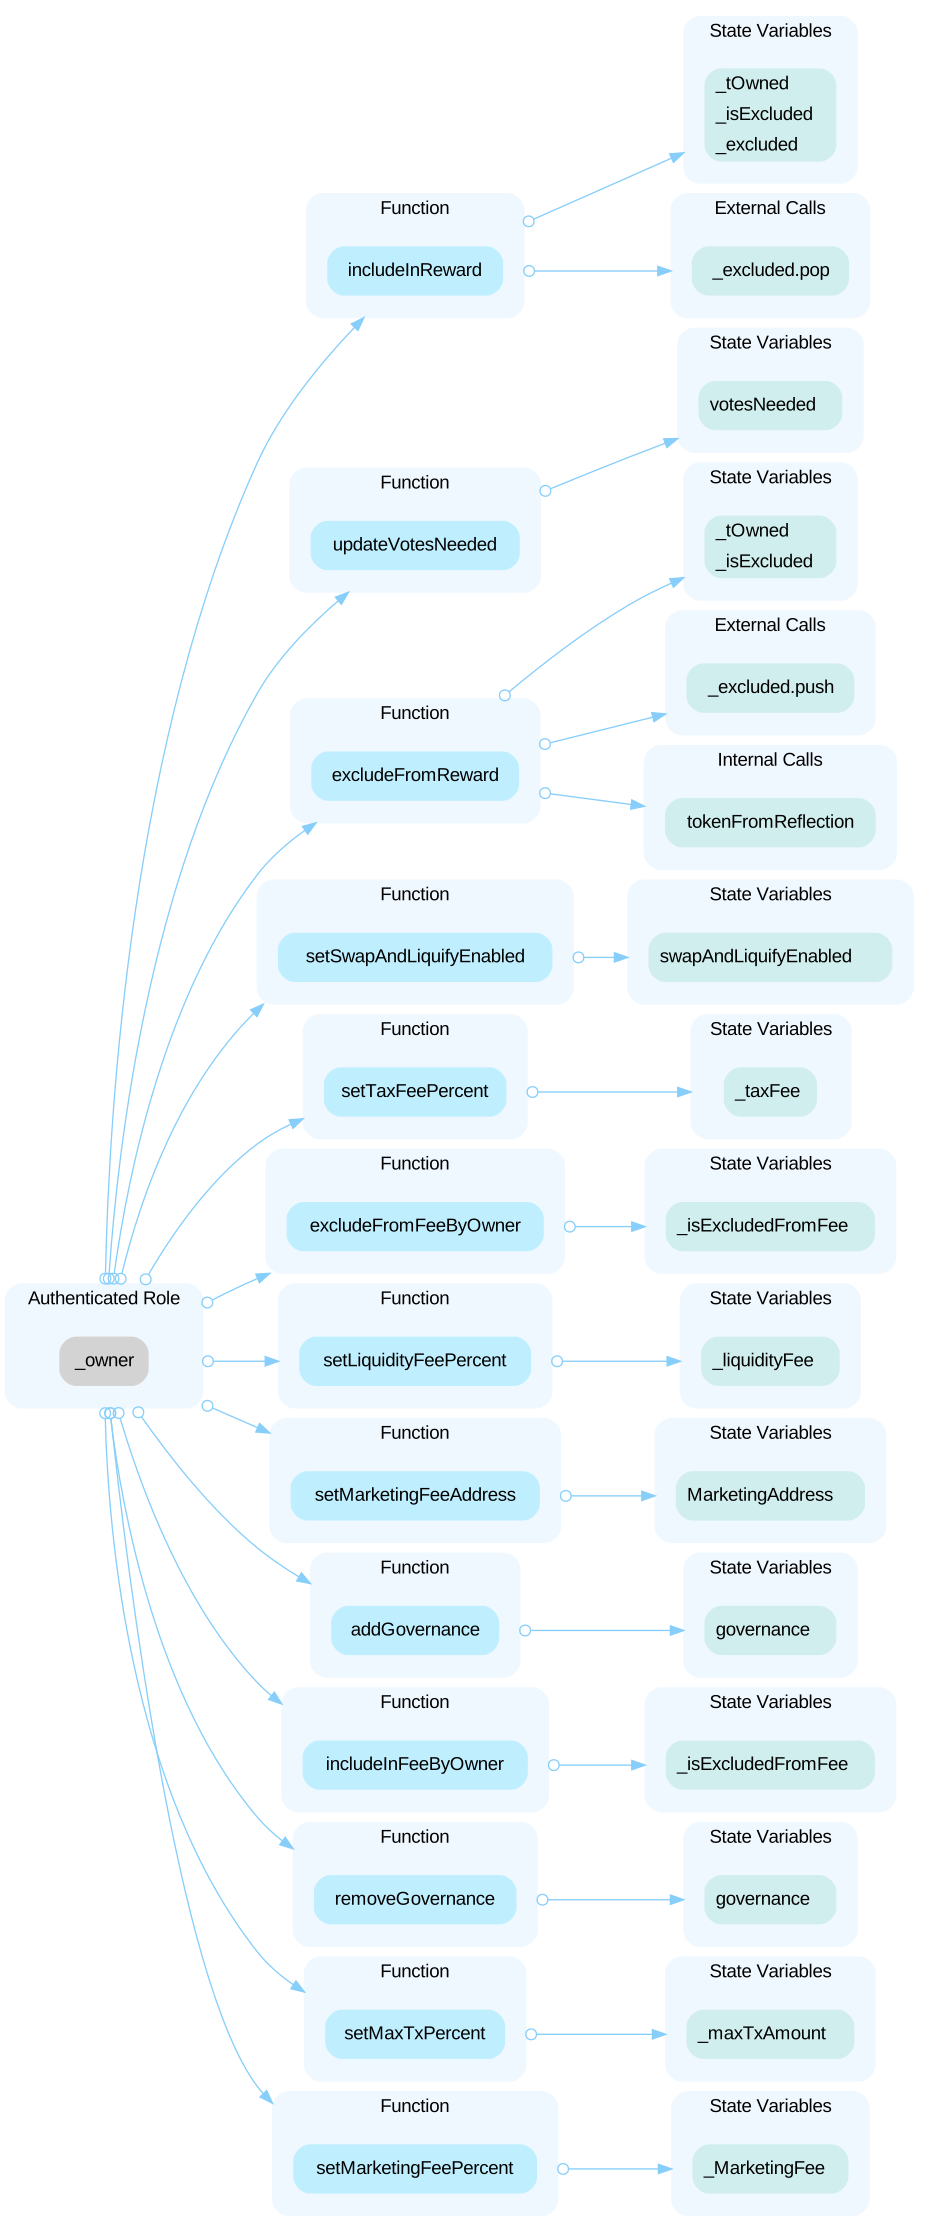 - `updateVotesNeeded(uint256 _votesNeeded)`: Updates the minimum number of votes needed for a proposal to be considered. Access is restricted to the owner of the contract. - `excludeFromReward(address account)`: Excludes an account from receiving reward distributions. Only the contract owner can call this function. - `includeInReward(address account)`: Includes an account back into the reward distribution. Only the contract owner can call this function. - `excludeFromFeeByOwner(address account)`: Excludes an account from having to pay transaction fees. Only the contract owner can call this function. - `includeInFeeByOwner(address account)`: Removes an account's exclusion from transaction fees, making them subject to fees again. Only the contract owner can call this function. - `setTaxFeePercent(uint256 taxFee)`: Sets the percentage of the tax fee for transactions. It is restricted to the owner and includes a check for total fee limits. - `setLiquidityFeePercent(uint256 liquidityFee)`: Sets the percentage of the liquidity fee for transactions. This function is restricted to the owner and includes a check for total fee limits. - `setMarketingFeePercent(uint256 marketingFee)`: Sets the percentage of the marketing fee for transactions. Access is limited to the owner and includes a check for total fee limits. - `setMaxTxPercent(uint256 maxTxPercent)`: Sets the maximum transaction amount as a percentage of total supply. Only the contract owner can call this function. - `setSwapAndLiquifyEnabled(bool _enabled)`: Toggles the state of the swap and liquify function. This is a privileged function that only the contract owner can call. - `setMarketingFeeAddress(address _marketingAddress)`: Sets the marketing fee wallet address. Only the contract owner has the privilege to call this function. - `addGovernance(address _governance)`: Adds an address to the list of governance addresses. Only the owner can call this function. - `removeGovernance(address _governance)`: Removes an address from the list of governance addresses. Only the owner can call this function. In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. 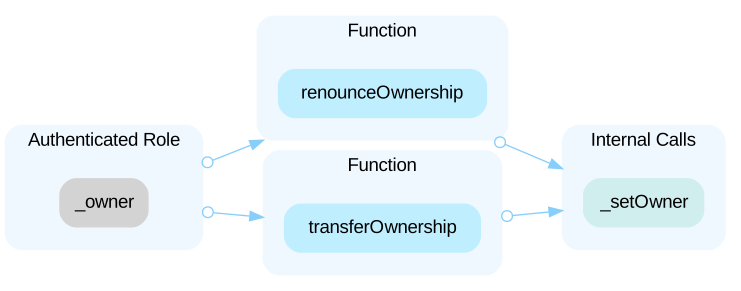 Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project.
Open the reportHighInitial Token DistributionMBD Financials Token · CertiK · 2 May 2024Open
All of the initial tokens are sent to the contract deployer or one or several externally-owned account (EOA) addresses. This is a centralization risk because the deployer or the owner(s) of the EOAs can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
Open the reportMediumUnrestricted Owner TransfersMBD Financials Token · CertiK · 2 May 2024Open
The function `_transfer` is designed to limit the amount of tokens transferred in a single transaction. However, the owner account may be exempted from this limit.
Open the reportLowPotential Logical Issue in Transaction Limit EnfoMBD Financials Token · CertiK · 2 May 2024Open
The logical condition within the `_transfer` function of the ERC20 token contract potentially incorrectly restricts the maximum transaction amount. The change from a logical OR (`||`) to a logical AND (`&&`) in the conditional check inadvertently allows transactions that exceed the `_maxTxAmount` limit if either `from` or `to` addresses are excluded from the maximum amount check. A user performs a token transfer where either the `from` address or the `to` address (but not both) is intended to be exempt from the maximum transaction amount check. However, with the current logic, the transaction will not be subject to the `_maxTxAmount` check, allowing potentially unrestricted transfer sizes.
Open the reportLowGas optimizationsMBD Financials (Token) · Paladin · 24 Apr 2024Open
The report gives no description here.
Open the reportContracts2
| Address | Chain | Source code |
|---|---|---|
| 0xa08898cabe14680cdfea55398143bc120889182e | Chain: Ethereum | Source code: Verified source |
| 0x4ff319847664b03a956d8f4f076a35ec2d4a6f46 | Chain: Ethereum | Source code: Verified source |
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="mbd-financials"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us