
Metacces audit reports
Metacces has 2 public audit reports from CertiK and SolidProof; the latest is CertiK, 19 Jul 2024; no critical findings reported. It also holds 4 deployed contracts on 1 chain.
Last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Open findings across every firm5
Statuses are the security firms’ own
5 findings are still open or acknowledged in the firms’ reports: 2 high, 1 medium, 2 low (all open).
- High
- 2
- Medium
- 1
- Low
- 2
- High Open
Centralization Related Risks
Metacces · CertiK · 19 Jul 2024 · Report ↗
- High Open
Initial Token Distribution
Metacces · CertiK · 19 Jul 2024 · Report ↗
- Medium Open
#1: Withdraw tokens from contract
Metacces · SolidProof · 6 Aug 2022 · Report ↗
- Low Open
#1: Bridge has no functionality
Metacces · SolidProof · 6 Aug 2022 · Report ↗
- Low Open
#1: floating pragma is
Metacces · SolidProof · 6 Aug 2022 · Report ↗
Audits2
Newest first
| Report | Security firm | Date | Scope | Critical findings | Findings | Source |
|---|---|---|---|---|---|---|
| Metacces | Security firm: CertiK | Date: | Scope: 3 addresses on BNB Chain | None open | Findings: 5 high · 8 medium · 7 low 18 fixed · 2 open | skynet.certik.com ↗ |
| Metacces | Security firm: SolidProof | Date: | Scope: 1 address on BNB Chain | None open | Findings: 1 medium · 2 low 3 open | IPFS ↗ |
Findings23
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 3 |
| Medium | 1 | 0 | 8 |
| Low | 2 | 0 | 7 |
HighCentralization Related RisksMetacces · CertiK · 19 Jul 2024Open
In the contract `AccesVesting` the role `owner` has authority over the functions shown as follows: - `transferOwnership`: This function is designed to transfer the ownership of the contract to a new owner. - `setMonthlyPercentage`: The `setMonthlyPercentage` function allows the contract owner to set a new monthly percentage (`mP`). - `addToBlackList`: The `addToBlackList` function adds an investor to the blacklist, preventing them from participating in certain contract activities. - `removeFromBlackList`: The `removeFromBlackList` function removes an investor from the blacklist, allowing them to participate again. - `activateSamePercentage`: The `activateSamePercentage` function allows the contract owner to enable the samePercentage feature by setting it to true. - `disableSamePercentage`: The `disableSamePercentage` function allows the owner to disable this feature by setting it to false. - `editInvestorLock`: The `editInvestorLock` function allows the contract owner to update the yearly and monthly percentage allocations for a specific investor. - `addInvestor`: The `addInvestor` function allows the contract owner to add a new investor with specific parameters, such as the investment amount, yearly percentage, lock time, and initial unlock time. - `withdrawalAcces`: This function allows the contract owner to withdraw Acces tokens from the contract. - `withdrawalBEP20`: This function allows the contract owner to withdraw BEP20 tokens (other than Acces) from the contract. - `withdrawalBNB`: This function allows the contract owner to withdraw BNB from the contract. Any compromise to the `owner` account may allow the hacker to take advantage of this authority to withdraw BEP20 tokens and native tokens. --- In the contract `Metacces` the role `owner` has authority over the functions shown in the diagram below. Any compromise to the `owner` account may allow the hacker to take advantage of this authority to take out BEP20 tokens and native tokens, start and end the sale, and change the minimum and maximum amount of private sales. 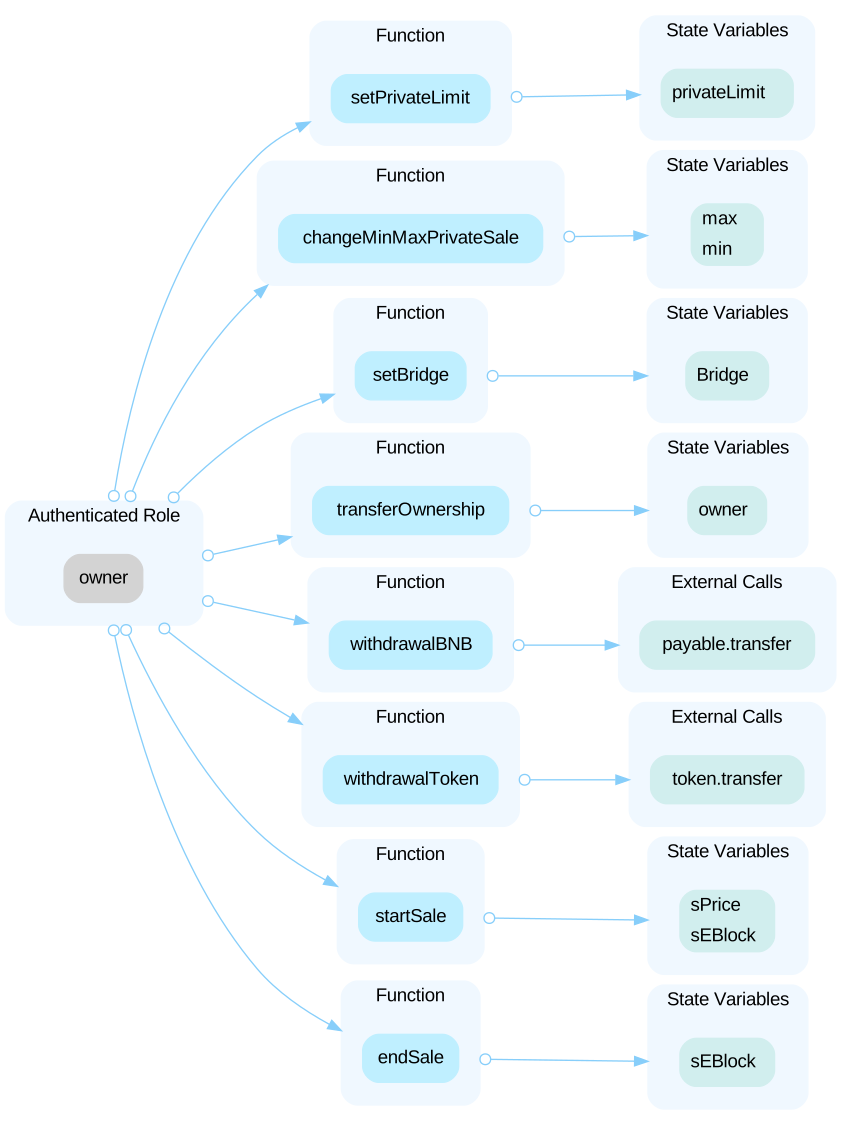 ---- The team has updated the `AccesVesting` contract. They removed the `onlyOwner` modifier and added OpenZeppelin's `AccessControl`. Now, the `ADMIN_ROLE` replaces the `owner`, and privileged functions can be called by anyone with the `ADMIN_ROLE`. The changes were reflected in the commit [02c8c1d5526b973909dd7f5f847a1ab0ca71e6b1](https://github.com/Metacces/AccesCoin/tree/02c8c1d5526b973909dd7f5f847a1ab0ca71e6b1).
Open the reportHighInitial Token DistributionMetacces · CertiK · 19 Jul 2024Open
90 % of the tokens are sent to `theCompany`. 10 % of the tokens are stored in the contract. This is a centralization risk because the `theCompany` account can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
Open the reportMedium#1: Withdraw tokens from contractMetacces · SolidProof · 6 Aug 2022Open
The report gives no description here.
Open the reportLow#1: Bridge has no functionalityMetacces · SolidProof · 6 Aug 2022Open
The report gives no description here.
Open the reportLow#1: floating pragma isMetacces · SolidProof · 6 Aug 2022Open
The report gives no description here.
Open the reportContracts4
| Address | Chain | Source code |
|---|---|---|
| 0x1e5c718b4377b5deeef01aff5bdc29a9528df1a3 | Chain: BNB Chain | Source code: Verified source |
| 0x5a72f21de88b96db1b2c16c8c81af846c103a674 | Chain: BNB Chain | Source code: Verified source |
| 0xfece3a7bbbc893907eb5e0e9dd8197e01f63f0d5 | Chain: BNB Chain | Source code: Verified source |
| 0xe52b49b35d10b0c9ebf6398aac4f7cd7a17a43e0 | Chain: BNB Chain | Source code: Verified source |
Metacces: questions
Is Metacces audited?
Trustblock holds 2 public audit reports for Metacces, dated 6 Aug 2022 to 19 Jul 2024. The latest is by CertiK (“Metacces”).
Who audited Metacces?
2 security firms wrote the reports Trustblock holds for Metacces: CertiK and SolidProof.
Are there open findings in Metacces’s audits?
5 findings are still open or acknowledged in the firms’ reports: 2 high, 1 medium, 2 low (all open). No critical finding is reported. Statuses are the security firms’ own.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="metacces"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us