Metahub has 1 public audit report from CertiK; dated 30 Aug 2023; no critical findings reported. It also holds 1 deployed contract on 1 chain.
Last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Statuses are the security firms’ own
17 findings are still open or acknowledged in the firms’ reports: 3 high, 3 medium, 11 low (14 open, 3 acknowledged).
Centralization Related Risks
METAHUBToken · CertiK · 30 Aug 2023 · Report ↗
Centralization Risks in METAHUBToken.sol
METAHUBToken · CertiK · 30 Aug 2023 · Report ↗
Centralized Token Holding Position Risk
METAHUBToken · CertiK · 30 Aug 2023 · Report ↗
Incorrect Condition Check
METAHUBToken · CertiK · 30 Aug 2023 · Report ↗
Incorrect validations
METAHUBToken · CertiK · 30 Aug 2023 · Report ↗
Logical issue of transfer to zero address
METAHUBToken · CertiK · 30 Aug 2023 · Report ↗
Divide Before Multiply
METAHUBToken · CertiK · 30 Aug 2023 · Report ↗
Logical issue about _validateSelling
METAHUBToken · CertiK · 30 Aug 2023 · Report ↗
Logical issue about cashOutTaxPercentage
METAHUBToken · CertiK · 30 Aug 2023 · Report ↗
Logical issue about totalTaxPercentage
METAHUBToken · CertiK · 30 Aug 2023 · Report ↗
Newest first
| Report | Security firm | Date | Scope | Critical findings | Findings | Source |
|---|---|---|---|---|---|---|
| METAHUBToken | Security firm: CertiK | Date: | Scope: 1 address on Polygon (POS) | None open | Findings: 3 high · 3 medium · 11 low 3 acknowledged · 14 open | skynet.certik.com ↗ |
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 3 | 0 | 0 |
| Medium | 0 | 3 | 0 |
| Low | 11 | 0 | 0 |
In the contract `METAHUBToken` the roles `developmentAddress` and `mn` have authority over the functions shown in the diagram below. Any compromise to the `developmentAddress` and `mn` accounts may allow the hacker to take advantage of this authority and mint vesting MetaHub tokens to the `developmentAddress` EOA address. 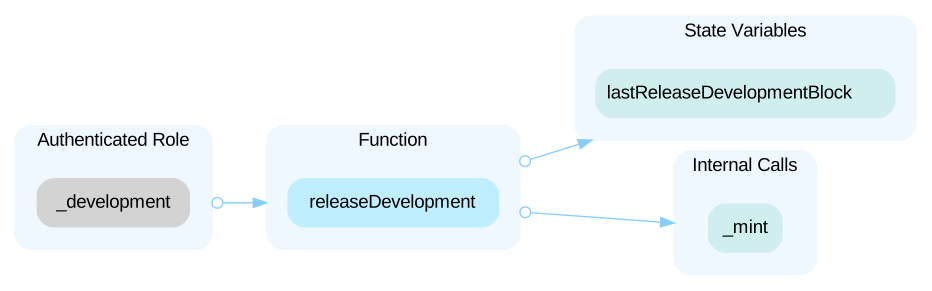 In the contract `METAHUBToken` the role `vault` has authority over the functions shown in the diagram below. Any compromise to the `vault` account may allow the hacker to take advantage of this authority and mint up to `maxMintingBeMinted` MetaHub tokens to the `vault` address. 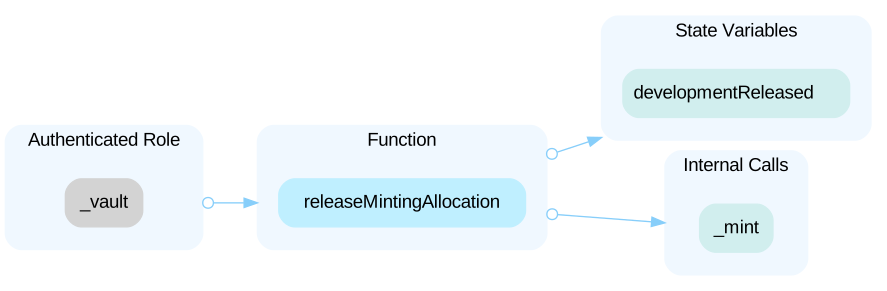
Open the reportIn the contract `METAHUBToken` the role `mn` has authority over the functions shown in the diagram below. Any compromise to the `mn` account may allow the hacker to take advantage of this authority and: - startVestingDevelopment(), to start the vesting of `developmentAddress` and mint 20% of DEVELOPMENT_ALLOCATION tokens to the `developmentAddress`. - updateTwoWayTaxWhitelist(), to update `twoWayTaxWhitelist`. - updateWaitStatus(), to update `config.wait`. - updateWaitingStatus(), to update `waitingList`. - disableWaitingFunction(), to disable `config.waitingFunctionEnabled`. - updateMaxContractMinting(), to update `maxMintingBeMinted` and `maxCLSBeMinted`. - setAddressBook(), to set the `addressBook` and call the internal function `_initDependentContracts()`. The `_initDependentContracts()` function can set the sensitive state variables such as uniswapV2Router, menToken, usdtToken, lpToken, swapAddress and etc. And it can approve unlimited allowance to these addresses. - updateConfig(), to update the config. - updateSoftCap(), to update the `config.softCap[_user]` for a user. - updateTaxWhitelist(), to update the `whitelistTax[_user][_type]`. - updateLSDTaxDiscount(), to update the `lsdDiscountTaxPercentages[_type]`. 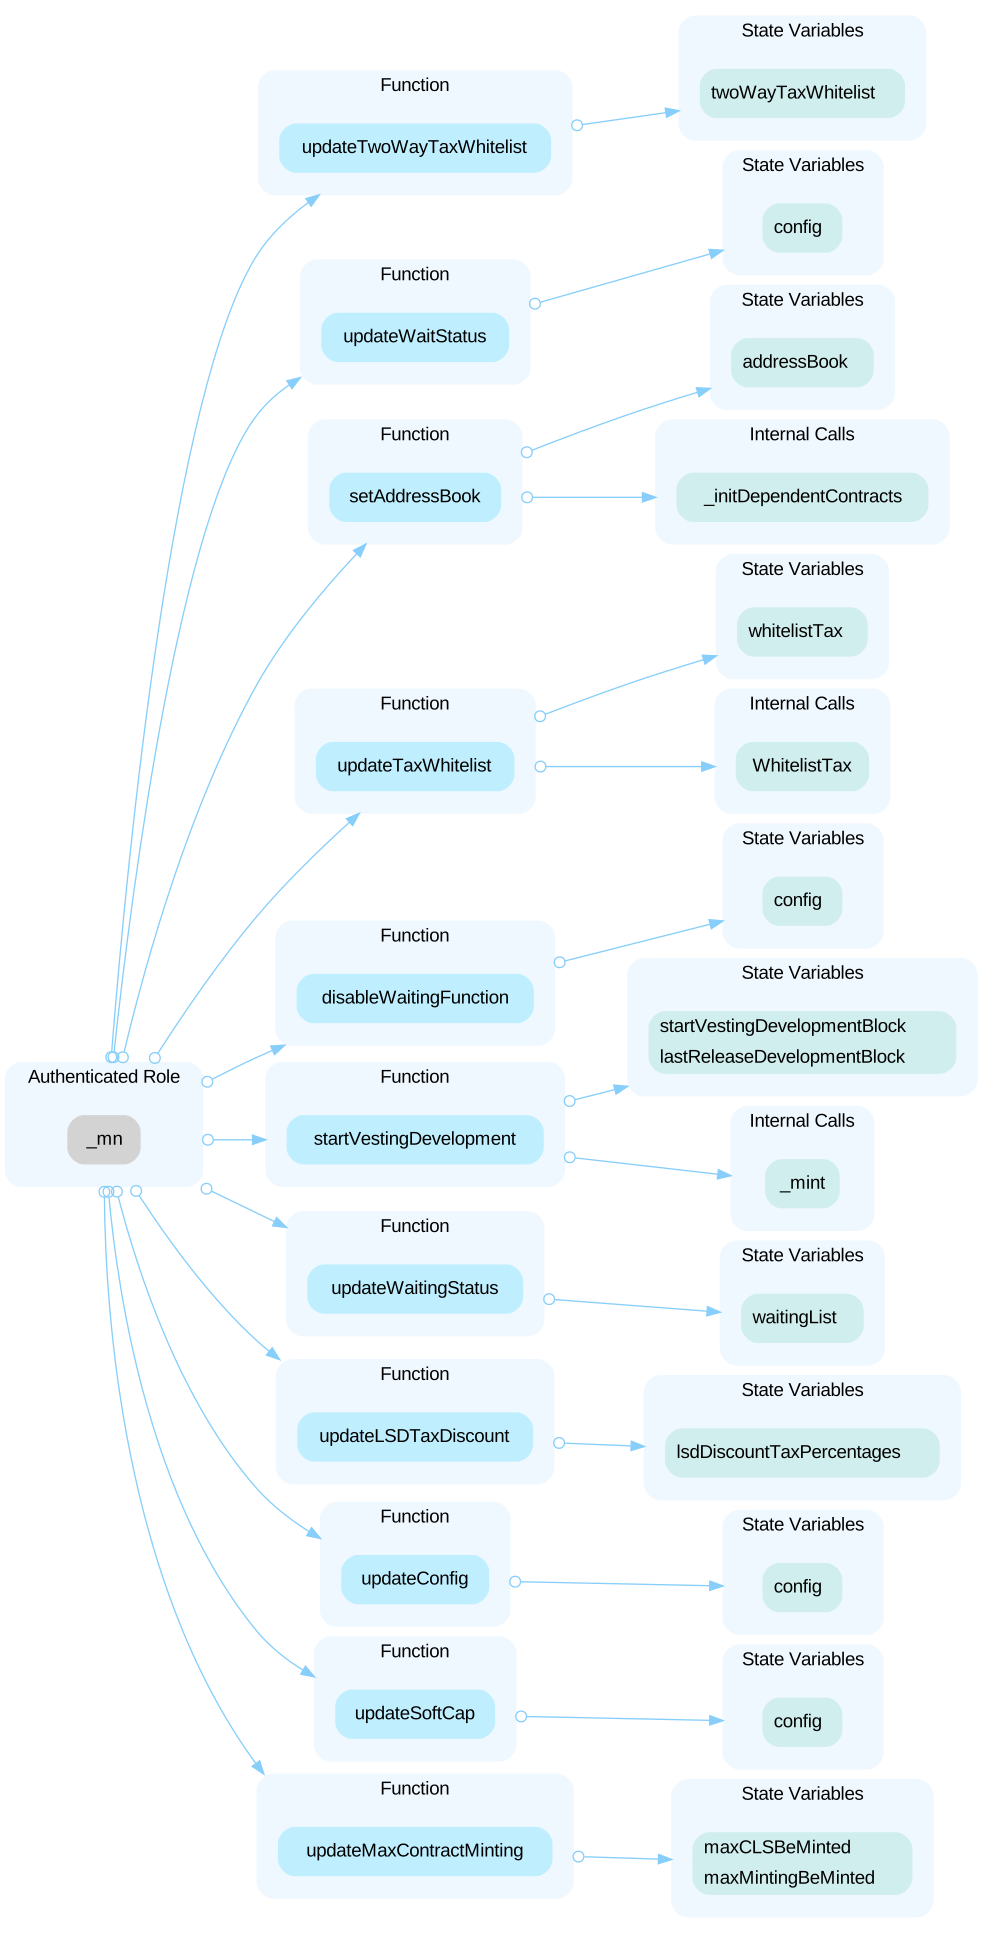 In the contract `METAHUBToken` the role `clsAddress` has authority over the functions shown in the diagram below. Any compromise to the `clsAddress` account may allow the hacker to take advantage of this authority and mint up to `maxCLSBeMinted` amount of MetaHub tokens to the CLS contract. 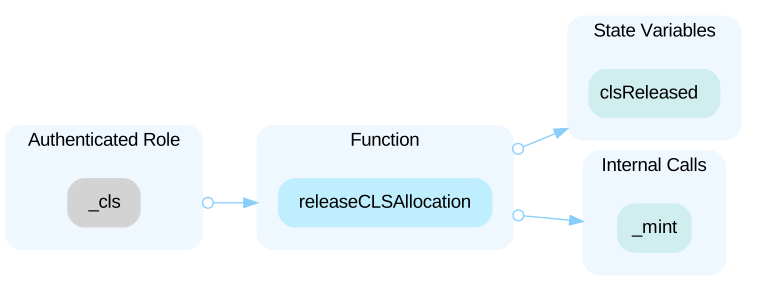 In the contract `TokenAuth` the role `bk` has authority over the functions shown in the diagram below. Any compromise to the `bk` account may allow the hacker to take advantage of this authority and update the roles `bk` and `mn`. 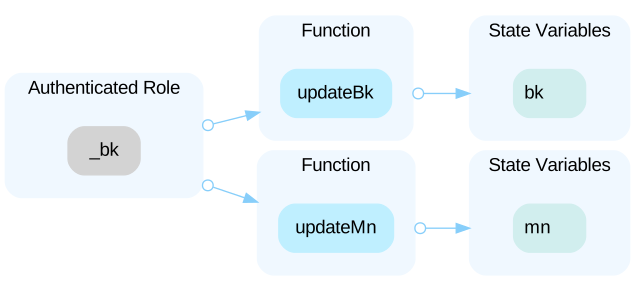
Open the reportIn the contract METAHUBToken, tokens are gradually centralized into the `taxManager` address over time. This creates a severe centralization risk and can lead to manipulation of the tokenomics of the project. ```solidity function _transfer(address _from, address _to, uint _value) private { ... uint tax = _calculateTax(_from, _to, _value); if (tax > 0) { _balances[_to] += _value - tax; _balances[address(taxManager)] += tax; emit Transfer(_from, address(taxManager), tax); } ... } ``` Any compromise to the private keys of the taxManager address may allow a hacker to take advantage of the address authority and sell tokens on the market and/or remove the pool liquidity, causing a severe price drop.
Open the reportPerforming integer division before multiplication truncates the low bits, losing the precision of calculation. ```solidity=292 uint baseTax = _value * 1000 / taxManager.totalTaxPercentage(); ``` ```solidity=300 return baseTax * (oneHundredPercentageDecimal3 - lsdDiscountTaxPercentages[IMENToken.TaxType.Buy]) / oneHundredPercentageDecimal3; ``` --- ```solidity=322 return baseTax * (oneHundredPercentageDecimal3 - lsdDiscountTaxPercentages[IMENToken.TaxType.Claim]) / oneHundredPercentageDecimal3; ``` ```solidity=342 baseTax = baseTax * (oneHundredPercentageDecimal3 - lsdDiscountTaxPercentages[IMENToken.TaxType.Transfer]) / oneHundredPercentageDecimal3; ```
Open the reportWhen selling tokens, there is a validation `_validateSelling` for cap and time interval checks. However, if the `userWhitelistTax.status` is true, the tax value is directly returned and the valition will not be effected.
Open the reportWhen the sold value is greater than the `cashOutTaxPercentage` of the deposited amount, the seller will be charged 50% selling tax. ```solidity=337 (uint deposited,) = vault.getUserInfo(_from); if (_value >= deposited * config.cashOutTaxPercentage / 100) { baseTax = _value / 2; } ```
Open the reportThe scalar factor used to compute the base tax is determined by the `totalTaxPercentage` function of the external contract `taxManager`. This prevents readers of `METAHUBToken` from knowing the bounds on how much a transaction will be taxed.
Open the reportThe function `_validateAbility` is used for many different external function calls. Only one address is validated, but operations generally involve multiple parties such as `_from`, `_to`, and `_msgSender`. We would like to know how the validated address is chosen for each external function. In particular, why does `transferFrom` validate the `_from` address but not `msg.sender`? Why does `mint` validate the `_to` address while `transfer` does not? Why does `startVestingDevelopment` validate any address considering that its caller `Mn` has control over the `config.wait` flag and the `waitingList` array? Have you considered perform validation directly in the external function calls instead of `_transfer` and `_mint` for greater control?
Open the reportThe field `METAHUBToken.Config.secondsInADay` leads readers to believe that its value is the number of seconds in a day. However, this field can be assigned to arbitrary values at different points in time, whereas the number of seconds in a day remains constant at 86400.
Open the reportSome address book values are set in the function `_initDependentContracts()`. The `_initDependentContracts()` function will be called in the `setAddressBook()` function together with setting the addressBook. So it is not neccesary to call the external functions addressBook.get in the below codes: ```solidity if ( twoWayTaxWhitelist[_from] || twoWayTaxWhitelist[_to] || _to == addressBook.get("vault") || _from == addressBook.get("cls") || _to == addressBook.get("cls") || _from == addressBook.get("lsd") || _to == addressBook.get("lsd") || ... ) { return 0; }
Open the reportThe contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=54 IAddressBook public addressBook; ``` - The contract `METAHUBToken` interacts with third party contract with `IAddressBook` interface via `addressBook`. --- ```solidity=55 ITaxManager public taxManager; ``` - The contract `METAHUBToken` interacts with third party contract with `ITaxManager` interface via `taxManager`. --- ```solidity=56 ILSD public lsd; ``` - The contract `METAHUBToken` interacts with third party contract with `ILSD` interface via `lsd`. --- ```solidity=13 IAddressBook public addressBook; ``` - The contract `Auth` interacts with third party contract with `IAddressBook` interface via `addressBook`.
Open the reportSome events are never emitted, which can lead to confusion and code maintainability issues. ```solidity=72 event WaitingStatusUpdated(address user, bool status, uint timestamp); ``` - `WaitingStatusUpdated` is declared in `METAHUBToken` but never emitted.
Open the reportSome state variables are not used in the codebase. This can lead to incomplete functionality or potential vulnerabilities if these variables are expected to be utilized. Some variables in `METAHUBToken` are never used. ```solidity=12 uint public startVestingAdvisorAndTeamBlock; ``` ```solidity=58 uint private constant DECIMAL3 = 1000; ``` ```solidity=12 contract METAHUBToken is IBEP20, TokenAuth { ```
Open the reportSome state variables are not used in the codebase. This can lead to incomplete functionality or potential vulnerabilities if these variables are expected to be utilized. Variable `DECIMAL3` in `METAHUBToken` is never used in `METAHUBToken`. ```solidity=58 uint private constant DECIMAL3 = 1000; ``` ```solidity=12 contract METAHUBToken is IBEP20, TokenAuth { ```
Open the report| Address | Chain | Source code |
|---|---|---|
| 0x94b9…aa120x94b959c93761835f634b8d6e655070c58e2caa12 | Chain: Polygon (POS) | Source code: Verified source |
Trustblock holds 1 public audit report for Metahub, dated 30 Aug 2023. The latest is by CertiK (“METAHUBToken”).
CertiK wrote the report Trustblock holds for Metahub.
17 findings are still open or acknowledged in the firms’ reports: 3 high, 3 medium, 11 low (14 open, 3 acknowledged). No critical finding is reported. Statuses are the security firms’ own.
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="metahub-global"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us