
MetalSwap audit reports
MetalSwap has 1 public audit report from CertiK; dated 5 Dec 2022; 6 critical findings, 6 open.
Last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Open findings across every firm10
Statuses are the security firms’ own
10 findings are still open or acknowledged in the firms’ reports: 6 critical, 3 high, 1 low (all open).
- Critical
- 6
- High
- 3
- Low
- 1
- Critical Open
Centralization Related Risks
MetalSwap (Audit #2) · CertiK · 5 Dec 2022 · Report ↗
- Critical Open
Centralization Risks in `FeeManager.sol`
MetalSwap (Audit #2) · CertiK · 5 Dec 2022 · Report ↗
- Critical Open
Centralization Risks in `MetalSwapAbstract.sol`
MetalSwap (Audit #2) · CertiK · 5 Dec 2022 · Report ↗
- Critical Open
Centralization Risks in `MetalSwapPoolAbstract.so
MetalSwap (Audit #2) · CertiK · 5 Dec 2022 · Report ↗
- Critical Open
Centralization Risks in `SettlementFeeContainer.s
MetalSwap (Audit #2) · CertiK · 5 Dec 2022 · Report ↗
- Critical Open
Centralization Risks in `StakingPoolV2Base.sol` a
MetalSwap (Audit #2) · CertiK · 5 Dec 2022 · Report ↗
- High Open
Centralization Related Risks in `ETHUSDTSwap.sol`
MetalSwap (Audit #2) · CertiK · 5 Dec 2022 · Report ↗
- High Open
Centralization Risks in `NFTDescriptor.sol`
MetalSwap (Audit #2) · CertiK · 5 Dec 2022 · Report ↗
- High Open
Initial Token Distribution
MetalSwap (Audit #2) · CertiK · 5 Dec 2022 · Report ↗
- Low Open
Third Party Dependency
MetalSwap (Audit #2) · CertiK · 5 Dec 2022 · Report ↗
Audits1
Newest first
| Report | Security firm | Date | Scope | Critical findings | Findings | Source |
|---|---|---|---|---|---|---|
| MetalSwap (Audit #2) | Security firm: CertiK | Date: | Scope: Files listed | 6 open critical findings | Findings: 6 critical · 3 high · 2 medium · 20 low 21 fixed · 10 open | skynet.certik.com ↗ |
Findings31
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 6 | 0 | 0 |
| High | 3 | 0 | 0 |
| Medium | 0 | 0 | 2 |
| Low | 1 | 0 | 19 |
CriticalCentralization Related RisksMetalSwap (Audit #2) · CertiK · 5 Dec 2022Open
In the contracts `ETHPool.sol`, `USDTPool.sol`, and `WBTCPool.sol`, the role `onlyHighLevelAccess` has authority over the following functions: - `sendPremium()` - `send()` - `sendProfit()` Any compromise to the `onlyHighLevelAccess` account may allow a hacker to take advantage of this authority and wipe the contracts of all ether or tokens.
Open the reportCriticalCentralization Risks in `FeeManager.sol`MetalSwap (Audit #2) · CertiK · 5 Dec 2022Open
In the contract `FeeManager` the role `owner` has authority over the functions shown in the diagram below. Any compromise to the `owner` account may allow the hacker to take advantage of this authority and: * Transfer the entire balance of `ETH` or any `ERC20` tokens out of the contract to the `owner` address. 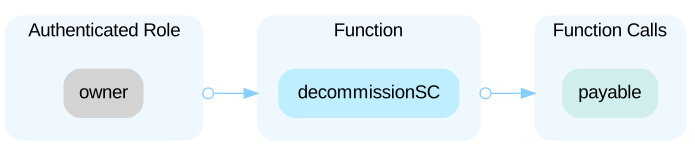 In the contract `FeeManager` the roles `_governance` and `owner` has authority over the functions: * `setiV()` * `setSettlementFeePerc()` Any compromise to the `_governance` or `owner` accounts may allow the hacker to take advantage of this authority and: * Set `iV` to any value. * Set `settlementFeePerc` to any value between 0 and 100,000,000.
Open the reportCriticalCentralization Risks in `MetalSwapAbstract.sol`MetalSwap (Audit #2) · CertiK · 5 Dec 2022Open
In the contract `MetalSwapAbstract` the role `owner` has authority over the functions shown in the diagram below. Any compromise to the `owner` account may allow the hacker to take advantage of this authority and: * Set `marginFactorAsset` and `marginFactorCurrency` to any value. * Set the `settlementFeeContainer` contract to any address. * Set the `rateReward` to any value, which is used to calculate the reward rate per second for the `getReward()` function. * Transfer the privildeged role `_governance` to any address. * Set the `swapAvgCurrency` to any value, which is used to calculate the bonus percentage additionally added to rewards. * Set the `swapAvgAsset` to any value, which is used to calculate the bonus percentage additionally added to rewards. * Set the `PRICE_DECIMALS` to any value, which is used to increase/decrease the number of decimal places for an asset during calculations. * Set the `AggregatorInterface` address `priceProvider`, which is in charge of returning the latest price for an asset. * Set the `poolAsset` address, which is used to retrieve the asset balance in that address. This balance is used to calculate the availability of the asset. * Set the `poolCurrency` address, which is used to retrieve the currency balance in that address. This balance is used to calculate the availability of the currency. * Pause and unpause the following unimplemented functions: * `createSwap()` * `closeSwap()` * `executeSwap()` * `marginCall()` * `addCover()` * Transfer the entire balance of `ETH` or any `ERC20` tokens out of the contract to the `owner` address. 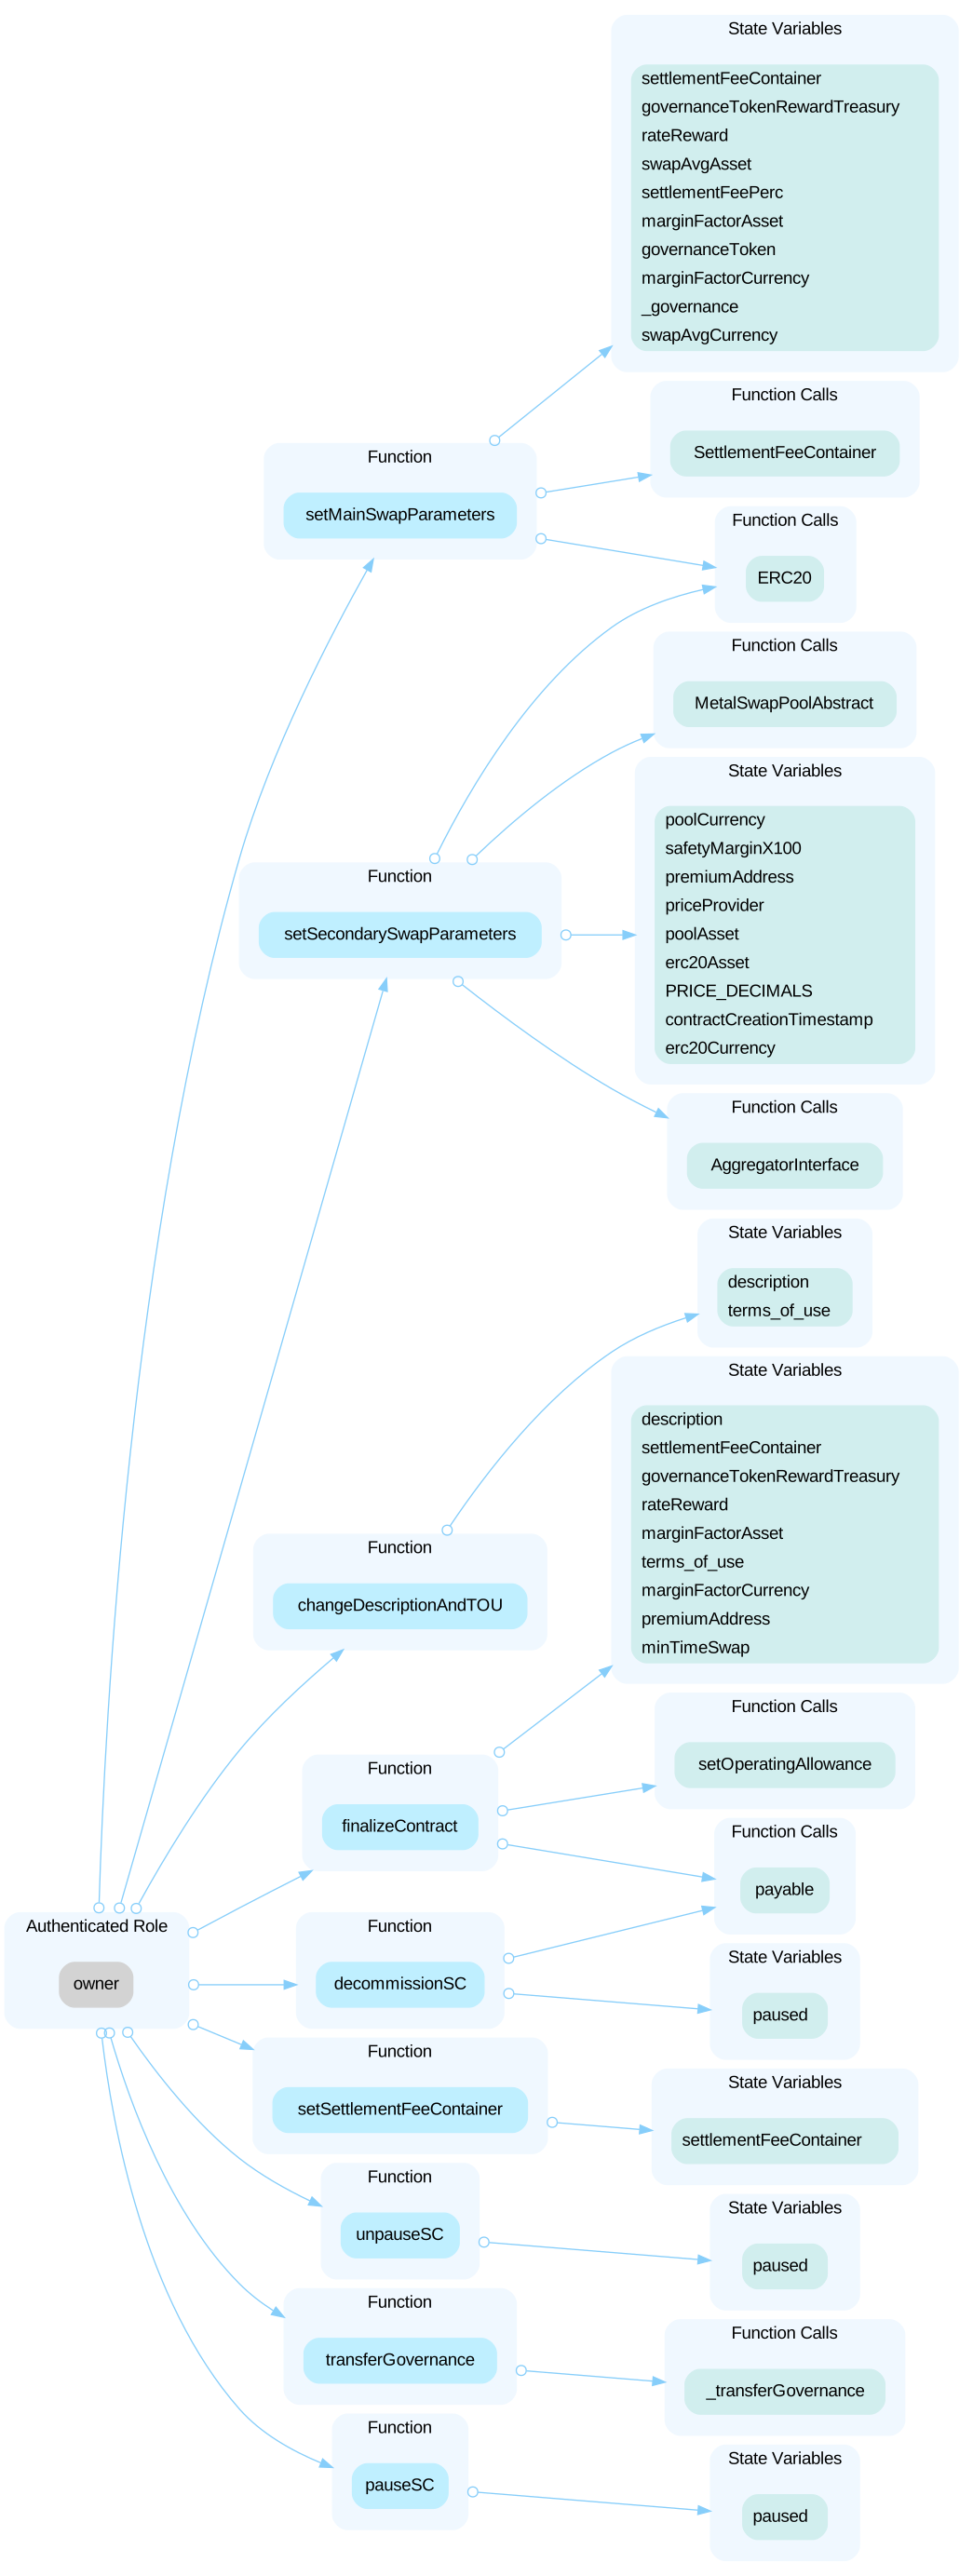 In the contract `MetalSwapAbstract` the roles `_governance` and `owner` has authority over the functions: * `setOperatingAllowance()` * `setTokenRewardTreasury()` * `setSafetyMarginX100()` * `setRewardRate()` * `setMinTimeSwap()` * `setMarginFactorAsset()` * `setMarginFactorCurrency()` Any compromise to the `_governance` or `owner` accounts may allow the hacker to take advantage of this authority and: * Set the `rateReward` to any value, which is used to calculate the reward rate per second for the `getReward()` function. * Set `marginFactorAsset` and `marginFactorCurrency` to any value.
Open the reportCriticalCentralization Risks in `MetalSwapPoolAbstract.soMetalSwap (Audit #2) · CertiK · 5 Dec 2022Open
In the contract `MetalSwapPoolAbstract` the role `owner` has authority over the functions shown in the diagram below. Any compromise to the `owner` account may allow the hacker to take advantage of this authority and: * Add and remove addresses from the privildeged role `swapPairsManagement`. * Pause and unpause functions with the modifier `checkSCUnpaused()`. Currently there are no functions with this modifier. * Transfer the entire balance of `ETH` or any `ERC20` tokens out of the contract to the `owner` address. 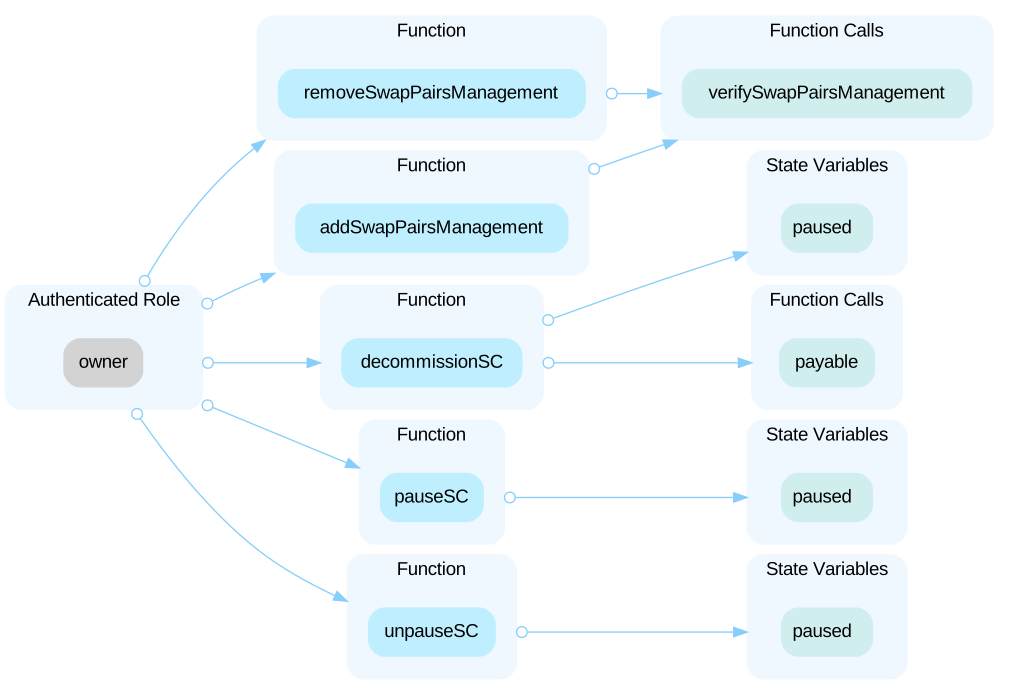 \ In the contract `MetalSwapPoolAbstract` the roles `swapPairsManagement` and `owner` has authority over the functions: * `changeNFTDescriptor()` * `finalizePool()` * `lock()` * `unlock()` * `sendPremium()` * `unlockPremium()` * `send()` * `sendProfit()` * `changeDescriptionAndTOU()` * `setMinLiquidity()` * `setLockupPeriod()` * `setRewardTokensPerDay()` Any compromise to the `swapPairsManagement` or `owner` accounts may allow the hacker to take advantage of this authority and: * Send reward tokens to the contract to be distributed in the future * Set the `rewardTokensPerDay` to any value, which dictates the number of reward tokens issued to liquidity providing positions. * Lock and unlock any amount of funds in the contract. * Unlock any amount of locked premium in the contract. * Set the `lockupPeriod` to any value, which is used to calculate the percentage of penalties taken from a premature withdraw.
Open the reportCriticalCentralization Risks in `SettlementFeeContainer.sMetalSwap (Audit #2) · CertiK · 5 Dec 2022Open
In the contract `SettlementFeeContainer` the role `owner` has authority over the functions shown in the diagram below. Any compromise to the `owner` account may allow the hacker to take advantage of this authority and: * Add and remove addresses from the privileged role `swapPairsManagement`. * Pause and unpause the function `payLiquidationFee()` from being called. * Transfer the entire balance of `ETH` or any `ERC20` tokens out of the contract to the `owner` address. 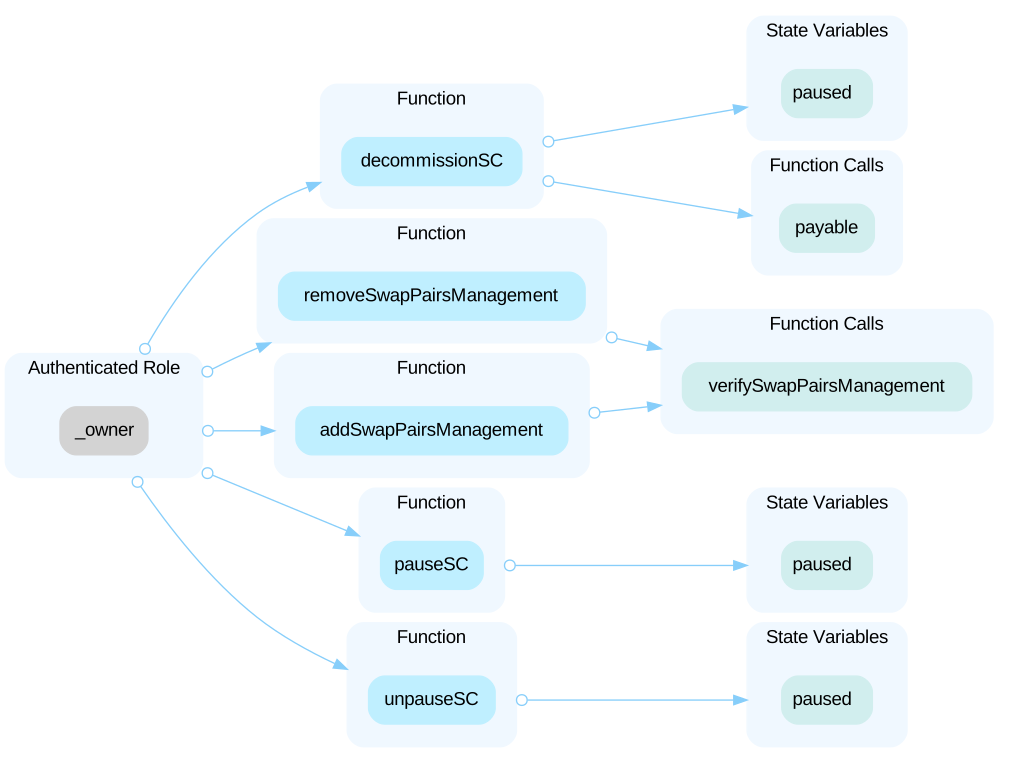 \ In the contract `SettlementFeeContainer` the roles `swapPairsManagement` and `owner` has authority over the function: * `payLiquidationFee()` Any compromise to the `swapPairsManagement` or `owner` accounts may allow the hacker to take advantage of this authority and: * Transfer any amount of `ETH` or `ERC20` tokens out of the contract to any destination address.
Open the reportCriticalCentralization Risks in `StakingPoolV2Base.sol` aMetalSwap (Audit #2) · CertiK · 5 Dec 2022Open
In the contract `StakingPoolV2Base` the roles `_owner` and `_governance` have authority over the following functions. * `finalizePoolCreation()` * `addRewardTokensAmount()` * `setTime()` * `closePool()` * `pauseStaking()` * `unpauseStaking()` Any compromise to the `_owner` or `_governance` account may allow the hacker to take advantage of this authority by closing the pool, wiping the contract of all its tokens, pausing staking and then renouncing ownership, which would disrupt total functionality. ---- In the contract `StakingPoolSlowRelease` the role `_governance` has authority over the following functions. * `finalizePoolCreation()` * `finalizeRedeemParameters()` Any compromise to the `_governance` account may allow the hacker to take advantage of this authority and create a pool with potentially unintended parameters.
Open the reportHighCentralization Related Risks in `ETHUSDTSwap.sol`MetalSwap (Audit #2) · CertiK · 5 Dec 2022Open
In the contracts ETHUSDTSwap.sol and WBTCUSDTSwap.sol, the roles `onlyOwner` and `onlyGovernance` have authority over the following functions: - `transferGovernance()` - `setOperatingAllowance()` Any compromise to the `onlyOwner` or `onlyGovernance` account may allow a hacker to take advantage of this authority and transfer governance to an address he/she controls, which can be used to approve the associated addresses to be allowed to transfer anything from these contracts.
Open the reportHighCentralization Risks in `NFTDescriptor.sol`MetalSwap (Audit #2) · CertiK · 5 Dec 2022Open
In the contract `NFTDescriptor` the role `owner` has authority over the functions shown in the diagram below. Any compromise to the `owner` account may allow the hacker to take advantage of this authority and: * Set which token addresses will receive an advantage during SVG generation to obtain more rare features. 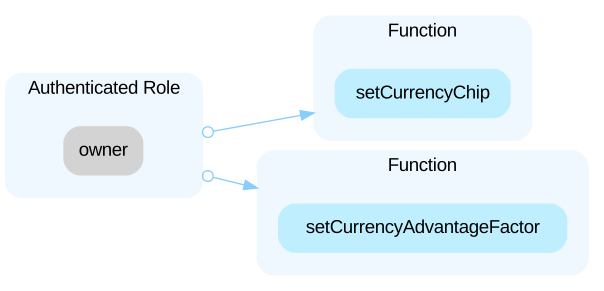
Open the reportHighInitial Token DistributionMetalSwap (Audit #2) · CertiK · 5 Dec 2022Open
All of the `XMT` tokens are sent to the contract deployer when deploying the contract. This could be a centralization risk as the deployer can distribute `XMT` tokens without obtaining the consensus of the community.
Open the reportLowThird Party DependencyMetalSwap (Audit #2) · CertiK · 5 Dec 2022Open
The contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assume their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=32 AggregatorInterface public priceProvider; ``` - The contract `MetalSwapAbstract` interacts with third party contract with Chainlink's `AggregatorInterface` interface via `priceProvider`.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
MetalSwap: questions
Is MetalSwap audited?
Trustblock holds 1 public audit report for MetalSwap, dated 5 Dec 2022. The latest is by CertiK (“MetalSwap (Audit #2)”).
Who audited MetalSwap?
CertiK wrote the report Trustblock holds for MetalSwap.
Are there open findings in MetalSwap’s audits?
10 findings are still open or acknowledged in the firms’ reports: 6 critical, 3 high, 1 low (all open). Of 6 critical findings: 6 open. Statuses are the security firms’ own.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="metalswap"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us