
NetMind security record
As of 24 Oct 2026, NetMind has 2 audit reports by 1 security firm on Trustblock; the latest is by CertiK, dated 13 Jan 2025. Those reports list no open critical findings.
Record last updated . It holds audits and findings, contracts and incidents up to Oct 2026. Trustblock does not review code.
Audits2
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| NetMind XYZ | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
| NetMind-Audit | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
Findings65
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 6 | 5 |
| Medium | 0 | 4 | 10 |
| Low | 10 | 5 | 25 |
HighCentralization Related RisksNetMind XYZ · CertiK · 13 Jan 2025Acknowledged
In the contract `AgentFactory`, the role `_bonding` has authority over the functions shown in the diagram below. Any compromise to the `_bonding` account may allow the hacker to take advantage of this authority and register a new application, graduate a token with specified dex pair. 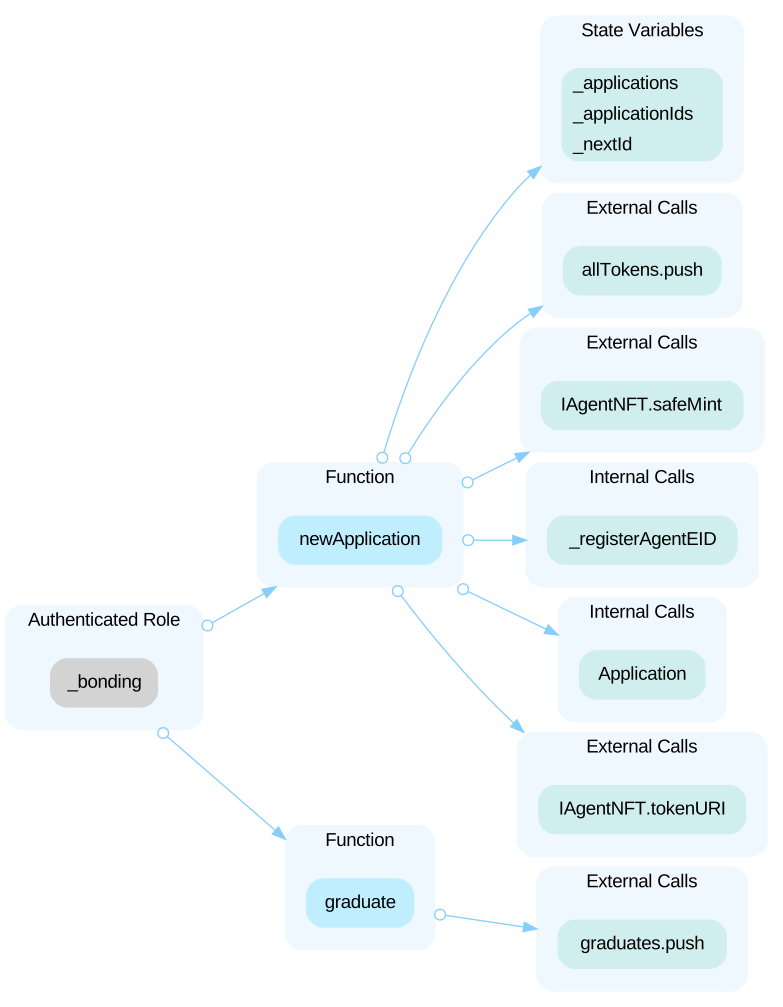 In the contract `AgentFactory`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set the bonding address, set the agent NFT address, and set the vault address. 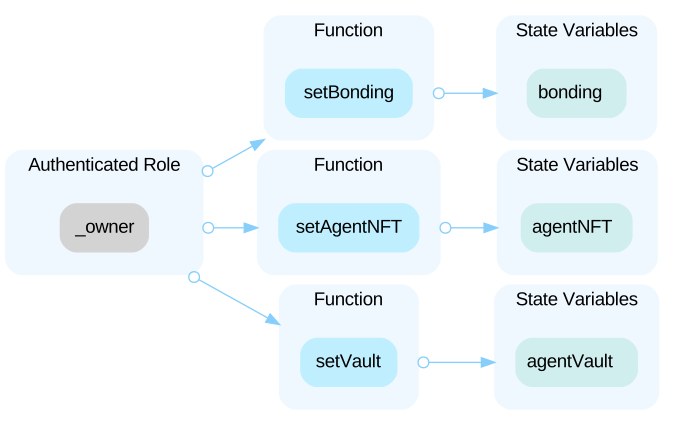 In the contract `NetmindAgentNFT`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and mint new tokens safely. 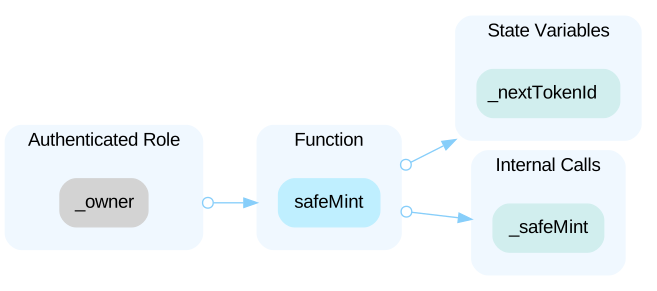 In the contract `AgentToken`, the role `_ownerorbonding` has authority over the functions shown in the diagram below. Any compromise to the `_ownerorbonding` account may allow the hacker to take advantage of this authority and set the swap threshold basis points, set project tax rates, set the token status, add a new liquidity pool address, remove a liquidity pool, withdraw ETH to a specified address, set the project tax recipient, and withdraw specified ERC20 tokens to a given address. 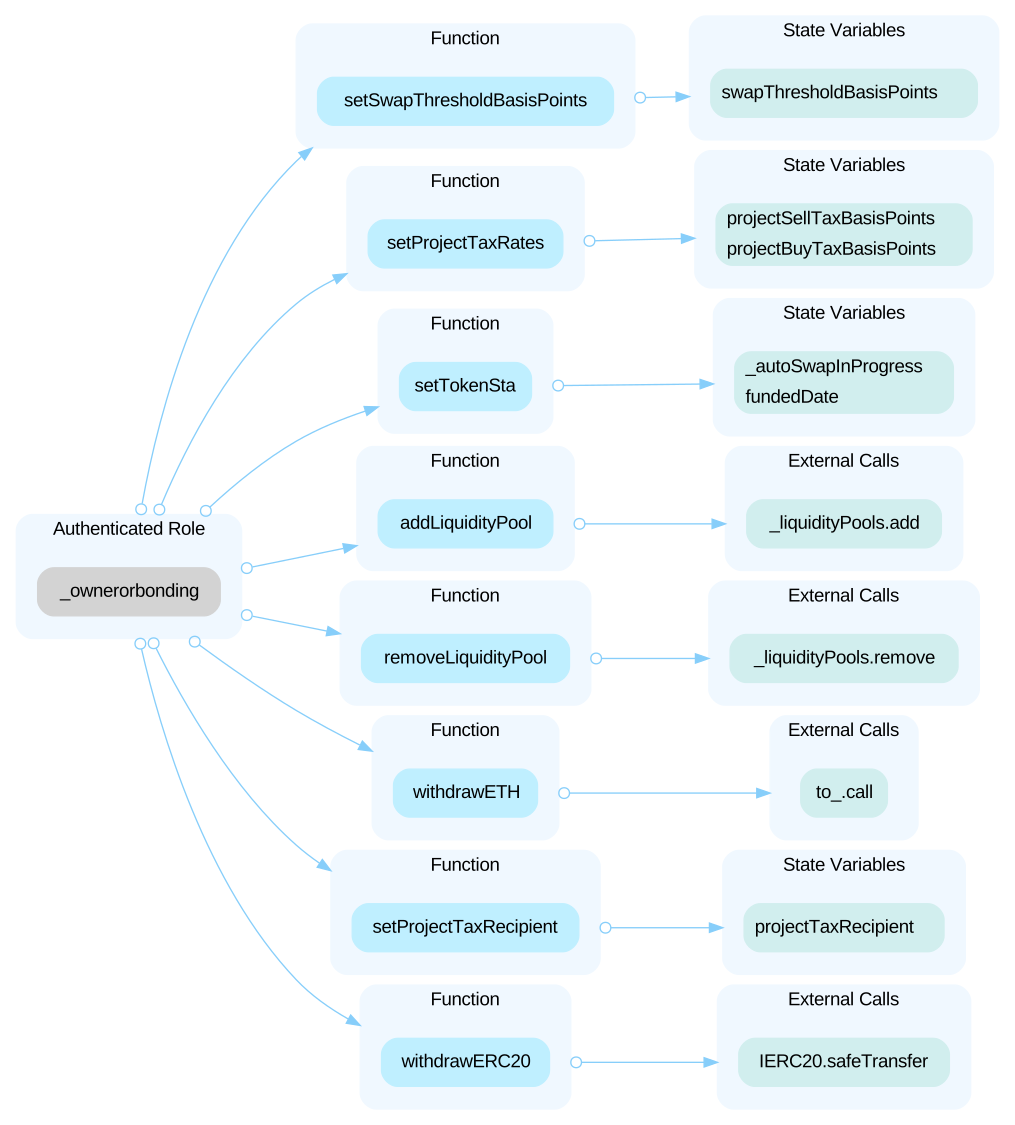 In the contract `AgentVault`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and safely transfer token ownership. 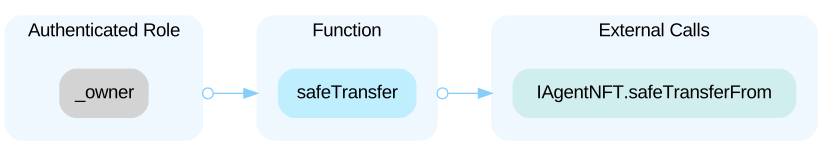 In the contract `StakeVault`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set the lock period, withdraw tokens after the lock period ends, and burn tokens by transferring to address zero. 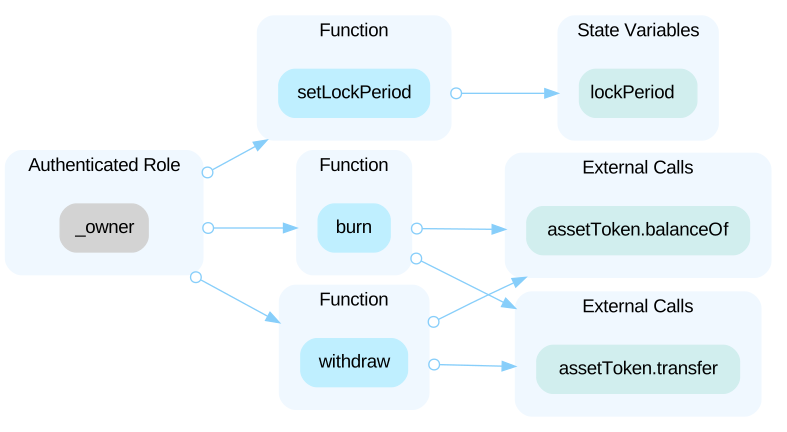 In the contract `Bonding`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set the agent token implementation address, set the stake vault implementation address, set token admin address, set the grad threshold, set token parameters, set the initial supply, set the fee and fee recipient address, and set the asset rate and set the token information. 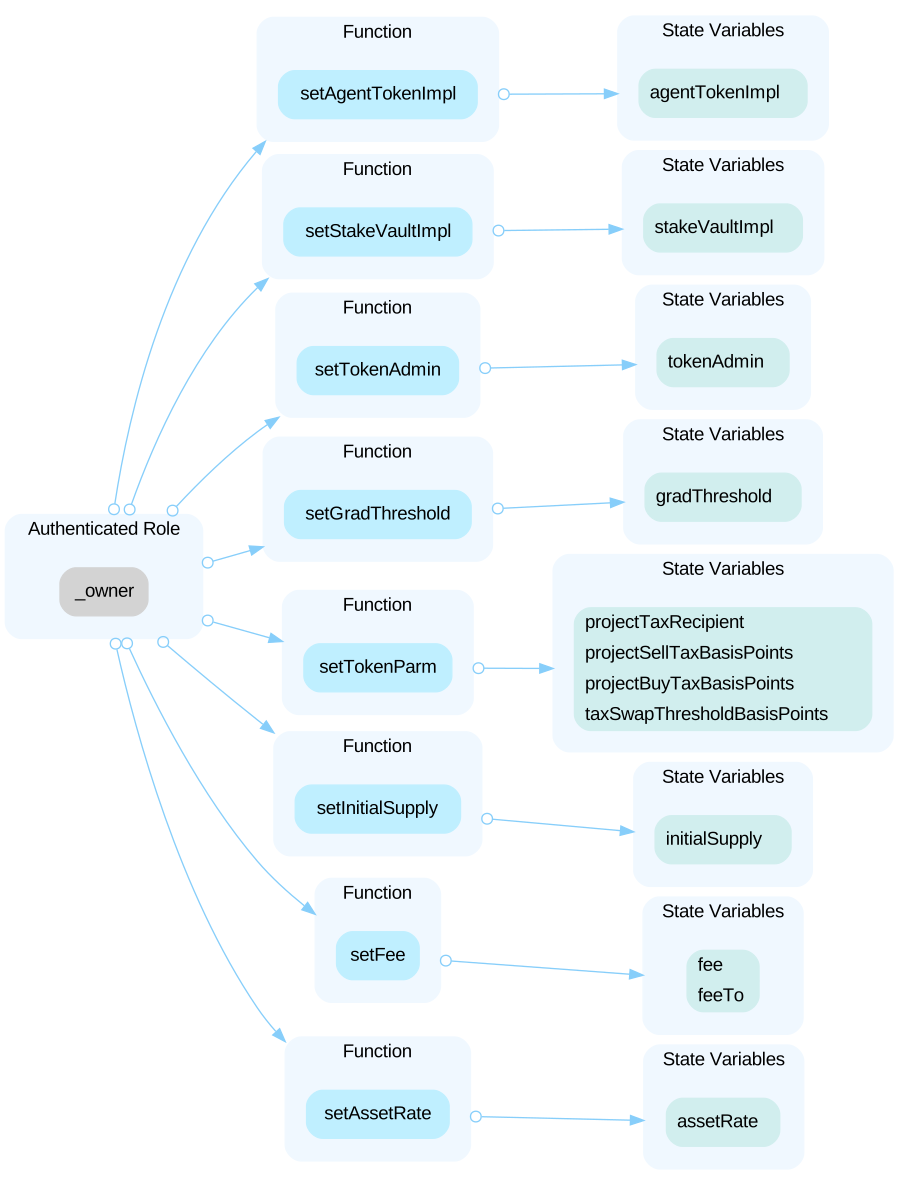 In the contract `FFactory`, the role `ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ADMIN_ROLE` account may allow the hacker to take advantage of this authority and set tax parameters or set the router address. 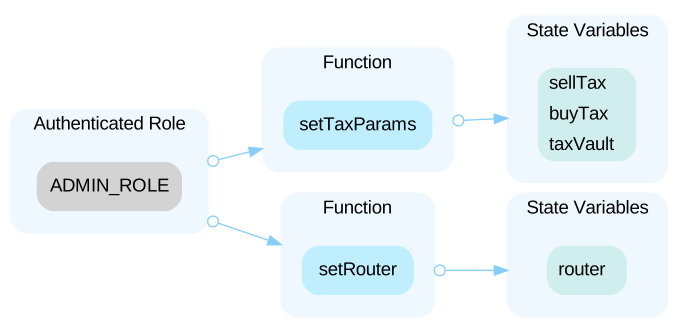 In the contract `FFactory`, the role `CREATOR_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `CREATOR_ROLE` account may allow the hacker to take advantage of this authority and create a token pair. 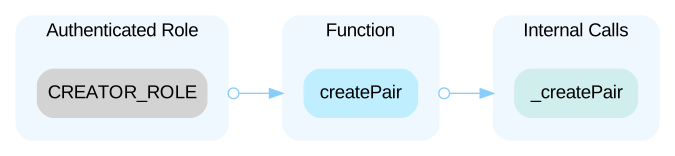 In the contract `FRouter`, the role `EXECUTOR_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `EXECUTOR_ROLE` account may allow the hacker to take advantage of this authority and transfer tokens and assets from a specified token address, sell tokens and transfer assets with fees, add initial liquidity to a token pair, approve asset spending for a given pair and spender, and perform a token purchase with a specified amount and address. 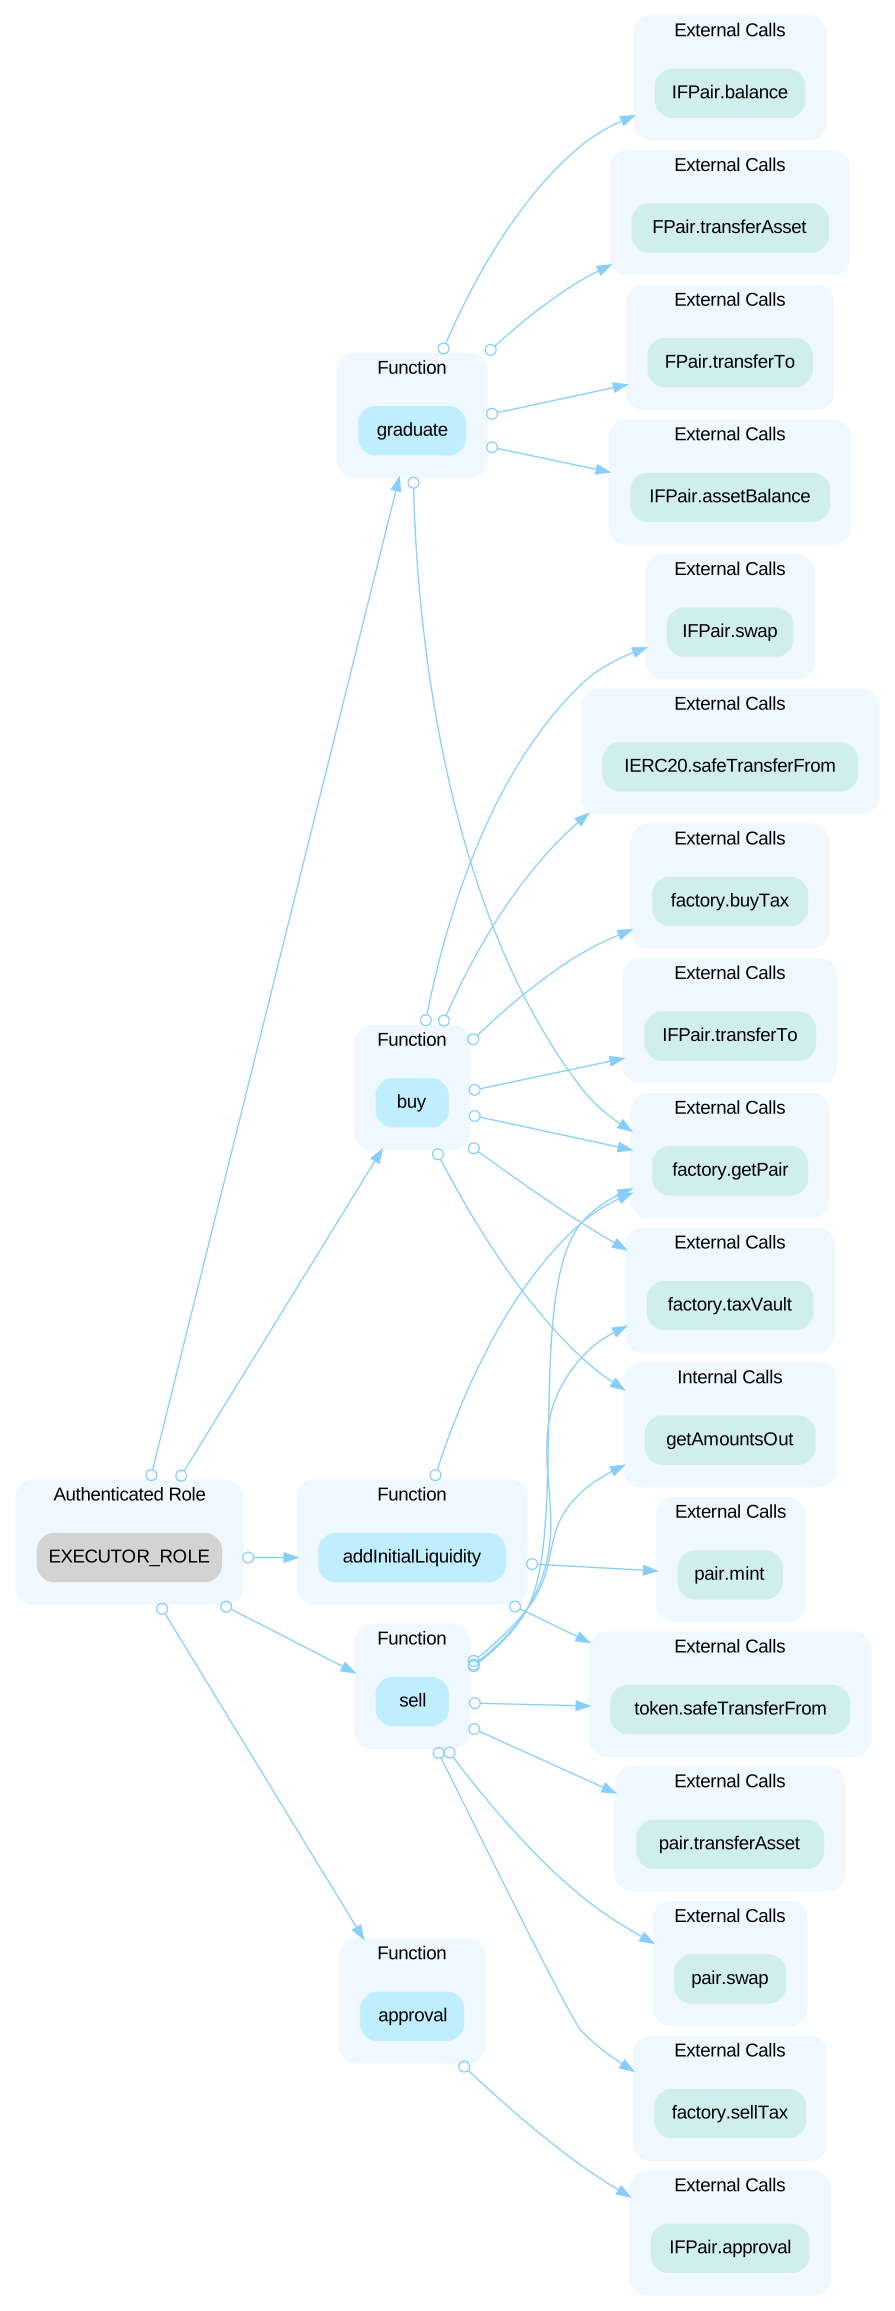 In the contract `FPair`, the role `router` has authority over the functions shown in the diagram below. Any compromise to the `router`
Open the reportHighCentralized Control of Contract UpgradeNetMind XYZ · CertiK · 13 Jan 2025Acknowledged
In the contract `Bonding`, `FFactory`, `FRouter`, `AgentFactory`, `AgentToken` and `StakeVault`, the role `admin` has the authority to update the implementation contract behind the contract. Any compromise to the `admin` account may allow a hacker to take advantage of this authority and change the implementation contract which is pointed by proxy and therefore execute potential malicious functionality in the implementation contract.
Open the reportHighInitial Token DistributionNetMind XYZ · CertiK · 13 Jan 2025Acknowledged
All of the `AgentToken` tokens are sent to the contract deployer. This is a centralization risk because the deployer can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
Open the reportHighModifiable Token Reception AddressNetMind XYZ · CertiK · 13 Jan 2025Acknowledged
The function `_swapTax` is designed to exchange a certain amount of the contract's tokens for USDC using the PancakeSwap/Uniswap protocol `uniswapRouter` function. This function specifies the `projectTaxRecipient` address as the recipient of the swapped tokens. The `projectTaxRecipient` address is a critical parameter within this function, as it determines the destination of the output tokens. It has been identified that the admin has the ability to alter the `projectTaxRecipient` address at any given time. This poses a security risk, as a compromised admin account could lead to unauthorized modification of the recipient address, resulting in the misdirection of funds to an attacker-controlled address. ```solidity=664 function _swapTax(uint256 tokenAmount, address pool) private { // ... (other code) uniswapRouter .swapExactTokensForTokensSupportingFeeOnTransferTokens( swapBalance_, 0, path, projectTaxRecipient, block.timestamp + 600 ) // ... (other code) } ```
Open the reportHighCentralization Related RisksNetMind-Audit · CertiK · 4 Mar 2024Acknowledged
In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. - transfer ownership of the contract to a new account - renounce ownership will leave the contract without an owner 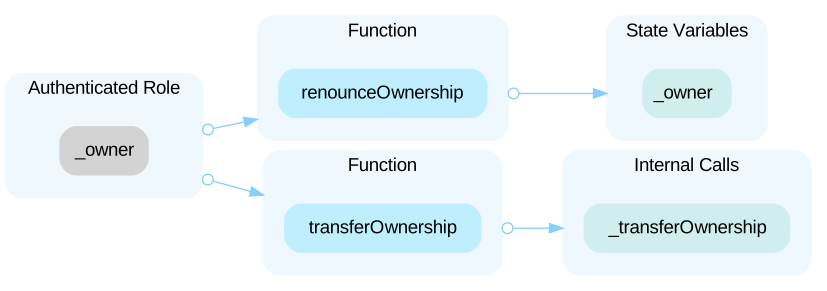 In the contract `AccountManage` the role `_auth` has authority over the functions shown in the diagram below. Any compromise to the `_auth` account may allow the hacker to take advantage of this authority. - freeze user's tokens for the job - deduct assets from user's account 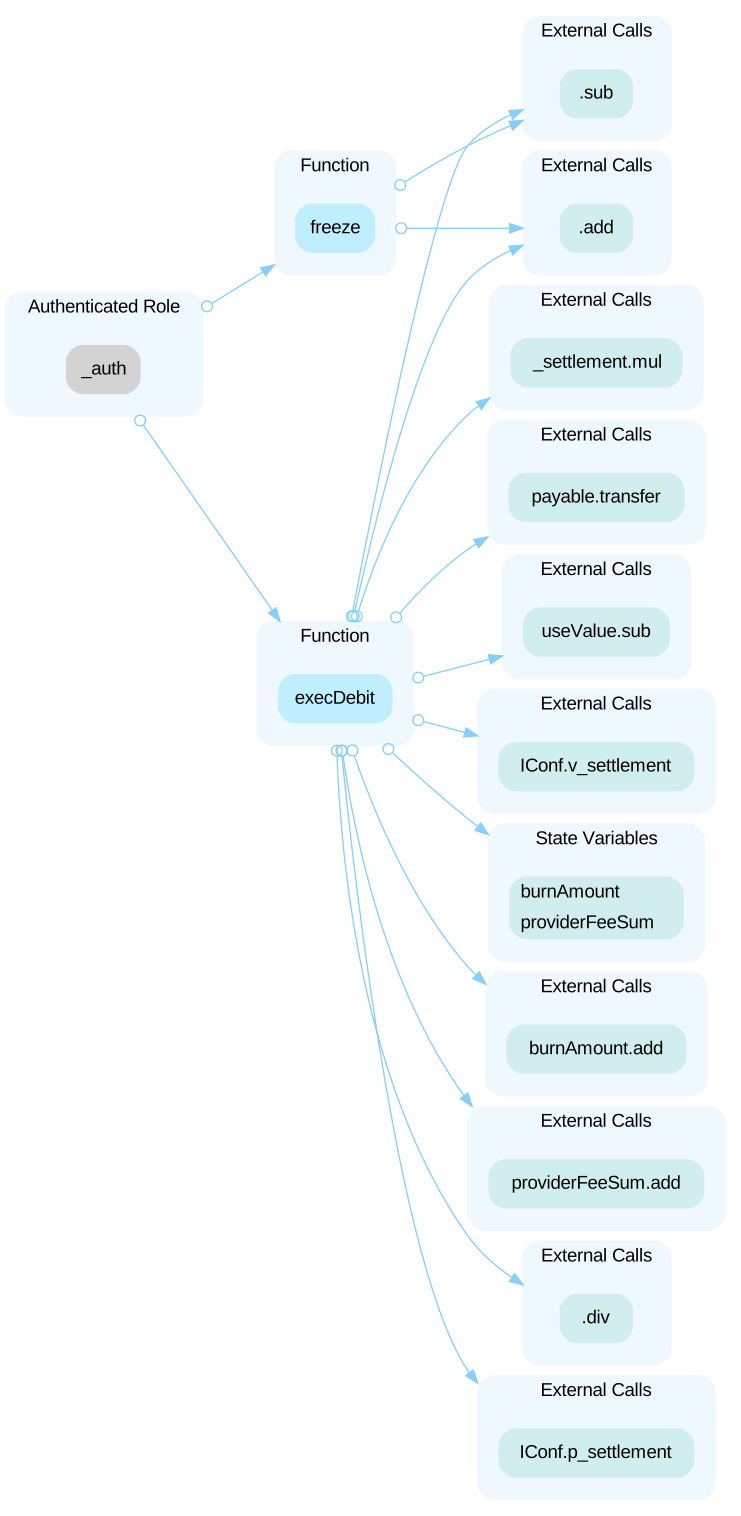 In the contract `AccountManage` the role `_executor` has authority over the functions shown in the diagram below. Any compromise to the `_executor` account may allow the hacker to take advantage of this authority. - init user’s information - update user‘s address 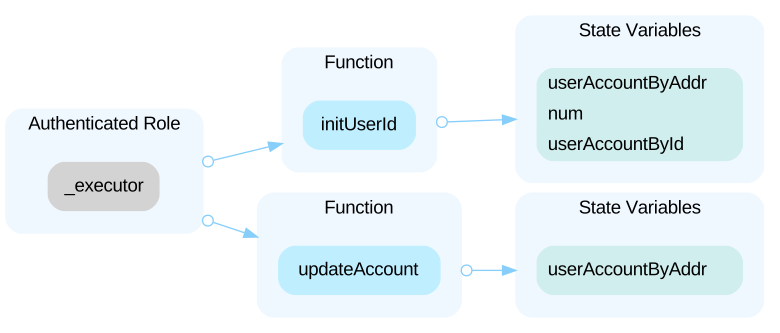 In the contract `AccountManage` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. - set `signNum`, `authSta` 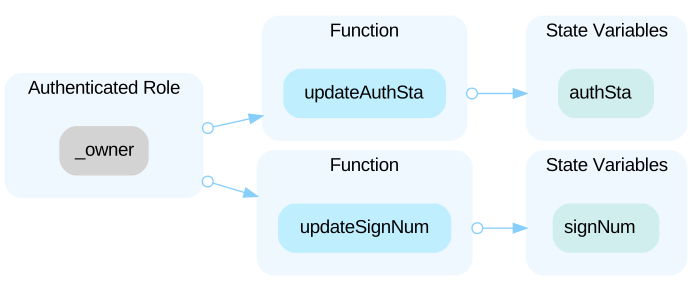 In the contract `CommunityFund` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. - set `LockTime`, `votingPeriod` - add node information - delete node information 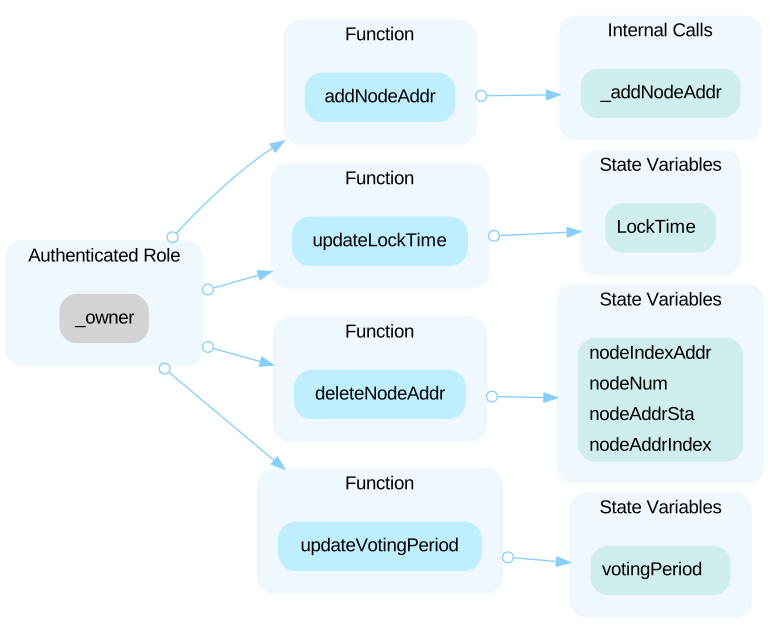 In the contract `Conf` the role `wards` has authority over the functions shown in the diagram below. Any compromise to the `wards` account may allow the hacker to take advantage of this authority. - grant/revoke `wards` role. - update state values of `Conf` contract. - update accountant addresses. In the contract `Crosschain` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. - set `trader`, `exector`, `threshold`, `signNum`, `pause`, `chargeRate`, `tokenSta` - withdraw the fee - add node information - delete node information 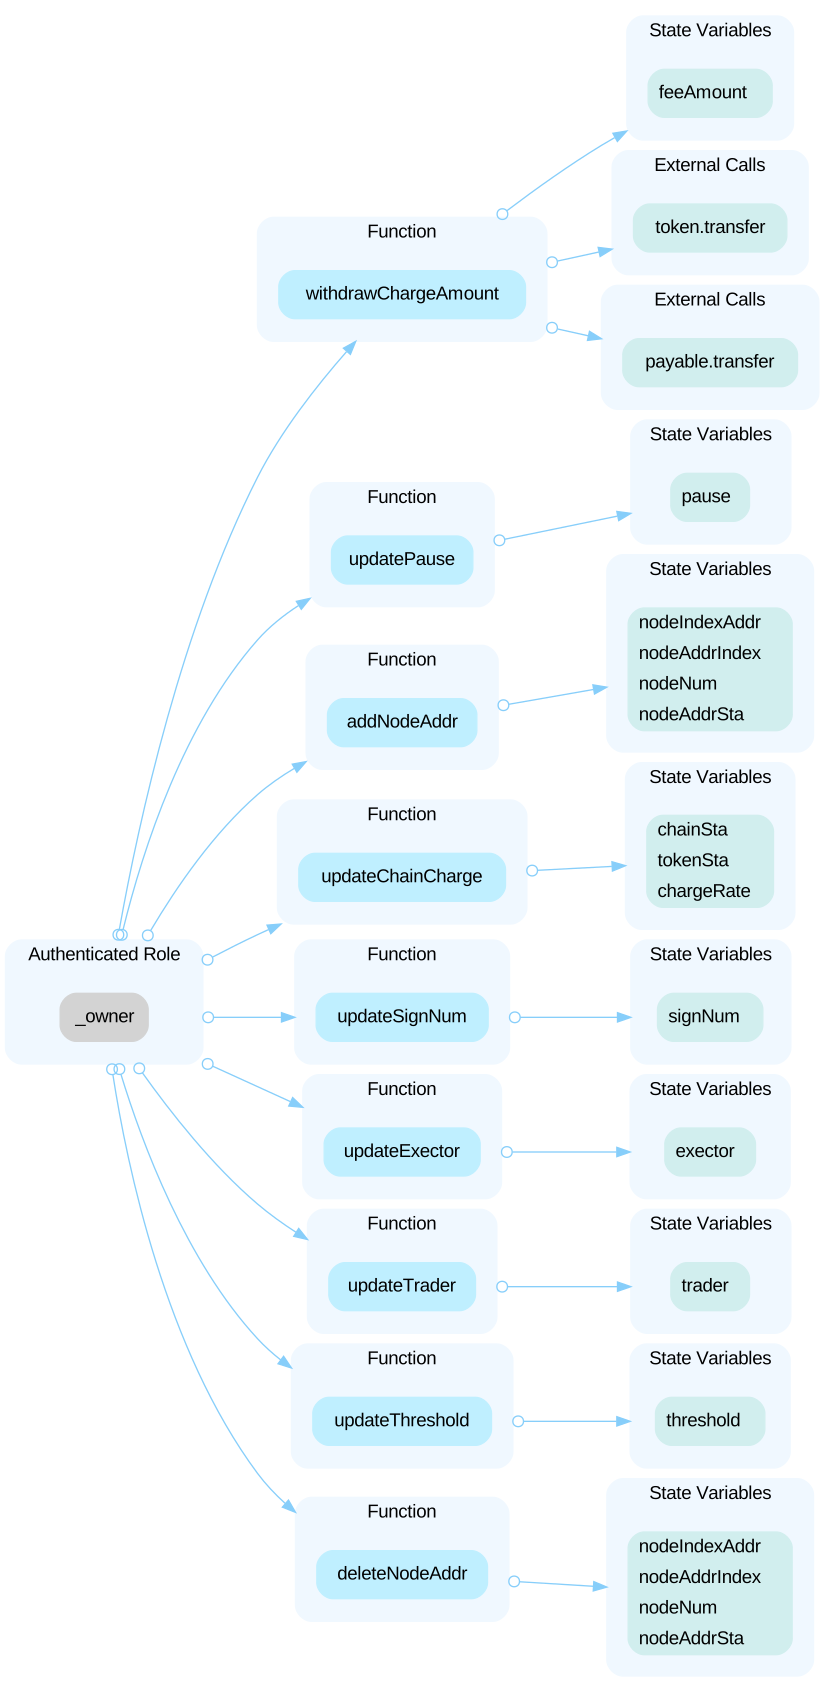 In the contract `Crosschain` the role `exector` has authority over the functions shown in the diagram below. Any compromise to the `exector` account may allow the hacker to take advantage of this authority. - pause the contract 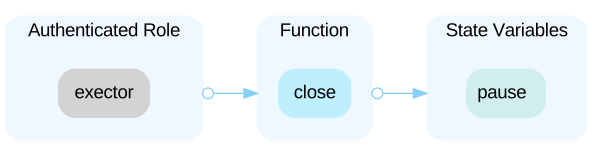 In the contract `Crosschain` the role `trader` has authority over the functions shown in the diagram below. Any compromise to the `trader` account may allow the hacker to take advantage of this authority. - transfer the token for the user 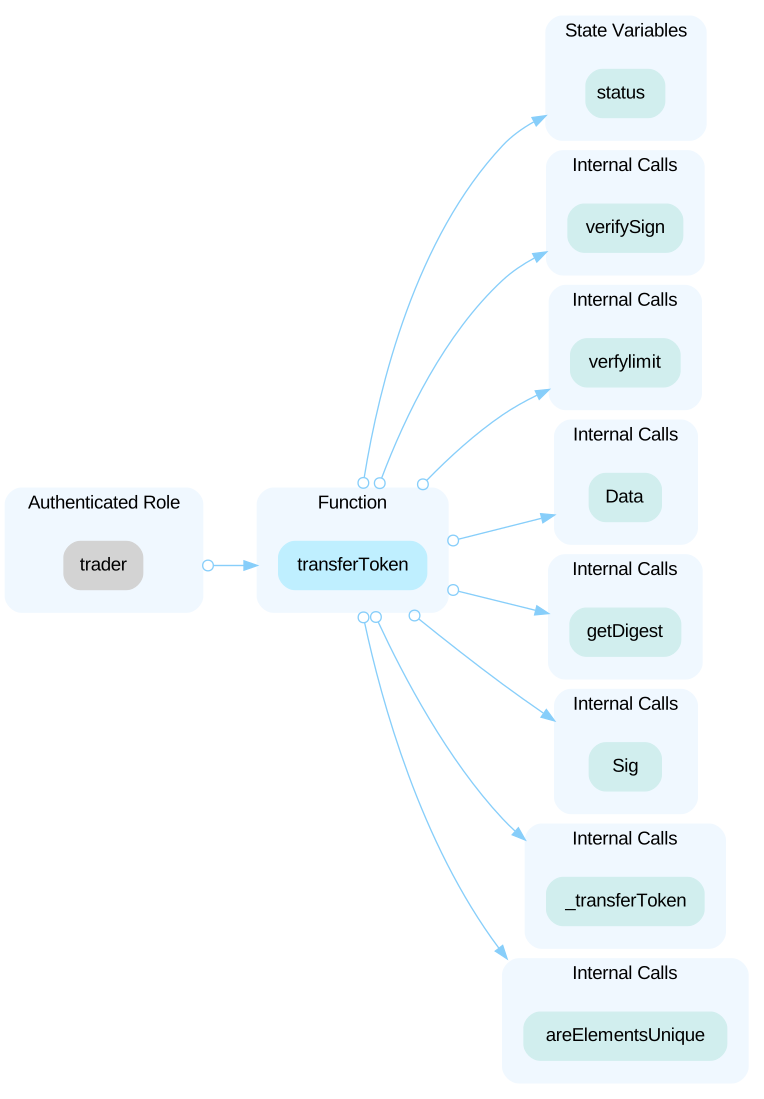 In the contract `Ledger` the role `accountant` has authority over the functions shown in the diagram below. Any compromise to the `accountant` account may allow the hacker to take advantage of this authority. - update ledger. In the contract `Pledge` the role `_nodeaddr` has authority over the functions shown in the diagram below. Any compromise to the `_nodeaddr` account may allow the hacker to take advantage of this authority. - stake NMT or ERC20 token assets. 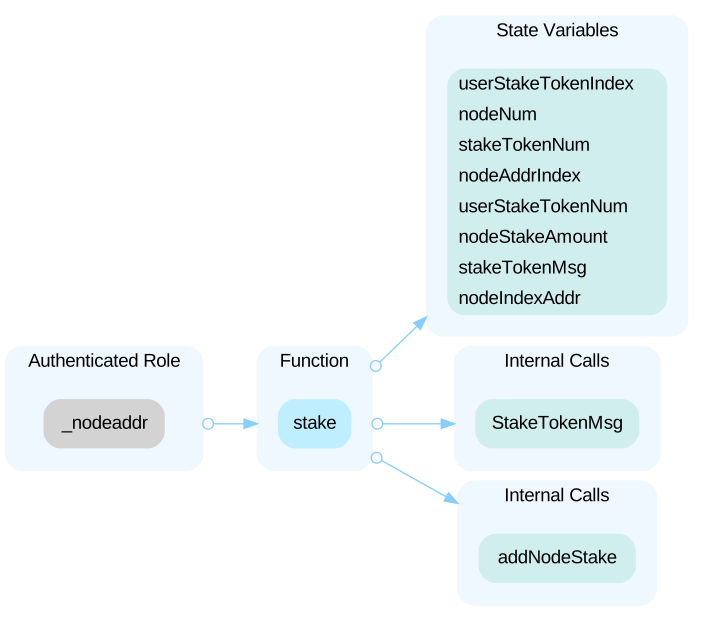 In the contract `Pledge` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. - set `guarder`, `tokenSta` - update node information - add node information - delete node information 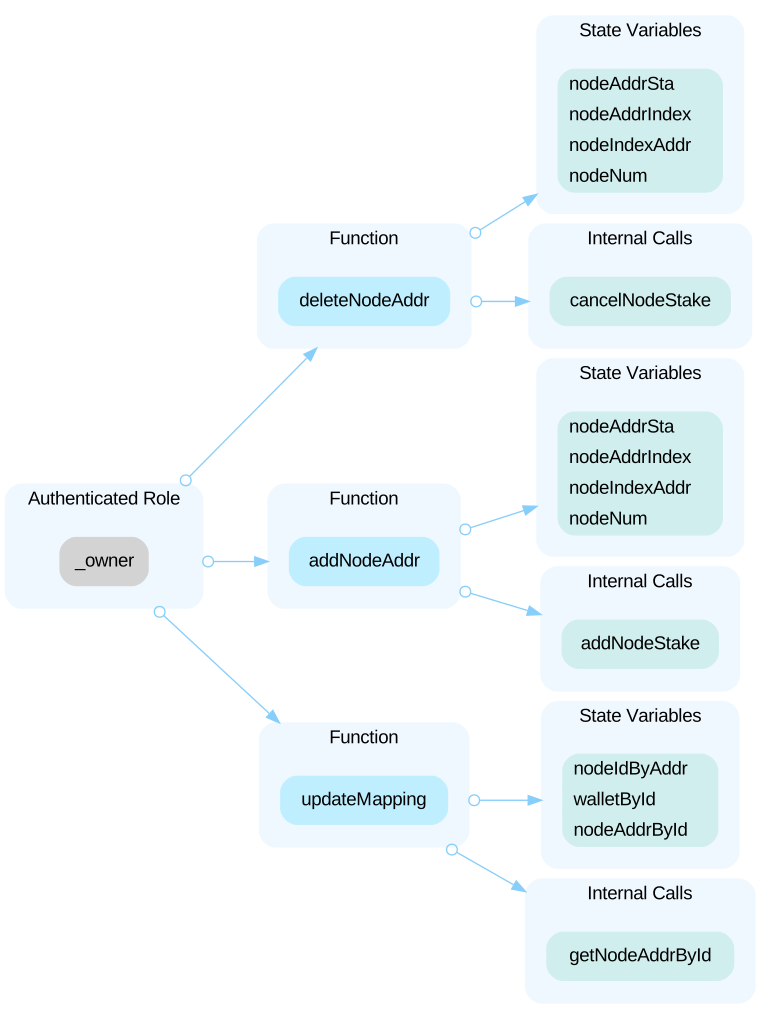 In the contract `Pledge` the role `guarder` has authority over the functions shown in the diagram below. Any compromise to the `guarder` account may allow the hacker to take advantage of this
Open the reportHighCentralized Control of Contract UpgradeNetMind-Audit · CertiK · 4 Mar 2024Acknowledged
All contracts in the project inherits upgradeable contracts, indicating that it is part of an upgradeable system. Upgradeable contracts often pair with a proxy contract that is responsible for managing contract upgrades. The `privileged roles` of the proxy often have the authority to update the implementation contract. Any compromise of the privileged account could allow a hacker to exploit this authority, potentially altering the implementation contract pointed to by the proxy and thus executing malicious functionality within the implementation contract.
Open the reportMediumImproper Ownership Handling in `stakeVault` LeadiNetMind XYZ · CertiK · 13 Jan 2025Acknowledged
The `_addInitialLiquidity()` function transfers LP tokens to a newly created `stakeVault` contract. Since the `stakeVault` contract's `initialize()` function is called by the `Bonding` contract, the owner of the `stakeVault` contract is set to the `Bonding` contract. As a result, only the `Bonding` contract can call owner-restricted functions in the `stakeVault`. However, the `Bonding` contract does not invoke these functions, leading to the LP tokens being locked in the `stakeVault`. **contracts/fun/Bonding.sol** ```solidity=305 function _addInitialLiquidity(IAgentToken token_, IERC20 _assetToken) internal returns(address){ ... (, , uint256 lpTokens) = uniswapRouter .addLiquidity( address(token_), address(_assetToken), token_.balanceOf(address(this)), _assetToken.balanceOf(address(this)), 0, 0, address(this), block.timestamp ); IStakeVault stakeVault = IStakeVault(Clones.clone(stakeVaultImpl)); tokenStake[address(token_)] = address(stakeVault); IERC20(uniswapV2Pair_).approve(address(stakeVault), lpTokens); stakeVault.initialize(uniswapV2Pair_, lpTokens); return uniswapV2Pair_; } ``` **contracts/StakeVault.sol** ```solidity=21 function initialize(address assetToken_, uint256 amount) external initializer { __Ownable_init(_msgSender()); assetToken = IERC20(assetToken_); assetToken.transferFrom(_msgSender(), address(this), amount); lockAmount = amount; lockTime = block.timestamp; lockPeriod = 10 * 365 * 1 days; } ```
Open the reportMediumIncompatibility with Deflationary TokensNetMind XYZ · CertiK · 13 Jan 2025Acknowledged
When transferring deflationary ERC20 tokens, the input amount may not be equal to the received amount due to the charged transaction fee. For example, if a user sends 100 deflationary tokens (with a 10% transaction fee),, only 90 tokens actually arrived to the contract. However, a failure to discount such fees may allow the same user to withdraw 100 tokens from the contract, which causes the contract to lose 10 tokens in such a transaction. Reference: https://thoreum-finance.medium.com/what-exploit-happened-today-for-gocerberus-and-garuda-also-for-lokum-ybear-piggy-caramelswap-3943ee23a39f
Open the reportMediumLack of Storage Gap in Upgradeable ContractNetMind-Audit · CertiK · 4 Mar 2024Acknowledged
There is no storage gap preserved in the logic contract. The storage gap is essentially reserved space within a contract's storage layout. It's a placeholder for future variables that might be added in upgraded versions of the contract. The storage gap ensures that new variables added during upgrade do not overwrite existing storage variables, preserving the integrity of the contract's state. Any logic contract that acts as a base contract and which is inherited by other upgradeable contracts should have a reasonably sized storage gap preserved. In the audit scope, all contracts are upgradeable and derive from either the `Initializable`, `Ownable`, or `ERC20` super contract.
Open the reportMediumPotential Locked TokenNetMind-Audit · CertiK · 4 Mar 2024Acknowledged
The `refund()` function is designed to be called to return contract assets to users. when the function is invoked with an `amt` parameter less than the `paymentId`'s token amount, the remaining tokens are irretrievably locked in the contract because the function is callable only once with a specific `paymentId`. ```solidity=166 require(R.amount >= amt, "invalid amt"); ```
Open the reportShow 5 more
LowBlock Timestamp Used As Deadline Parameter In UniNetMind XYZ · CertiK · 13 Jan 2025Acknowledged
In the Uniswap AMM system, a deadline is typically set for token swaps to prevent transactions from being executed after a certain amount of time, which could result in unfavorable price slippage. However, in the current contract, when conducting transactions using the Uniswap function, the deadline is set to `block.timestamp` or more than `block.timstamp`, meaning "the deadline check will pass whatever block the transaction is in" due to the check of deadline `require(deadline >= block.timestamp, 'UniswapV2Router: EXPIRED')` which will always pass. If bots and maximal extractable value (MEV) strategies are widely used, it could affect many transactions. A malicious miner can hold the transaction as he wants to incur the maximum loss is reached. Therefore, the absence or incorrect usage of a deadline could make transactions more susceptible to front-running / MEV attacks, leading to greater price slippage losses.
Open the reportLowNot Recommended MetadataURI ProtocolNetMind XYZ · CertiK · 13 Jan 2025Acknowledged
HTTP/HTTPS should not be used for token metadata because the server owner can change token metadata at will, which can dramatically affect the token value. ```solidity=17 function _baseURI() internal pure override returns (string memory) { return "http://xyz.netmind.ai/agentNFT/"; } ```
Open the reportLowPotential Sandwich AttacksNetMind XYZ · CertiK · 13 Jan 2025Acknowledged
A sandwich attack can occur when an attacker notices a transaction involving token swaps or liquidity additions that lacks slippage restrictions or minimum output amount settings. The attacker can exploit this by frontrunning the transaction to purchase one of the assets, thereby manipulating the exchange rate, and then backrunning the transaction to sell the asset for a profit. The referenced functions are invoked without setting slippage restrictions or minimum output amounts, making transactions that trigger these functions particularly vulnerable to sandwich attacks, especially when large input amounts are involved.
Open the reportLowThird-Party Dependency UsageNetMind XYZ · CertiK · 13 Jan 2025Acknowledged
The contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=53 IUniswapV2Router public uniswapRouter; ``` - The contract `AgentToken` interacts with third party contract with `IUniswapV2Router` interface via `uniswapRouter`. ```solidity=11 IERC20 public assetToken; ``` - The contract `StakeVault` interacts with third party contract with `IERC20` interface via `assetToken`. ```solidity=24 address public assetToken; ``` - The contract `FRouter` interacts with third party contract with `IERC20` interface via `assetToken`. ```solidity=37 IUniswapV2Router public uniswapRouter; ``` - The contract `Bonding` interacts with third party contract with `IUniswapV2Router` interface via `uniswapRouter`. ```solidity=4 interface IProxyAdmin { function changeProxyAdmin(address proxy, address newAdmin) external; function upgrade(address proxy, address implementation) external; function transferOwnership(address newOwner) external; } ``` - The contract `Management` interacts with third party contract with `IProxyAdmin` interface via `proxyAdmin`.
Open the reportLowUnchecked ERC-20 `transfer()`/`transferFrom()` CaNetMind XYZ · CertiK · 13 Jan 2025Acknowledged
The return values of the `transfer()` and `transferFrom()` calls in the smart contract are not checked. Some ERC-20 tokens' transfer functions return no values, while others return a bool value, they should be handled with care. If a function returns `false` instead of reverting upon failure, an unchecked failed transfer could be mistakenly considered successful in the contract. ```solidity=36 assetToken.transfer(to, assetToken.balanceOf(address(this))); ``` ```solidity=24 assetToken.transferFrom(_msgSender(), address(this), amount); ``` ```solidity=40 assetToken.transfer(address(0), assetToken.balanceOf(address(this))); ``` ```solidity=256 token.transfer(msg.sender, token.balanceOf(address(this))); ```
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="netmind-xyz"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us