
Nimbus Platform security record
As of 3 Nov 2026, Nimbus Platform has 1 audit report on Trustblock, by CertiK, dated 30 Sep 2022. That report lists no open critical findings.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Audits1
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| NimbusPlatform ET - NFT | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
Findings22
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 4 | 2 |
| Medium | 0 | 0 | 3 |
| Low | 0 | 0 | 13 |
HighCentralization Risks in HubRouting.solNimbusPlatform ET - NFT · CertiK · 30 Sep 2022Acknowledged
In the contract `HubRouting` the role `StakingMain` has authority over the functions **stake**, **registerSet**, **withdrawReward** and **burn** shown in the diagram below. Any compromise to the `StakingMain` account may allow the hacker to take advantage of this authority and stake the tokens to his/her desired addresses, register the set when the tokens are purchased, withdraw the reward to his/her desired account, and also burn/destroy the tokens. 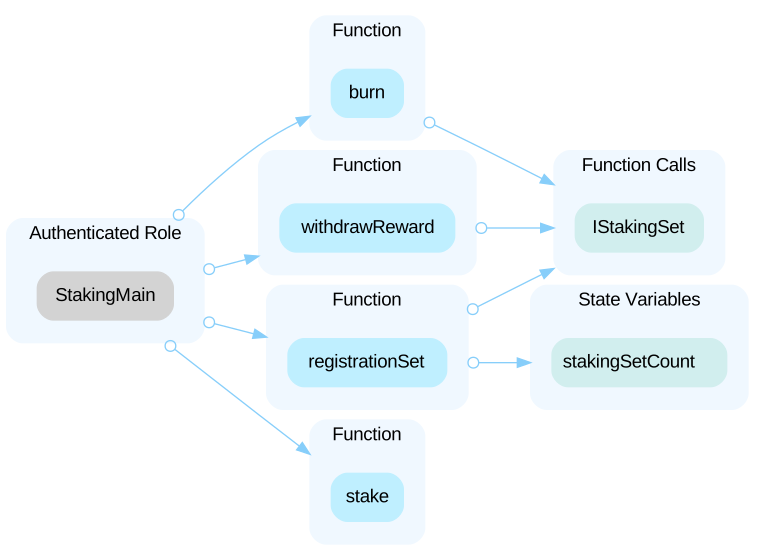 In the contract `HubRouting` the role `_owner` has authority over the functions **activateSet** and **deactivateSet** shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and activate and deactivate set when the tokens are purchased. 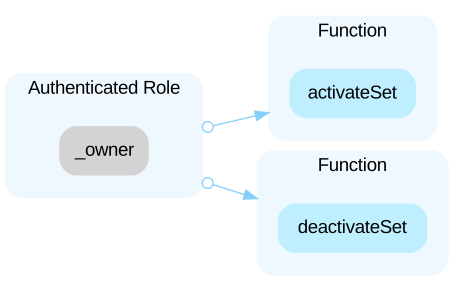 In the contract `HubRouting` the role `owner` has authority over the functions **deactivateSet** and **activateSet** shown in the diagram below. Any compromise to the `owner` account may allow the hacker to take advantage of this authority and deactivate and activate set when the tokens are purchased. 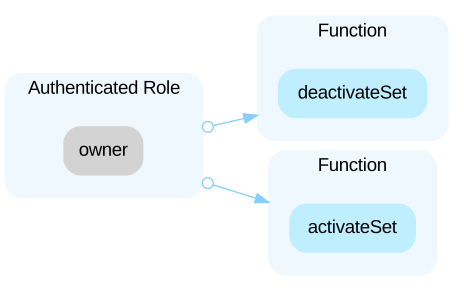
Open the reportHighCentralization Risks in StakingMain.solNimbusPlatform ET - NFT · CertiK · 30 Sep 2022Acknowledged
In the contract `StakingMain` the role `_owner` has authority over the functions **setHubRouting**, **addSet**, and **rescue** shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set the hub for routing, add the stakers in the set, and rescue the tokens to the desired address. 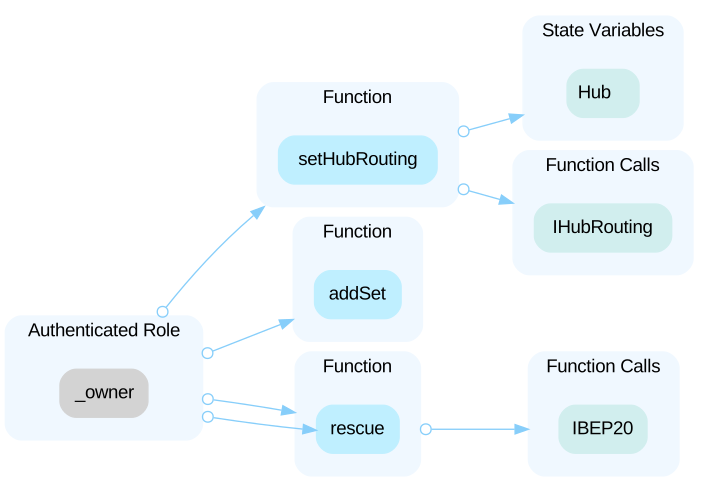 In the contract `StakingMain` the role `owner` has authority over the functions **setHubRouting**, **rescue**, **approve**, and **addSet** shown in the diagram below. Any compromise to the `owner` account may allow the hacker to take advantage of this authority and set the hub for routing, rescue the tokens to the desired address, add the stakers in the set, and approve the transfer of tokens to the desired address. 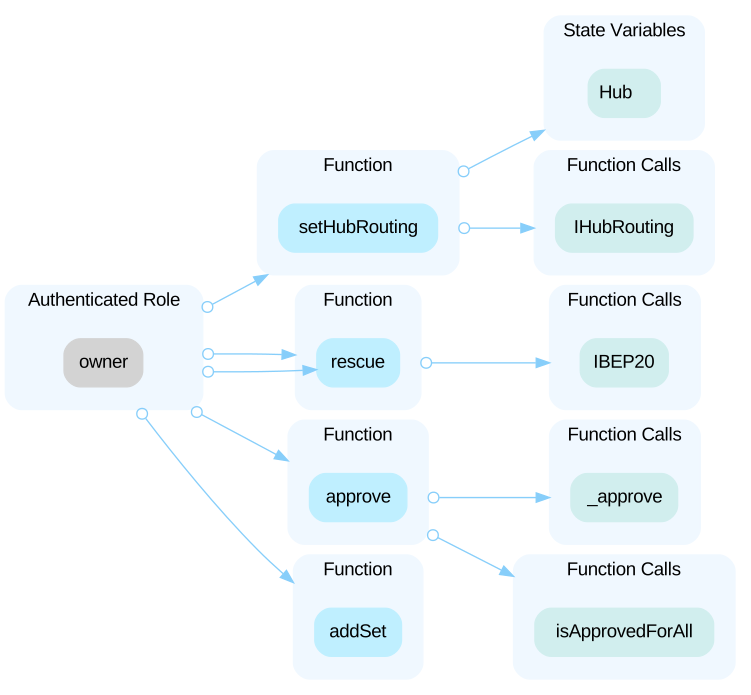
Open the reportHighCentralization Risks in StakingSet.solNimbusPlatform ET - NFT · CertiK · 30 Sep 2022Acknowledged
In the contract `StakingSet` the role `_owner` has authority over the functions **rescue**, **updateNimbusRouter**, **updateTokenAllowance**, **updateNbuStaking**, **initialize**, **updateGnbuStaking**, **updateCakeStaking**, **updateMinPurchaseAmount**, **setCakePID**, and **setLockTime** shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and rescue the tokens to the desired address, update Nimbus Router once new address is received, update Nimbus Staking once new address for `newLpStaking` is received, initialize the addresses to the desired value, update Gnbu Staking once new address for `newLpStaking` is received, update Cake Staking once new address for `newCakeCasting` is received, increase or decrease the minimum purchase amount, set cake PID and set lock time. 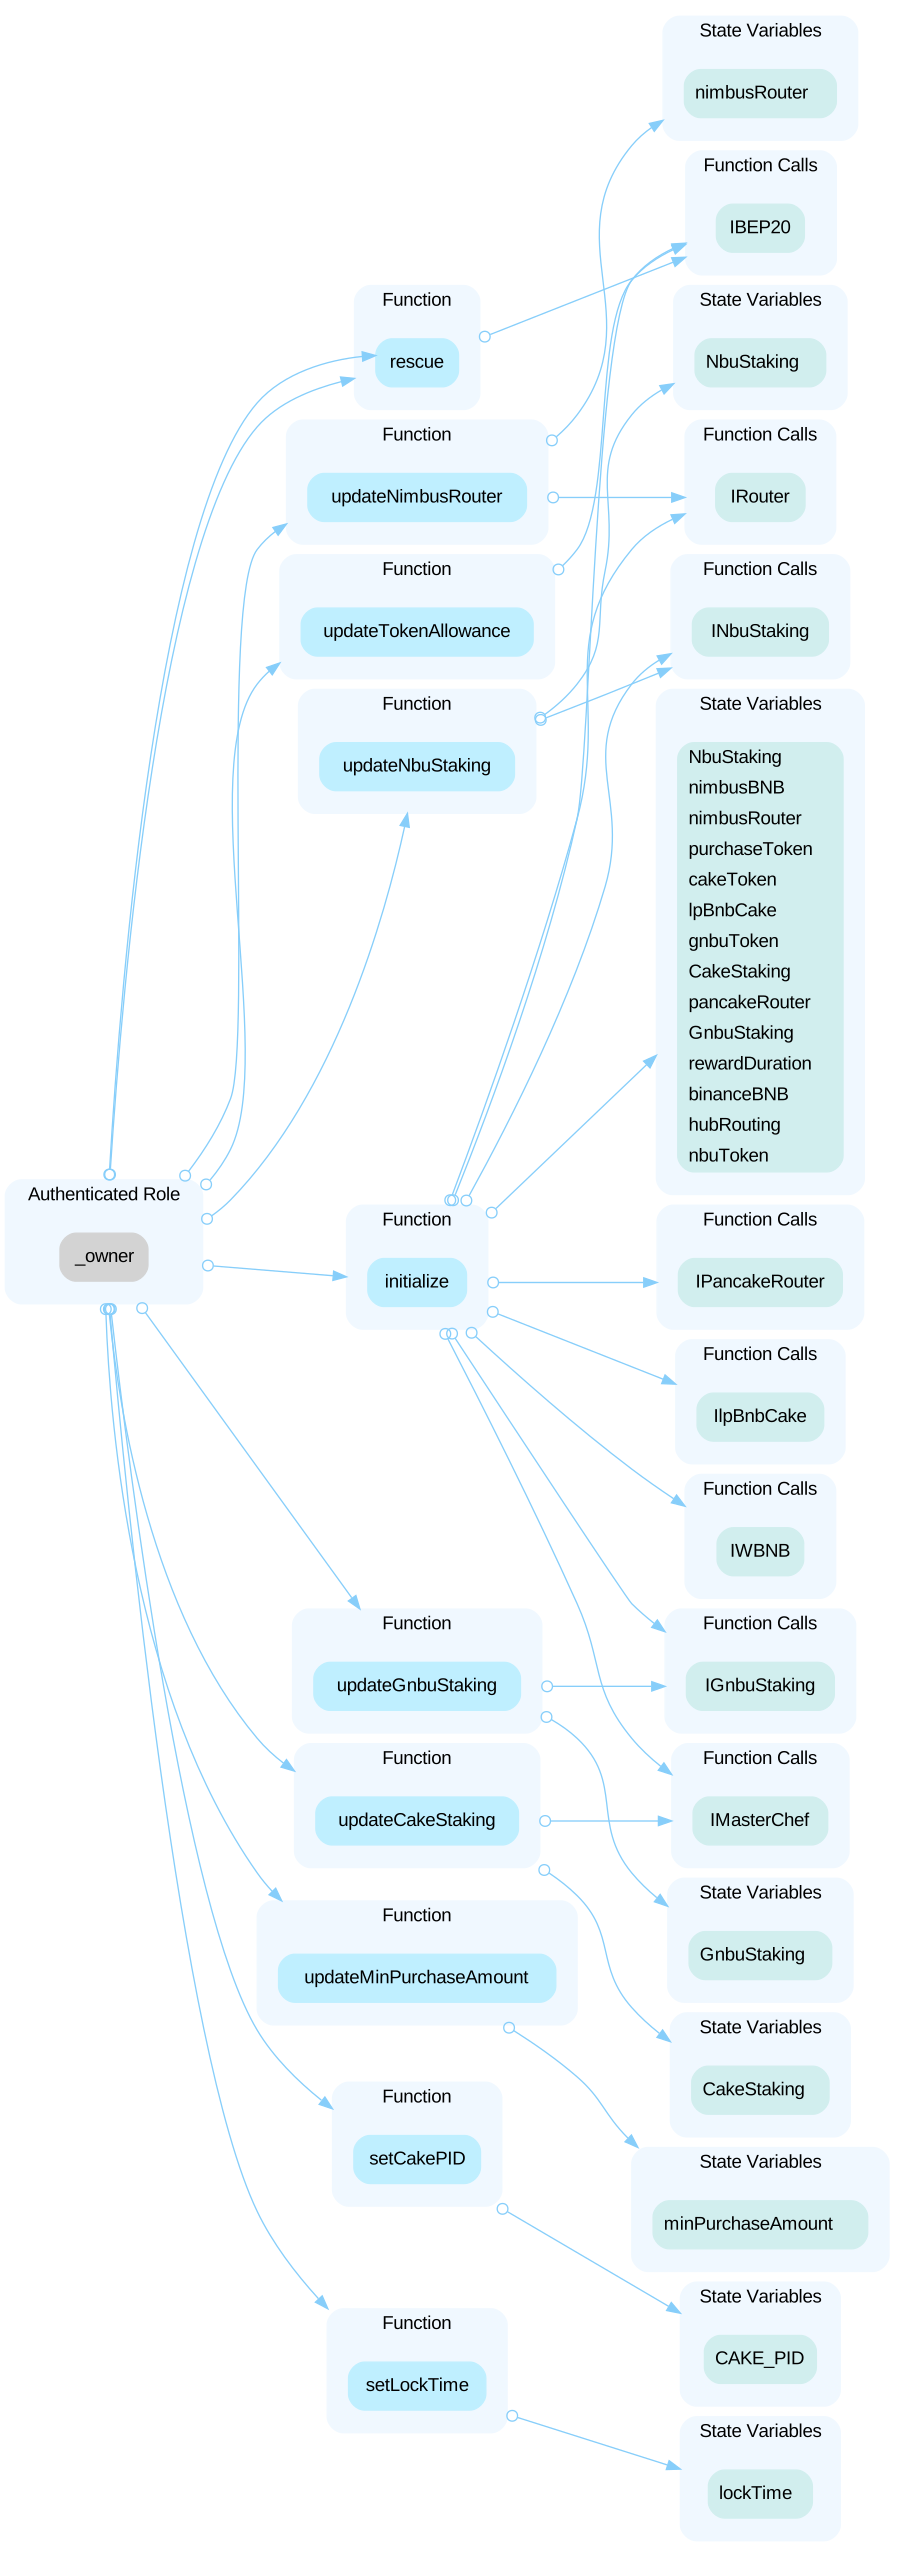 In the contract `StakingSet` the role `hubRouting` has authority over the functions **withdrawUserRewards**, **burnStakingSet**, and **buyStakingSet** shown in the diagram below. Any compromise to the `hubRouting` account may allow the hacker to take advantage of this authority and withdraw the rewards from user to his/her desired account, and buy as well as destroy the staking set. 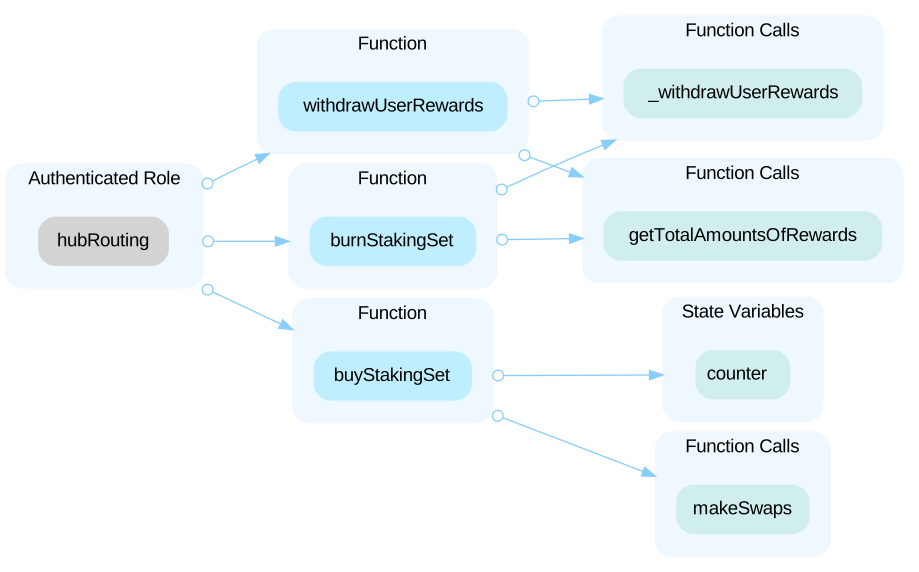 In the contract `StakingSet` the role `owner` has authority over the functions **rescue**, **updateNimbusRouter**, **updateTokenAllowance**, **updateNbuStaking**, **initialize**, **updateGnbuStaking**, **updateCakeStaking**, **updateMinPurchaseAmount**, **setCakePID**, and **setLockTime** shown in the diagram below. Any compromise to the `owner` account may allow the hacker to take advantage of this authority and rescue the tokens to the desired address, update Nimbus Router once new address is received, update Nimbus Staking once new address for `newLpStaking` is received, initialize the addresses to the desired value, update Gnbu Staking once new address for `newLpStaking` is received, update Cake Staking once new address for `newCakeCasting` is received, increase or decrease the minimum purchase amount, set cake PID and set lock time. 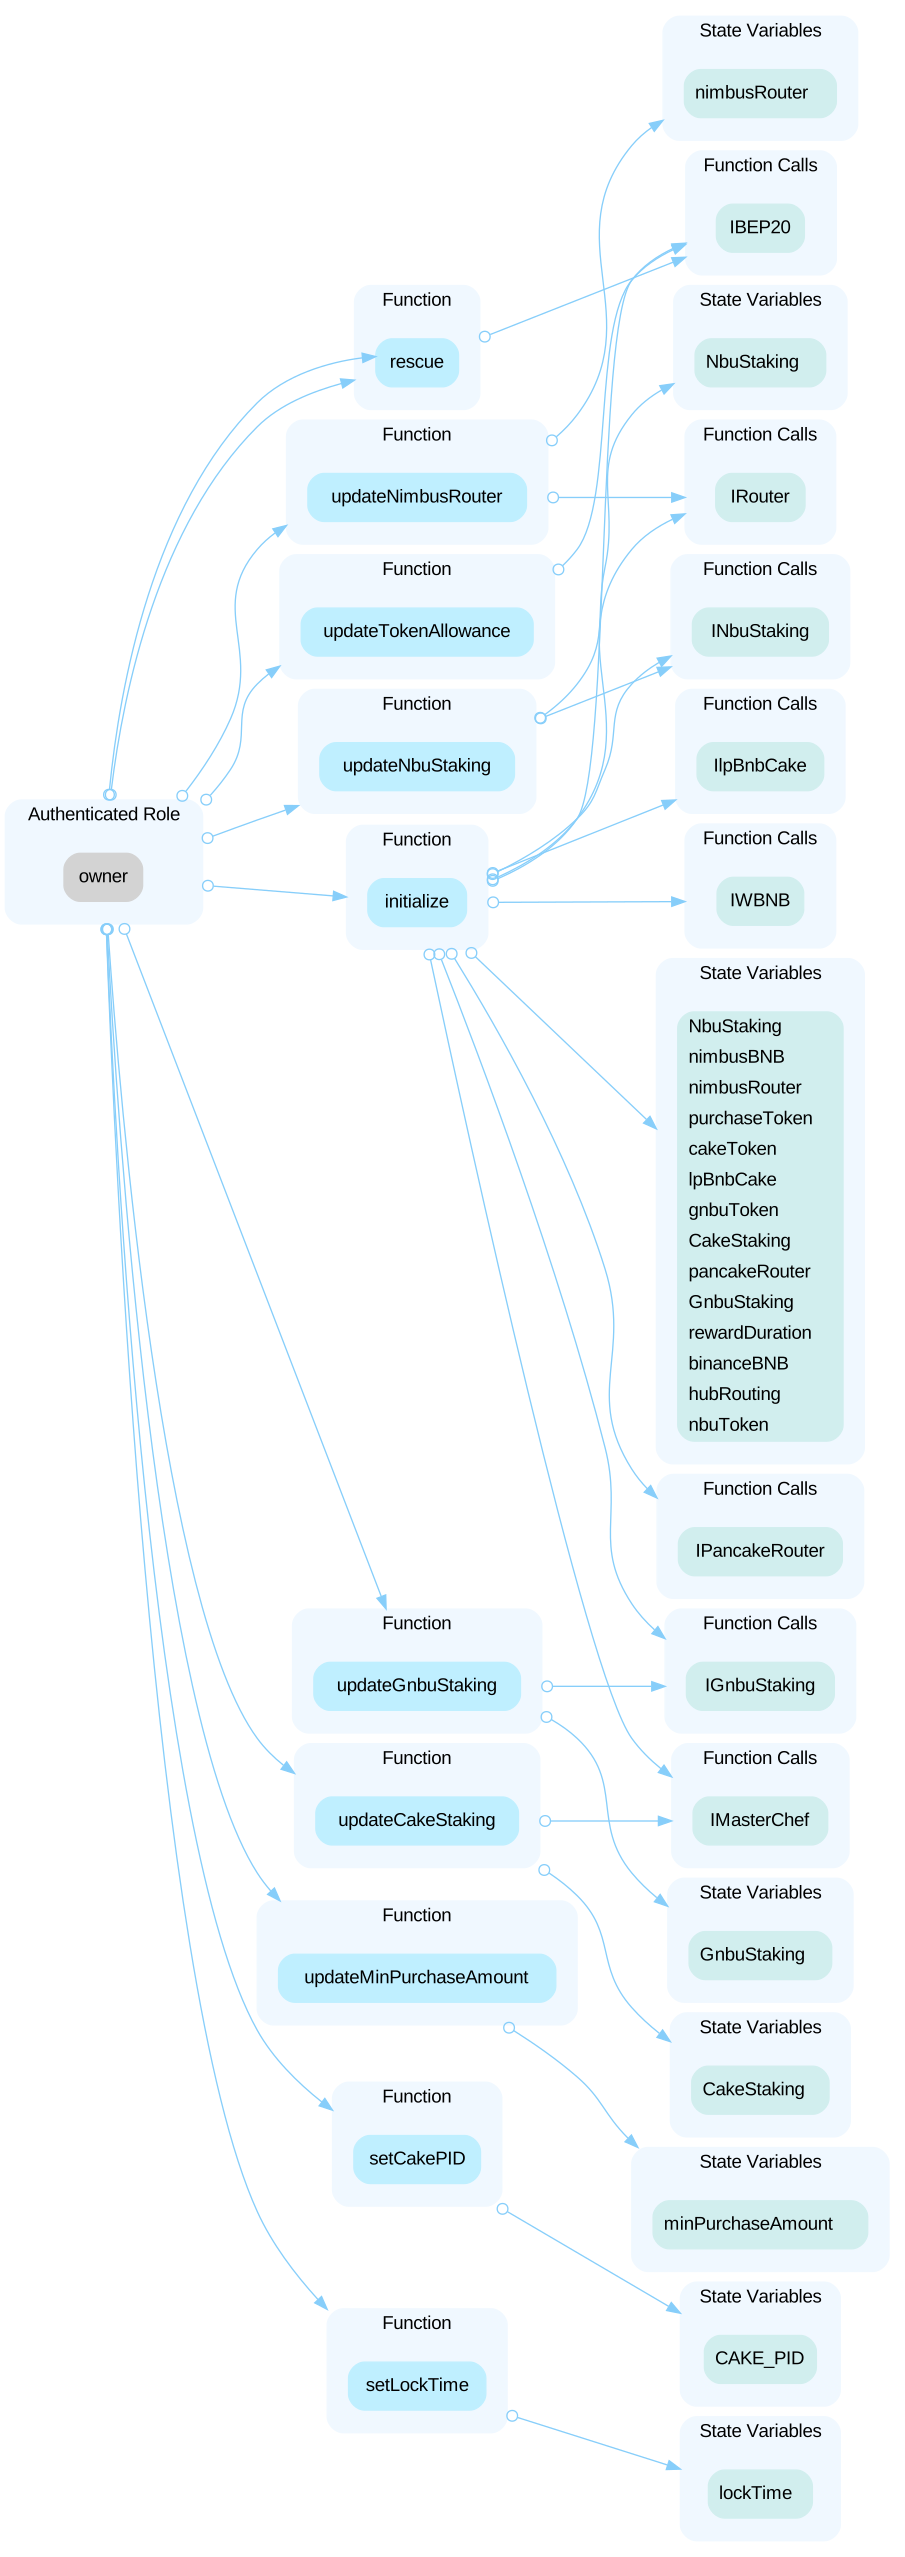
Open the reportHighCentralization Risks in StakingSetBusd.solNimbusPlatform ET - NFT · CertiK · 30 Sep 2022Acknowledged
In the contract `StakingSetBusd` the role `_owner` has authority over the functions **updateCakeStaking**, **updateNbuStaking**, **initialize**, **updateGnbuStaking**, **updateNimbusRouter**, **rescue**, **updateTokenAllowance**, **setCakePID**, **setLockTime**, **updateMinPurchaseAmount** shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update Cake Staking once new address for `newCakeCasting` is received, update Nimbus Staking once new address for `newLpStaking` is received, initialize the addresses to the desired value, update Gnbu Staking once new address for `newLpStaking` is received, update Nimbus Router once new address is received, rescue the tokens to the desired address, update token allowances, increase or decrease the minimum purchase amount, set cake PID and set lock time. 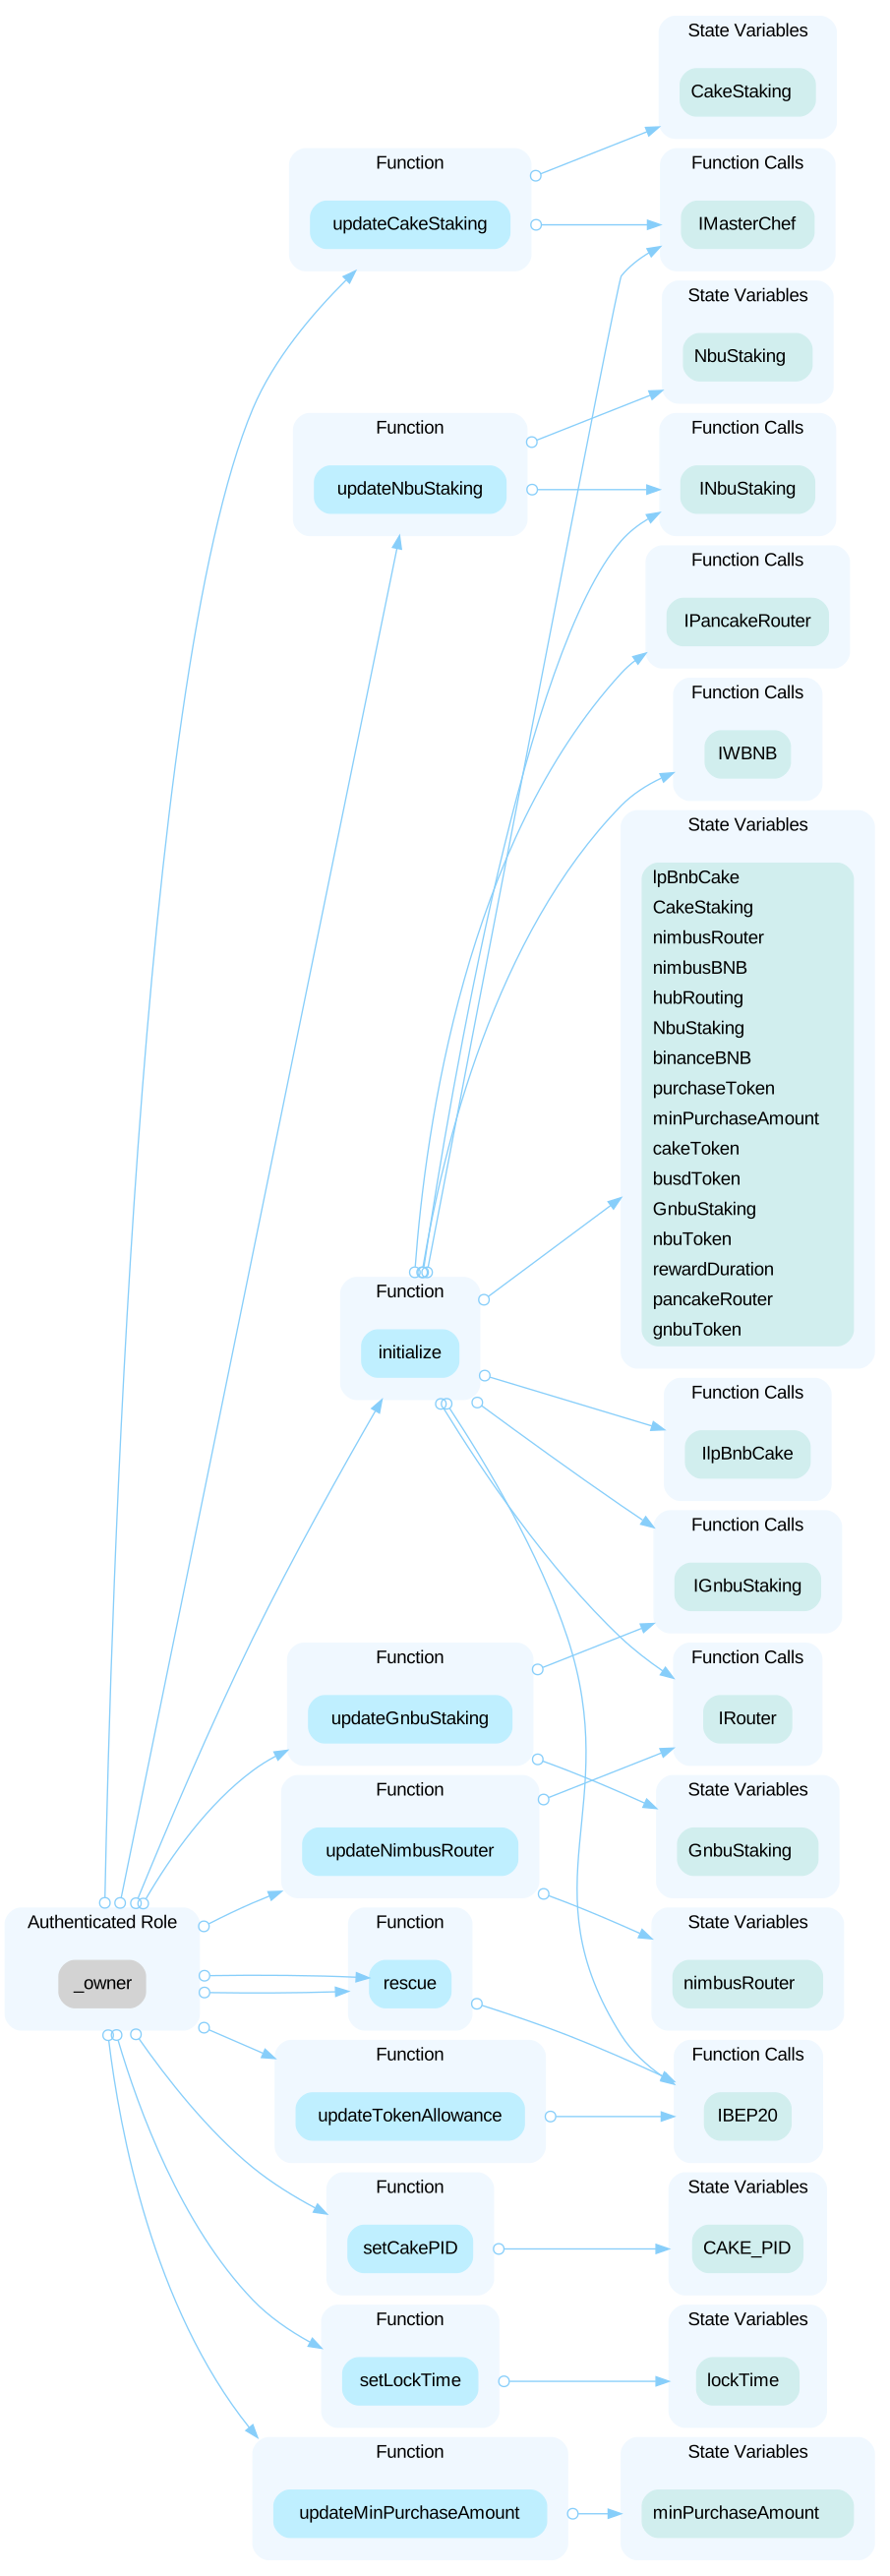 In the contract `StakingSetBusd` the role `hubRouting` has authority over the functions **withdrawUserRewards**, **burnStakingSet**, and **buyStakingSet** shown in the diagram below. Any compromise to the `hubRouting` account may allow the hacker to take advantage of this authority and withdraw the rewards from user to his/her desired account, and buy as well as destroy the staking set. 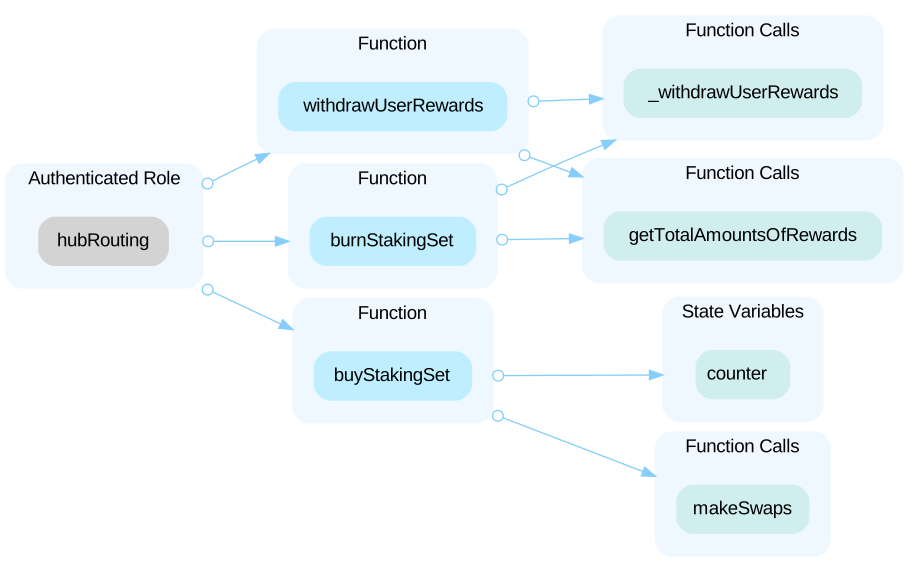 In the contract `StakingSetBusd` the role `owner` has authority over the functions **updateNbuStaking**, **updateCakeStaking**, **initialize**, **updateNimbusRouter**, **updateGnbuStaking**, **updateMinPurchaseAmount**, **setCakePID**, **setLockTime**, **updateTokenAllowance**, and **rescue** shown in the diagram below. Any compromise to the `owner` account may allow the hacker to take advantage of this authority and update Nimbus Staking once new address for `newLpStaking` is received, update Cake Staking once new address for `newCakeCasting` is received, initialize the addresses to the desired value, update Nimbus Router once new address is received, update Gnbu Staking once new address for `newLpStaking` is received, increase or decrease the minimum purchase amount, set cake PID, set lock time, update token allowances, and rescue the tokens to the desired address. 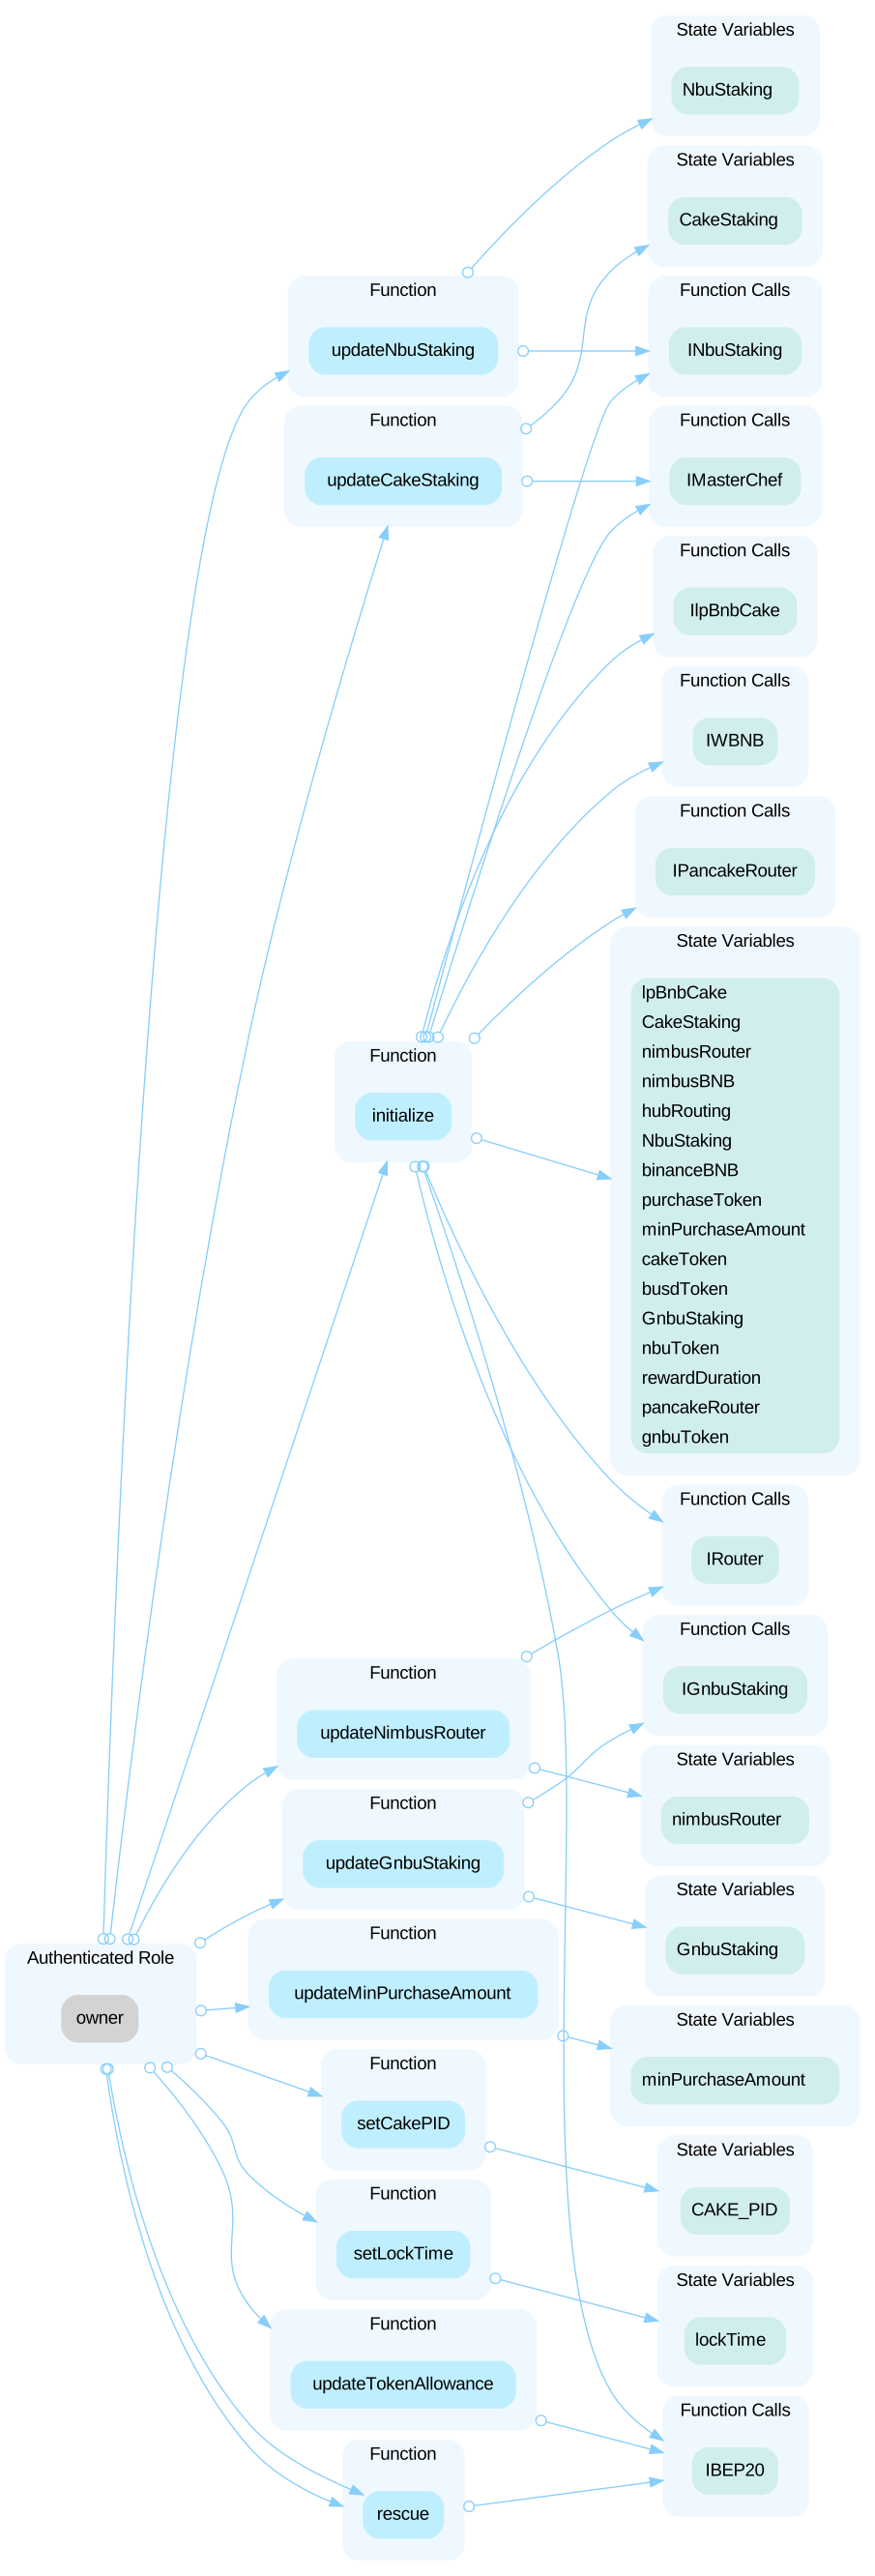
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="nimbus"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us