
ONFA security record
As of 3 Nov 2026, ONFA has 1 audit report on Trustblock, by CertiK, dated 30 Dec 2024. That report lists no open critical findings.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Audits1
Newest first
1 other security report listed, not counted
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| ONFA - Audit | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
| ONFA - Pentesting | Security firm: CertiK | Date: | Scope: Not recorded (see the report) | No open critical findings | Open · skynet.certik.com |
Findings14
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 1 |
| Medium | 3 | 0 | 0 |
| Low | 4 | 1 | 4 |
HighCentralization Related RisksONFA - Audit · CertiK · 30 Dec 2024Fixed
In the contract `ONFA_NFT` the role `DEFAULT_ADMIN_ROLE` has authority over the following functions: - grantRole - revokeRole Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and grant/revoke minter and pauser roles. In the contract `ONFA_NFT` the role `MINTER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this authority and mint NFTs. 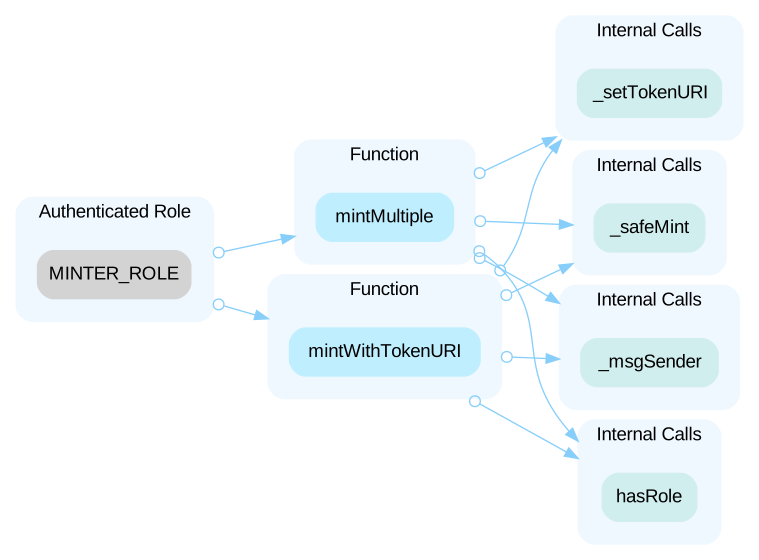 In the contract `ONFA_NFT` the role `PAUSER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `PAUSER_ROLE` account may allow the hacker to take advantage of this authority and pause/unpause the contract. 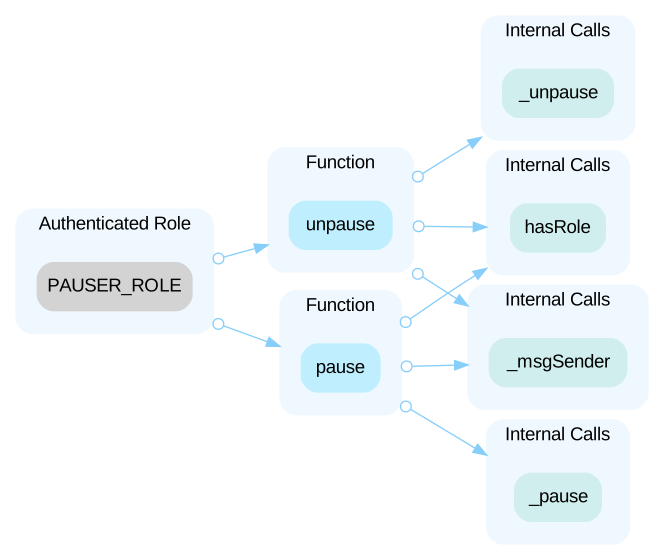 ----- In the contract `TetherUSD` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and mint tokens, transfer/renounce ownership. 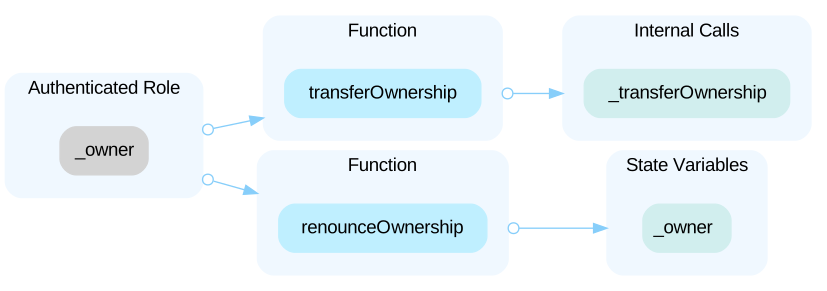 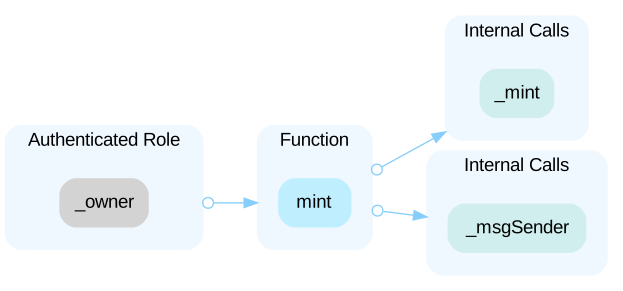 ----- In the contract `VNDT` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer/renounce the ownership and mint tokens. 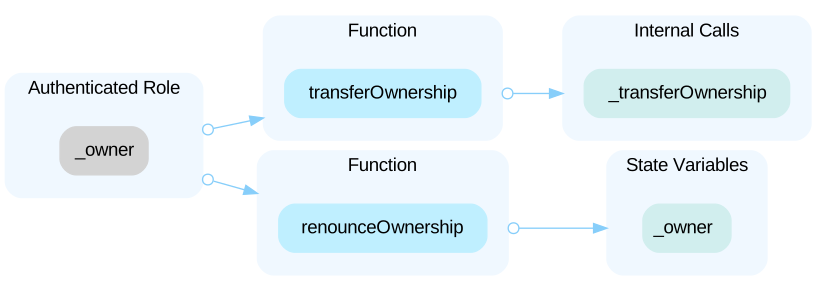 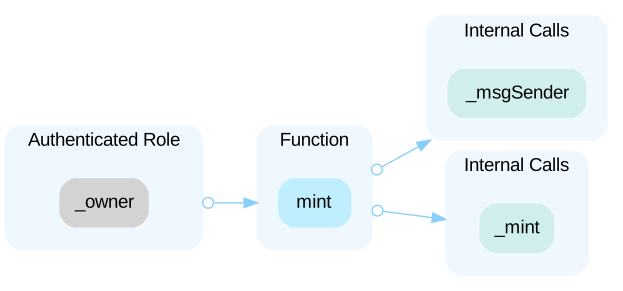
Open the reportLowLack of Jailbreak/Root detectionONFA - Pentesting · CertiK · 16 Nov 2024Fixed
The Onfa iOS application does not adequately detect if the device is jailbroken. As a result, the data which is stored via the applications can be exposed when the device is rooted.
Open the reportLowSelf Cross-Site Scripting (XSS) in Activity LogsONFA - Pentesting · CertiK · 16 Nov 2024Fixed
When a user performs actions such as login, logout, or removing an IP from the whitelist, the application logs the IP and User-Agent. These logs are displayed to the user in `Settings > Activity Logs`. By modifying the User-Agent to include an XSS payload, a user can execute JavaScript code within their own session.
Open the reportLowUser Enumeration in LoginONFA - Pentesting · CertiK · 16 Nov 2024Fixed
The `Login` functionality allows an attacker to infer if an email is registered on the platform based on the server response. When an invalid email is sent to the server, the server responds with `Email address does not exist.`. If the email is registered but the password is wrong, the server responds with `Wrong password.`
Open the reportLowWeb server information disclosureONFA - Pentesting · CertiK · 16 Nov 2024Fixed
The application exposes information about the software version used through the HTTP headers. - `X-Powered-By: ASP.NET` - `X-Aspnet-Version: 4.8.50727` - `X-Aspnetmvc-Version: 4.8`
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="onfa"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us