
OpenWorld security record
As of 3 Nov 2026, OpenWorld has 1 audit report on Trustblock, by CertiK, dated 16 May 2023. That report lists no open critical findings.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Audits1
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| Open World | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
Findings30
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 4 | 0 |
| Medium | 0 | 2 | 1 |
| Low | 10 | 0 | 13 |
HighCentralization Related RisksOpen World · CertiK · 16 May 2023Acknowledged
In the contract `OapRouter` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and: - set any address they control as the owner; - set any address as the new `pancakeRouter`; - set any address as the new `rewardRouter`; - set any token address as whitelisted or non-whitelisted; This could lead to a loss of assets or complete sabotage of the contract. 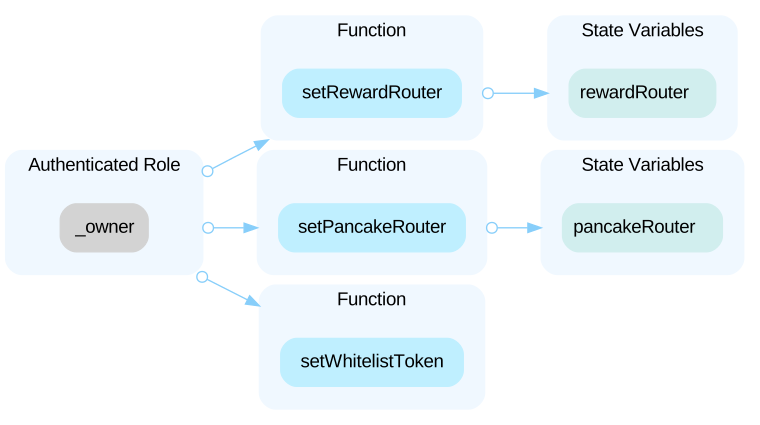 ----- In the contract `OpenStaking.sol` the role `isOperator` has authority over the following functions: - `addOperator()` - `removeOperator()` - `setUnstakingFee()` - `setUnstakingThreshold()` - `emergencyWithdraw()` Any compromise to an `isOperator` account may allow a hacker to take advantage of this authority and : - set any address they control as an operator; - revoke the operator privilege from any other address; - set the fees to any value less than 20%, those fees will not be transferred to the caller unstaking their `depositToken`; - set any non-zero value as `unstakingThreshold`; - drain all ERC20 tokens from the contract. ----- In the contract `RewardRouterV2.sol`, the role `onlyGov` has authority over the following functions: - `initialize()` - `withdrawToken()` - `batchStakeOpenForAccount()` - `stakeOpenForAccount()` - `compoundForAccount()` - `batchCompoundForAccounts()` Any compromise to an `onlyGov` account may allow a hacker to take advantage of this authority and: - initialize the contract if it has not be done already; - drain all ERC20 from the contract; - open staking for any address; - allow compounding for any address; ----- In the contract `OPEN` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and : - transfer the ownership to an address they control; - mint any amount of token to any address; - burn any amount of token from any address; - blacklist or whitelist any address, both for EOA and contracts; - add or remove any address to the set of `_sellAddresses`; - change the `sellFeeRate`; - add or remove any address to the set of `_exceptionAddresses`; - set any address as the `stakerAddress`; - drain every ERC20 token from the contract. 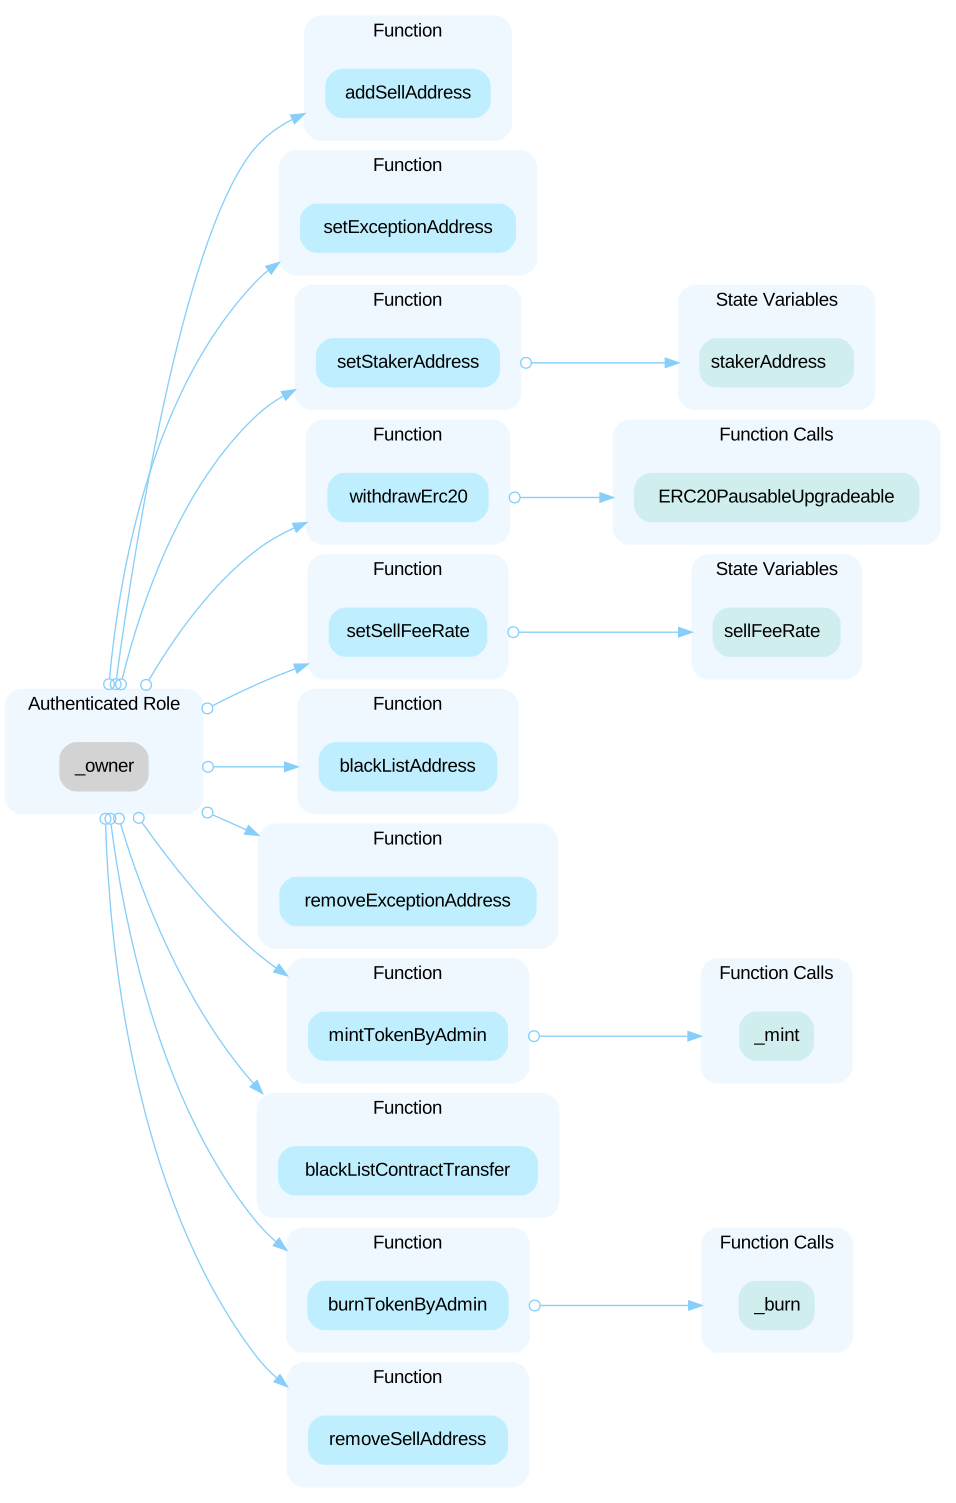
Open the reportHighCentralized Control of Contract UpgradeOpen World · CertiK · 16 May 2023Acknowledged
`OPEN` is an upgradeable contract, the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, they can change the implementation of the contract and drain tokens from the contract.
Open the reportHighInitial Token DistributionOpen World · CertiK · 16 May 2023Acknowledged
All `OPEN` tokens are sent to the address given as an input parameter when initializing the contract. This is a potential centralization risk as the receiver can distribute `OPEN` tokens without the consensus of the community.
Open the reportHighOperators can remove each otherOpen World · CertiK · 16 May 2023Acknowledged
In `OpenStaking`, the privileged role `isOperator` has power over functions `addOperator()` and `removeOperator()`. \ Any operator can then remove anyone from the set of operators, if a malicious user acquires the role `isOperator`, they would be able to revoke the privileged role from any other user.
Open the reportMediumIncompatibility with Deflationary TokensOpen World · CertiK · 16 May 2023Acknowledged
When transferring deflationary ERC20 tokens, the input amount may not be equal to the received amount due to the charged transaction fee. For example, if a user sends 100 deflationary tokens (with a 10% transaction fee), only 90 tokens actually arrived to the contract. However, a failure to discount such fees may allow the same user to withdraw 100 tokens from the contract, which causes the contract to lose 10 tokens in such a transaction. Reference: https://thoreum-finance.medium.com/what-exploit-happened-today-for-gocerberus-and-garuda-also-for-lokum-ybear-piggy-caramelswap-3943ee23a39f
Open the reportMediumInitializer Gives Large AllowanceOpen World · CertiK · 16 May 2023Acknowledged
In `OpenWorld.sol`, when `initialize()` is called the caller will be set as the `owner` of the contract and will also be approved to transfer up to the total supply of `OPEN` tokens from the contract. This allowance will not be revocated nor transferred if the ownership is renounced or transferred.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="open-world"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us