
OSIS security record
As of 3 Nov 2026, OSIS has 1 audit report on Trustblock, by CertiK, dated 5 Dec 2022. That report lists no open critical findings.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Audits1
Newest first
Findings18
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 1 |
| High | 1 | 0 | 0 |
| Medium | 0 | 2 | 2 |
| Low | 5 | 0 | 7 |
HighCentralization Related RisksOSIS · CertiK · 5 Dec 2022Open
In the contract `Collection` the role `onlyOwner` has authority over the functions shown in the diagram below. Any compromise to the `onlyOwner` account may allow the hacker to take advantage of this. The malicious user could change the max amount of tokens to mint, and they could change the baseURI of the token. The base extension could also be changed destroying potentially destroying the IFPS hash. As well as pausing or unpausing the contract when they want to. The user could also drain all the assets sent to the contract. 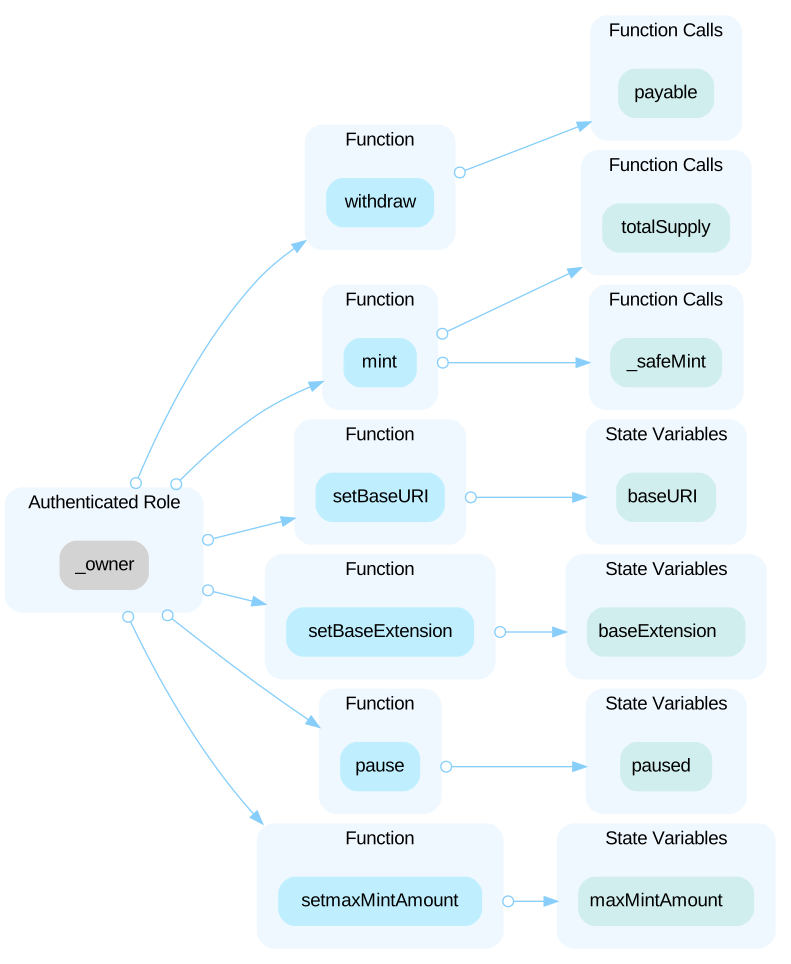 ---- In the contract `MBGTokensV2` the role `BURNER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `BURNER_ROLE` account may allow the hacker to take advantage of this by calling the burn function to burn anyone's tokens. 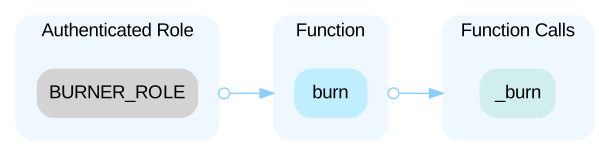 In the contract `MBGTokensV2` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this. The malicious user could grant themselves the ability to burn or mint tokens. The malicious user would then call these functions to exploit the contract by granting themselves large quantities of tokens or burning from any user. 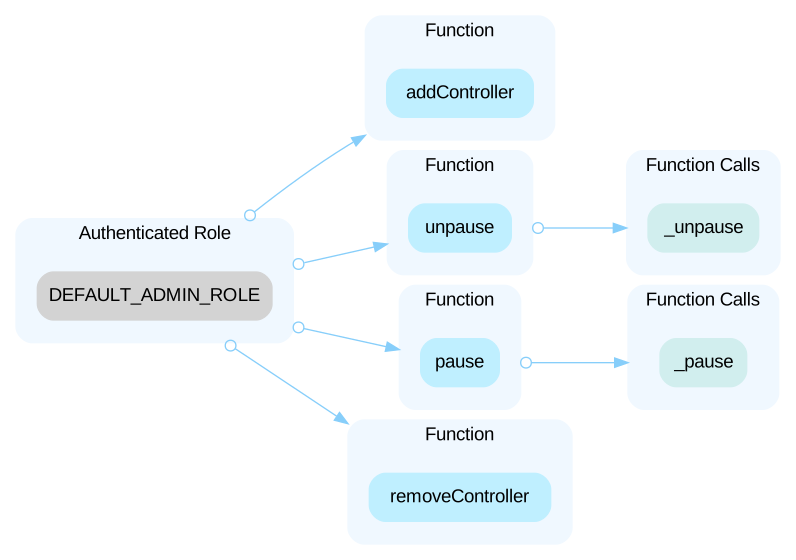 In the contract `MBGTokensV2` the role `MINTER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this by minting any amount of tokens they want. 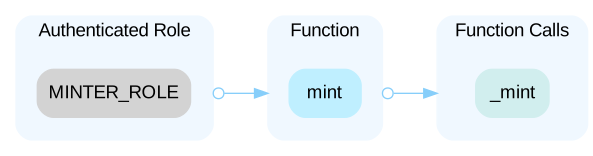 In the contract `MBGTokensV2` the role `controllers` has authority over the functions shown in the diagram below. Any compromise to the `controllers` account may allow the hacker to take advantage of this authority. This would allow an airdrop to any user by minting tokens to the user. 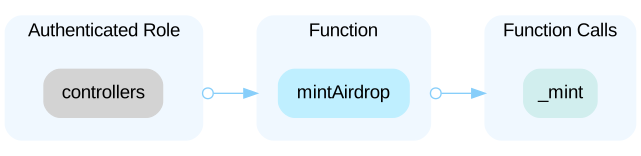 --- In the contract `Collection` the role `onlyOwner` has authority over the functions shown in the diagram below. Any compromise to the `onlyOwner` account may allow the hacker to take advantage of this. The malicious user could change the max amount of tokens to mint, and they could change the baseURI of the token. The base extension could also be changed destroying potentially destroying the IFPS hash. As well as pausing or unpausing the contract when they want to. The user could also drain all the assets sent to the contract. 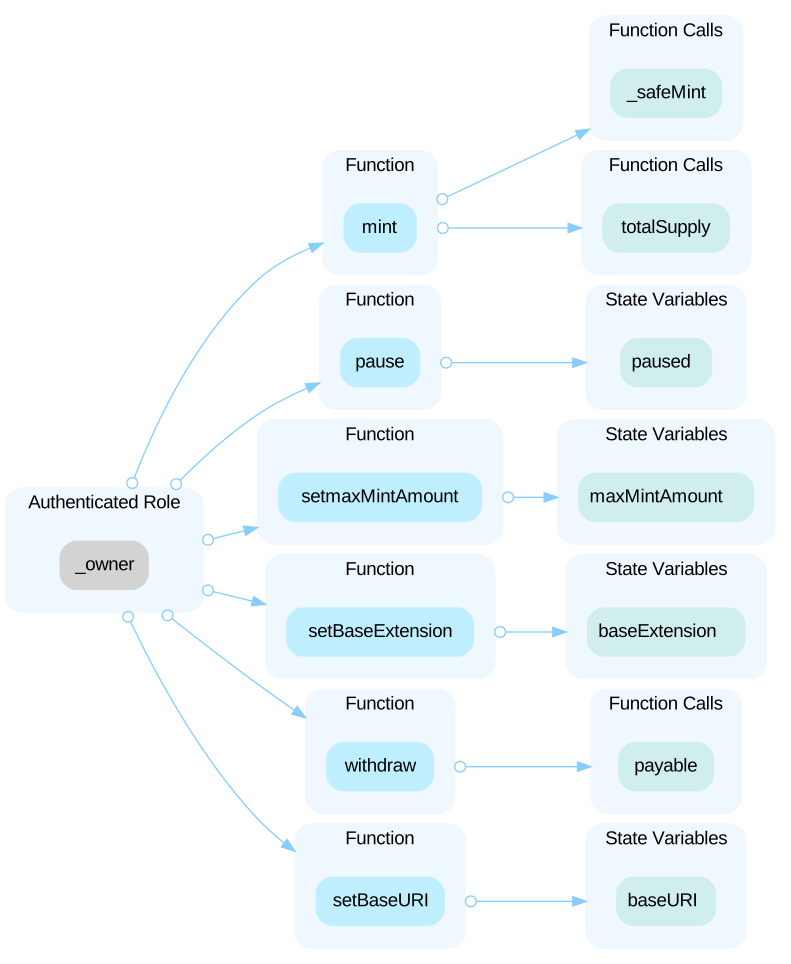 --- In the contract `OSIS` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this. The deployer receives all the tokens on deployment. Along with being able to add and remove controllers. 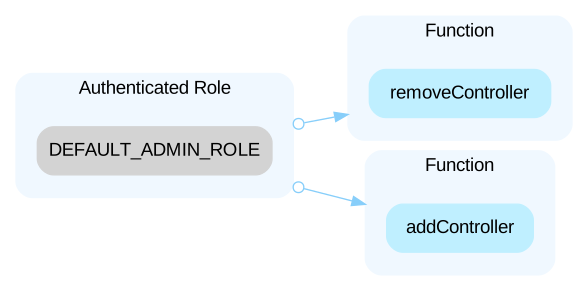 ---- In the contract `MBStaking` the role `onlyOwner` has authority over the functions shown in the diagram below. Any compromise to the `onlyOwner` account may allow the hacker to take advantage of this and change the rewards. 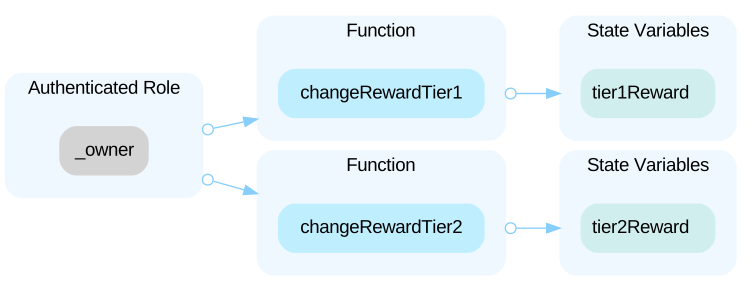
Open the reportLowMissing Emit EventsOSIS · CertiK · 5 Dec 2022Open
Functions that update state variables should emit relevant events as notifications.
Open the reportLowPotential Out-Of-Gas ExceptionOSIS · CertiK · 5 Dec 2022Open
The function `mint()` uses a loop to mint tokens to a certain address. This can loop to any number input.
Open the reportLowStaking File Could Include Approval AllOSIS · CertiK · 5 Dec 2022Open
It could be more efficient to have an approve all functionality for users to approve multiple at once.
Open the reportLowUnnecessary Use of SafeMathOSIS · CertiK · 5 Dec 2022Open
The `SafeMath` library is used unnecessarily. With Solidity compiler versions 0.8.0 or newer, arithmetic operations will automatically revert in case of integer overflow or underflow. ```solidity=13 using SafeMath for uint256; ``` - `SafeMath` library is used for `uint256` type in `MBGTokensV2` contract.
Open the reportLowUsecase of `saveUserStakedTokenId()` and `removeUOSIS · CertiK · 5 Dec 2022Open
Anyone can call this and create vaults. These functions are called when using `stake()` and `unstake()`. However, we are wondering the utility of these functions being public Additionally, multiple Vaults Can be Opened with Same ID.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="osis"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us