Incident
Incident,
The contract owner could disable the transfer function, which restricted users in selling their tokens.
Source: De.Fi incident database.
- Audits before it
- 0.
- Audits since
- 1, the latest dated 12 Jul 2023.
As of 15 Oct 2026, PLANET has 1 audit report on Trustblock, by CertiK, dated 12 Jul 2023. That report lists no open critical findings. It also holds 1 deployed contract on 1 chain and 1 incident (latest 12 Sep 2021).
Record last updated . It holds audits and findings, contracts and incidents up to Oct 2026. Trustblock does not review code.
Newest first
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 1 |
| Medium | 2 | 0 | 0 |
| Low | 7 | 0 | 0 |
In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer or renounce ownership. 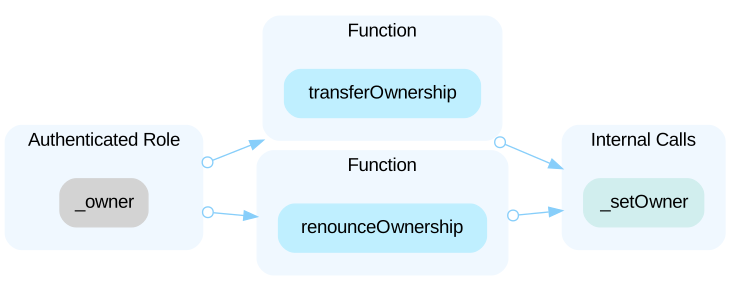 In the contract `PLANET` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and: - drain all `Eth` from the contract through `rescueETH()`. - drain all tokens from the contract through `rescueERC20()`. - exclude or include addresses from paying fees. - set `taxes`, `sellTaxes`, `maxWalletLimit`, `tokenLiquidityThreshold` without reasonable boundaries, so they can be given arbitrary values after deploying. - change the value of `providingLiquidity`. - set the address of `marketingWallet`. - set `isearlybuyer`, users in this mapping cannot transfer their tokens until the owner moves them out of the mapping. 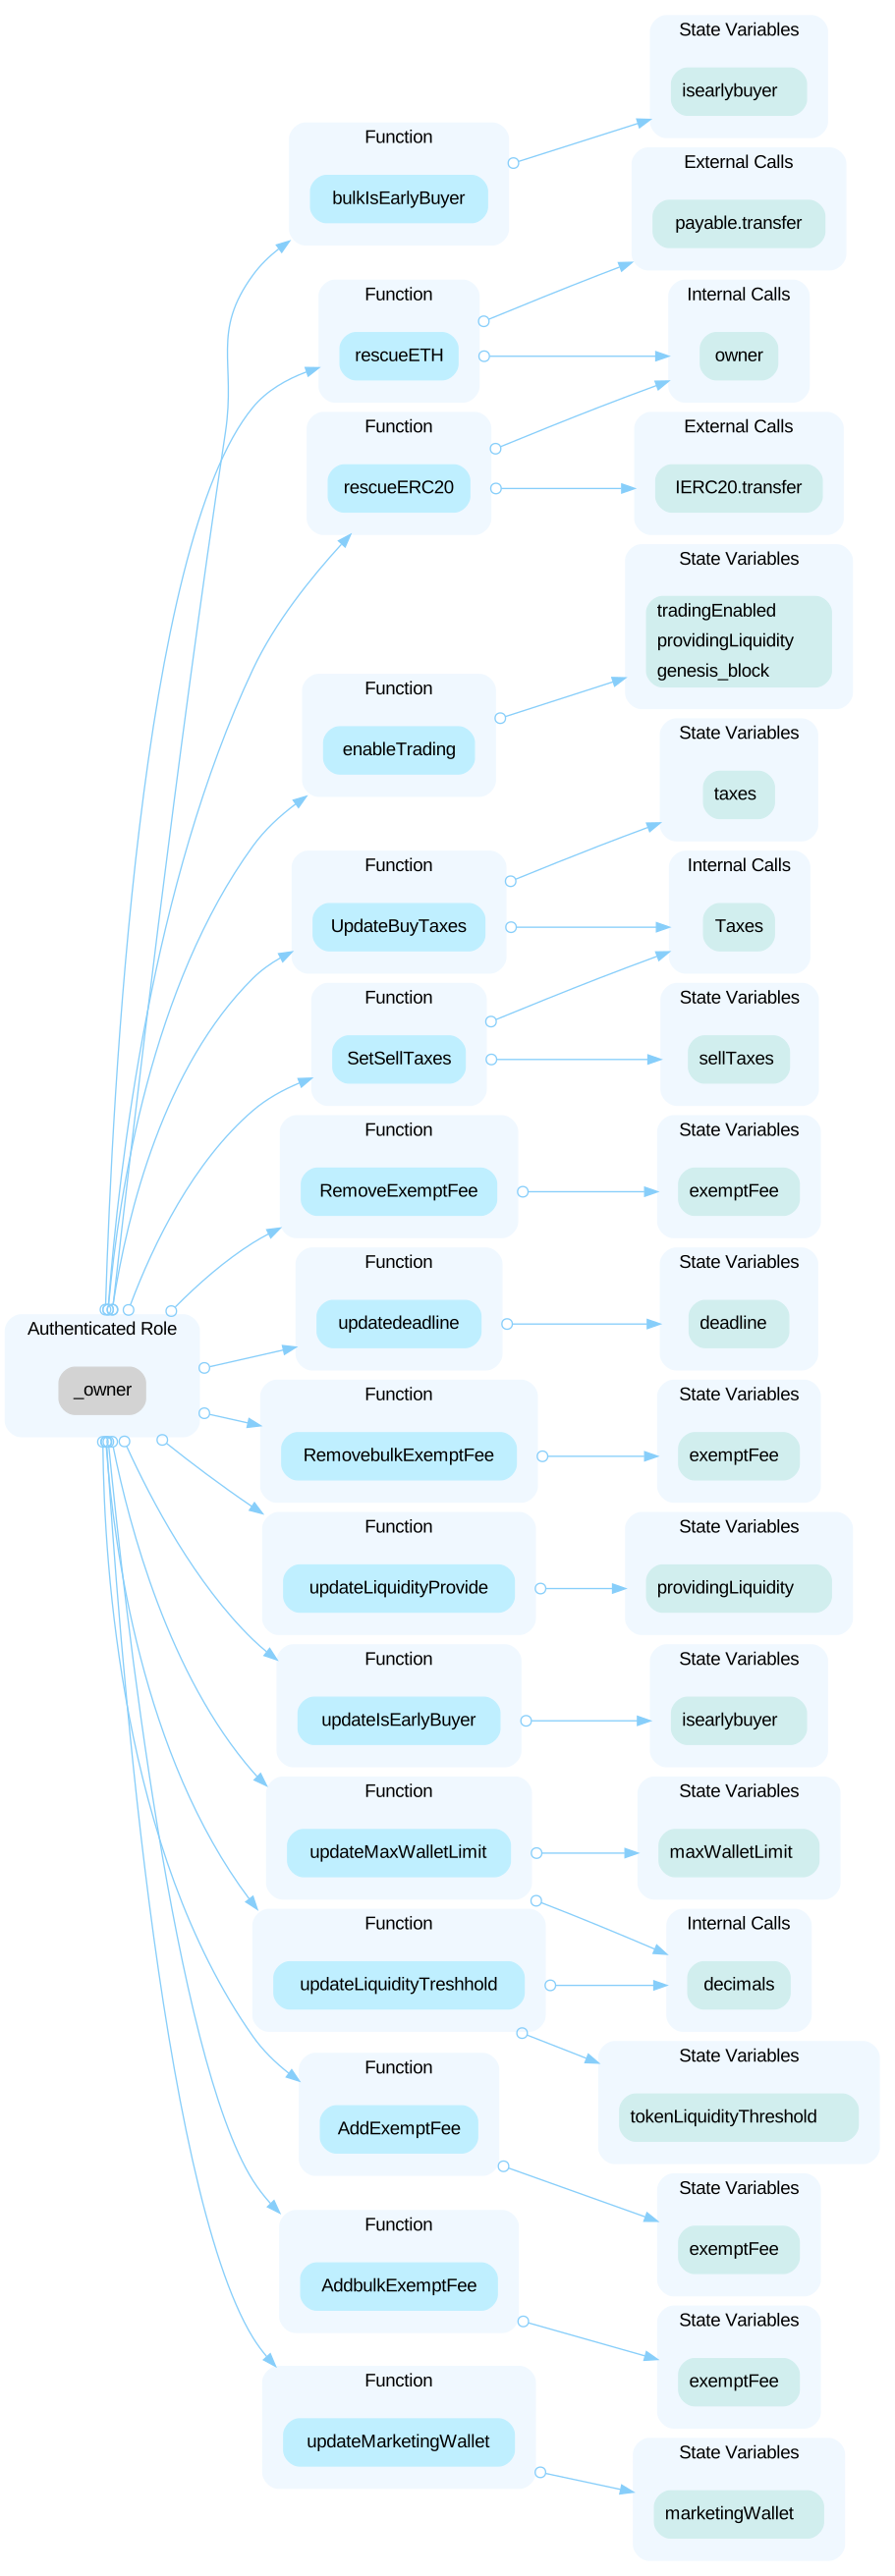
Open the reportAll of the **PLANET** tokens are sent to the contract deployer when deploying the contract. This could be a centralization risk as the anonymous deployer can distribute tokens without obtaining the consensus of the community. Any compromise to the deployer account that holds undistributed tokens may allow the attacker to steal and sell tokens on the market, resulting in severe damage to the project.
Open the reportIn the function `_transfer()`, the `currentTaxes` is not initialized in the below case. ```solidity } else if (useLaunchFee) { feeswap = launchtax; feesum = launchtax; } ``` If the threshold has been reached, the `handle_fees()` will fail in this case.
Open the reportThe `tokenLiquidityThreshold` can be set to arbitrary values. If `tokenLiquidityThreshold` is set to a big enough value, the taxes will not be used for liquidity until the `tokenLiquidityThreshold` is reached. Based on the logic of the below functions, the owner has the ability to transfer out all taxes before the `tokenLiquidityThreshold` is reached. ```solidity function updateLiquidityTreshhold(uint256 new_amount) external onlyOwner { //update the treshhold tokenLiquidityThreshold = new_amount * 10**decimals(); } function rescueETH(uint256 weiAmount) external onlyOwner { payable(owner()).transfer(weiAmount); } function rescueERC20(address tokenAdd, uint256 amount) external onlyOwner { IERC20(tokenAdd).transfer(owner(), amount); } ```
Open the report```solidity if (sender == pair && !exemptFee[recipient] && !_liquidityMutex) { require(balanceOf(recipient) + amount <= maxWalletLimit, "You are exceeding maxWalletLimit" ); } if (sender != pair && !exemptFee[recipient] && !exemptFee[sender] && !_liquidityMutex) { if (recipient != pair) { require(balanceOf(recipient) + amount <= maxWalletLimit, "You are exceeding maxWalletLimit" ); } } ``` `maxWalletLimit` validation in the above code conditions can be bypassed if `_liquidityMutex` is true. The state variable `_liquidityMutex` will only be true inside the `handle_fees()` function. However, in the `handle_fees()`, tokens are only transferred to the pair. Hence this `&& !_liquidityMutex` logic is redundant.
Open the reportPerforming integer division before multiplication truncates the low bits, losing the precision of calculation. ```solidity=615 uint256 unitBalance = deltaBalance / (denominator - swapTaxes.liquidity); ``` ```solidity=616 uint256 ethToAddLiquidityWith = unitBalance * swapTaxes.liquidity; ```
Open the reportIn a modifier, the `_` symbol is used to continue the execution of the function with the modifier applied. If a modifier does not execute `_` or revert, the modifier will not execute the function body and in that case the return variables are set to their default values just as if the function had an empty body, which can be misleading for the caller. Modifier PLANET.mutexLock() (PLANET.sol#444-450) does not always execute _; or revert ```solidity=444 modifier mutexLock() { if (!_liquidityMutex) { _liquidityMutex = true; _; _liquidityMutex = false; } } ```
Open the reportThe `feesum` eqauls the `feeswap` in all cases. The linked statements do not affect the functionality of the codebase.
Open the reportVariables are written but never read and subsequently written again, suggesting potential inefficiencies or logic errors in the code. This may lead to confusion when analyzing the code or impact the performance of the smart contract during execution. `fee` is written twice, but not used in-between. Since the `feesum` is not initialized in this case, it defaults to zero and the fee is set to zero in L574 again. ```solidity=554 fee = 0; ``` ```solidity=574 fee = (amount * feesum) / 100; ```
Open the reportThe contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=415 IRouter public router; ``` - The contract `PLANET` interacts with third party contract with `IRouter` interface via `router`.
Open the reportLiterals with many digits are difficult to read and review. ```solidity=422 uint256 private tokenLiquidityThreshold = 2000000000 * 10**18; ``` --- ```solidity=423 uint256 public maxWalletLimit = 20000000000 * 10**18; ``` --- ```solidity=453 _tokengeneration(msg.sender, 1000000000010 * 10**decimals()); ```
Open the reportAttached through a shared contract address. Our incident data ends in Oct 2026.
The contract owner could disable the transfer function, which restricted users in selling their tokens.
Source: De.Fi incident database.
| Address | Chain | Source code |
|---|---|---|
| 0x2ad9…ab0b0x2ad9addd0d97ec3cdba27f92bf6077893b76ab0b | Chain: Ethereum | Source code: Verified source |
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="planet"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us