
Playbux audit reports
Playbux has 1 public audit report from CertiK; dated 27 Jun 2023; no critical findings reported.
Last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Open findings across every firm2
Statuses are the security firms’ own
2 findings are still open or acknowledged in the firms’ reports: 1 high, 1 low (all open).
- High
- 1
- Low
- 1
Audits1
Newest first
| Report | Security firm | Date | Scope | Critical findings | Findings | Source |
|---|---|---|---|---|---|---|
| Playbux | Security firm: CertiK | Date: | Scope: Files listed | None open | Findings: 1 high · 1 medium · 6 low 6 fixed · 2 open | skynet.certik.com ↗ |
Findings8
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 1 | 0 | 5 |
HighCentralization Related RisksPlaybux · CertiK · 27 Jun 2023Open
***In the contract `PlaybuxQuestNFT`*** the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and modify the configs of the contract. 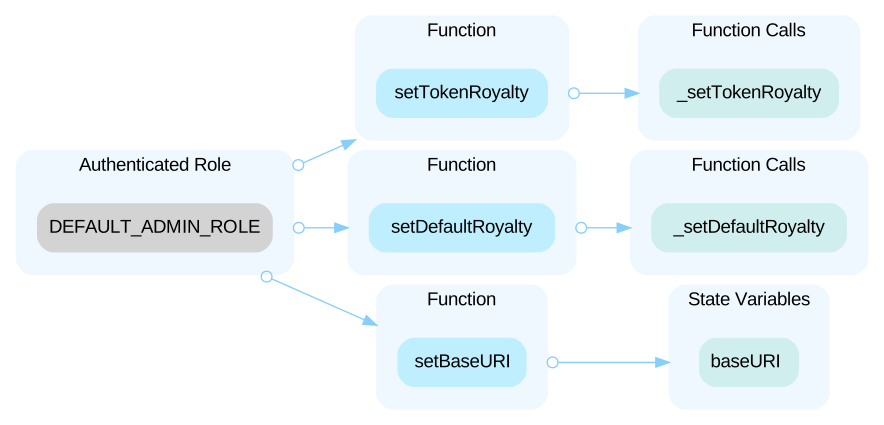 AND The role `FACTORY_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `FACTORY_ROLE` account may allow the hacker to take advantage of this authority and mint tokens for arbitrary addresses. 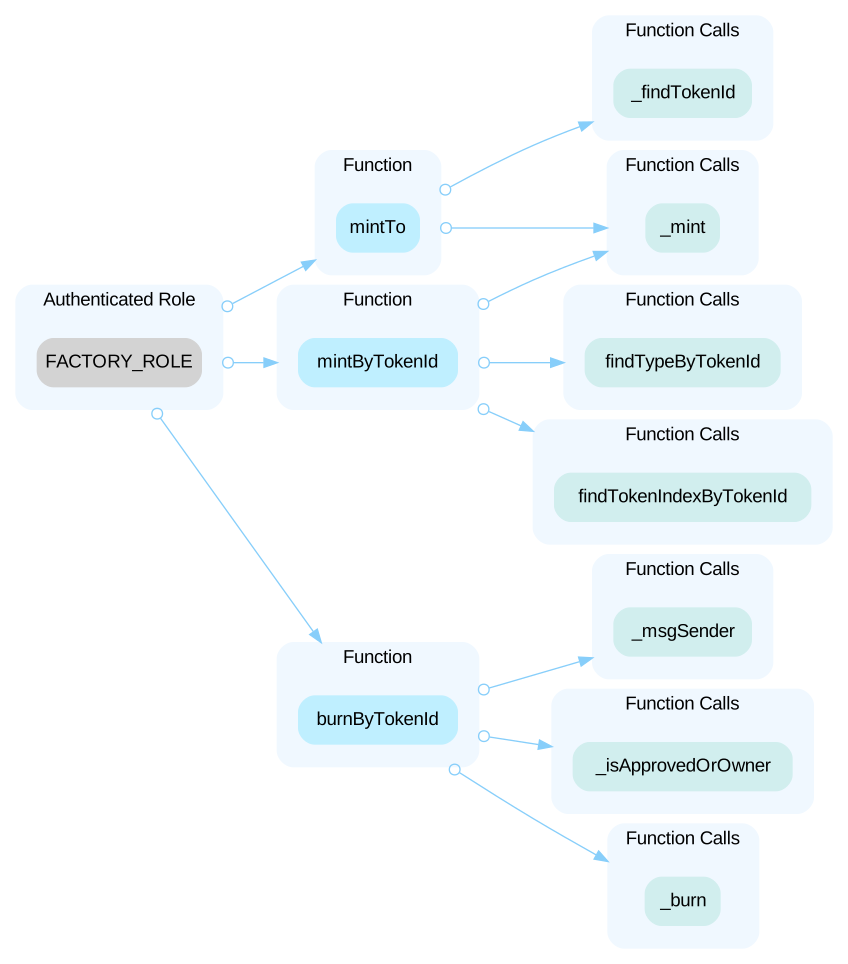 ***In the contract `BUSDFactory`*** the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and change the configs of the contract. 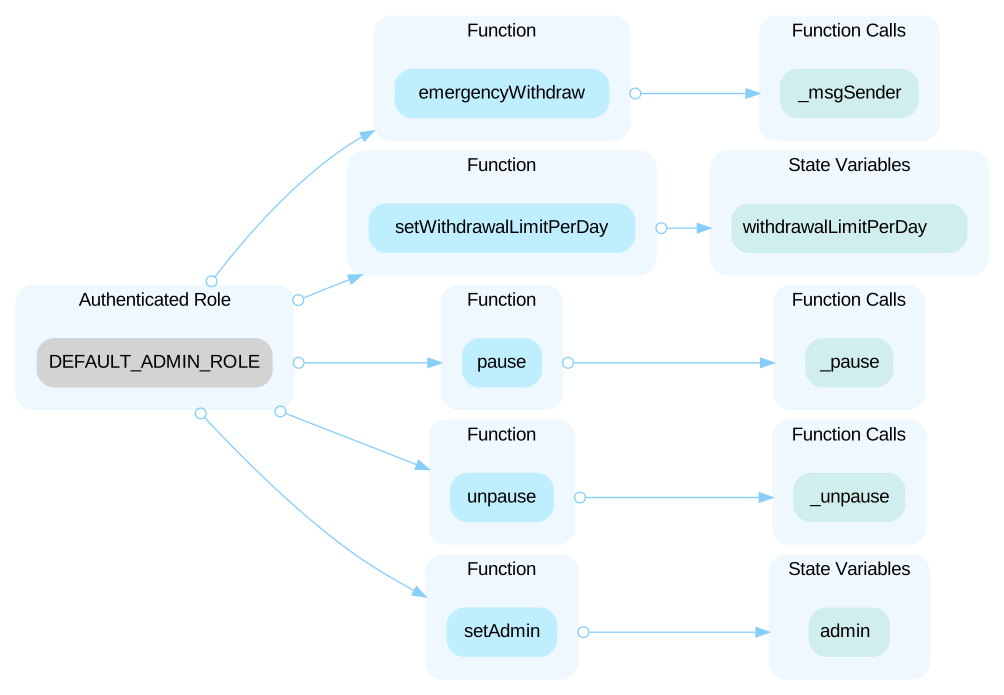 AND The role `admin` has authority over the following function(s): - function `withdraw()`, to withdraw **BUSD** token from the contract. Any compromise to the `admin` account may allow the hacker to take advantage of this authority and withdraw money from the contract. ***In the contract `NFTCompound`*** the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and change the configs of the contract. 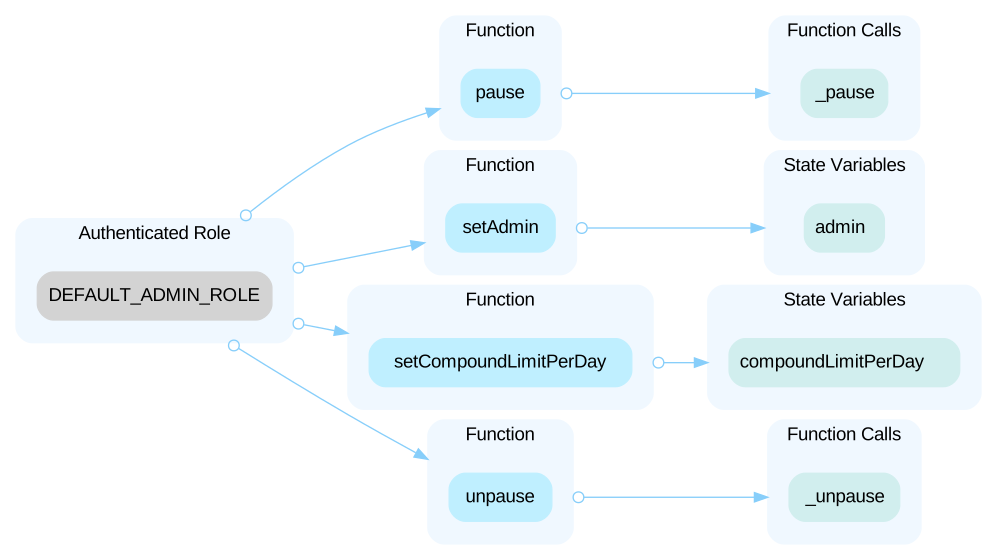 AND The role `admin` has authority over the following function(s): - function `compound()`, to mint an NFT to `_receiver`. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and change the configs of the contract. ***In the contract `NFTFactory`*** the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and change the configs of the contract. 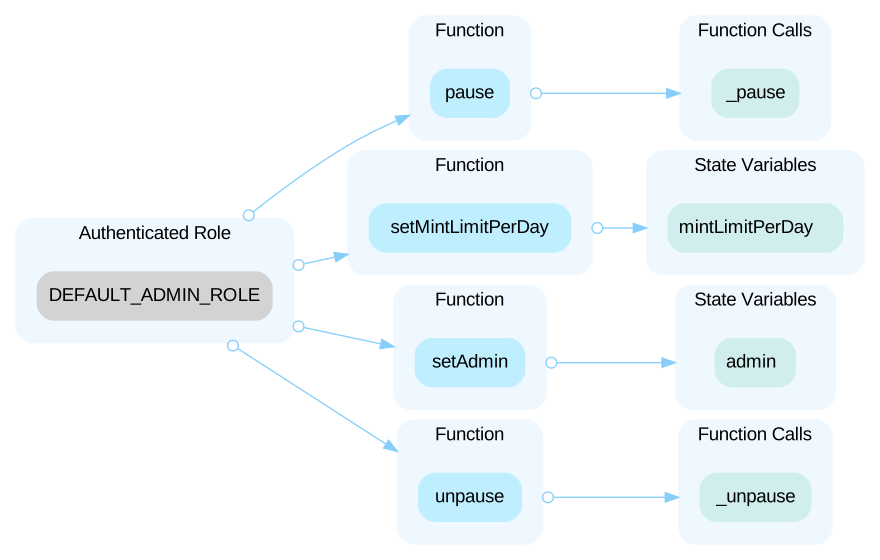 AND The role `admin` has authority over the following function(s): - function `mint()`, to mint an nft token to `_receiver`. Any compromise to the `admin` account may allow the hacker to take advantage of this authority and mint tokens for arbitrary addresses. ***In the contract `PlaybuxSBT`*** the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and bring unpredictable damages to the project. 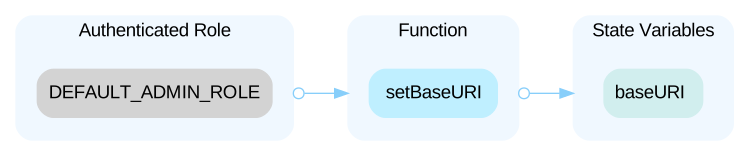 AND The role `FACTORY_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `FACTORY_ROLE` account may allow the hacker to take advantage of this authority and bring unpredictable damages to the project. 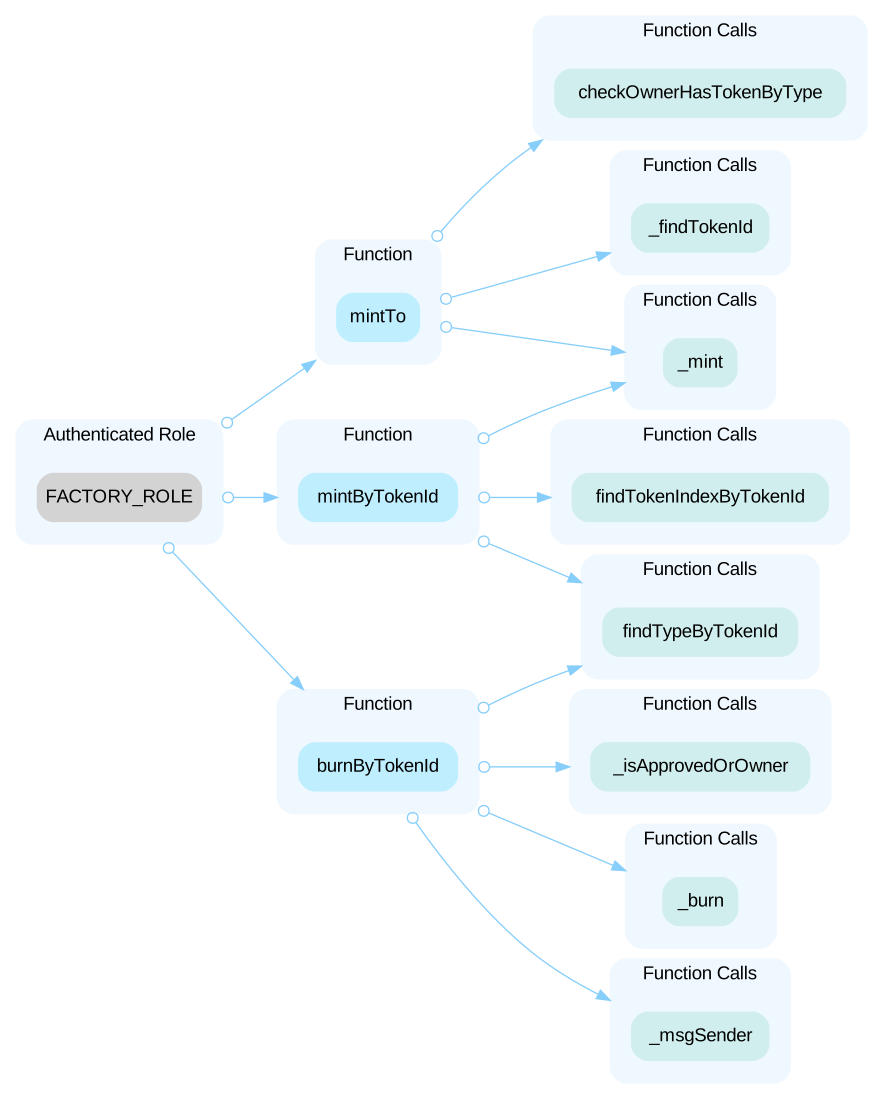 ***In the contract `PlaybuxSBTFactory`*** the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and bring unpredictable damages to the project. 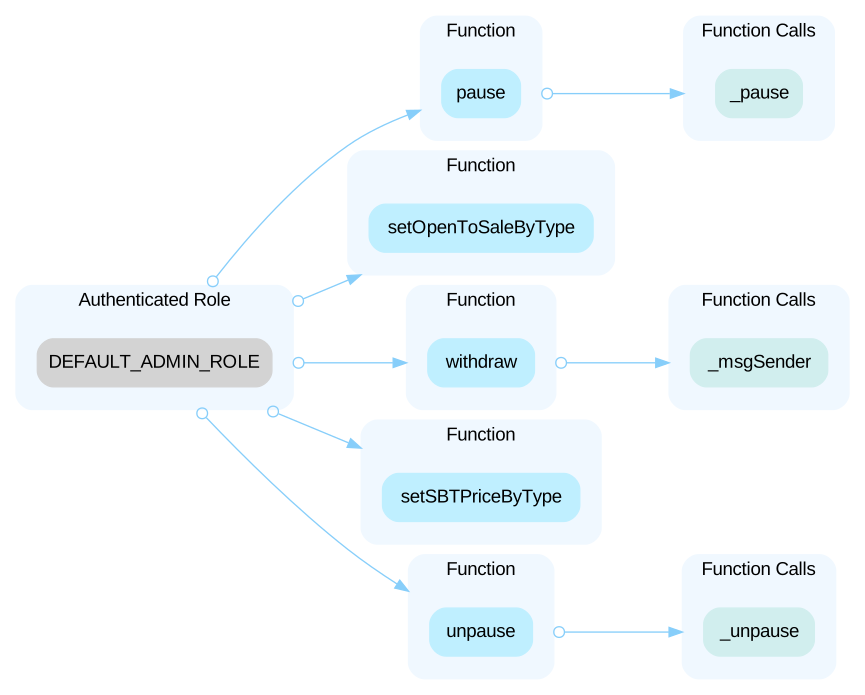 All of the above contracts inherit the contract `AccessControl` and the role `DEFAULT_ADMIN_ROLE` has authority over the following function(s): - function `grantRole()`, to grant a role to one arbitrary account. - function `revokeRole()`, to revoke a role from one arbitrary account. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and destroy the permission control of the protocol.
Open the reportLowThird Party DependencyPlaybux · CertiK · 27 Jun 2023Open
The contract is serving as the underlying entity to interact with one or more third-party protocols. The scope of the audit treats third-party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=16 IERC20 public immutable busd; ``` - The contract `BUSDFactory` interacts with third-party contract with `IERC20` iterface via `busd`. --- ```solidity=12 IERC20 public immutable busd; ``` - The contract `PlaybuxSBTFactory` interacts with third-party contract with `IERC20` iterface via `busd`. --- ```solidity=17 IPlaybuxQuestNFT public immutable nft; ``` - The contract `NFTCompound` interacts with third-party contract with `IPlaybuxQuestNFT` interface via `nft`. --- ```solidity=17 IPlaybuxQuestNFT public immutable nft; ``` - The contract `NFTFactory` interacts with third-party contract with `IPlaybuxQuestNFT` interface via `nft`. We understand the nft in NFTCompound and NFTFactory might be the PlaybuxQuestNFT (PBN) contract. However, in the audit, any presumptions are dangerous to the auditor because they may cause some potential issues not reviewed/listed if we believe the presumptions always hold. Once the protocol is deployed, this finding can be removed from the report after our verifications.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Playbux: questions
Is Playbux audited?
Trustblock holds 1 public audit report for Playbux, dated 27 Jun 2023. The latest is by CertiK (“Playbux”).
Who audited Playbux?
CertiK wrote the report Trustblock holds for Playbux.
Are there open findings in Playbux’s audits?
2 findings are still open or acknowledged in the firms’ reports: 1 high, 1 low (all open). No critical finding is reported. Statuses are the security firms’ own.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="playbux"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us