
Probinex audit reports
Probinex has 1 public audit report from CertiK; dated 3 Nov 2022; no critical findings reported.
Last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Open findings across every firm4
Statuses are the security firms’ own
4 findings are still open or acknowledged in the firms’ reports: 2 high, 2 low (all open).
- High
- 2
- Low
- 2
- High Open
Centralization Risks in PbxToken.sol
Probinex - New Deal · CertiK · 3 Nov 2022 · Report ↗
- High Open
Initial Token Distribution
Probinex - New Deal · CertiK · 3 Nov 2022 · Report ↗
- Low Open
Too Many Digits
Probinex - New Deal · CertiK · 3 Nov 2022 · Report ↗
- Low Open
Unnecessary Code
Probinex - New Deal · CertiK · 3 Nov 2022 · Report ↗
Audits1
Newest first
| Report | Security firm | Date | Scope | Critical findings | Findings | Source |
|---|---|---|---|---|---|---|
| Probinex - New Deal | Security firm: CertiK | Date: | Scope: Files listed | None open | Findings: 2 high · 2 low 4 open | skynet.certik.com ↗ |
Findings4
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 2 | 0 | 0 |
HighCentralization Risks in PbxToken.solProbinex - New Deal · CertiK · 3 Nov 2022Open
In the contract `PbxToken` the role `BLACKLISTER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `BLACKLISTER_ROLE` account may allow the hacker to take advantage of this authority and 1) Blacklist all the users with `DEFAULT_ADMIN_ROLE`, rendering them useless, by preventing them from calling the `grantRoleString()` and `revokeRoleString()` functions. It would become impossible to revoke the `BLACKLISTER_ROLE` from the hacker, if this were to happen. 2) Blacklist the users with `PAUSER_ROLE`, rendering them useless, and making it impossible to call the `pause()` function that disables the transfer of tokens and `unpause()` function that enables the transfer of tokens. 3) Blacklist the users using the `blacklist()` function that prevents them from participating in transfer of tokens and prevents the user with `DEFAULT_ADMIN_ROLE` to assign any new roles to them. 4) Allow the blacklisted users to participate in transfer of tokens using the `unBlacklist()` function. 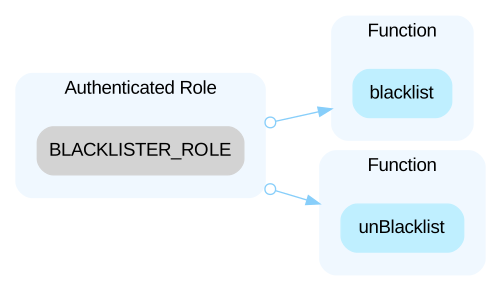 In the contract `PbxToken` the role `PAUSER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `PAUSER_ROLE` account may allow the hacker to take advantage of this authority and 1) Disable the transfer of tokens using the `pause()` function. 2) Enable the transfer of token using the `unpause()` function. 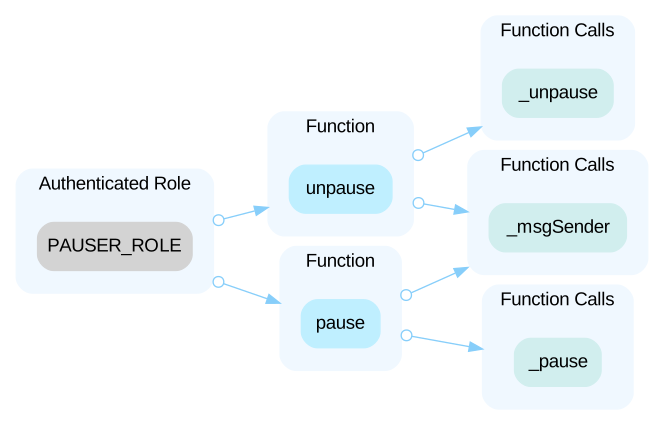 In the contract `PbxToken` the role `SNAPSHOT_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `SNAPSHOT_ROLE` account may allow the hacker to take advantage of this authority to hold tokens as short a time as possible to be included in each snapshot. 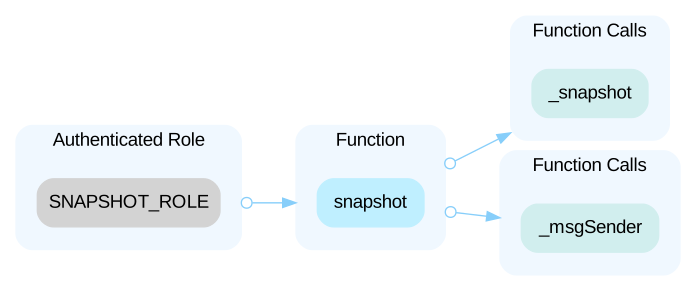 In the contract `PbxToken` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and grant `PAUSER_ROLE`, `SNAPSHOT_ROLE` and `BLACKLISTER_ROLE` to users, or revoke them using `grantRoleString()` and `revokeRoleString()` functions. 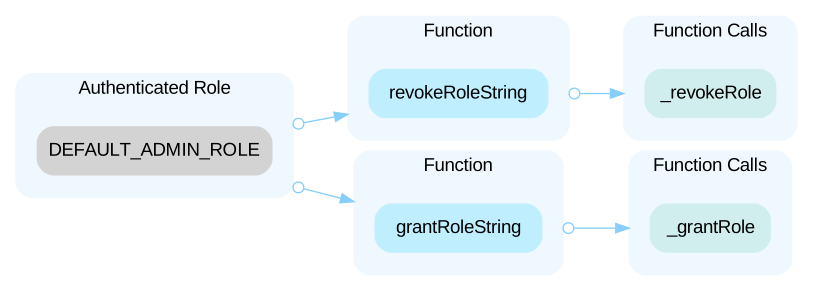
Open the reportHighInitial Token DistributionProbinex - New Deal · CertiK · 3 Nov 2022Open
All the tokens are sent to the `_msgSender()` when deploying the contract and no further minting of the tokens is possible. This could be a centralization risk as the deployer of the contract can distribute these tokens without obtaining the consensus of the community.
Open the reportLowToo Many DigitsProbinex - New Deal · CertiK · 3 Nov 2022Open
Literals with many digits are difficult to read and review.
Open the reportLowUnnecessary CodeProbinex - New Deal · CertiK · 3 Nov 2022Open
1) The `_mint()` function is called only in the constructor where no user is blacklisted. The modifiers `notBlacklisted(account)` and `notBlacklisted(_msgSender())` in the definition of `_mint()` function will always return true. 2) The `_mint()` function has the following require statement to put a cap on the total number of tokens in the contract but the parent contract `ERC20Capped` already takes care of it so, it can be removed. ```solidity=123 require( ERC20.totalSupply() + amount <= cap(), "ERC20Capped: cap exceeded" ); ``` 3) The contract does not allow minting of new tokens after construction. The inheritance of `ERC20Capped` contract can be avoided since the tokens in the contract are never going to increase after the minting of `CAP` amount of tokens during deployment.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Probinex: questions
Is Probinex audited?
Trustblock holds 1 public audit report for Probinex, dated 3 Nov 2022. The latest is by CertiK (“Probinex - New Deal”).
Who audited Probinex?
CertiK wrote the report Trustblock holds for Probinex.
Are there open findings in Probinex’s audits?
4 findings are still open or acknowledged in the firms’ reports: 2 high, 2 low (all open). No critical finding is reported. Statuses are the security firms’ own.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="probinex"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us