
RealFevr security record
As of 3 Nov 2026, RealFevr has 1 audit report on Trustblock, by CertiK, dated 1 Mar 2024. That report lists no open critical findings.
Record last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Audits1
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| RealFevr - bridge | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
Findings29
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 3 | 0 |
| Medium | 3 | 0 | 2 |
| Low | 10 | 0 | 11 |
HighCentralization Related RisksRealFevr - bridge · CertiK · 1 Mar 2024Acknowledged
## ERC20BridgeImpl.sol In the contract `ERC20BridgeImpl` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and - change the implementation logic used by the proxy to malicious code - give any role used within the contract to an address they control - remove the role privilege from a legitimate account - remove all available ERC20 tokens in the contract and send to an account they control - deposit any amount of an ERC20 approved to be bridged in the contract, potentially preventing others from depositing that token if the daily maximum is exceeded - create new ERC20 tokens to be used maliciously with the bridge protocol - burn all ERC20 tokens currently held in the contract - mint any amount of any ERC20 token for which the contract is the owner of 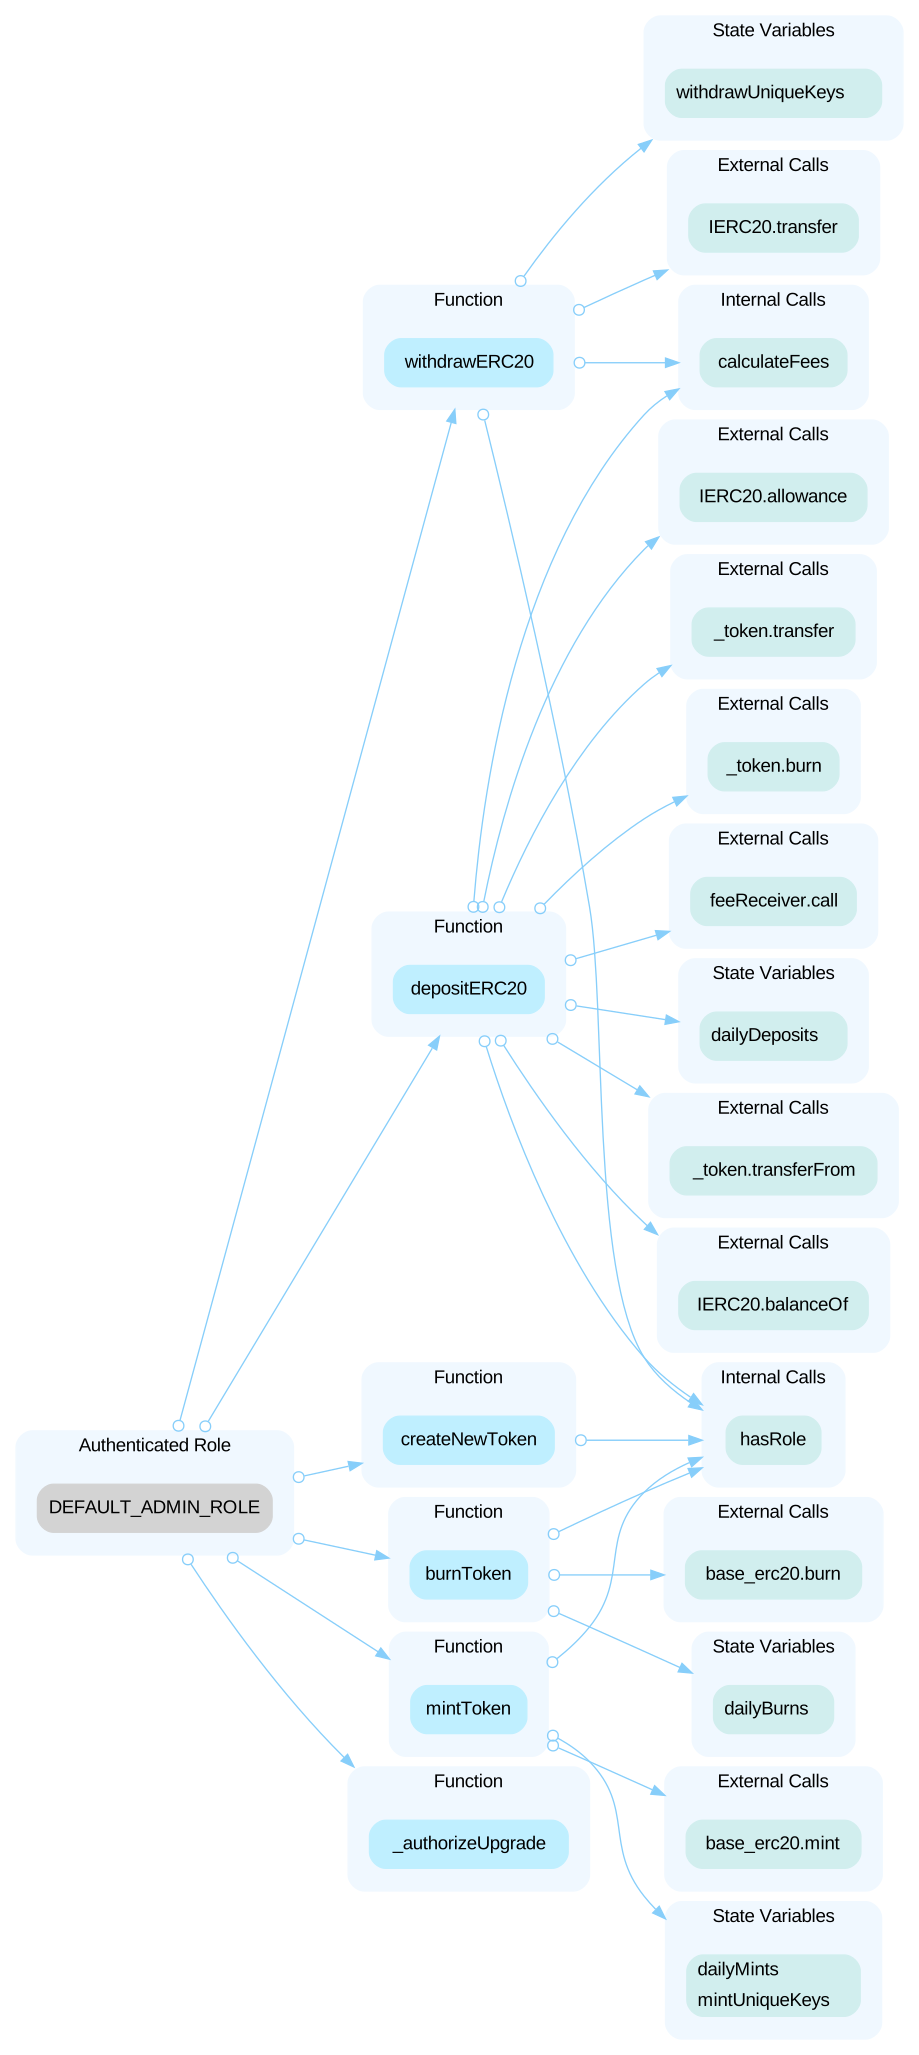 In the contract `ERC20BridgeImpl` the role `BRIDGE` has authority over the functions shown in the diagram below. Any compromise to the `BRIDGE` account may allow the hacker to take advantage of this authority and - withdraw all available ERC20 tokens in the contract and send to an account they control, as long as the amount does not cause the daily maximum to be exceeded for that token - burn all ERC20 tokens currently held in the contract, as long as the amount does not cause the daily maximum to be exceeded for that token - mint any amount of any ERC20 token for which the contract is the owner of, as long as the amount does not cause the daily mint maximum to be exceeded for that token 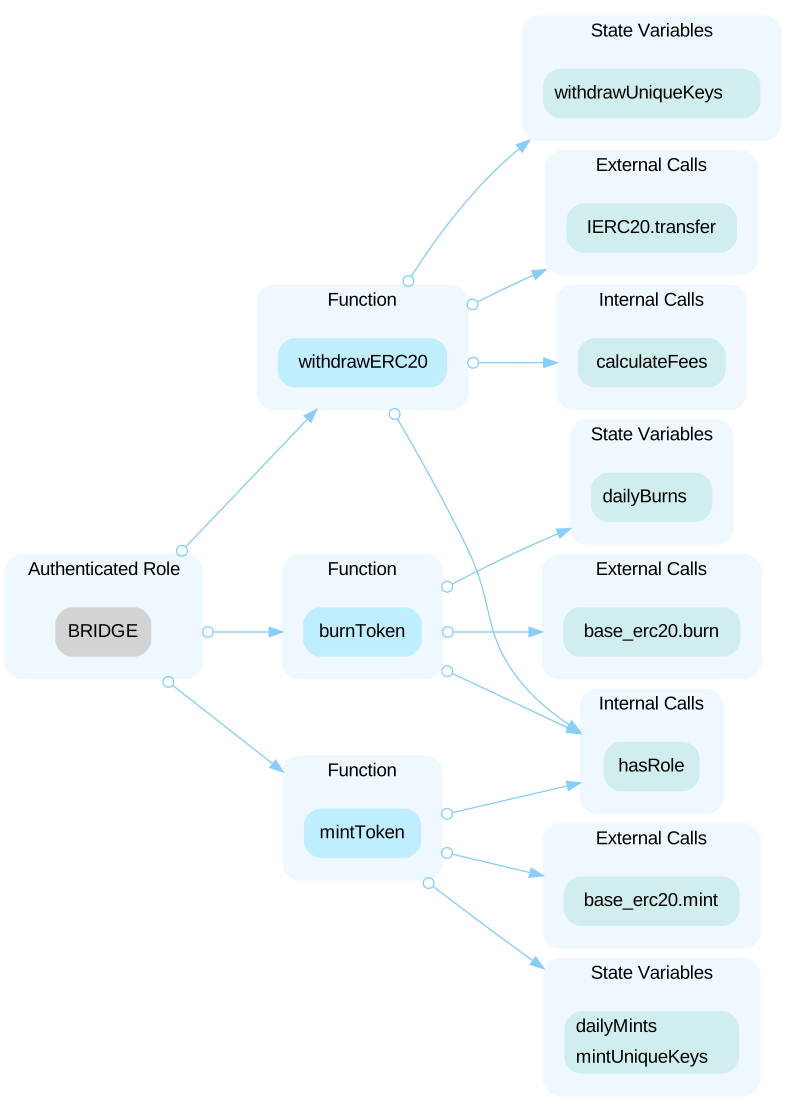 In the contract `ERC20BridgeImpl` the role `OPERATOR` has authority over the functions shown in the diagram below. Any compromise to the `OPERATOR` account may allow the hacker to take advantage of this authority and - update the bridge status in order to use or prevent the use of bridge functionality during a time-sensitive period. - change the `feeReceiver` address to an account they control, and update fees to collect a maximal amount from deposits and withdrawals - update supported chains to allow unintended chains, or to prevent legitimate chains from being used - create new ERC20 tokens to be used maliciously with the bridge protocol - change the 24 hour maximum values for deposit, withdrawal, minting and burning to either prevent these actions or allow an unintended amount to pass for their own gain - set `burnOnDeposit` to false for a token in order to remove the tokens through withdrawal and re-use within the bridge or other protocols for gain. This can be done if the account possesses both the `OPERATOR` role and either the `DEFAULT_ADMIN_ROLE` or the `BRIDGE` role - set up a malicious ERC20 token contract for use with the bridge 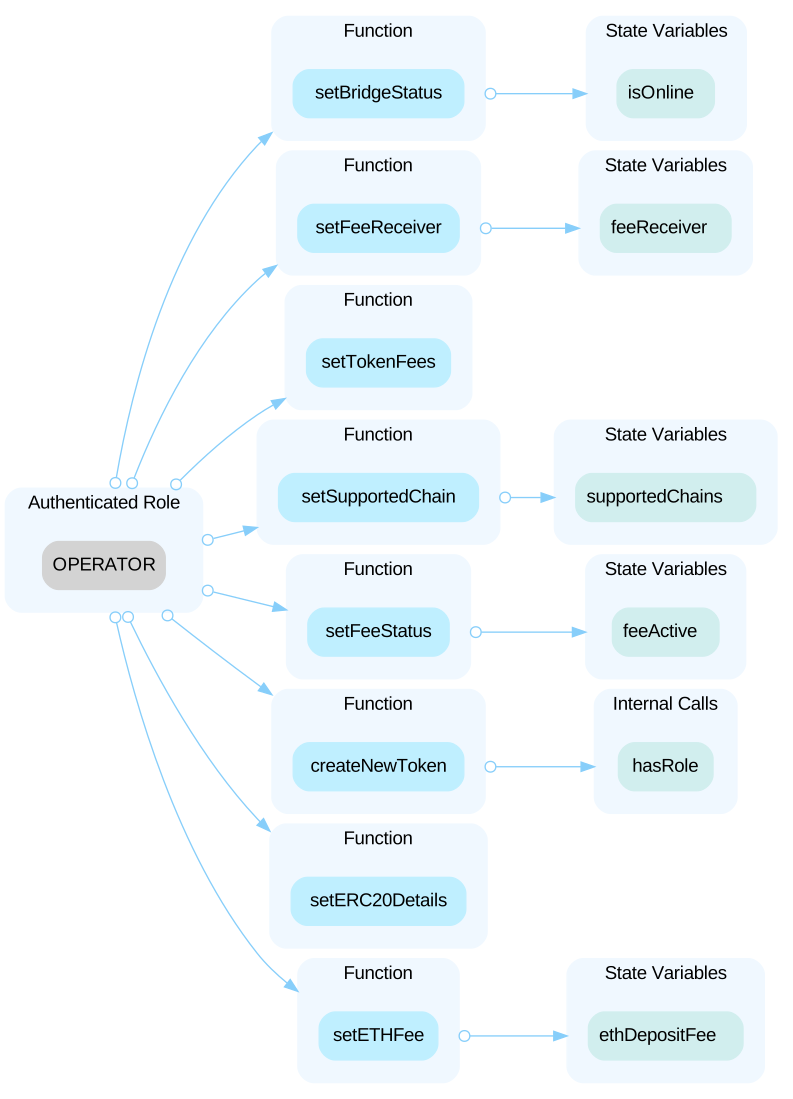 --- ## ERC721BridgeImpl.sol In the contract `ERC721BridgeImpl` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and - change the implementation logic used by the proxy to malicious code - give any role used within the contract to an address they control - remove the role privilege from a legitimate account 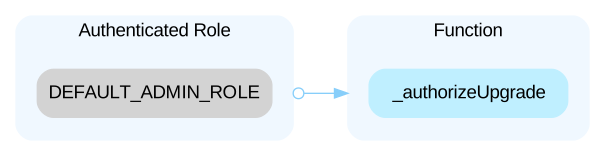 In the contract `ERC721BridgeImpl` the role `BRIDGE` has authority over the functions shown in the diagram below. Any compromise to the `BRIDGE` account may allow the hacker to take advantage of this authority and - withdraw all available ERC721 tokens in the contract and send to an account they control - mint any amount of any ERC721 tokens for which the bridge contract is the owner - update any NFT's market distributions to include any address and any uint rate, as long as the bridge contract is the owner of the ERC721 contract 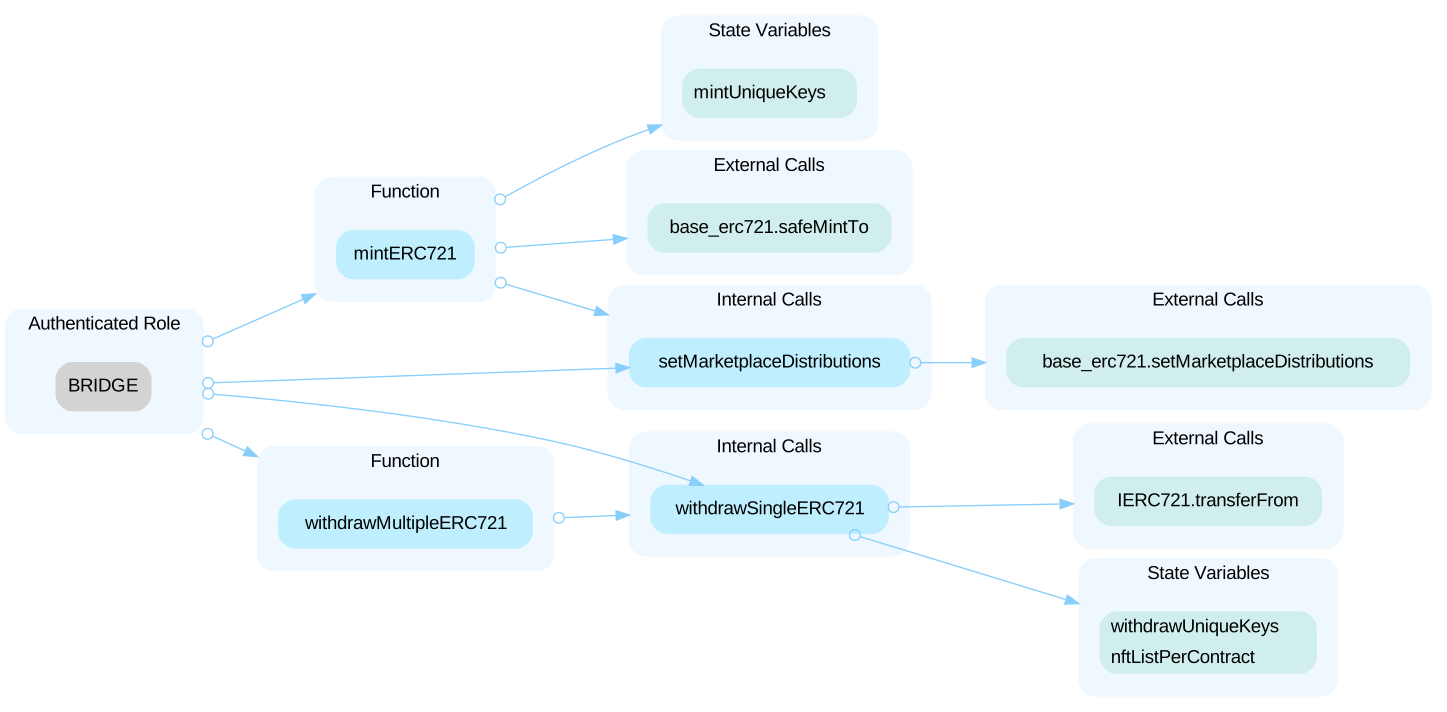 In the contract `ERC721BridgeImpl` the role `OPERATOR` has authority over the functions shown in the diagram below. Any compromise to the `OPERATOR` account may allow the hacker to take advantage of this authority and - update the bridge status in order to use or prevent the use of bridge functionality during a time-sensitive period. - change the `feeReceiver` address to an account t
Open the reportHighCentralized Control of Contract UpgradeRealFevr - bridge · CertiK · 1 Mar 2024Acknowledged
In contracts `ERC20BridgeImpl` and `ERC721BridgeImpl`, the role `DEFAULT_ADMIN_ROLE` has the authority to update the implementation contract behind each contract. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow a hacker to take advantage of this authority and change the implementation contract pointed by proxy and execute potential malicious functionality in the implementation contract.
Open the reportHighMinting Centralization RiskRealFevr - bridge · CertiK · 1 Mar 2024Acknowledged
In contracts `base_erc721` and `base_erc20`, the role `_owner` has the authority to mint tokens to arbitrary addresses. Any compromise to the `_owner` account may allow a hacker to take advantage of this authority and mint tokens to an address they control.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="realfevr"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us