As of 3 Nov 2026, Shopdi has 1 audit report on Trustblock, by CertiK, dated 27 Sep 2022. That report lists no open critical findings.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Newest first
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 1 | 0 |
| Medium | 0 | 1 | 0 |
| Low | 1 | 0 | 7 |
In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and call the `inCaseTokenGetStuck()` function to claim any stuck tokens held by the contract for themselves and transfer or renounce ownership. 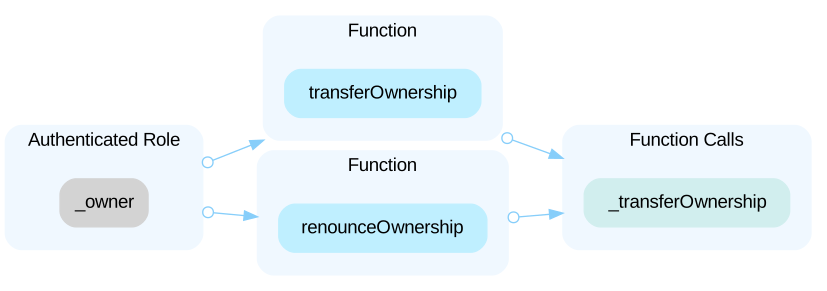 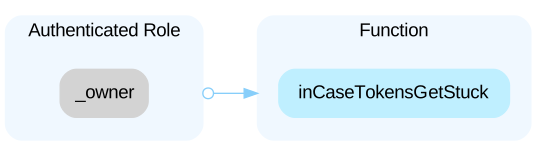 In the contract `Token` the role `gnosisSafeWallet` has authority over the functions shown in the diagram below. Any compromise to the `gnosisSafeWallet` account may allow the hacker to take advantage of this authority and exploit the contract in multiple ways. 1) The hacker could mint as many tokens as they want and send it to anyone. 2) They could change the `TokenStrategy` address, which receives all the tax amount. 3) They could increase the `transferTaxRate`, in addition to changing the `TokenStrategy` address, which would lead to more tax being sent to the `TokenStrategy` address, on every transfer that's not excluded from tax. 4) They could modify the `maxTransferAmountRate` variable, which decides the maximum amount that a user can transfer. 5) They could modify the `_excludedFromAntiWhale` array using the `setExcludedFromAntiWhale()` function. It could lead users to bypass the limit set by `maxTransferAmountRate`. The hacker could set the `maxTransferAmountRate` to be really low, and dictate who can transfer the tokens using `_excludedFromAntiWhale` array. 6) They could use the `setExcludedFromTax()` function to enable the users, who previously did not have to pay tax, to pay tax. 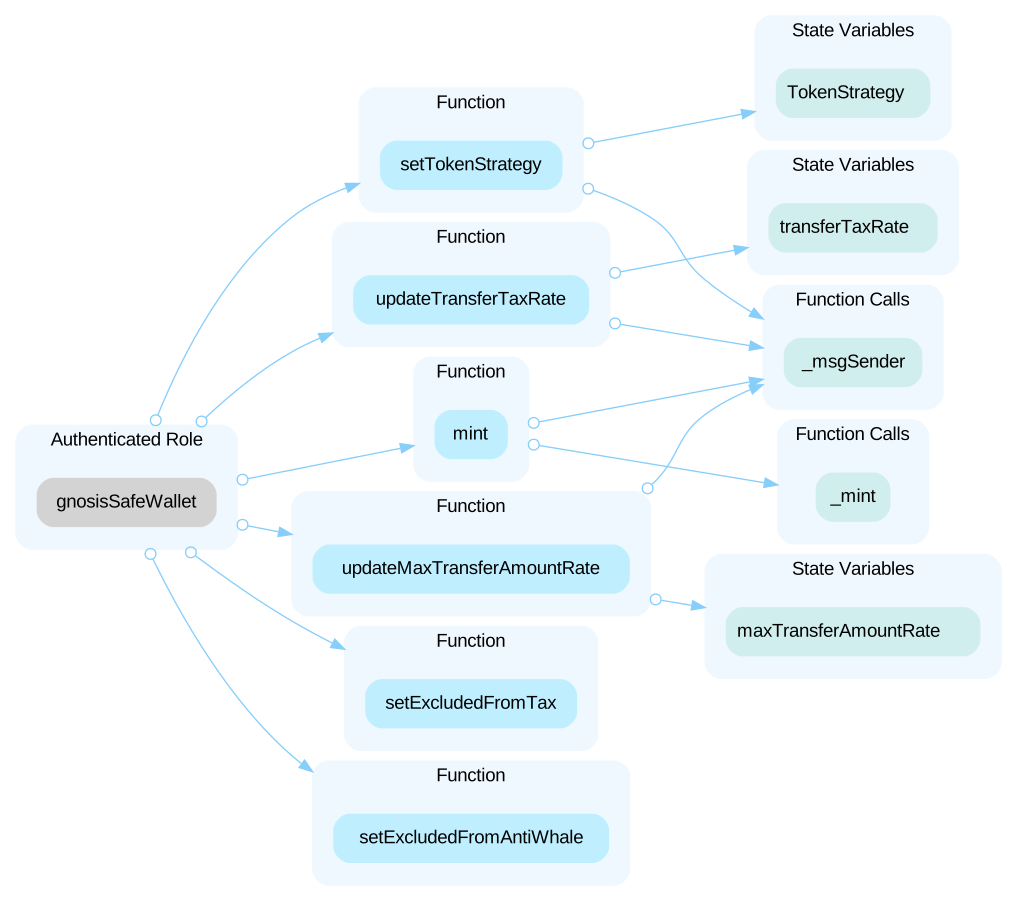
Open the reportThere is a `BURN_ADDRESS` variable in the contract, and every time tokens are burnt, it is checked whether the balance of the `BURN_ADDRESS` is above `MAX_BURN`. However, the `_burn()` function does not send or keep track of the burnt tokens.
Open the reportThe reports name a repository or files. Open a report to see its scope.
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="shopdi"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us