
Solidus Ai Tech security record
As of 30 Oct 2026, Solidus Ai Tech has 4 audit reports by 2 security firms on Trustblock; the latest is by CertiK, dated 12 Feb 2025. Those reports list no open critical findings. It also holds 1 deployed contract on 1 chain.
Record last updated . It holds audits and findings, contracts and incidents up to Oct 2026. Trustblock does not review code.
Audits4
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| Vision Makers | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
| SOLIDUS AI TECH / Gpu-Blockchain-Smartcontra | Security firm: Hacken | Date: | Scope: 1 address on BNB Chain | No open critical findings | Open · hacken.io |
| SOLIDUS AI TECH / ERC20 | Security firm: Hacken | Date: | Scope: 1 address on BNB Chain | No open critical findings | Open · hacken.io |
| Ai-Tech - Revised | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
Findings25
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 2 | 1 |
| Medium | 0 | 0 | 5 |
| Low | 2 | 4 | 10 |
HighCentralization RisksVision Makers · CertiK · 12 Feb 2025Acknowledged
In the contract `InvestmentPool`, the role `_projectfounder` has authority over the functions shown in the diagram below. Any compromise to the `_projectfounder` account may allow the hacker to take advantage of this authority and claim project funds after conditions are met. 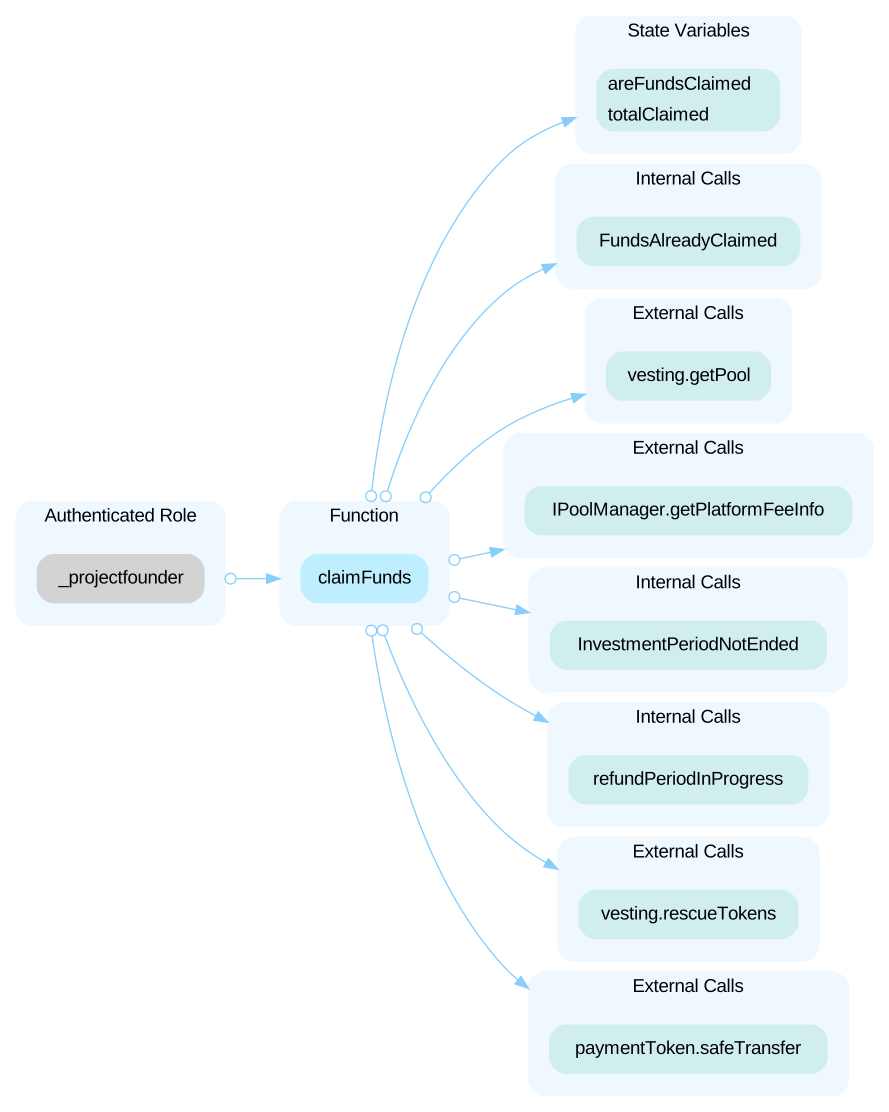 In the contract `LinearVestingPool`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and revoke a stream from a wallet address, update stream status, add a new or update existing stream, and mark a stream as refunded. Note that the `InvestmentPool` contract is supposed to have this `_owner` role, but depending on the contract deployment process, this assumption is not always guaranteed. 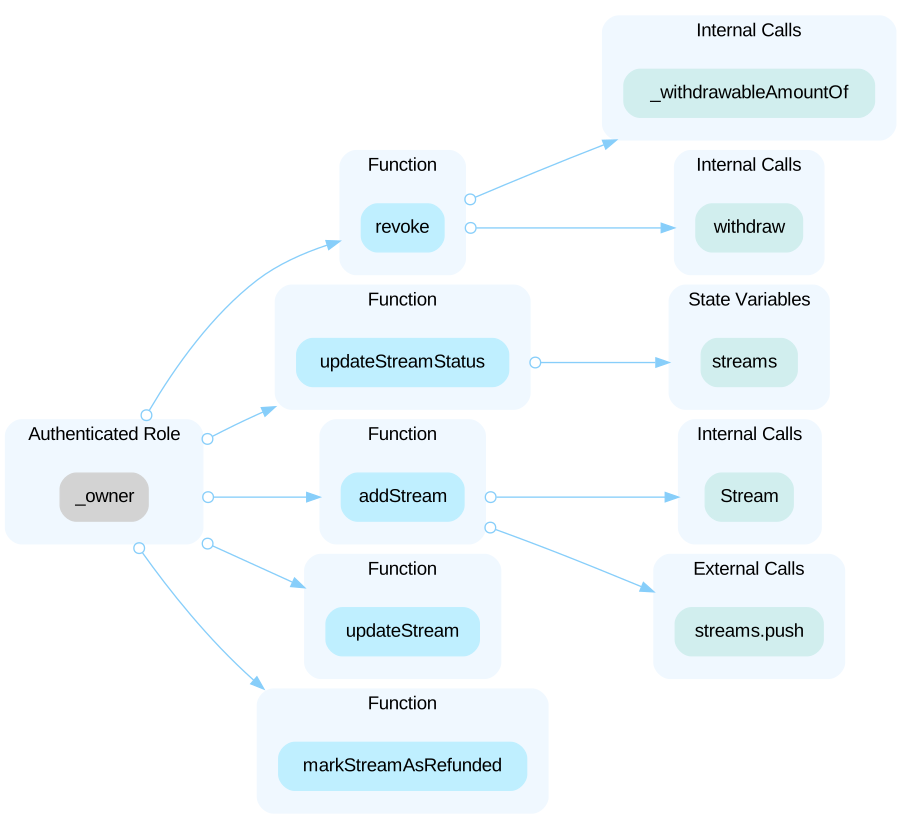 In the contract `PoolManager`, the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and update implementation addresses of the `InvestmentPool` and `LinearVestingPool` contracts, set pool manager role. 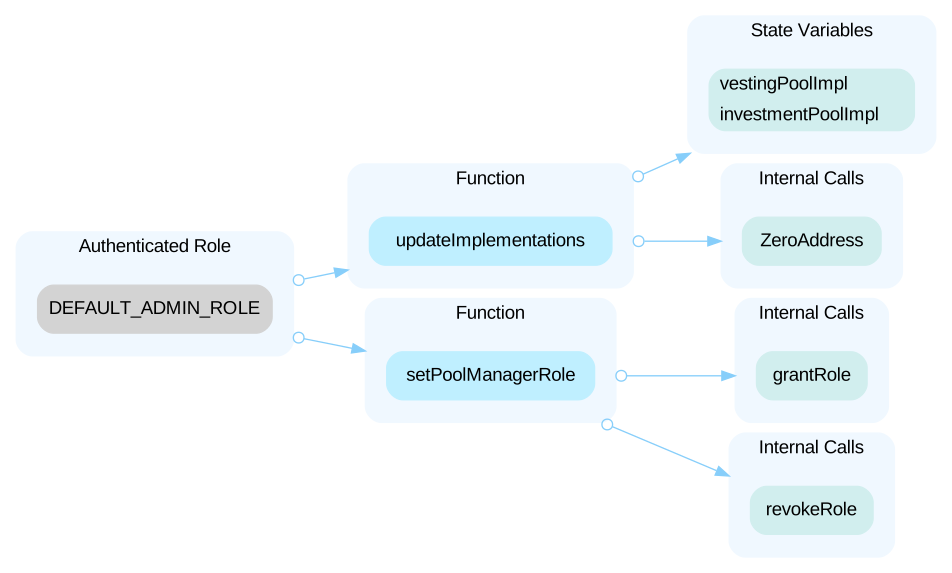 In the contract `PoolManager`, the role `MANAGER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MANAGER_ROLE` account may allow the hacker to take advantage of this authority and rescue tokens to a specified recipient and amount, deploy new investment and vesting pools, change the token for a specific pool, set the platform fee receiver, set investment pool configuration, and set the platform fee receiver address. 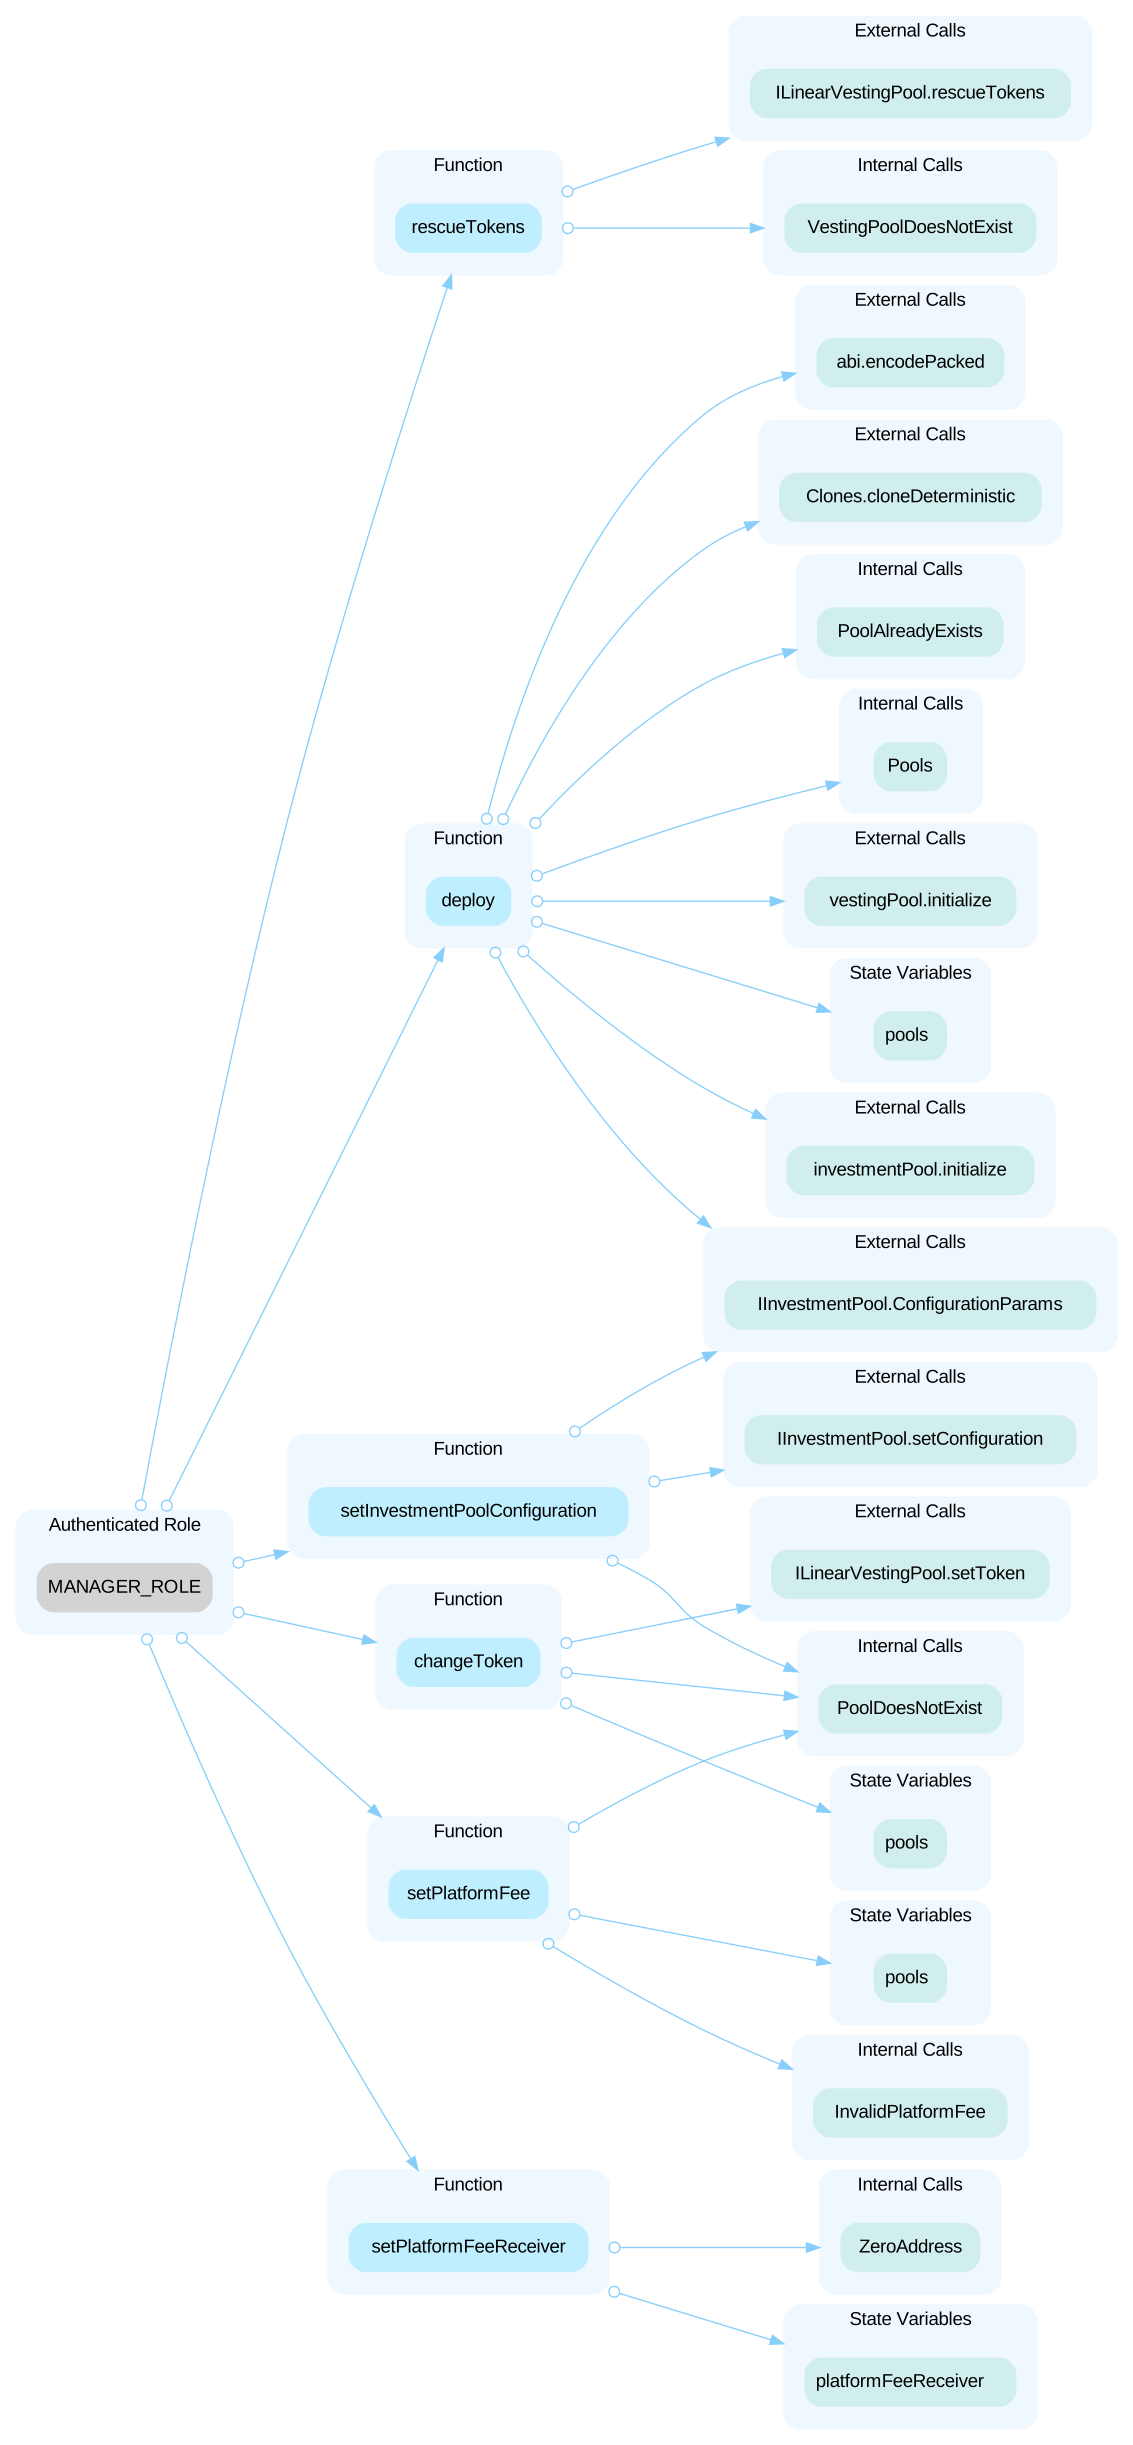
Open the reportHighCentralized Control of Contract UpgradeVision Makers · CertiK · 12 Feb 2025Acknowledged
In the contract `PoolManager`, the role `DEFAULT_ADMIN_ROLE` has the authority to update the implementation contract behind the `InvestmentPool` and `LinearVestingPool` contracts. The `PoolManager` contract itself is also upgradeable and could sit behind a proxy contract. Any compromise to the `DEFAULT_ADMIN_ROLE` account or the account that can upgrade the `PoolManager` contract may allow a hacker to take advantage of this authority and change the implementation contract pointed by the proxy and execute potentially malicious transactions.
Open the reportLowIncompatibility With Deflationary TokensVision Makers · CertiK · 12 Feb 2025Acknowledged
When transferring standard ERC20 deflationary tokens, the input amount may not be equal to the received amount due to the charged transaction fee. As a result, an inconsistency in the amount will occur and the transaction may fail due to the validation checks. The `InvestmentPool` contract implicitly assumes that the `paymentToken` is not a deflationary token.
Open the reportLowMissing Emit EventsVision Makers · CertiK · 12 Feb 2025Acknowledged
There should always be events emitted in the sensitive functions that are controlled by centralization roles.
Open the reportLowSolidity Version 0.8.23 Won't Work For All ChainsVision Makers · CertiK · 12 Feb 2025Acknowledged
Since Solidity Release 0.8.23, `MCOPY` opcode is introduced. However, this may not be compatible with all chains and L2s. As a result, the compatibility of the code could be affected.
Open the reportLowThird-Party Dependency UsageVision Makers · CertiK · 12 Feb 2025Acknowledged
The contract is serving as the underlying entity to interact with one or more third party protocols, and contain off chain components such as the construction of Merkle tree for token sale allocation. The tokens being sold/vested is also out of scope and its behavior and distribution is unknown to the auditor. The scope of the audit treats third party entities and off chain components as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc.
Open the reportContracts1
| Address | Chain | Source code |
|---|---|---|
| 0x2d060ef4d6bf7f9e5edde373ab735513c0e4f944 | Chain: BNB Chain | Source code: Verified source |
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="solidus-ai-tech"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us