
Starfish Finance audit reports
Starfish Finance has 2 public audit reports from CertiK; the latest is CertiK, 9 Dec 2022; no critical findings reported.
Last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Open findings across every firm11
Statuses are the security firms’ own
11 findings are still open or acknowledged in the firms’ reports: 3 high, 8 low (7 open, 4 acknowledged).
- High
- 3
- Low
- 8
- High Open
Centralization Related Risks
Starfish Finance Ⅲ · CertiK · 9 Dec 2022 · Report ↗
- High Open
Centralized Control of Contract Upgrade
Starfish Finance Ⅲ · CertiK · 9 Dec 2022 · Report ↗
- High Acknowledged
Centralization Related Risks
Starfish Finance · CertiK · 18 May 2022 · Report ↗
- Low Open
External Dependency
Starfish Finance Ⅲ · CertiK · 9 Dec 2022 · Report ↗
- Low Open
Incompatibility with Deflationary Tokens
Starfish Finance Ⅲ · CertiK · 9 Dec 2022 · Report ↗
- Low Open
Third Party Dependency
Starfish Finance Ⅲ · CertiK · 9 Dec 2022 · Report ↗
- Low Open
Unchecked ERC-20 `transfer()`/`transferFrom()` Ca
Starfish Finance Ⅲ · CertiK · 9 Dec 2022 · Report ↗
- Low Open
Variables That Could Be Declared as `Immutable`
Starfish Finance Ⅲ · CertiK · 9 Dec 2022 · Report ↗
- Low Acknowledged
External Dependencies
Starfish Finance · CertiK · 18 May 2022 · Report ↗
- Low Acknowledged
Improper Usage of public and external type
Starfish Finance · CertiK · 18 May 2022 · Report ↗
Audits2
Newest first
| Report | Security firm | Date | Scope | Critical findings | Findings | Source |
|---|---|---|---|---|---|---|
| Starfish Finance Ⅲ | Security firm: CertiK | Date: | Scope: Files listed | None open | Findings: 2 high · 2 medium · 11 low 8 fixed · 7 open | skynet.certik.com ↗ |
| Starfish Finance | Security firm: CertiK | Date: | Scope: Files listed | None open | Findings: 1 high · 3 low 4 acknowledged | skynet.certik.com ↗ |
Findings19
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 1 | 0 |
| Medium | 0 | 0 | 2 |
| Low | 5 | 3 | 6 |
HighCentralization Related RisksStarfish Finance Ⅲ · CertiK · 9 Dec 2022Open
In the contract `LiquidStaking.sol` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and: * Set the contract's staking/unstaking transaction fee to any value with function `setTransactionFee()`. An extremely high transaction fee could cause staking to transfer a majority of the `dot` tokens to the `feeCollector` address, and prevent user's from staking/unstaking. 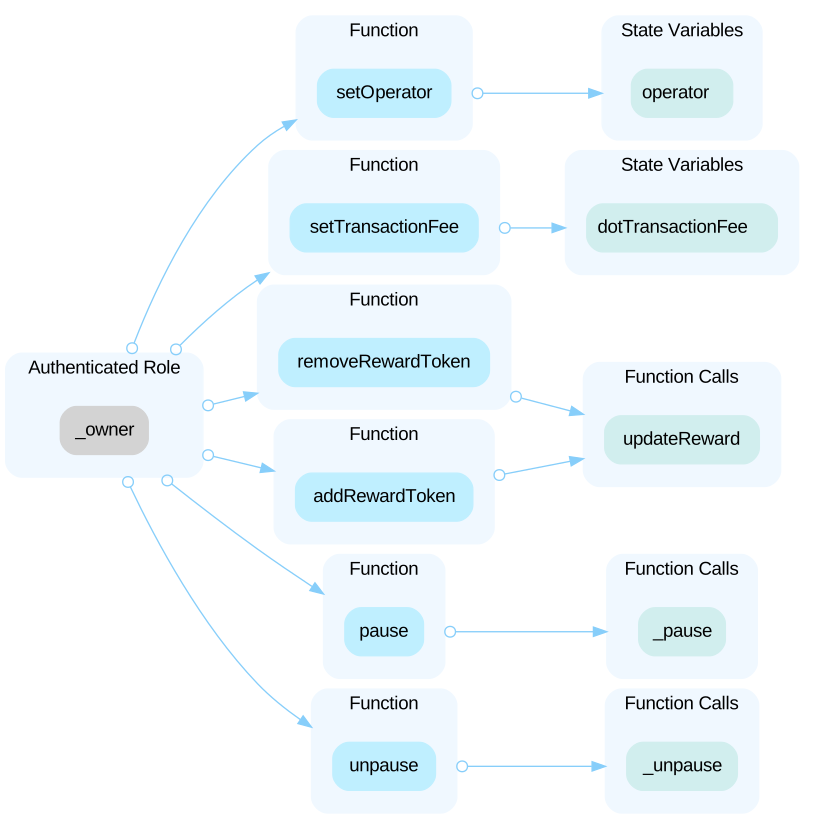 --- In the contract `LiquidStaking.sol` the role `operator` has authority over the following functions: * `withdrawPendingBond()` - Withdraws all staked `dot` out of contract. * `depositUnbonded()` Any compromise to the `operator` account may allow the hacker to take advantage of this authority and: * Transfer all of the staking `dot` tokens out of the contract to the `operator` address.
Open the reportHighCentralized Control of Contract UpgradeStarfish Finance Ⅲ · CertiK · 9 Dec 2022Open
`LiquidStaking.sol` is an upgradeable contract and the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, they can change the implementation of the contract and drain tokens from the contract.
Open the reportLowExternal DependencyStarfish Finance Ⅲ · CertiK · 9 Dec 2022Open
The implementation of contract `DataTypes` is unknown and not in the audit scope. The scope of this audit would treat the external dependency entity as black boxes and assume functional correctness.
Open the reportLowIncompatibility with Deflationary TokensStarfish Finance Ⅲ · CertiK · 9 Dec 2022Open
When transferring deflationary ERC-20 tokens, the input amount may not be equal to the received amount due to the charged transaction fee. For example, if a user sends 100 deflationary tokens (with a 10% transaction fee), only 90 tokens actually arrived to the contract. However, a failure to discount such fees may allow the same user to withdraw 100 tokens from the contract, which causes the contract to lose 10 tokens in such a transaction. --- - The `pendingBondUser[]` array is used for bookkeeping purposes without compensating for the potential transfer fees. ```solidity=120 DataTypes.PendingBondUser memory pendingBondUser = DataTypes.PendingBondUser(_msgSender(), _amountMinusFee); pendingBondUsers.push(pendingBondUser); ``` - Transferring `dot` token amount `_amountMinusFee` into the contract. ```solidity=129 dot.transferFrom(_msgSender(), address(this), _amountMinusFee); ``` --- - The amount to unstake is then retrieved from the `pendingBondUser[]` array, which did not compensate for the potential transfer fees. ```solidity function unstake(uint256 _amount) public { ... uint256 instantUnstakeAmount = pendingBondUsers[i].amount; ... dot.transfer(_msgSender(), instantUnstakeAmount); ... ``` Reference: https://thoreum-finance.medium.com/what-exploit-happened-today-for-gocerberus-and-garuda-also-for-lokum-ybear-piggy-caramelswap-3943ee23a39f
Open the reportLowThird Party DependencyStarfish Finance Ⅲ · CertiK · 9 Dec 2022Open
The contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assume their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=39 IERC20Plus public dot; ``` - The contract `LiquidStaking.sol` interacts with a third party contract with the `IERC20Plus` interface via address `dot`.
Open the reportLowUnchecked ERC-20 `transfer()`/`transferFrom()` CaStarfish Finance Ⅲ · CertiK · 9 Dec 2022Open
The return value of the `transfer()`/`transferFrom()` calls are not checked. ```solidity=129 dot.transferFrom(_msgSender(), address(this), _amountMinusFee); ``` --- ```solidity=131 dot.transferFrom(_msgSender(), feeCollector, dotTransactionFee); ``` --- ```solidity=191 dot.transfer(_msgSender(), instantUnstakeAmount); ``` --- ```solidity=203 dot.transfer(_msgSender(), _amount); ``` --- ```solidity=230 dot.transfer(_msgSender(), currClaimableUnbondedAmount); ``` --- ```solidity=262 dot.transfer(_msgSender(), lastTotalPendingBondAmount); ``` --- ```solidity=279 dot.transferFrom(_msgSender(), address(this), _amountMinusFee); ``` --- ```solidity=281 dot.transferFrom(_msgSender(), feeCollector, dotTransactionFee); ```
Open the reportLowVariables That Could Be Declared as `Immutable`Starfish Finance Ⅲ · CertiK · 9 Dec 2022Open
The linked variables assigned in the constructor can be declared as `immutable`. Immutable state variables can be assigned during contract creation but will remain constant throughout the lifetime of a deployed contract. A big advantage of immutable variables is that reading them is significantly cheaper than reading from regular state variables since they will not be stored in storage.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Starfish Finance: questions
Is Starfish Finance audited?
Trustblock holds 2 public audit reports for Starfish Finance, dated 18 May 2022 to 9 Dec 2022. The latest is by CertiK (“Starfish Finance Ⅲ”).
Who audited Starfish Finance?
CertiK wrote the 2 reports Trustblock holds for Starfish Finance.
Are there open findings in Starfish Finance’s audits?
11 findings are still open or acknowledged in the firms’ reports: 3 high, 8 low (7 open, 4 acknowledged). No critical finding is reported. Statuses are the security firms’ own.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="starfish-finance"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us