
TrueUSD audit reports
TrueUSD has 1 public audit report from CertiK; dated 7 Feb 2023; no critical findings reported.
Last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Open findings across every firm8
Statuses are the security firms’ own
8 findings are still open or acknowledged in the firms’ reports: 5 high, 3 low (all open).
- High
- 5
- Low
- 3
- High Open
Centralization Risks in AllowanceSheet.sol
TrueUSD - TUSD · CertiK · 7 Feb 2023 · Report ↗
- High Open
Centralization Risks in BalanceSheet.sol
TrueUSD - TUSD · CertiK · 7 Feb 2023 · Report ↗
- High Open
Centralization Risks in ModularBasicToken.sol
TrueUSD - TUSD · CertiK · 7 Feb 2023 · Report ↗
- High Open
Centralization Risks in ModularMintableToken.sol
TrueUSD - TUSD · CertiK · 7 Feb 2023 · Report ↗
- High Open
Centralization Risks in ModularStandardToken.sol
TrueUSD - TUSD · CertiK · 7 Feb 2023 · Report ↗
- Low Open
Inefficient Memory Parameter
TrueUSD - TUSD · CertiK · 7 Feb 2023 · Report ↗
- Low Open
Solidity Version Not Recommended
TrueUSD - TUSD · CertiK · 7 Feb 2023 · Report ↗
- Low Open
Unlocked Compiler Version
TrueUSD - TUSD · CertiK · 7 Feb 2023 · Report ↗
Audits1
Newest first
| Report | Security firm | Date | Scope | Critical findings | Findings | Source |
|---|---|---|---|---|---|---|
| TrueUSD - TUSD | Security firm: CertiK | Date: | Scope: Files listed | None open | Findings: 5 high · 3 low 8 open | skynet.certik.com ↗ |
Findings8
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 5 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 3 | 0 | 0 |
HighCentralization Risks in AllowanceSheet.solTrueUSD - TUSD · CertiK · 7 Feb 2023Open
In the contract `AllowanceSheet` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify the allowances of any user. 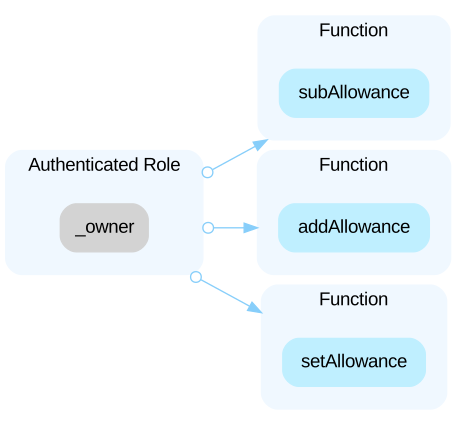
Open the reportHighCentralization Risks in BalanceSheet.solTrueUSD - TUSD · CertiK · 7 Feb 2023Open
In the contract `BalanceSheet` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change the balances of the token, effectively stealing tokens from any user. 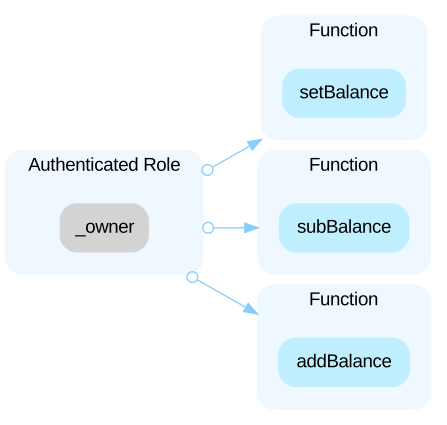
Open the reportHighCentralization Risks in ModularBasicToken.solTrueUSD - TUSD · CertiK · 7 Feb 2023Open
In the contract `ModularBasicToken` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change the balance sheet used by the token. 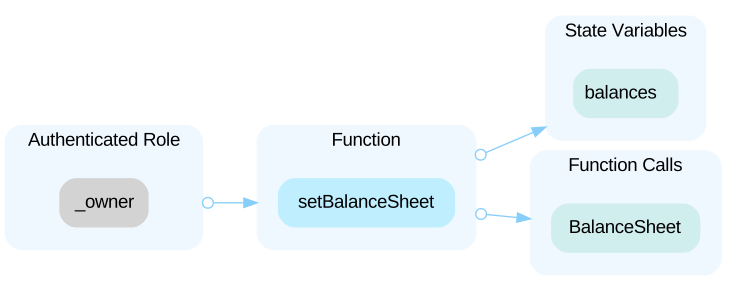
Open the reportHighCentralization Risks in ModularMintableToken.solTrueUSD - TUSD · CertiK · 7 Feb 2023Open
In the contract `ModularMintableToken` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and mint as many tokens as desired, as there is no upper limit for the number of minted tokens. 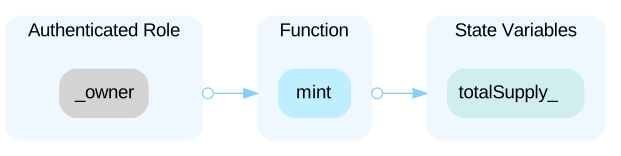
Open the reportHighCentralization Risks in ModularStandardToken.solTrueUSD - TUSD · CertiK · 7 Feb 2023Open
In the contract `ModularStandardToken` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change the allowance sheet used by the token. 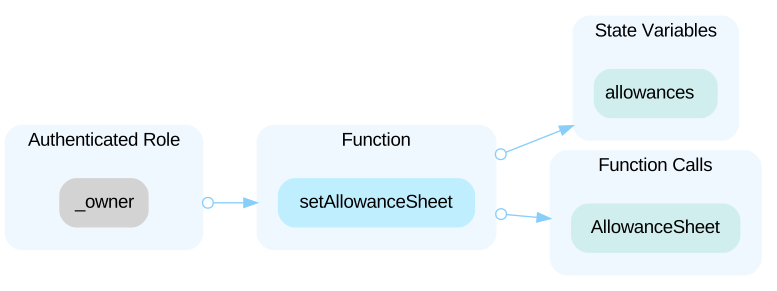
Open the reportLowInefficient Memory ParameterTrueUSD - TUSD · CertiK · 7 Feb 2023Open
One or more parameters with `memory` data location are never modified in their functions and those functions are never called internally within the contract. Thus, their data location can be changed to `calldata` to avoid the gas consumption copying from calldata to memory. ```solidity=17 function burn(uint256 _value, string _note) public returns(bool) { ``` `burn` has memory location parameters: `_note`.
Open the reportLowSolidity Version Not RecommendedTrueUSD - TUSD · CertiK · 7 Feb 2023Open
Solidity frequently releases new compiler versions. Using an old version prevents access to new Solidity security features. Also, recent versions may be too early to be trusted.
Open the reportLowUnlocked Compiler VersionTrueUSD - TUSD · CertiK · 7 Feb 2023Open
The contracts cited have an unlocked compiler version. An unlocked compiler version in the source code of the contract permits the user to compile it at or above a particular version. This, in turn, leads to differences in the generated bytecode between compilations due to differing compiler version numbers. This can lead to ambiguity when debugging, as compiler specific bugs may occur in the codebase that would be hard to identify over a span of multiple compiler versions rather than a specific one.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
TrueUSD: questions
Is TrueUSD audited?
Trustblock holds 1 public audit report for TrueUSD, dated 7 Feb 2023. The latest is by CertiK (“TrueUSD - TUSD”).
Who audited TrueUSD?
CertiK wrote the report Trustblock holds for TrueUSD.
Are there open findings in TrueUSD’s audits?
8 findings are still open or acknowledged in the firms’ reports: 5 high, 3 low (all open). No critical finding is reported. Statuses are the security firms’ own.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="trueusd"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us