
UNO.farm security record
As of 14 Oct 2026, UNO.farm has 1 audit report on Trustblock, by CertiK, dated 12 Sep 2022. That report lists no open critical findings.
Record last updated . It holds audits and findings, contracts and incidents up to Oct 2026. Statuses are the security firms’ own. Trustblock does not review code.
Audits1
Newest first
Findings17
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 3 | 0 | 0 |
| Medium | 1 | 0 | 2 |
| Low | 3 | 0 | 8 |
HighCentralization Related RisksUno · CertiK · 12 Sep 2022Not fixed
In the contract `UnoFarmBalancer`, `UnoFarmQuickswapDual`, `UnoFarmQuickswap`, `UnoFarmSushiswap` and `UnoFarmTrisolarisStandard` the role `assetRouter` has authority over the functions shown in the diagram below. Any compromise to the `assetRouter` account may allow the hacker to take advantage of this authority: - deposit tokens from this contract's balance to the vault through `deposit()` - withdraw funds and sends them to the recipient through `withdraw()` - claim rewards and re-investing rewards through `distribute()` 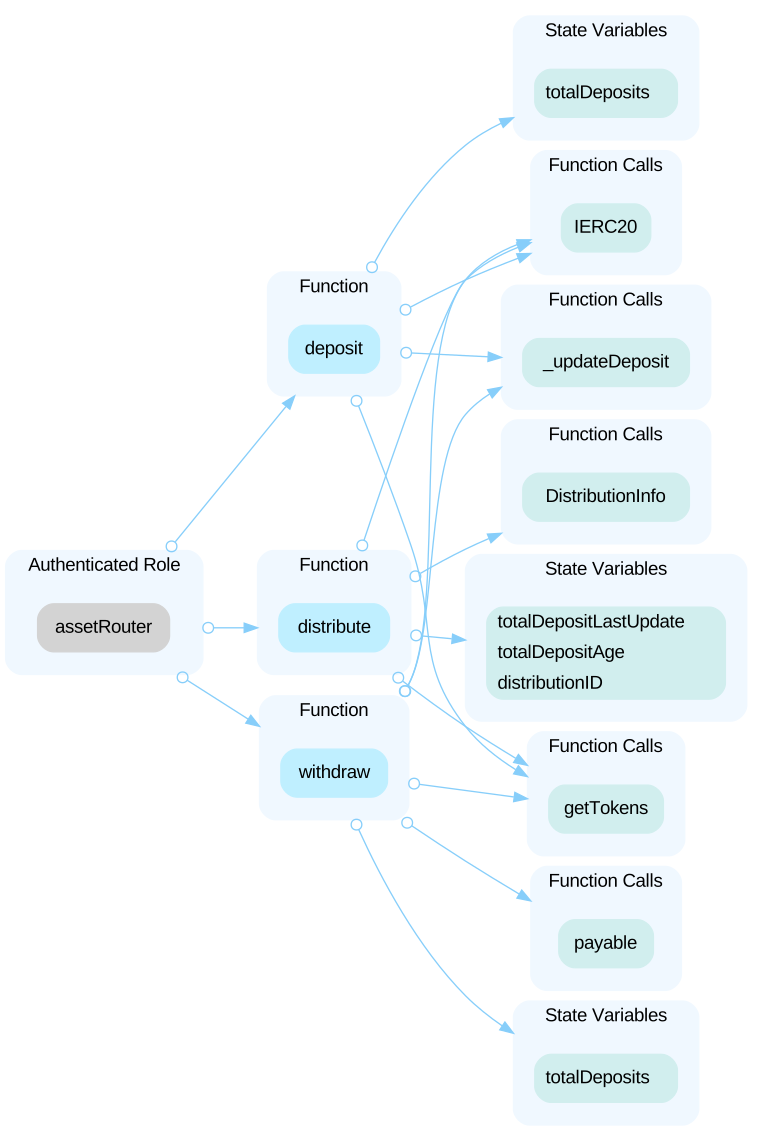
Open the reportHighCentralization Related RisksUno · CertiK · 12 Sep 2022Not fixed
To bridge the gap in trust between the administrators need to express a sincere attitude regarding the consideration of the administrator teamʼs anonymity. The `admin` of `UnoAutoStrategyFactory` has the responsibility to notify users about the following capabilities: - approve an address for use as an AssetRouter through `approveAssetRouter()` - revoke Asset Router approval from an address through `revokeAssetRouter()` - upgrade all AutoStrategy contracts to a new implementation using Beacon Proxy through `upgradeStrategies()` The `pauser` of `UnoAutoStrategyFactory`, `UnoAssetRouterTrisolarisStandard` and `UnoAssetRouterTrisolarisStable` have the responsibility to notify users about the following capabilities: - pause the contract through `pause()` - unpause the contract through `unpause()` The `admin` of `UnoAccessManager` has the responsibility to notify users about the following capabilities: - grant role to account through `grantRole()` - revoke a role from the account through `revokeRole()` The `ADMIN_ROLE` of `UnoFarmFactory` has the responsibility to notify users about the following capabilities: - upgrade farms through `upgradeFarms()`
Open the reportHighCentralized Control of Contract UpgradeUno · CertiK · 12 Sep 2022Not fixed
The contracts mentioned above are upgradeable contracts, the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, he can change the implementation of the contract and drain tokens from the contract.
Open the reportMediumCentralization Related Risks Of `LIQUIDITY_MANAGEUno · CertiK · 12 Sep 2022Not fixed
To bridge the gap in trust between the administrators need to express a sincere attitude regarding the consideration of the administrator teamʼs anonymity. The `LIQUIDITY_MANAGER_ROLE` of `UnoAutoStrategy` has the responsibility to notify users about the following capabilities: - move liquidity from one pool to another through `moveLiquidity()`
Open the reportLowLack of Storage GapUno · CertiK · 12 Sep 2022Not fixed
For upgradeable contracts, there must be storage gap to "allow developers to freely add new state variables in the future without compromising the storage compatibility with existing deployments". Otherwise it may be very difficult to write new implementation code. Without storage gap, the variable in child contract might be overwritten by the upgraded base contract if new variables are added to the base contract. Refer to https://docs.openzeppelin.com/upgrades-plugins/1.x/writing-upgradeable We noticed that there are several contracts that inherits upgradable contracts, but do not have storage gap.
Open the reportLowLogical issue about the leftoverUno · CertiK · 12 Sep 2022Not fixed
If the function `moveLiquidity()` is called by the LIQUIDITY_MANAGER_ROLE and the user does not retrieve the leftover tokens in the contract in time, then when the LIQUIDITY_MANAGER_ROLE calls `moveLiquidity()` again, this part of the user's unretrieved assets will be invested again in the new pool which will be shared with other users.
Open the reportLowThird Party DependencyUno · CertiK · 12 Sep 2022Not fixed
The contracts mentioned above serves as the underlying entity to interact with one or more third-party protocols. The scope of the audit treats third-party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised, which may lead to lost or stolen assets. In addition, third parties' upgrades can create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="uno-farm"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us