
VON security record
As of 23 Oct 2026, VON has 1 audit report on Trustblock, by CertiK, dated 29 Nov 2024. That report lists no open critical findings.
Record last updated . It holds audits and findings, contracts and incidents up to Oct 2026. Trustblock does not review code.
Audits1
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| Vameon - Audit 1 | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
Findings4
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 1 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 0 | 2 |
HighCentralization Risks in Vameon.solVameon - Audit 1 · CertiK · 29 Nov 2024Fixed
In the contract `Vameon` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change fee receive address or trust forwarder address. 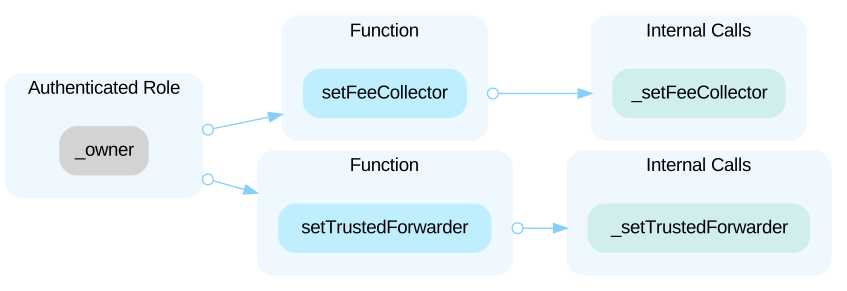
Open the reportLowIntended usage of `transferWithFee`Vameon - Audit 1 · CertiK · 29 Nov 2024Fixed
`transferWithFee` requires `_msgSender` to pay a fee to fee collector to perform a transaction. From a user's perspective, they can use `transfer` function instead of `transferWithFee` to avoid fees.
Open the reportLowUnknown implementation of trustedForwarderVameon - Audit 1 · CertiK · 29 Nov 2024Fixed
The variable `_trustedForwarder` serves as a 3rd party forwarder to help the `ERC2771Recipient` identify the address of the transaction signer. `BaseToken` and `MeldToken` inherit `ERC2771Recipient`, which decodes the `msg.sender` from `msg.data` when called from the forwarder by overriding the `_msgSender()` function. A malicious forwarder may forge the value of _msgSender() and effectively send transactions from any address. The scope of the audit treats these 3rd party forwarders as black boxes and assumes their functional correctness. However, in the real world, 3rd parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of 3rd parties can possibly create severe impacts. In this project, a compromised trust forwarder can transfer tokens out of any user's address, which imposes a critical risk. The trust forwarder address is set by the owner of the contract. Reference: [EIP-2771](https://eips.ethereum.org/EIPS/eip-2771)
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="vameon"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us