
WFCA Infrastructure security record
As of 3 Nov 2026, WFCA Infrastructure has 1 audit report on Trustblock, by CertiK, dated 14 Sep 2023. That report lists no open critical findings. It also holds 1 deployed contract on 1 chain.
Record last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Audits1
Newest first
Findings4
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 3 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 1 | 0 |
HighCentralization Related RisksWfca · CertiK · 14 Sep 2023Acknowledged
In the contract `TokenERC20` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and set critical variables. 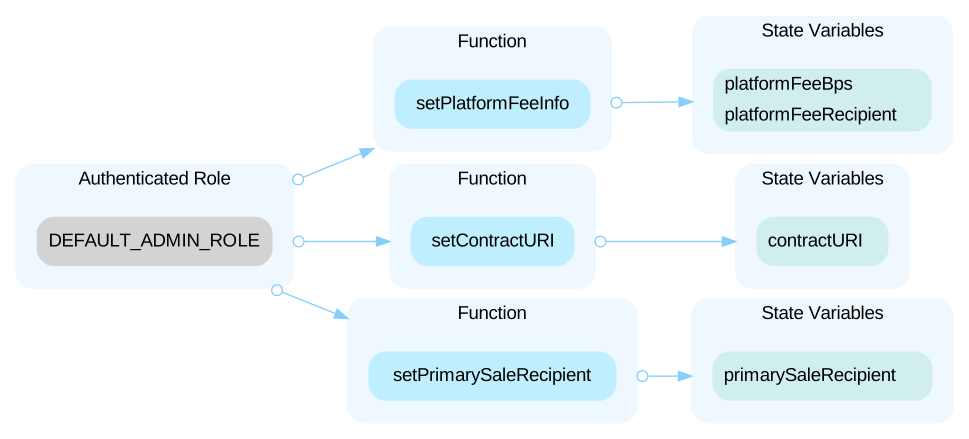 --- In the contract `TokenERC20` the role `MINTER_ROLE` has authority over the function shown in the diagram below. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this authority and mint tokens. 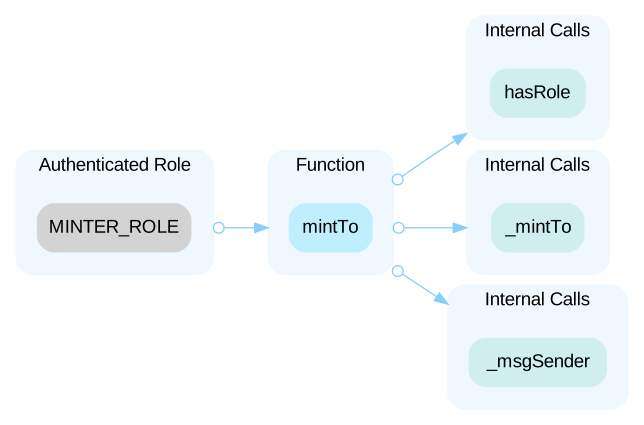 --- In the contract `AccessControlUpgradeable` the role `adminRole` has authority over the following functions: - grantRole() - revokeRole() Any compromise to the `adminRole` account may allow the hacker to take advantage of this authority and grant associated role to any account or revoke the role from any account. Note that `DEFAULT_ADMIN_ROLE` is the admin role for all roles. --- In the contract `AccessControlUpgradeable` the role `role` has authority over the following function: - renounceRole() Any compromise to the `role` account may allow the hacker to take advantage of this authority and renounce corresponding privileges to functions within other contracts.
Open the reportHighCentralization Related Risks in `_trustedForwardeWfca · CertiK · 14 Sep 2023Acknowledged
The `TokenERC20` contract inherits from the `ERC2771ContextUpgradeable` contract. This design enables designated accounts, known as `_trustedForwarders`, to execute calls on behalf of any other account. If a `_trustedForwarder` is compromised, it could allow unauthorized actions on the contract, including operations associated with the `DEFAULT_ADMIN_ROLE`. Reference: [EIP-2771](https://eips.ethereum.org/EIPS/eip-2771)
Open the reportHighCentralized Token Holding Position RiskWfca · CertiK · 14 Sep 2023Acknowledged
On Sep 12, 2023, the addresses 0x4955b9aCfBAe877295965B73d08BD679D30fDa2e and 0x97224595072094aA8a2730cbB4261D42c70ab378 have all the WFCA tokens. This is a centralization risk because these addresses can distribute tokens without obtaining the consensus of the community. Any compromise to the addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
Open the reportLowMissing Zero Address ValidationWfca · CertiK · 14 Sep 2023Acknowledged
Addresses are not validated before assignment or external calls, potentially allowing the use of zero addresses and leading to unexpected behavior or vulnerabilities. For example, transferring tokens to a zero address can result in a permanent loss of those tokens. ```solidity=94 primarySaleRecipient = _primarySaleRecipient; ``` - `_primarySaleRecipient` is not zero-checked before being used. --- ```solidity=95 platformFeeRecipient = _platformFeeRecipient; ``` - `_platformFeeRecipient` is not zero-checked before being used. --- ```solidity=179 primarySaleRecipient = _saleRecipient; ``` - `_saleRecipient` is not zero-checked before being used. --- ```solidity=191 platformFeeRecipient = _platformFeeRecipient; ``` - `_platformFeeRecipient` is not zero-checked before being used.
Open the reportContracts1
| Address | Chain | Source code |
|---|---|---|
| 0x28bd01e51a9f6b47d7826c6e1d8a0fbbf57fc2a0 | Chain: Ethereum | Source code: Verified source |
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="wfca"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us