As of 25 Oct 2026, XShares has 1 audit report on Trustblock, by CertiK, dated 5 Sep 2023. That report lists no open critical findings.
Record last updated . It holds audits and findings, contracts and incidents up to Oct 2026. Trustblock does not review code.
Newest first
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 1 |
| High | 0 | 3 | 0 |
| Medium | 0 | 1 | 0 |
| Low | 0 | 3 | 1 |
In the contract `XSharesSharesV1` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify important configurations of the contract, such as the fee amount and fee destination. 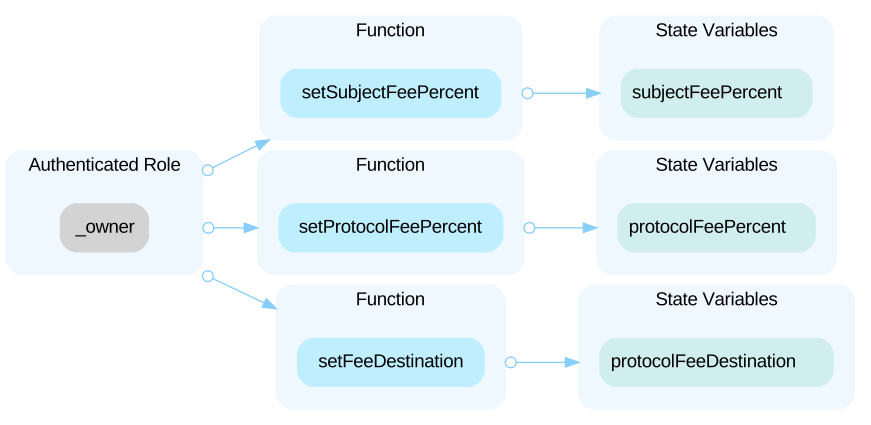
Open the reportThe “XSharesSharesV2” contract inherits upgradeable contracts, indicating that it’s part of an upgradeable system. Upgradeable contracts often pair with a proxy contract responsible for managing contract upgrades. The `admin` of the proxy has the authority to update the implementation contract (i.e., the XSharesSharesV2 contract). Any compromise of the admin account could allow a hacker to exploit this authority, potentially altering the implementation contract pointed to by the proxy, and thus executing malicious functionality within the implementation contract.
Open the reportThere are no upper boundaries for **setProtocolFeePercent** and **setSubjectFeePercent** function which is used to modify the protocol fee and subject fee. It is possible to set the total fee rate up to any arbitrary amount.
Open the reportThe contract requires the "sharesSubject" to have at least 1 share after the registration. The last share of the "sharesSubject" will become unsellable. It's possible for a regular user's share to become unsellable, and the user will lose its assets. ```sol require(supply > amount, "Cannot sell the last share"); ```
Open the reportThe smart contract contains one or more state changes related to arithmetic operations that do not emit events to communicate the changes outside the blockchain, which can lead to difficulties in tracking or verifying these changes and may affect the contract's transparency and auditability. ```solidity=147 protocolFeePercent = _feePercent; ``` --- ```solidity=151 subjectFeePercent = _feePercent; ```
Open the reportThe "register" function allows an EOA or smart contract to register a "sharesSubject." When selling or buying shares, the "sharesSubject" address needs to receive native tokens. If the "sharesSubject" is malicious or has incorrectly implemented the payment receive feature, it can cause the "XSharesSharesV2" to malfunction. The implementation of all the "sharesSubject" instances is out of the scope of the audit.
Open the reportOne or more logic contracts do not protect their initializers. An attacker can call the initializer and assume ownership of the logic contract, whereby she can perform privileged operations that trick unsuspecting users into believing that she is the owner of the upgradeable contract. ```solidity=6 contract XSharesSharesV2 is OwnableUpgradeable { ``` - `XSharesSharesV2` is an upgradeable contract that does not protect its initializer. ```solidity=23 function initialize() public initializer { ``` - `initialize` is an unprotected initializer function.
Open the reportThe reports name a repository or files. Open a report to see its scope.
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="xshares"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us