
ZAH Cards security record
As of 3 Nov 2026, ZAH Cards has 1 audit report on Trustblock, by CertiK, dated 6 Oct 2022. That report lists no open critical findings. It also holds 1 deployed contract on 1 chain.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Audits1
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| Zahnymous LTD | Security firm: CertiK | Date: | Scope: 1 address on BNB Chain | No open critical findings | Open · skynet.certik.com |
Findings13
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 2 | 0 | 8 |
HighCentralization Risks in ZAH.solZahnymous LTD · CertiK · 6 Oct 2022Open
In the contract `ZAH` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and: - activate trading prematurely - update the `marketingWallet` and `devWallet` addresses to their own, set fee rates to their maximum, and increase `swapTokensAtAmount` to a large amount, stealing fee funds not designated for them on each `swapBack()` call - exclude their own address from needing to pay fees, giving themselves favorable trading benefits - remove previously added automated market maker pair contract addresses - disable swapping without good reason 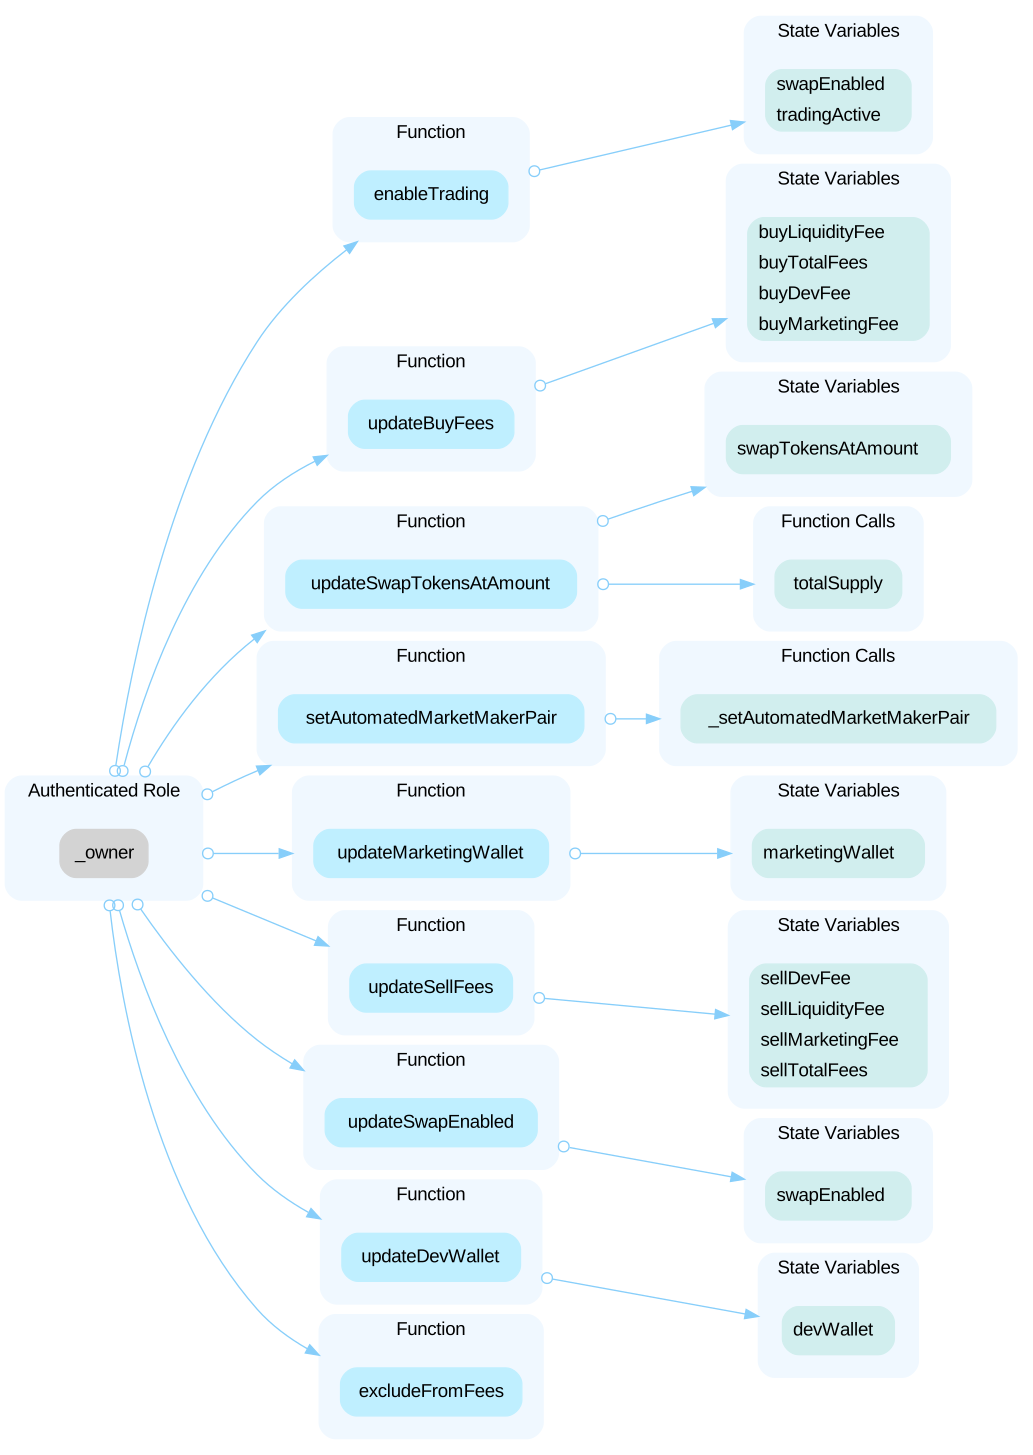
Open the reportHighInitial Token DistributionZahnymous LTD · CertiK · 6 Oct 2022Open
All of the ZAH tokens are sent to the contract deployer when deploying the contract. This could be a centralization risk as the deployer can distribute ZAH tokens without obtaining the consensus of the community.
Open the reportLowERC20 Approval Race ConditionZahnymous LTD · CertiK · 6 Oct 2022Open
The approval function of the ERC20 standard possesses a well-known vulnerability whereby two consecutive approvals can be exploited to instead “reset” the approval by consuming the approval that is meant to be replaced with a new one. ```solidity=514 function _approve(address owner, address spender, uint256 amount) private { require(owner != address(0), "ERC20: approve from the zero address"); require(spender != address(0), "ERC20: approve to the zero address"); _allowances[owner][spender] = amount; emit Approval(owner, spender, amount); } ```
Open the reportLowThird Party DependencyZahnymous LTD · CertiK · 6 Oct 2022Open
The contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assume their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=951 IUniswapV2Router02 public immutable uniswapV2Router; ``` - The contract `ZAH` interacts with third party contract with `IUniswapV2Router02` interface via `uniswapV2Router`.
Open the reportContracts1
| Address | Chain | Source code |
|---|---|---|
| 0xa78cc657877406b17f6ff9c7a3f10401d1a89cfb | Chain: BNB Chain | Source code: Verified source |
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="zahnymous"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us