0xa56ba554a859a011f8b10c87319f7774f534f4e0
As of 21 Nov 2026, Trustblock’s record holds 0xa56ba554a859a011f8b10c87319f7774f534f4e0 on BNB Chain as a contract of SolarX. 1 audit report on Trustblock lists this address: CertiK, 26 Mar 2024. 4 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| SolarX - Audit Addendum | CertiK | Not recorded (see the report) | Open |
2 High, 2 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `SolarX` the role `MINTER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this authority and mint tokens to any address and burn tokens from themselves. Note there's a 700,000,000 * 10 ** 18 `MAX_TOTAL_SUPPLY` cap. 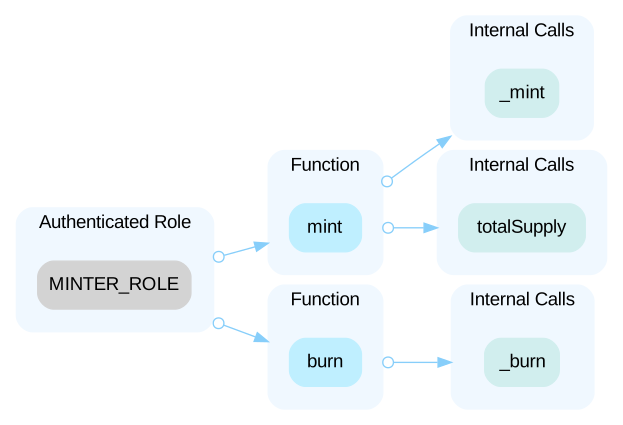 In the contract `SolarX` the role `PAUSER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `PAUSER_ROLE` account may allow the hacker to take advantage of this authority and pause/unpause the contract. 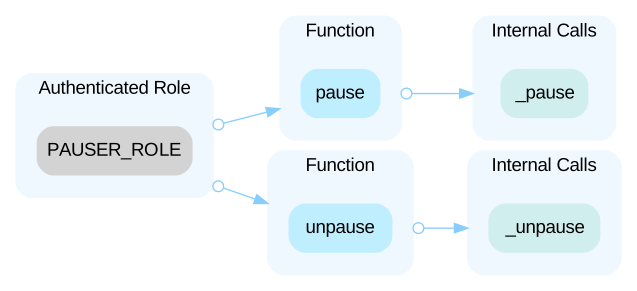 In the contract `SolarX` the role `UPDATER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `UPDATER_ROLE` account may allow the hacker to take advantage of this authority and set critical state variables. 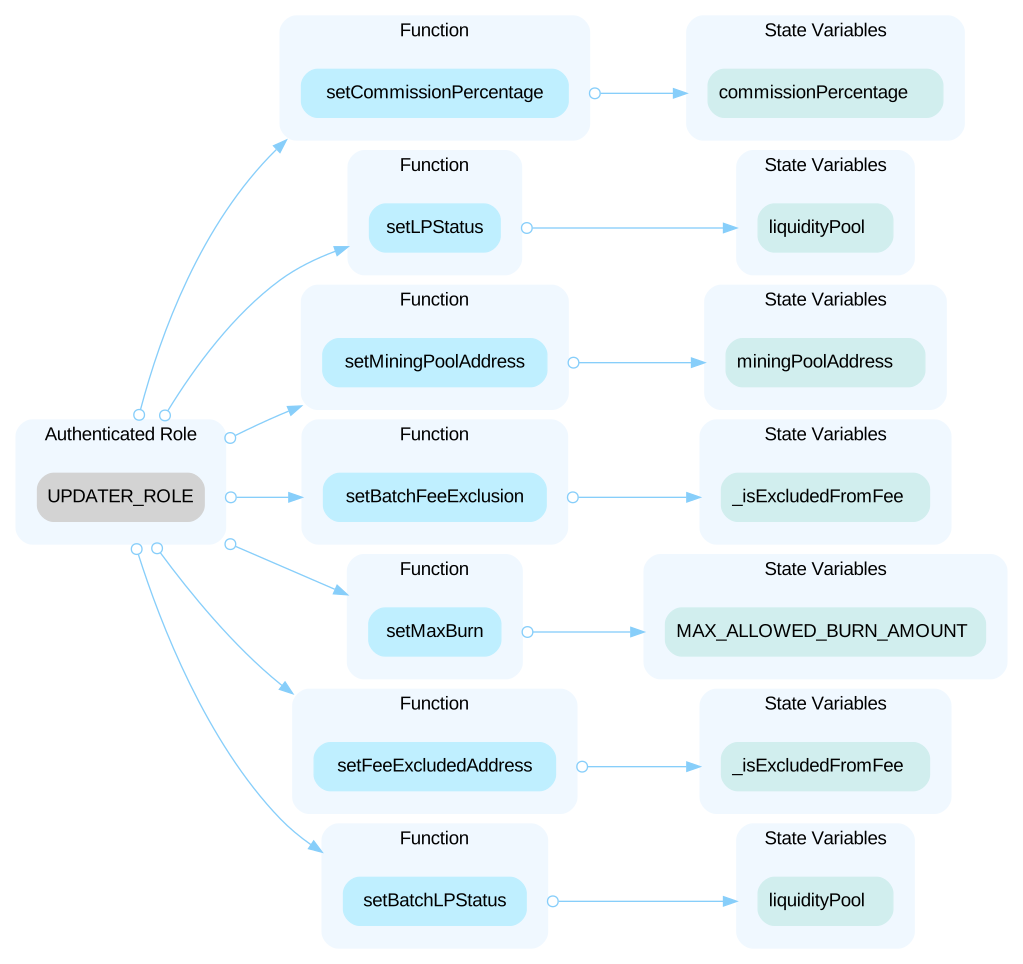 --- In the contract `AccessControl` the role `adminRole` has authority over the following functions: - grantRole() - revokeRole() Any compromise to the `adminRole` account may allow the hacker to take advantage of this authority and grant associated role to any account or revoke the role from any account. Note that `DEFAULT_ADMIN_ROLE` is the admin role for all roles. In the contract `AccessControl` the role `role` has authority over the following function: - renounceRole() Any compromise to the `role` account may allow the hacker to take advantage of this authority and renounce corresponding privileges to functions within other contracts.
The audit on Trustblock · Open the reportAll of the SolarX tokens are sent to the contract deployer. This is a centralization risk because the deployer can distribute tokens without obtaining the consensus of the community. Any compromise to the address may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
The audit on Trustblock · Open the reportIn the contract, comments within the `mint()` and `burn()` functions indicate that these functions should be called by the `UPDATER_ROLE`. However, the actual implementation restricts these functions to be called by the `MINTER_ROLE`.
The audit on Trustblock · Open the reportThe function `transfer()` has the restriction `to != address(this)` while the function `transferFrom()` does not, which creates an inconsistency between them. This will cause the problem that users can use the `transferFrom()` function to transfer tokens to `address(this)`. ```solidity=62 require(to != address(this), "No transfers to contract allowed."); ```
The audit on Trustblock · Open the reportThe SolarX security record · Every SolarX address · This address on the explorer