0xd55bb498716aae08a761077e1a196fd42ce669af
As of 21 Nov 2026, Trustblock’s record holds 0xd55bb498716aae08a761077e1a196fd42ce669af on BNB Chain as a contract of BUSDChain. 1 audit report on Trustblock lists this address: CertiK, 3 Jan 2023. 17 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| busdchain. | CertiK | Not recorded (see the report) | Open |
2 High, 2 Medium, 13 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `BUSDChain` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority - pause the contract - unpause the contract and anyone can not withdraw - whether enable the withdrawal limit check - whether enable draw pool - set pool excludes address - set whitelist - set blacklist - whether enable burn power - transfer power token to any address - disable emergency withdrawal - emergency withdraw token to any address - update the power address - update launch date 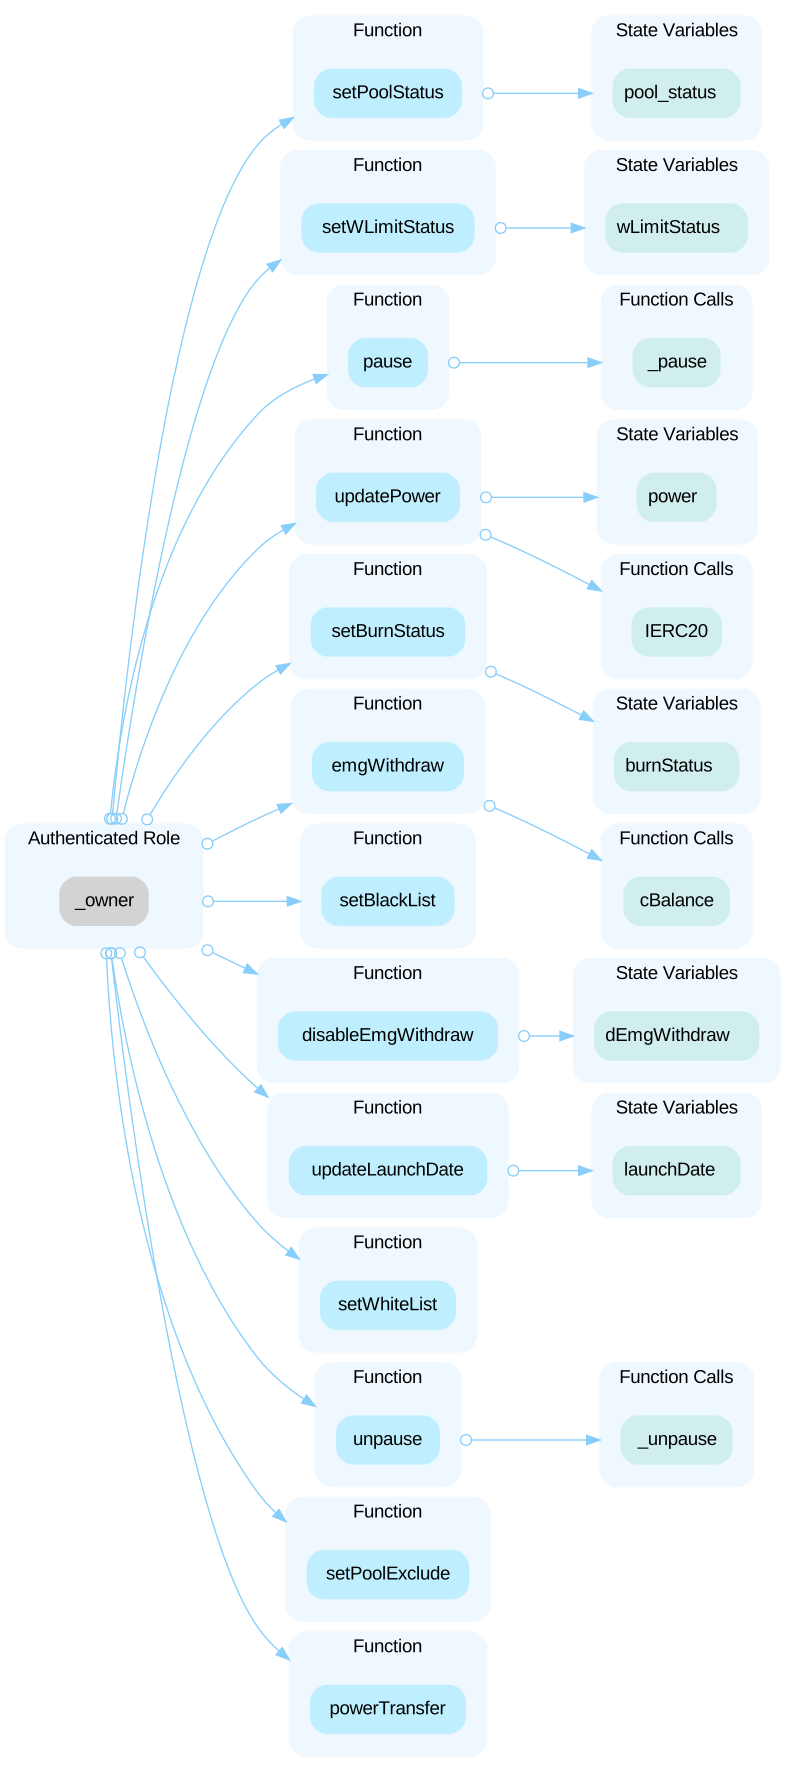 In the contract `BUSDChain`, the blacklist can not withdraw through the function `withdraw()`. In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and renounce and transfer ownership. 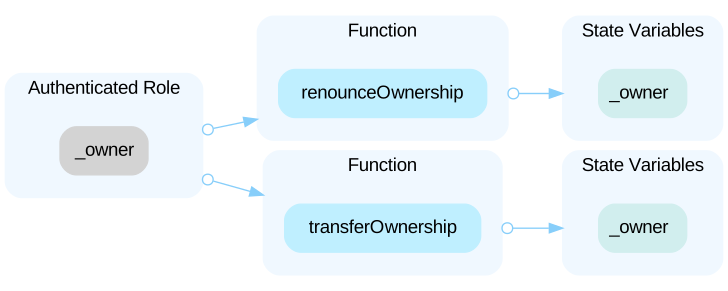 In the contract `UpgradeableBeacon` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and upgrade the beacon to a new implementation. 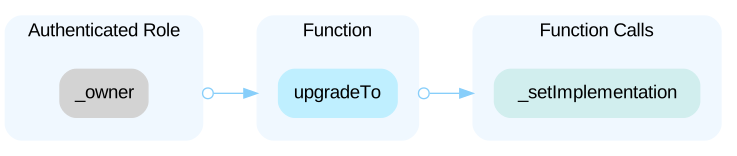 In the contract `ProxyAdmin` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and - change the admin of `proxy` to `newAdmin` - upgrade `proxy` to `implementation` - upgrade `proxy` to `implementation` and call a function on the new implementation 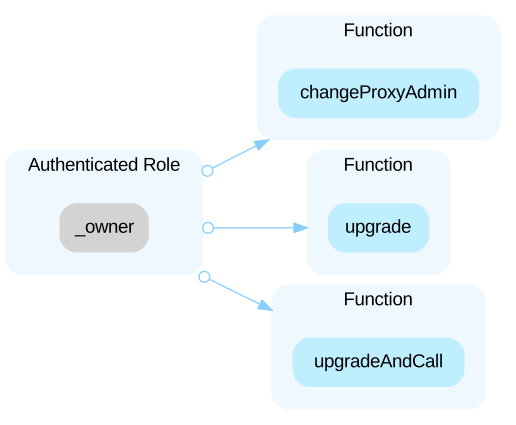
The audit on Trustblock · Open the report`import` and `BUSDChain` are upgradeable contracts, the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, he can change the implementation of the contract and drain tokens from the contract.
The audit on Trustblock · Open the reportIn the function `userAvailable()`, the function `payoutOf()` returns the deposit pending payout and max payout, and the `users[_addr].payouts` is the paid out. If the paid-out is less than the max payout, the direct bonus, pool bonus, and match bonus will be added to the pending payout and returned as a result. However, when processing deposit, direct, and pool payout, the `users[_addr].payouts` is not updated and the `to_payout` is not added. Therefore the returned `to_payout` will be larger than it actually is.
The audit on Trustblock · Open the reportIn the function `initialize()`, the initial upline of the owner is `address(0)`. The function `register()` requires that the upline of the caller is `address(0)`, which means that the owner can call the function to register. If the owner registers the `dfWallets[0]` as his upline, this forms a circle, because the upline of `dfWallets[0]` is the owner.
The audit on Trustblock · Open the reportIn the function `withdraw()`, the 'wL', 'wMY' and `dfWallets` can only get the direct and match bonus. However, there is no restriction in the function `deposit()` that these addresses cannot deposit. If they call the function `deposit()`, they will lose the deposit payout.
The audit on Trustblock · Open the reportThe loop is to move the data after index j forward, but one more loop is executed. ```solidity=450 for(uint256 k = j; k <= pool_size; k++) { pool_top[k] = pool_top[k + 1]; } ```
The audit on Trustblock · Open the reportFrom the contract, the power tokens are used as follows: 1. When the users deposit the `busd` token, they can get the five times the power tokens through the function `deposit()` 2. when the users withdraw, the power tokens are sent to the superior as a reward through the function `withdraw()` 3. If the `burnStatus` is true , the owner of the power tokens can burn them through the function `burnPower()` 4. Owner can transfer the power tokens to any address through the function `powerTransfer()` There is no logic related to power tokens in the contract, are the power tokens being used as intended and are there other uses for the power tokens?
The audit on Trustblock · Open the reportWhen transferring deflationary ERC20 tokens, the input amount may not be equal to the received amount due to the charged transaction fee. For example, if a user sends 100 deflationary tokens (with a 10% transaction fee), only 90 tokens actually arrived to the contract. However, a failure to discount such fees may allow the same user to withdraw 100 tokens from the contract, which causes the contract to lose 10 tokens in such a transaction. Reference: https://thoreum-finance.medium.com/what-exploit-happened-today-for-gocerberus-and-garuda-also-for-lokum-ybear-piggy-caramelswap-3943ee23a39f ```solidity=553 token.safeTransferFrom(msg.sender, address(this), _amount); ``` - Transferring tokens by `_amount`. ```solidity=563 _deposit(msg.sender, _amount); ``` - This function call executes the following operation. - In `BUSDChain._deposit`, - `_pollDeposits(_addr, _amount);` - In `BUSDChain._pollDeposits`, - `pool_users_refs_deposits_sum[pool_cycle][upline] += _amount;` - The `_amount` appears to be used for bookkeeping purposes without compensating the potential transfer fees.
The audit on Trustblock · Open the reportOn the function `withdraw()`, the loop that checks whether the sender is on the `dfWallets` could be more efficient if it aborted the loop once it has found a match.
The audit on Trustblock · Open the reportThe `withdraw()` function has the `whenNotPaused` modifier which checks that the contract is unpaused. If the owner pauses the contract, the caller can call the `deposit()` function but not the `withdraw()` function. Their tokens will be locked in the contract.
The audit on Trustblock · Open the reportThe `_upline` address is missing a check that it is not `address(0)`. If the `address(0)` is in the whitelist, the caller can register the `address(0)` as the upline. The caller considers he is already registered, then he calls the function `deposit()`, but is prompted "You need to register first".
The audit on Trustblock · Open the reportThe `wL`, `wMY`, and `dfWallets` can not get the pool bonus because the initial state of the `pool_exclude` is `true`. If the owner sets their status to `false`, then they can get the pool bonus, but the function `withdraw()` does not handle the logic about the pool bonus, so they may lose the pool bonus.
The audit on Trustblock · Open the reportIn the function `register()`, the whitelist can become upline without the deposit amount, the whitelist will get the direct and pool bonus when the users call the function `deposit()` or get the match bonus when the users call the function `withdraw()`. Due to the deposit amount being 0, then the max payout is 0. So the whitelist calls the function `withdraw()` will revert because it cannot pass the check on line 598.
The audit on Trustblock · Open the reportThe contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assume their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=195 IERC20 token; ``` - The contract `BUSDChain` interacts with third party contract with `IERC20` interface via `token`. --- ```solidity=197 IERC20 power; ``` - The contract `BUSDChain` interacts with third party contract with `IERC20` interface via `power`.
The audit on Trustblock · Open the reportThe return value of the transfer()/transferFrom() call is not checked. ```solidity=865 power.transfer(_addr, _amount); ```
The audit on Trustblock · Open the reportWeak PRNG due to a modulo on `block.timestamp`, `block.difficulty`, `msg.sender`, `block.coinbase`, `block.number`, `gasLeft` or `blockhash`. These can be influenced by miners to some extent, so they should be avoided. ```solidity=529 _upline = dfWallets[random() % 12]; ```
The audit on Trustblock · Open the reportThe BUSDChain security record · Every BUSDChain address · This address on the explorer