0x72beddf7032eec58f199857b79a8e37020c14e42
As of 21 Nov 2026, Trustblock’s record holds 0x72beddf7032eec58f199857b79a8e37020c14e42 on Ethereum as a contract of MXNB. 1 audit report on Trustblock lists this address: CertiK, 15 May 2024. 3 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on Ethereum.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| MXNB Audit 2024 | CertiK | Not recorded (see the report) | Open |
1 High, 2 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `Rescuable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the rescuer address. 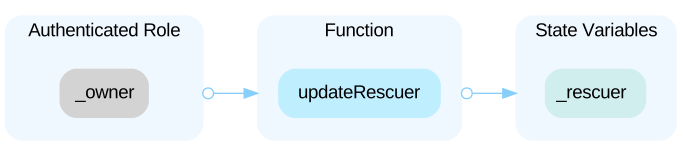 In the contract `Rescuable` the role `_rescuer` has authority over the functions shown in the diagram below. Any compromise to the `_rescuer` account may allow the hacker to take advantage of this authority and transfer tokens in this contract to any address. 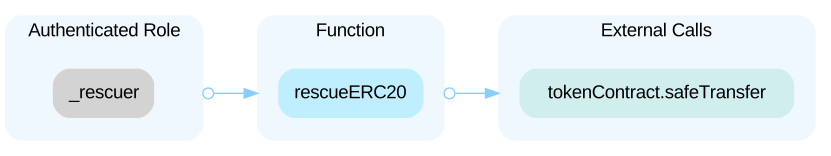 ----- In the contract `Blacklistable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the blacklister address. 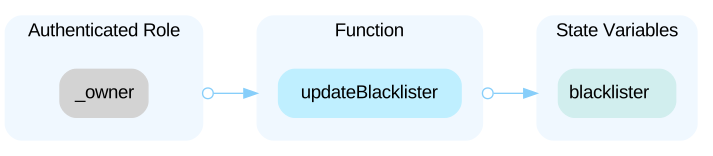 In the contract `Blacklistable` the role `blacklister` has authority over the functions shown in the diagram below. Any compromise to the `blacklister` account may allow the hacker to take advantage of this authority and add an account to the blacklist and remove the account from the blacklist. 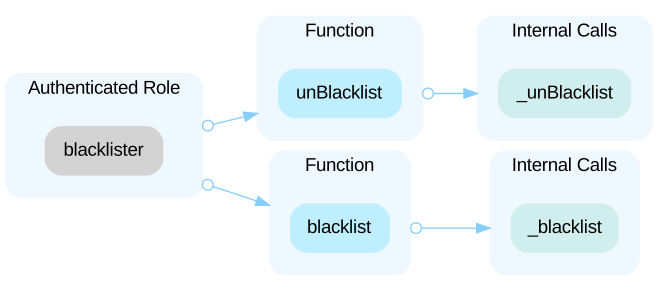 ----- In the contract `FiatTokenV1` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the master minter address. 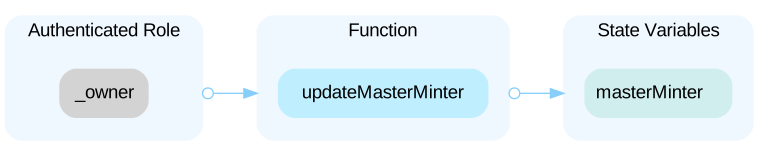 In the contract `FiatTokenV1` the role `masterMinter` has authority over the functions shown in the diagram below. Any compromise to the `masterMinter` account may allow the hacker to take advantage of this authority and add or update a new minter with a mint allowance and remove a minter. 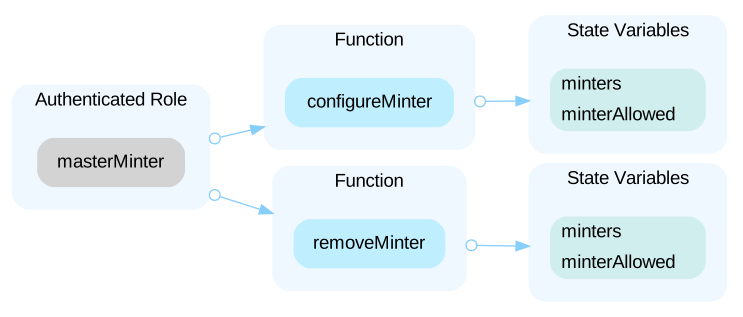 In the contract `FiatTokenV1` the role `minters` has authority over the functions shown in the diagram below. Any compromise to the `minters` account may allow the hacker to take advantage of this authority and mint fiat tokens to an address and allow minters to burn their own tokens. 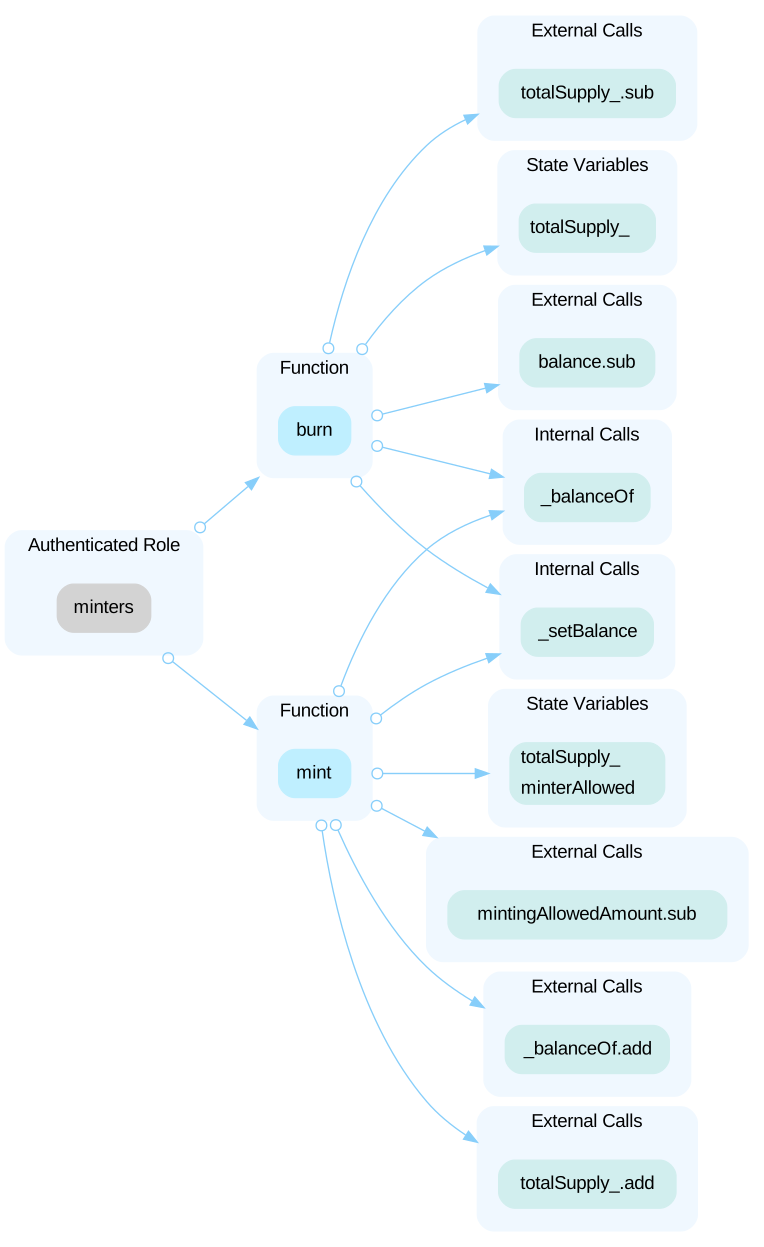 ----- In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and allow the current owner to transfer control of the contract to a new owner. 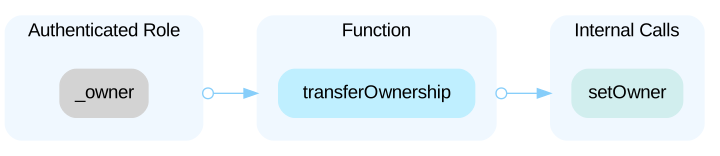 ----- In the contract `Pausable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the pauser address. 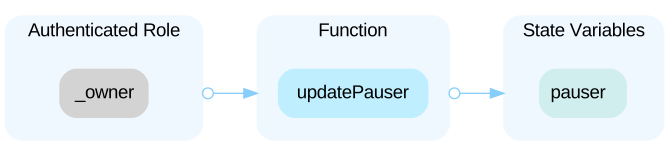 In the contract `Pausable` the role `pauser` has authority over the functions shown in the diagram below. Any compromise to the `pauser` account may allow the hacker to take advantage of this authority and pause/unpause the contract. 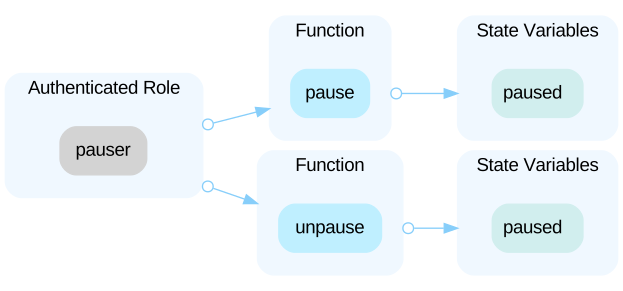
The audit on Trustblock · Open the reportThe `initialize()` function is not called by another contract atomically after the contract is deployed, so it's possible for a malicious user to call `initialize()` which, if it's noticed in time, would require the project to re-deploy the contract in order to properly initialize. The functions `initializeV2()`, `initializeV2_1()` and `initializeV2_2()` have the same issue.
The audit on Trustblock · Open the reportThe change of `_owner` by function `transferOwnership()` overrides the previously set `_owner` with the new one without guaranteeing the new `_owner` is able to actuate transactions on-chain.
The audit on Trustblock · Open the reportThe MXNB security record · Every MXNB address · This address on the explorer